
CVE-2024-52317
 tam-k592/cve-2024-52317
CVE-2024-52317 - Apache Tomcat HTTP/2 Data Leakage Vulnerability
data-exfiltrationexploitationinformation-gathering+2
3
tam-k592/cve-2024-52317CVE-2024-52317 - Apache Tomcat HTTP/2 Data Leakage Vulnerability
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 darabium/cve-2024-28987
**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…
 abdulazizalsewedy/cve-2021-29447
Step-by-step demonstration of CVE-2021-29447, a WordPress Media Library XXE vulnerability leaking sensitive files via crafted WAVE uploads, including…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 t4e-3/cve-2025-63296
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 paulpierre/informer
A Telegram Mass Surveillance Bot in Python
 mazen160/shennina
Automating Host Exploitation with AI
 b1tbreaker/cve-2025-48708
Lack of argument sanitization leading to password leakage in Ghostscript PDF versions up to 10.05.0.
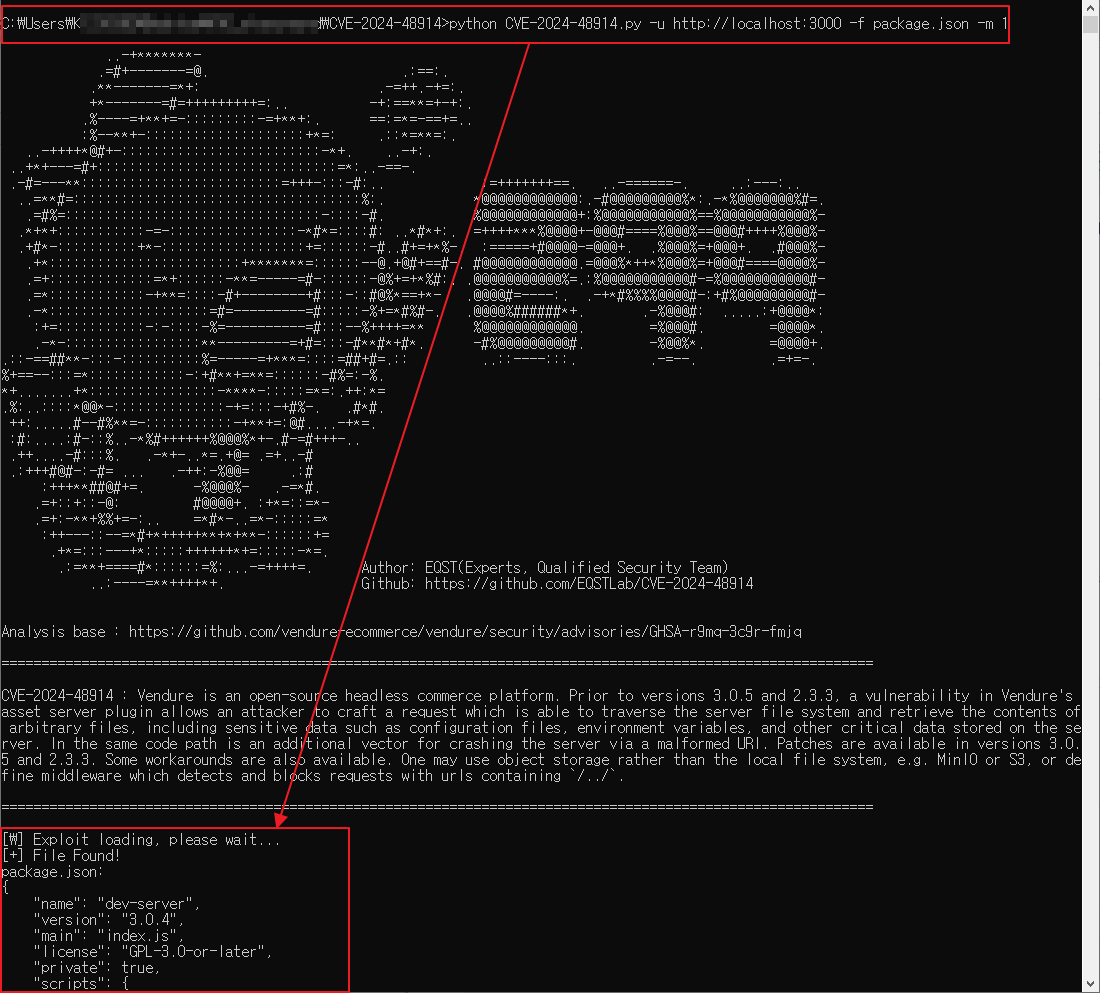 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
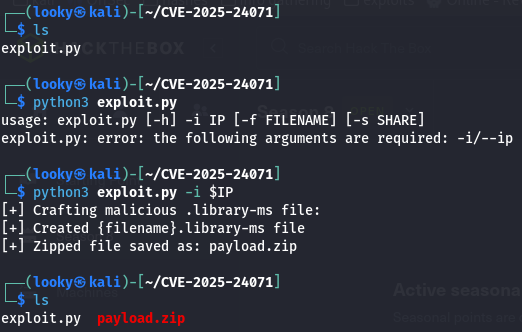 looky243/cve-2025-24071-poc
CVE-2025-24071 Proof Of Concept
 tea-on/cve-2021-29447-authenticated-xxe-wordpress-5.6-5.7
POC to exploit WordPress 5.6-5.7 (PHP 8+) Authenticated XXE Injection.
 amirzargham/cve-2023-08-21-exploit
Axigen < 10.3.3.47, 10.2.3.12 - Reflected XSS
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts
 francesc-h/firebase
Exploiting misconfigured firebase databases
 randomrobbiebf/cve-2024-56067
WP SuperBackup <= 2.3.3 - Missing Authorization to Unauthenticated Back-Up File Download