
CVE-2019-14678
 mbadanoiu/cve-2019-14678
CVE-2019-14678: XML External Entity in SAS XML Mapper
data-exfiltrationexploitationvulnerability-analysis+1
mbadanoiu/cve-2019-14678CVE-2019-14678: XML External Entity in SAS XML Mapper
 v3s9er/cve-2026-52886
Notepad++ CVE-2026-52886 — session.xml backupFilePath starts_with() path traversal (GHSA-rqfm-pw34-r7j6)
 randomrobbiebf/cve-2024-56067
WP SuperBackup <= 2.3.3 - Missing Authorization to Unauthenticated Back-Up File Download
 ch4120n/cve-2026-15409
Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…
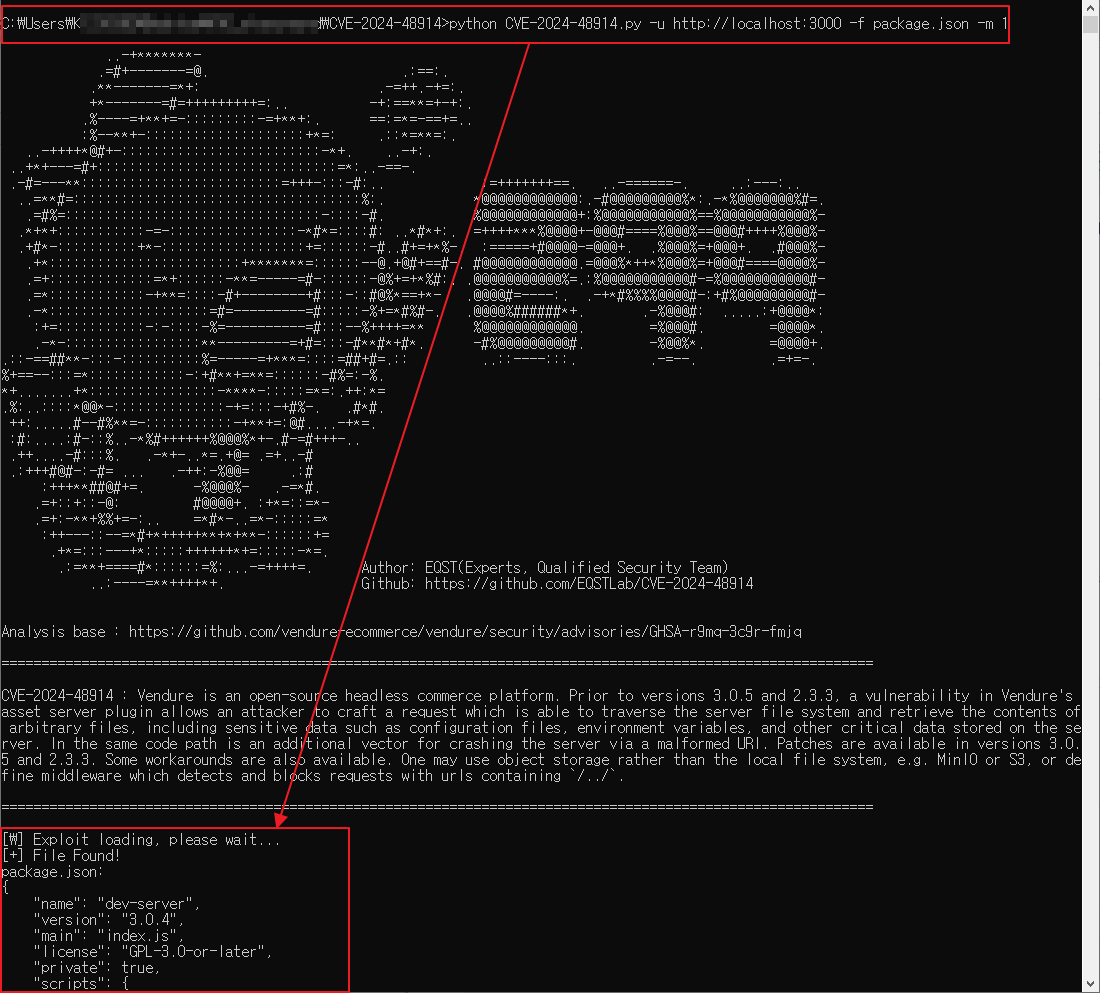 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
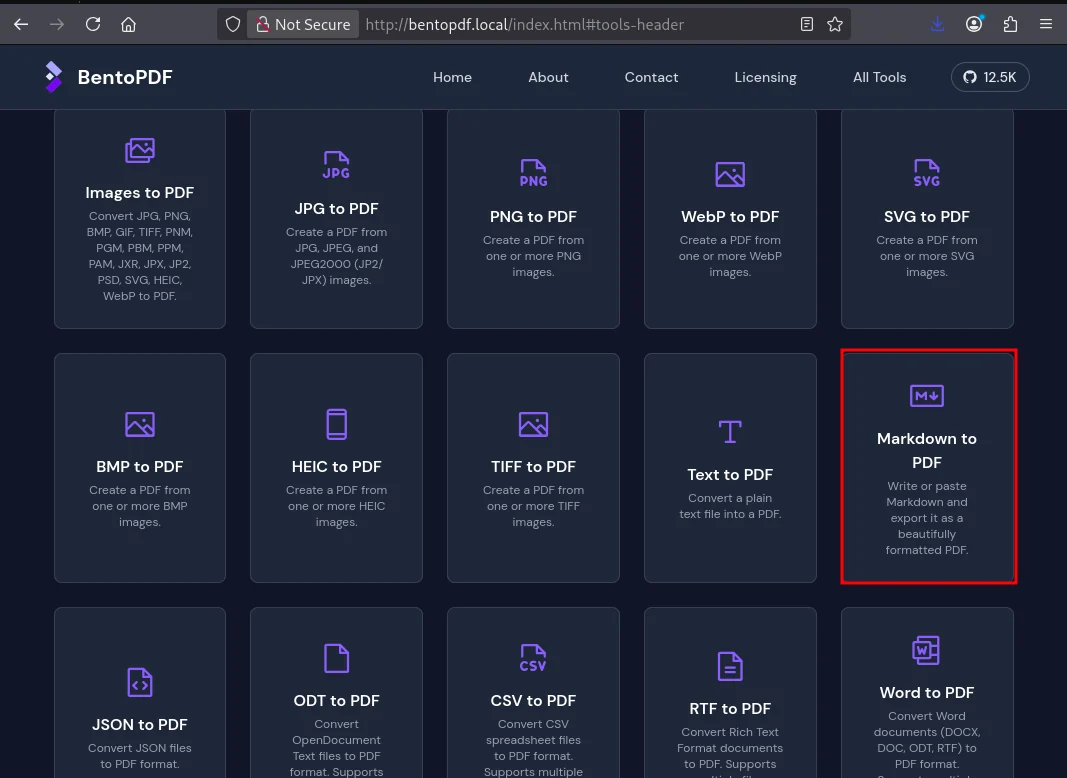 astaruf/cve-2026-41653
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
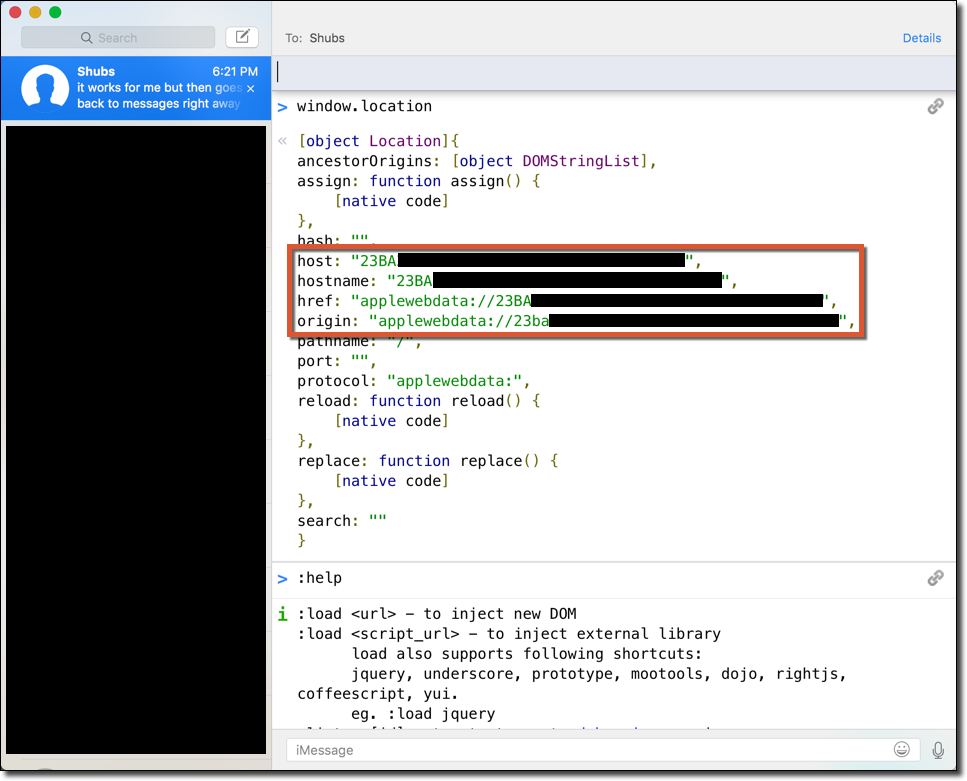 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
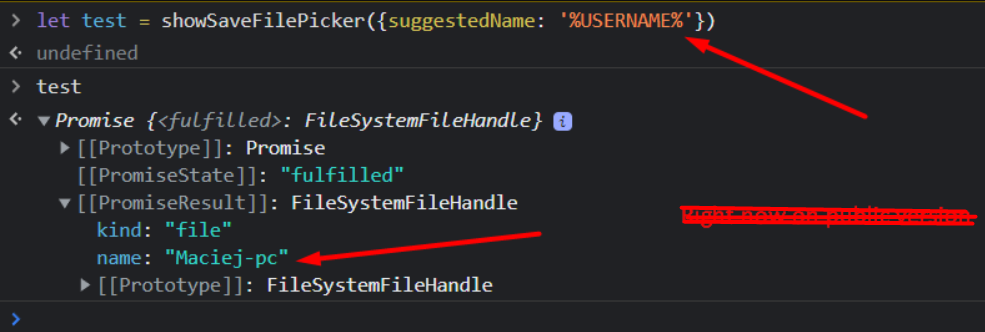 puliczek/cve-2022-0337-poc-google-chrome-microsoft-edge-opera
🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 yunuscadirci/callstranger
Vulnerability checker for Callstranger (CVE-2020-12695)
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 jollheef/libreoffice-remote-arbitrary-file-disclosure
Proof of concept of LibreOffice remote arbitrary file disclosure vulnerability
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 duy-31/cve-2023-35636
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC