

OneLogicalMyth_Shell
 nccgroup/onelogicalmyth_shell
A HTA shell to assist with breakout assessments.
command-and-controldata-exfiltrationpenetration-testing+3
110
nccgroup/onelogicalmyth_shellA HTA shell to assist with breakout assessments.
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 hunniccyber/sharpml
Machine Learning Network Share Password Hunting Toolkit
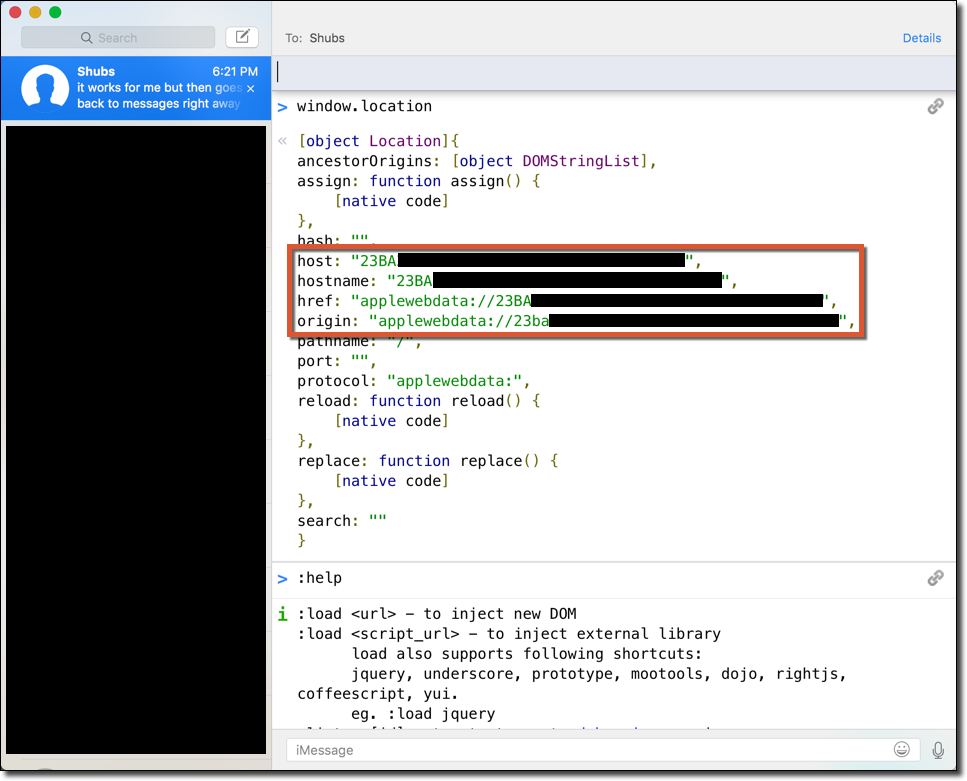 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
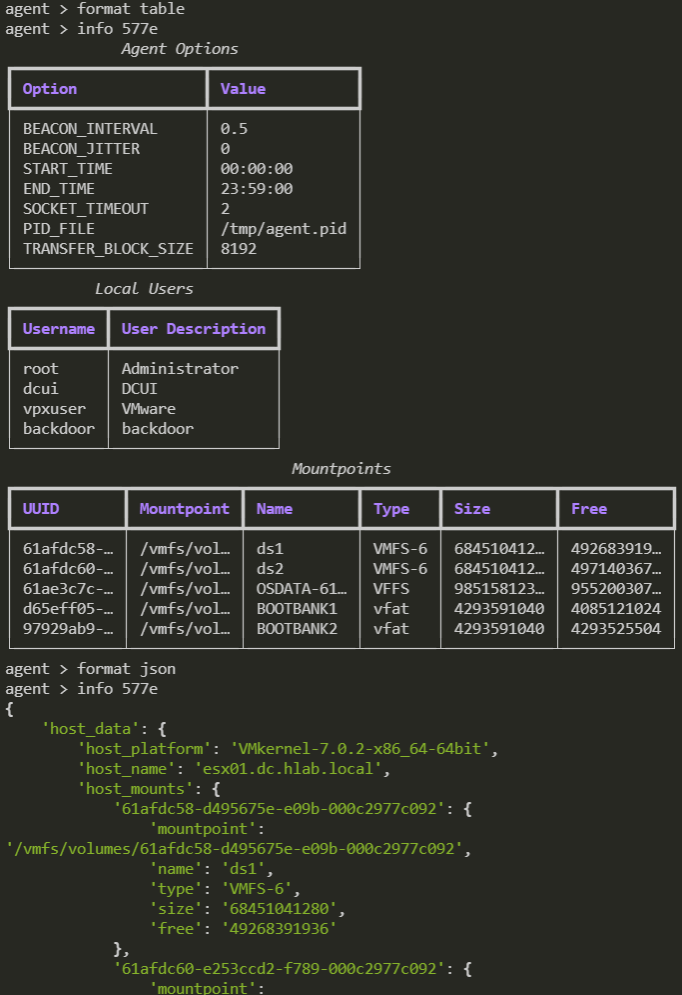 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 gursev/flash-xdomain-xploit
ActionScript Proof of Concept to perform cross-domain reads
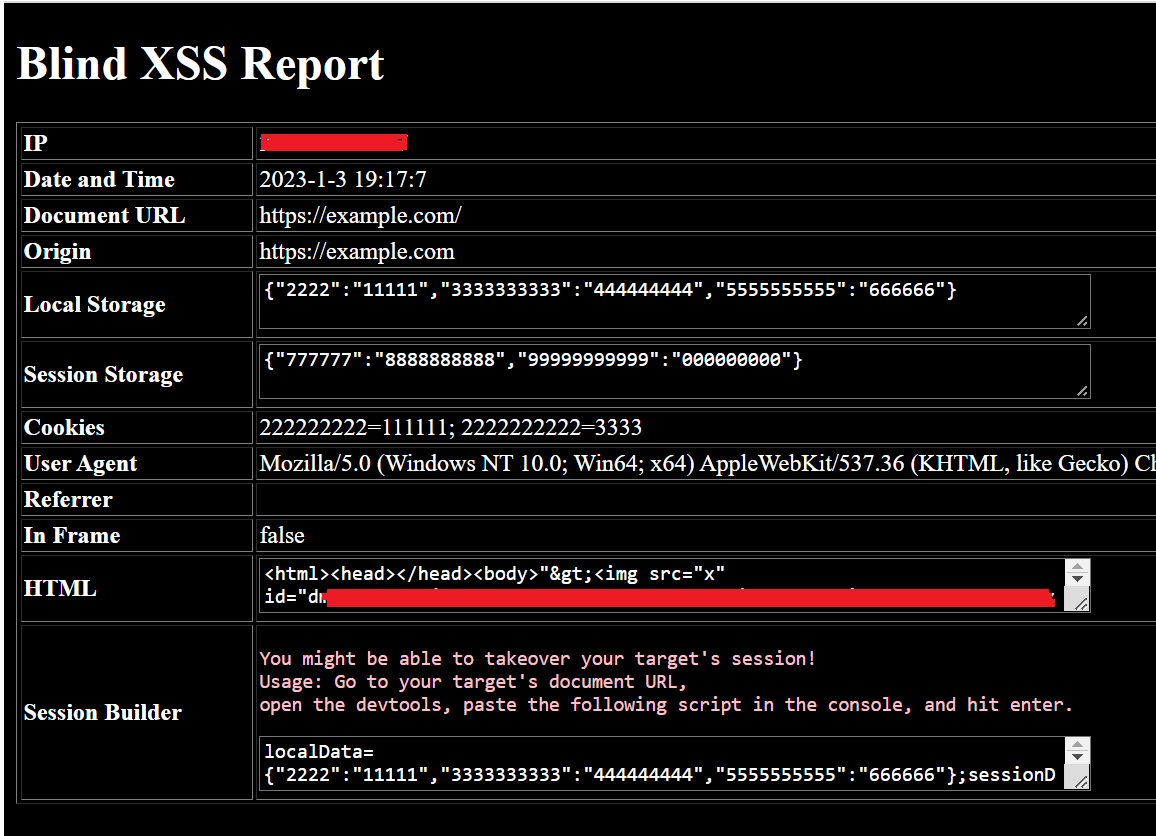 seifelsallamy/xssfire
A standalone Blind XSS Script.
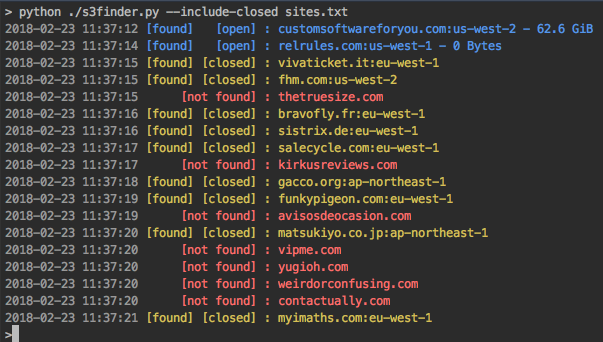 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 beetlechunks/cve-2020-12116
Proof of concept code to exploit CVE-2020-12116: Unauthenticated arbitrary file read on ManageEngine OpManger.
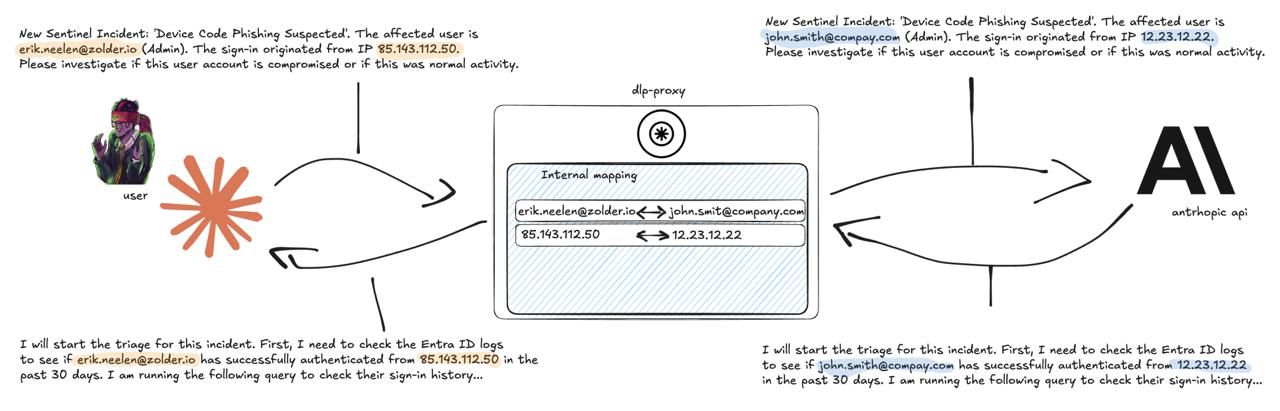 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 bibi1959/cve-2019-15514
telegram bug that discloses user's hidden phone number (still unpatched) (exploit included)
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
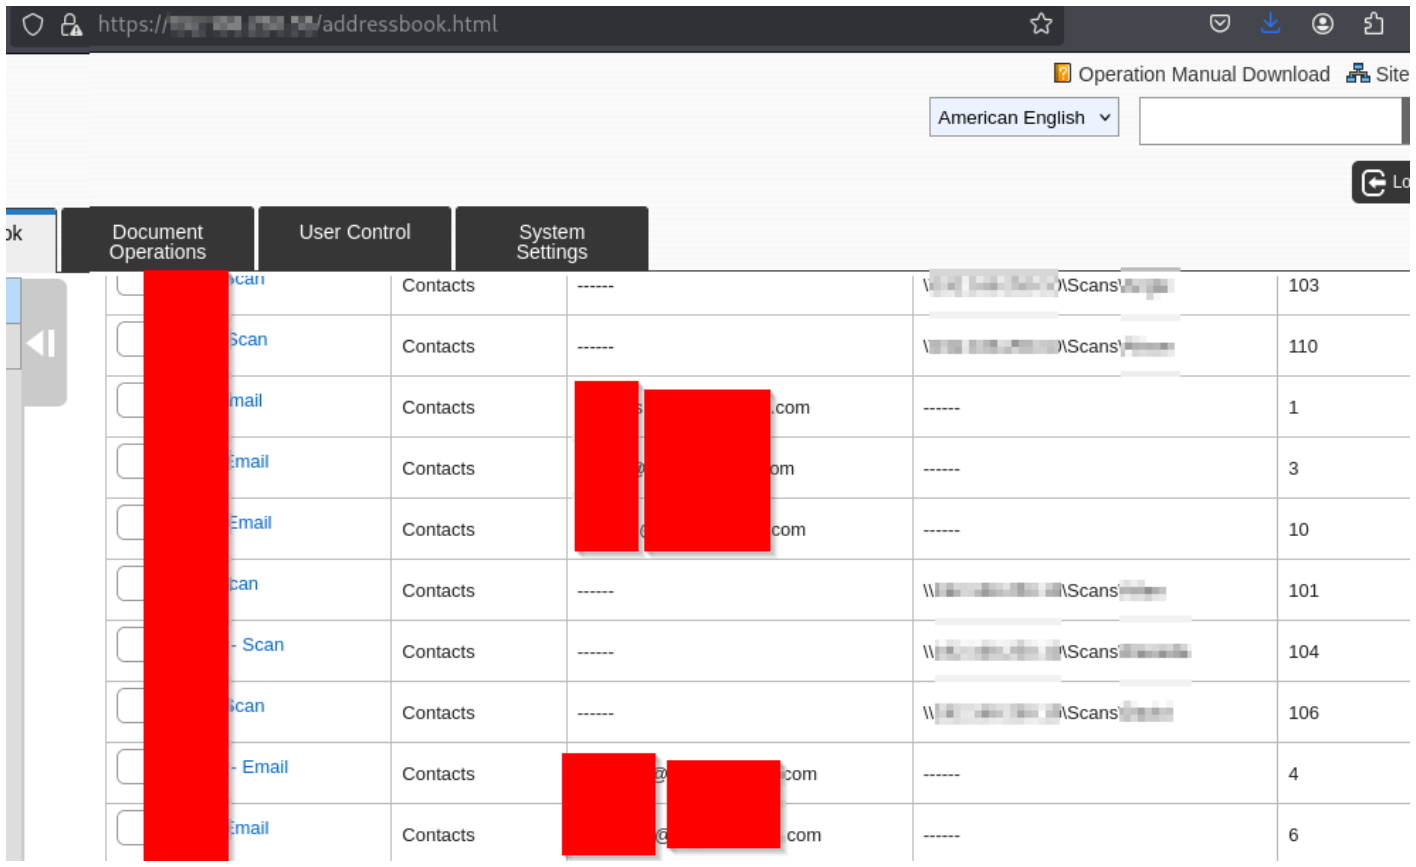 redr0nin/cve-2026-63563
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
 nxploited/cve-2025-7401
Premium Age Verification / Restriction for WordPress <= 3.0.2 - Unauthenticated Arbitrary File Read and Write
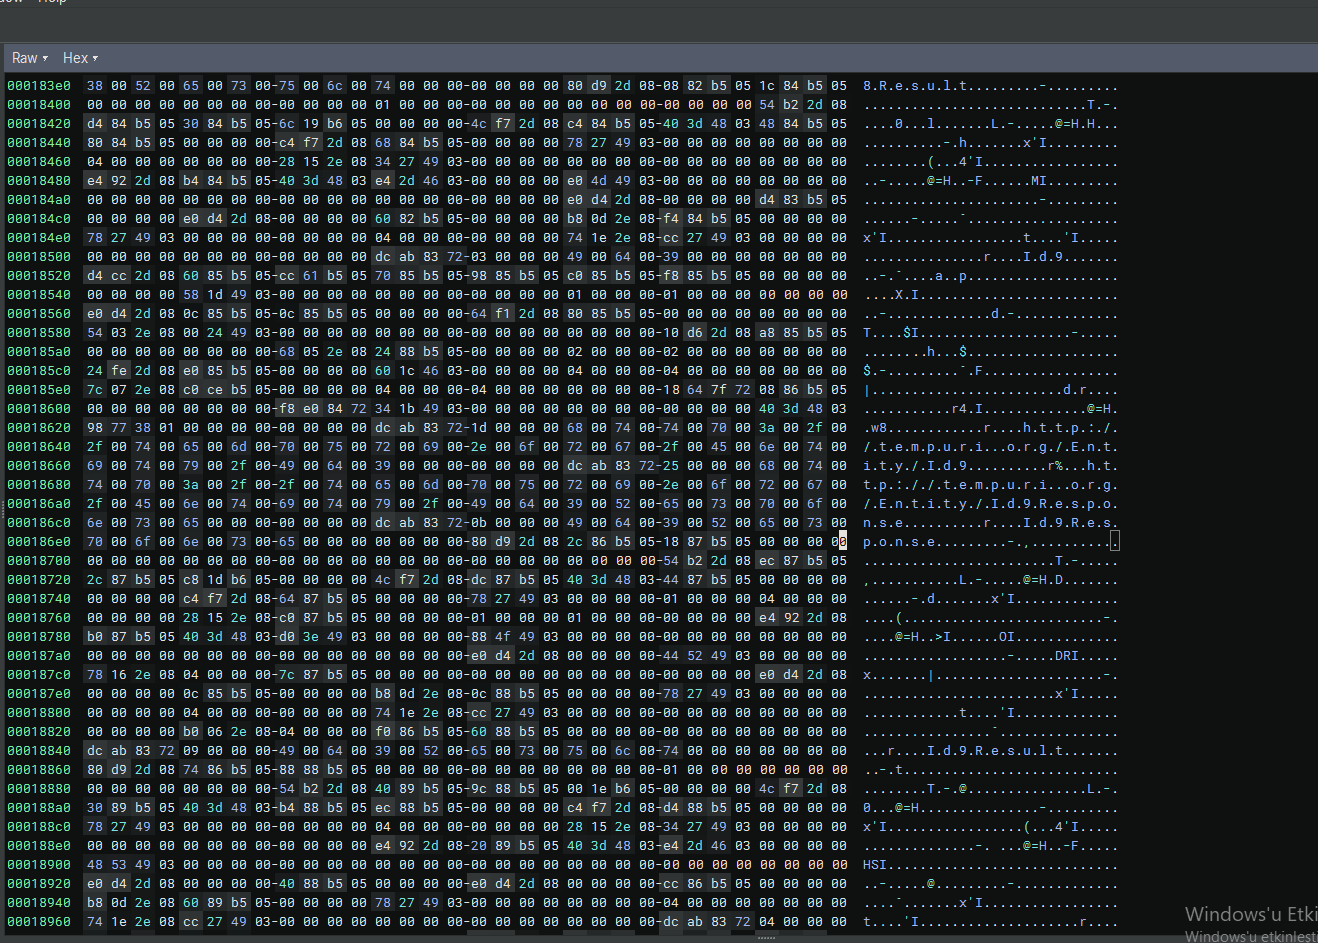 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…