
zygote-CVE-2024-31317
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
android-securitydata-exfiltrationexploitation+3
4
vnescape/zygote-cve-2024-31317This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
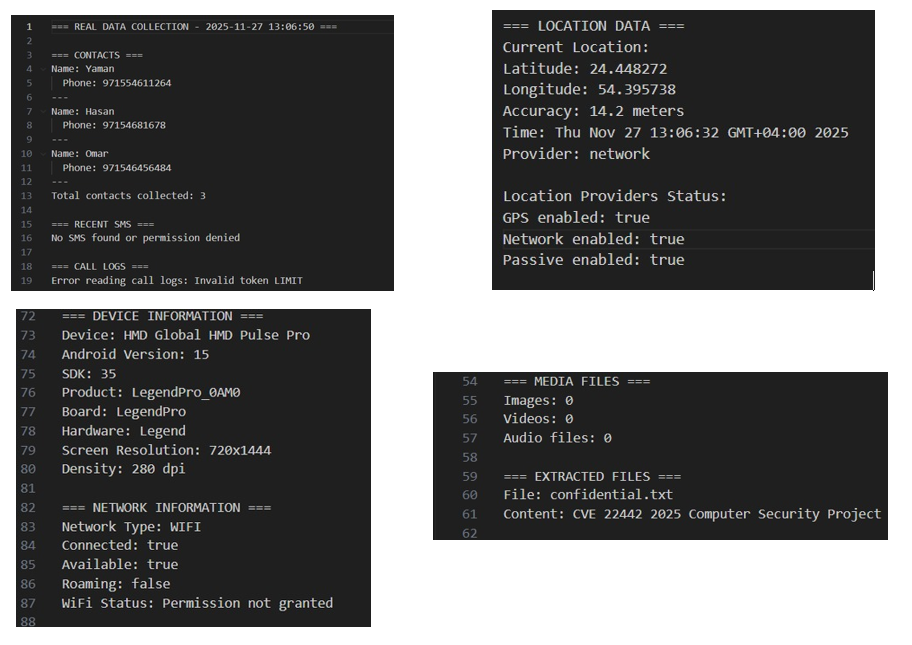 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 kai2er/cve-2024-0044-exp
利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
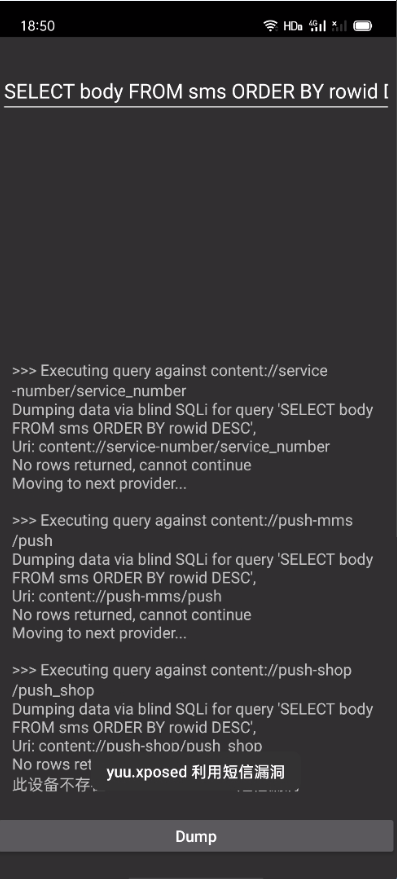 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
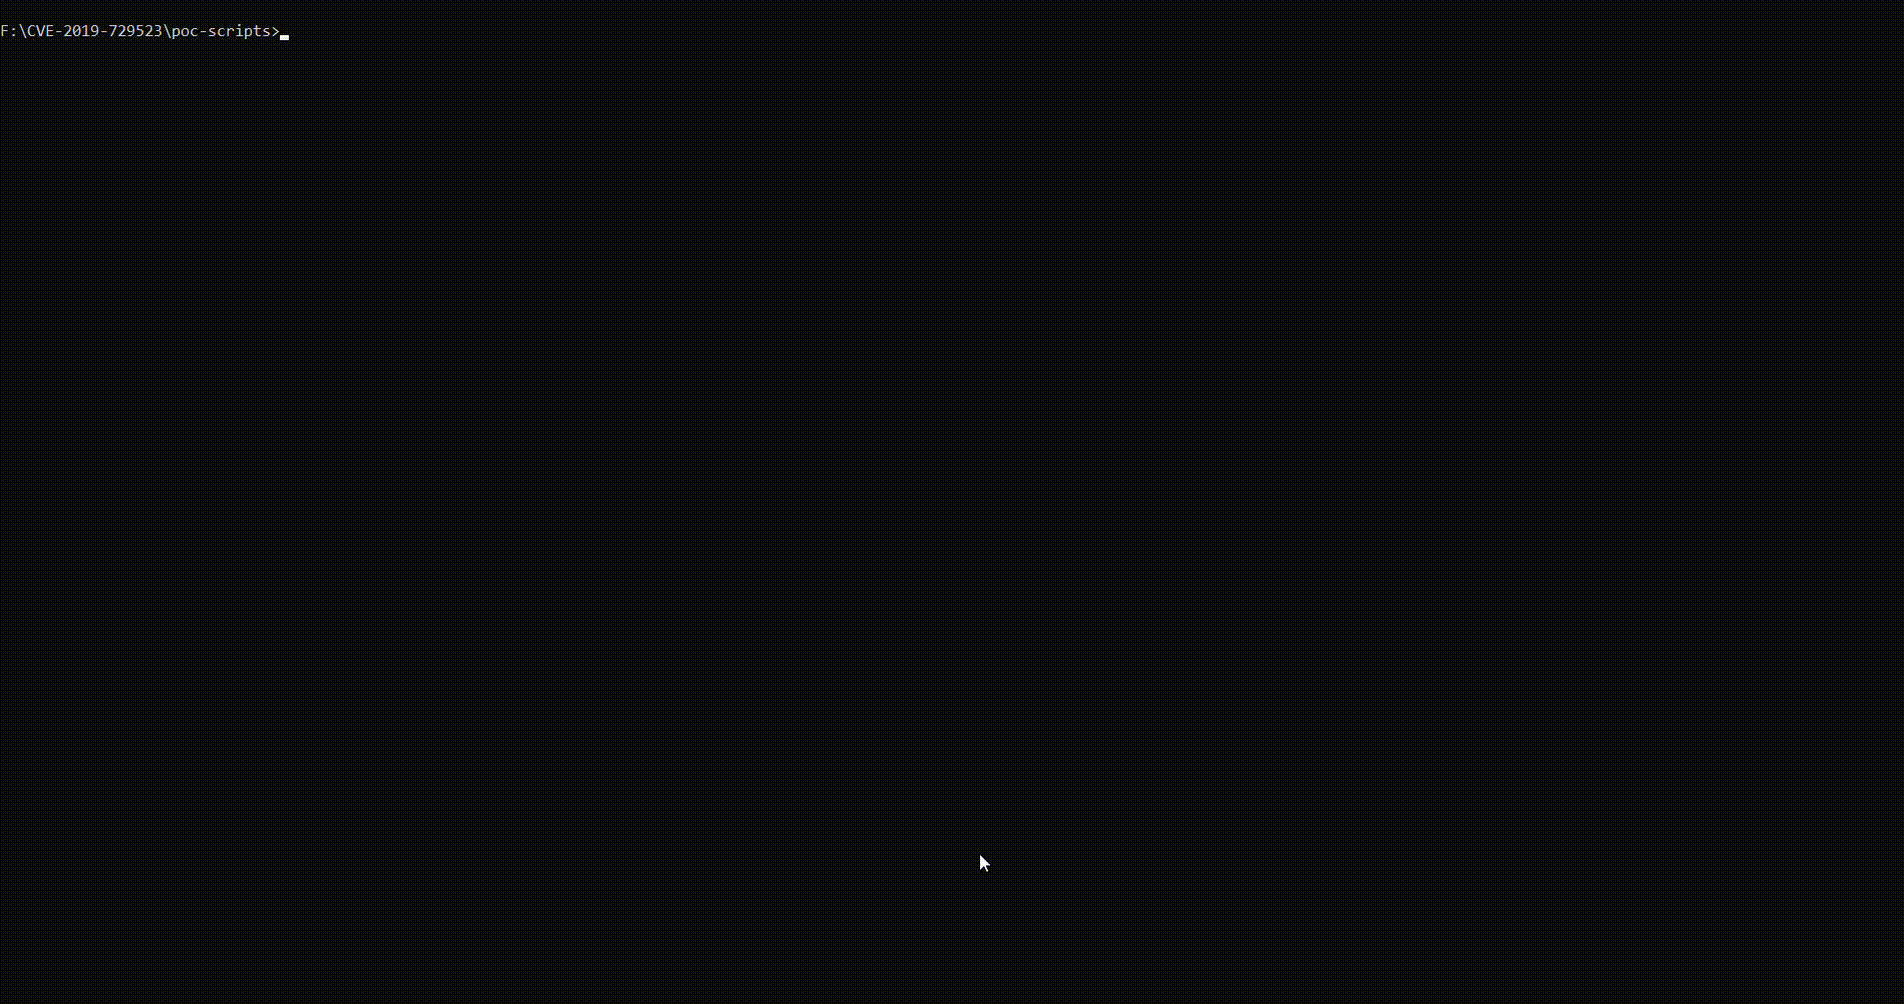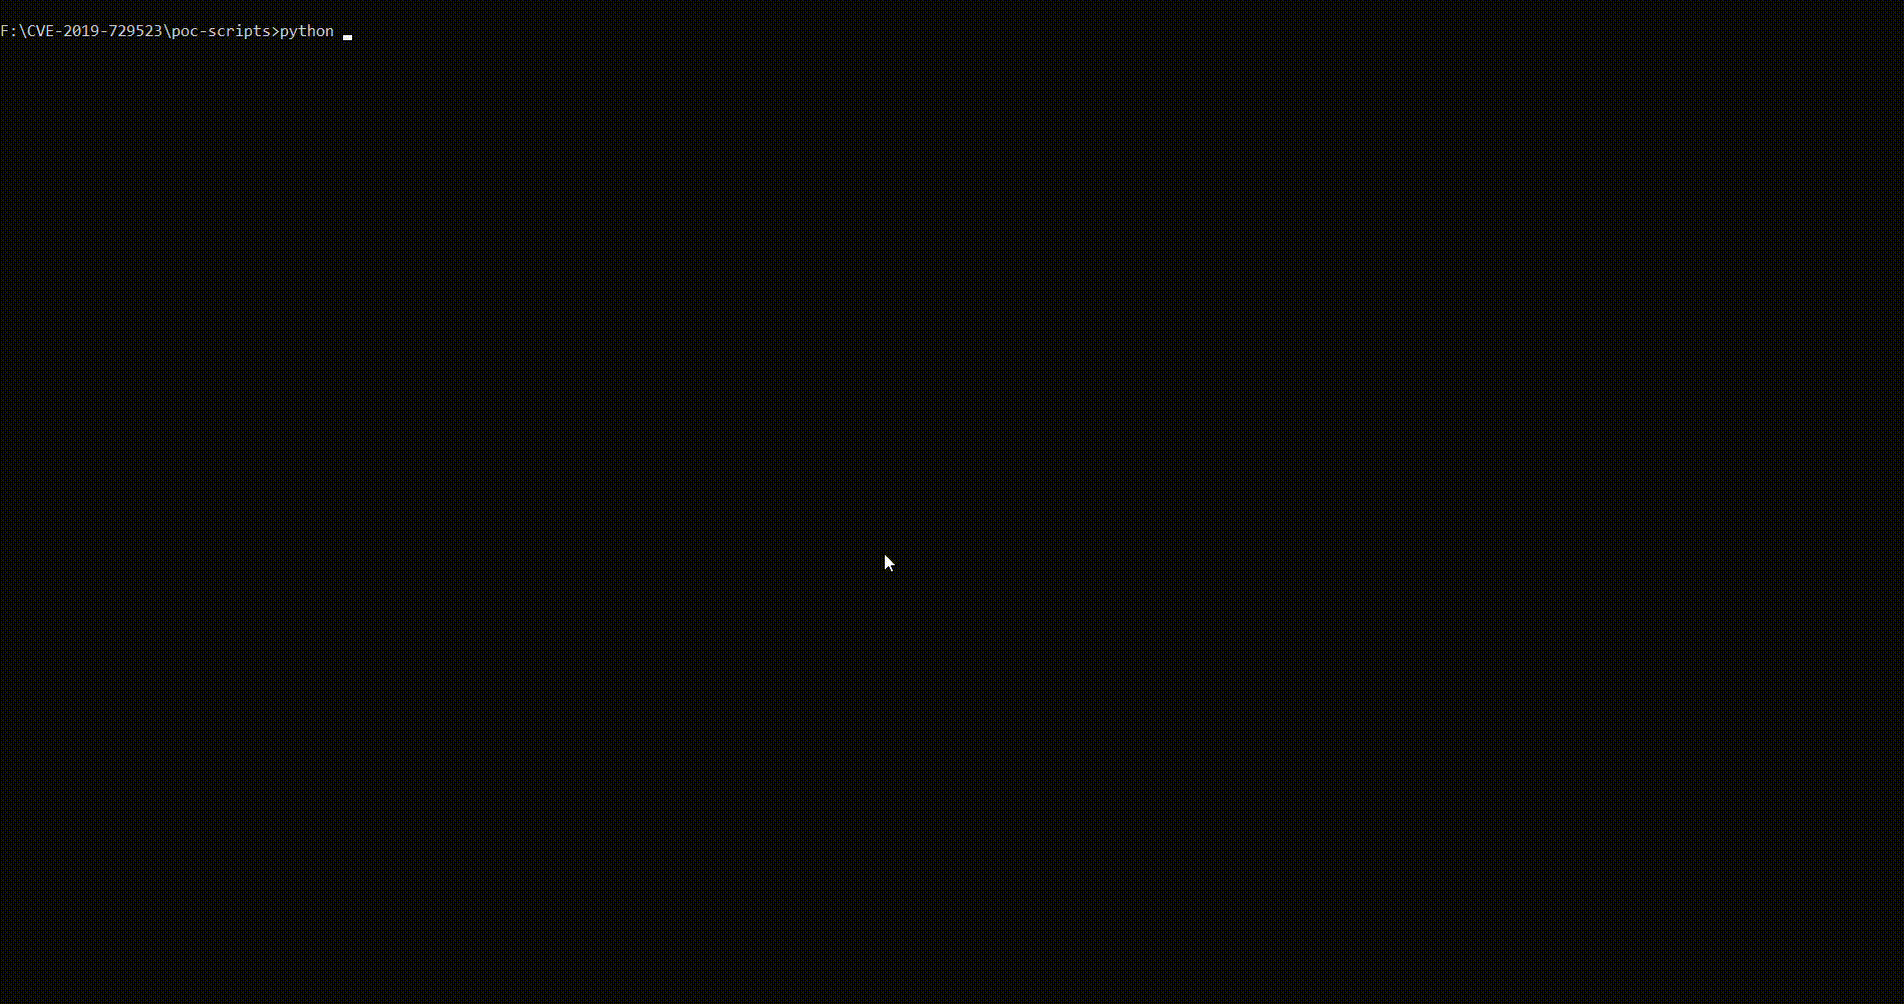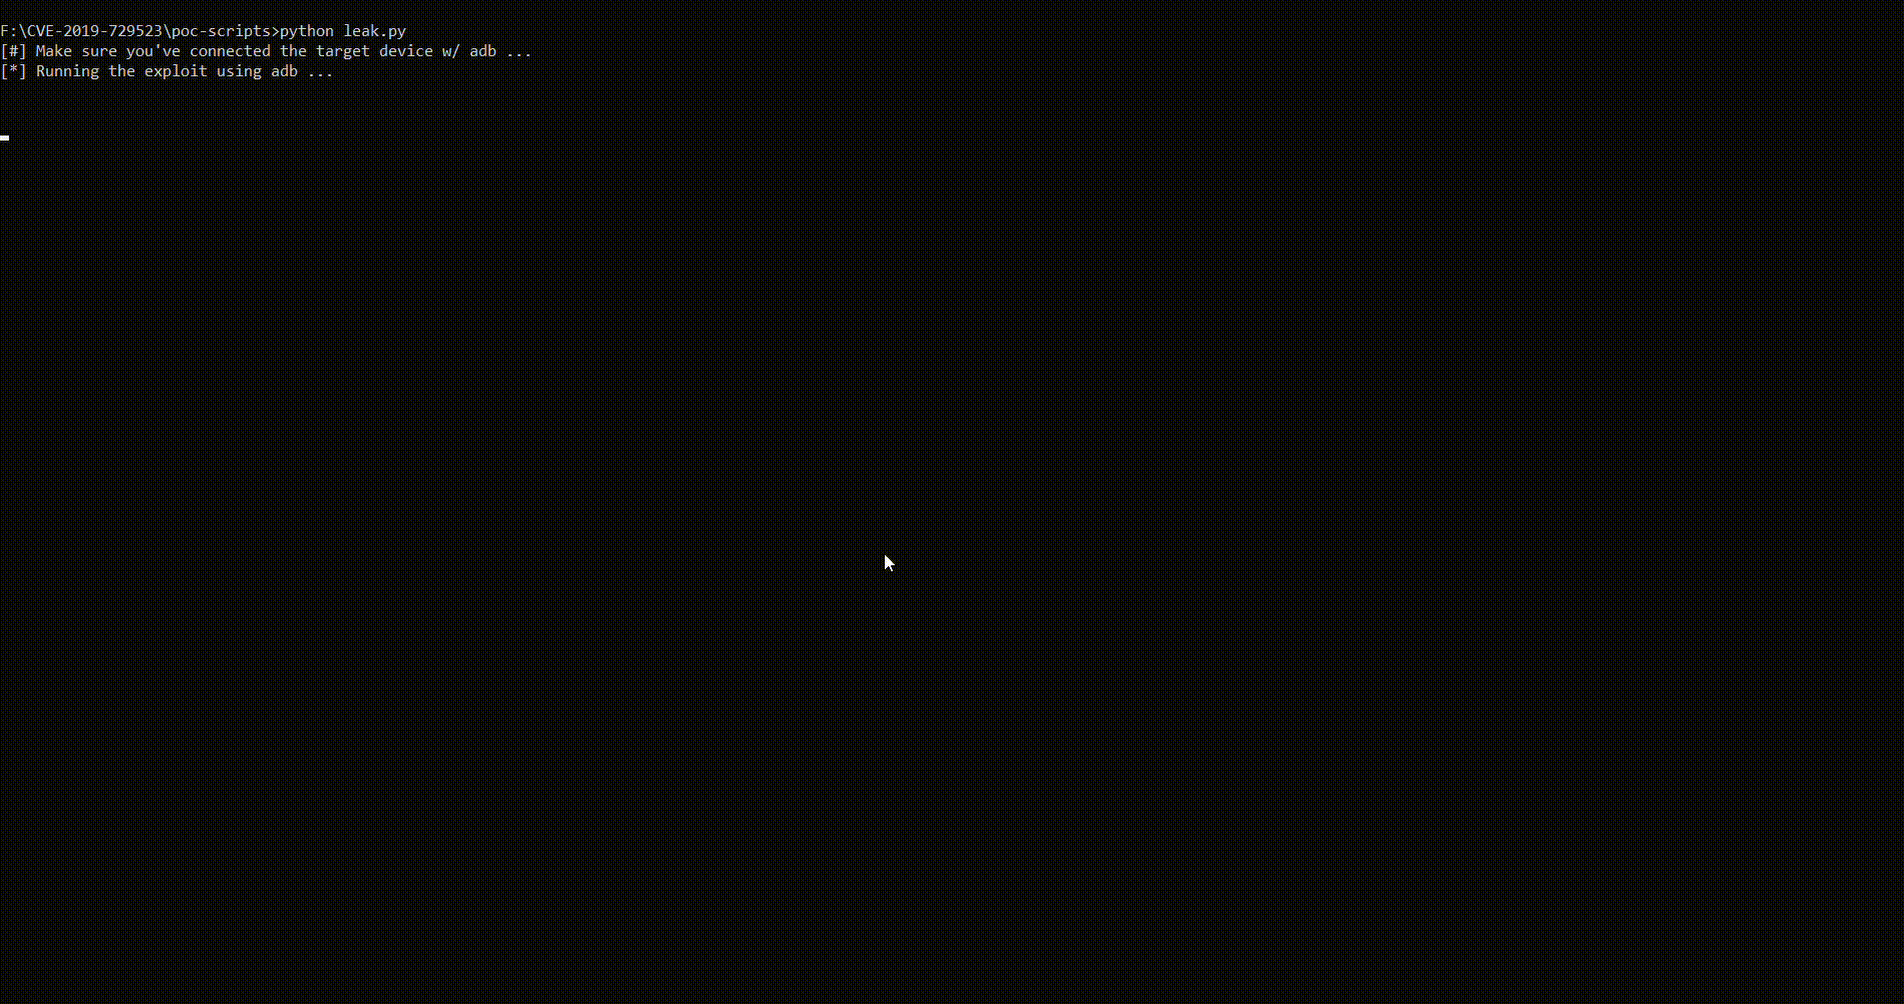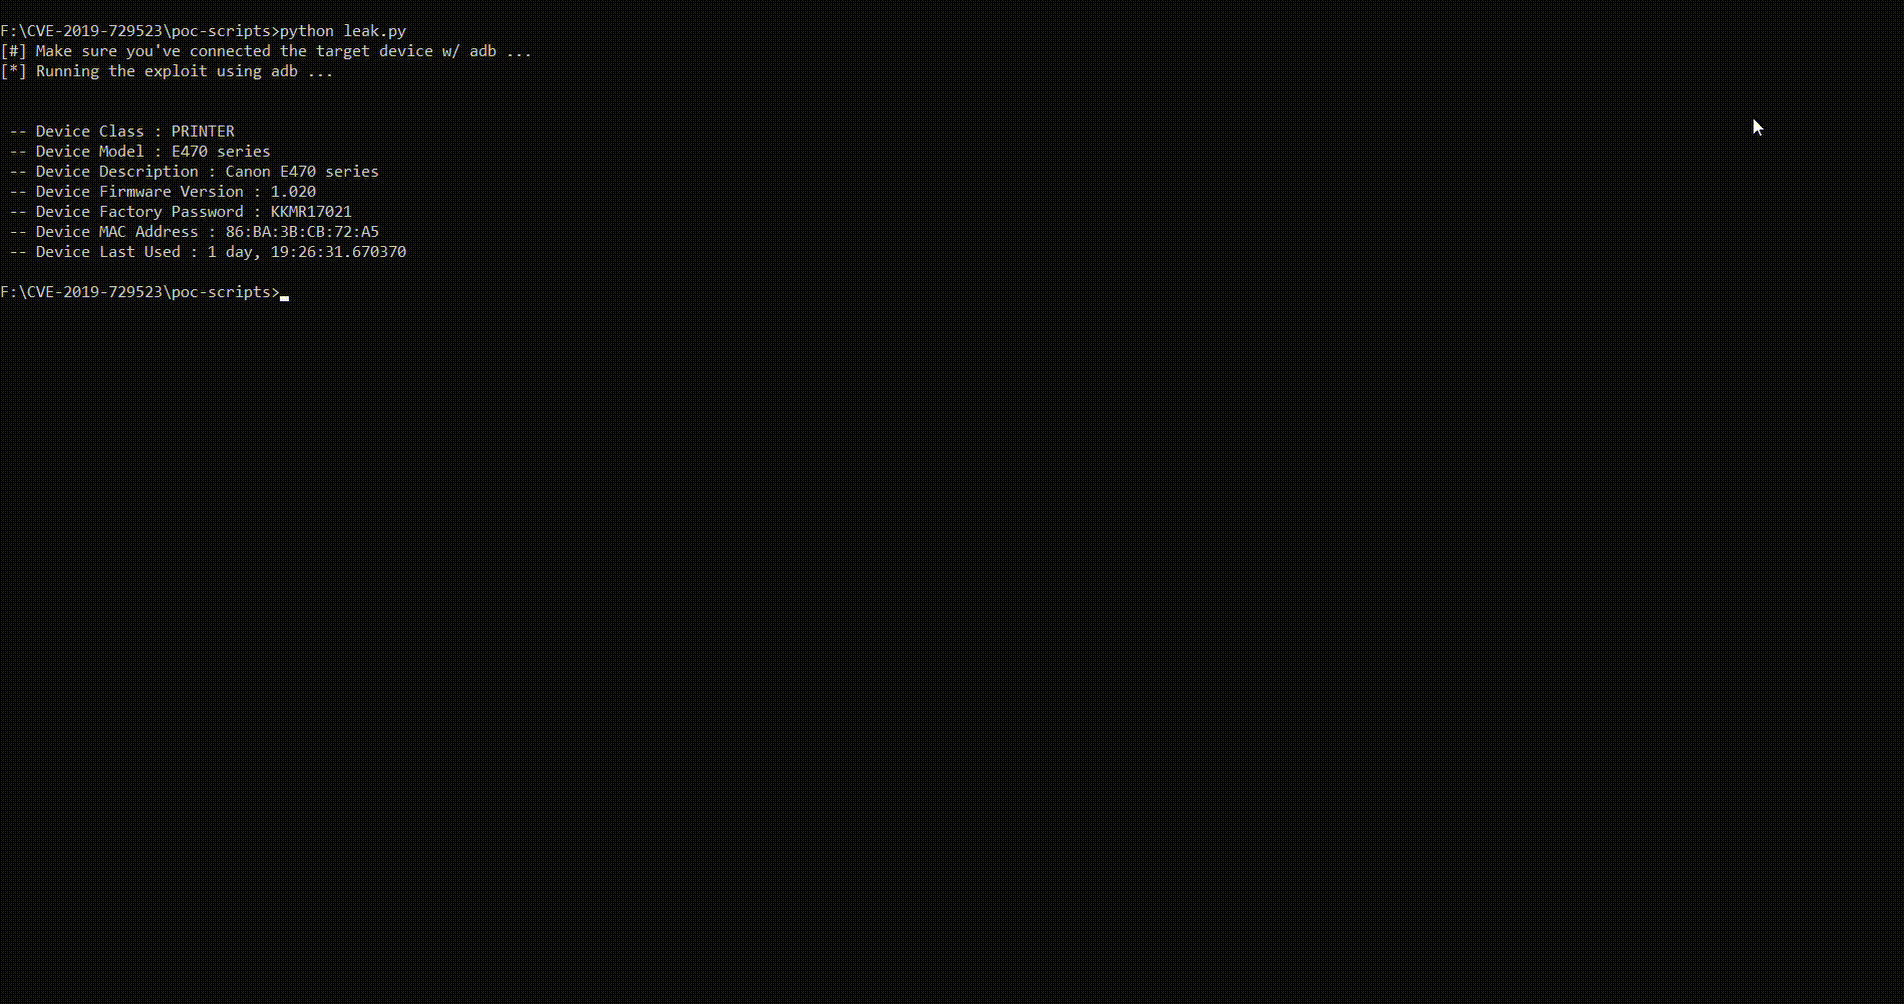 0x48piraj/cve-2019-14339
POC for CVE-2019-14339 Canon PRINT 2.5.5
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 thespeedx/tbomb
This is a SMS And Call Bomber For Linux And Termux
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration