
cve-2022-44268
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
data-exfiltrationexploitationinformation-gathering+2
4
agathanon/cve-2022-44268Payload generator and extractor for CVE-2022-44268 written in Python.
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 0xbassiouny1337/cve-2024-42009
This script exploits a stored XSS vulnerability (CVE-2024-42009) in Roundcube Webmail version 1.6.7. It injects a malicious payload into the webmail…
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
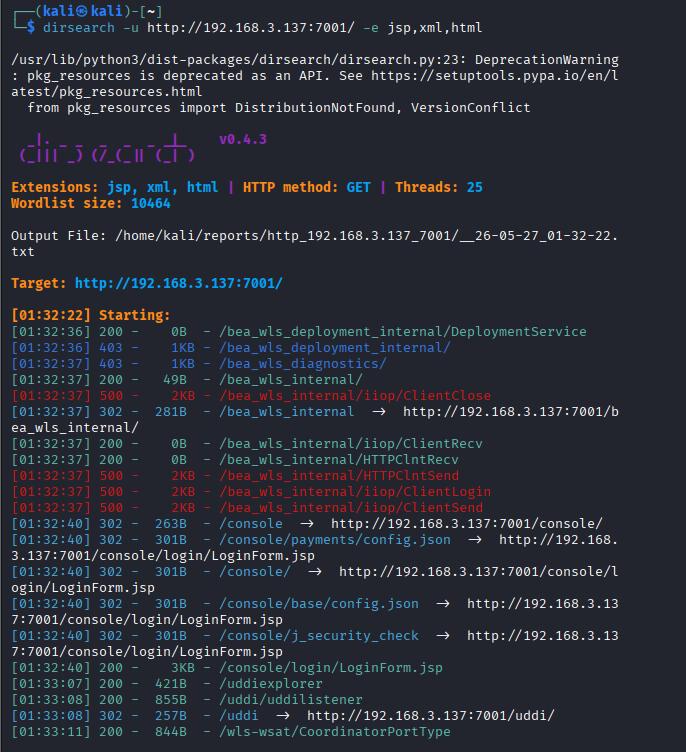 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 zakaria-laouani/cve-2023-0669-simulation
Simulation environment for CVE-2023-0669 with Docker-based attacker, vulnerable server, and listener containers. Demonstrates deserialization exploit…
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
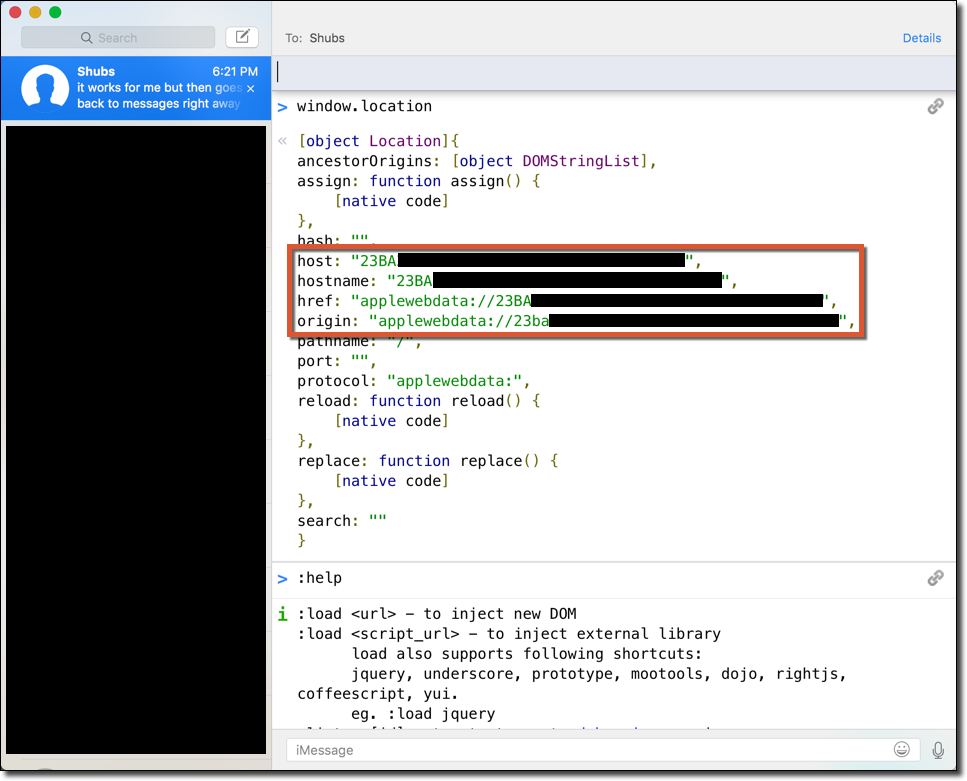 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 udyz/cve-2025-53770-exploit
Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
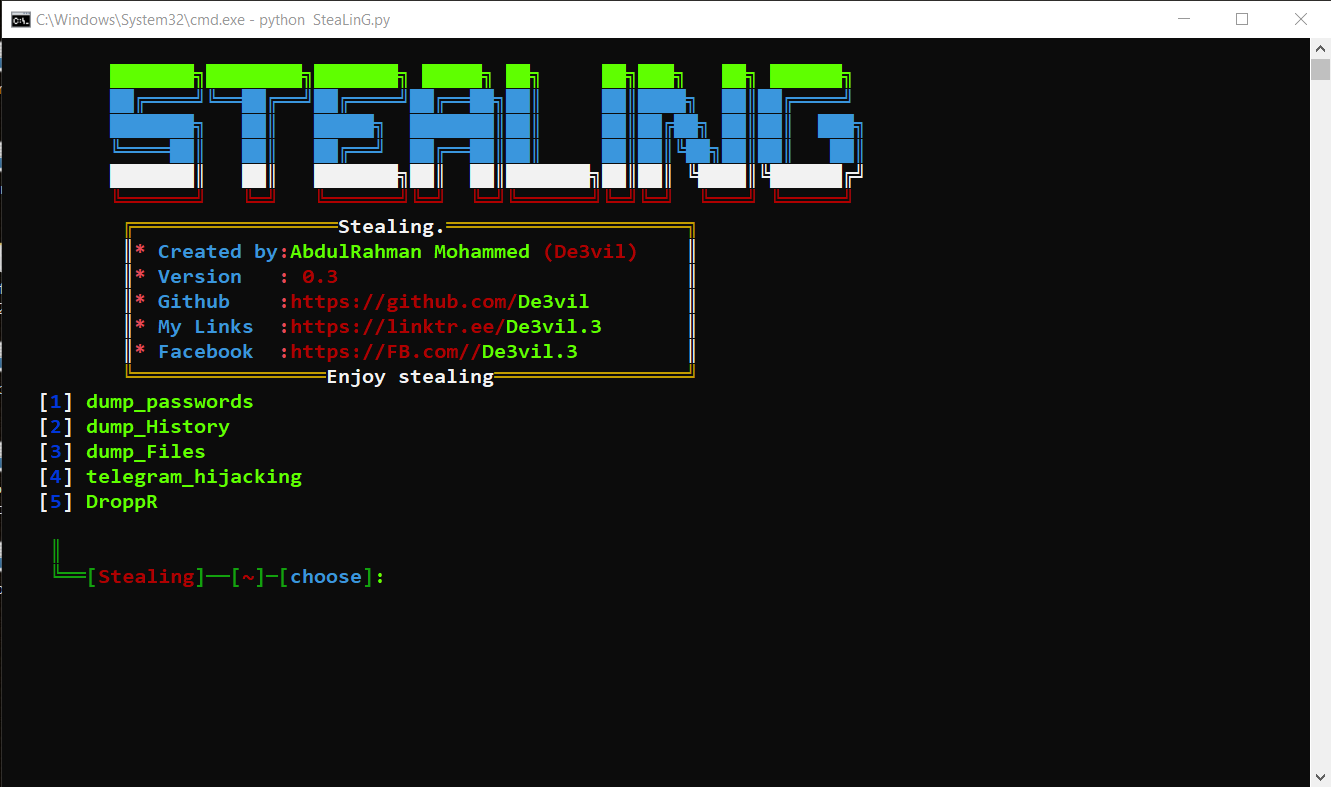 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 osandamalith/exe2image
A simple utility to convert EXE files to JPEG images and vice versa.
 shadowforge-cyber/cve-2026-84388-poc
Improper Restriction of Rendered UI Layers or Frames (CWE-1021)
 sectestannaquinn/grassmarlin-cve-2026-6807-xxe-poc
Reverse Engineered based on CISA disclosure of new CVE
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
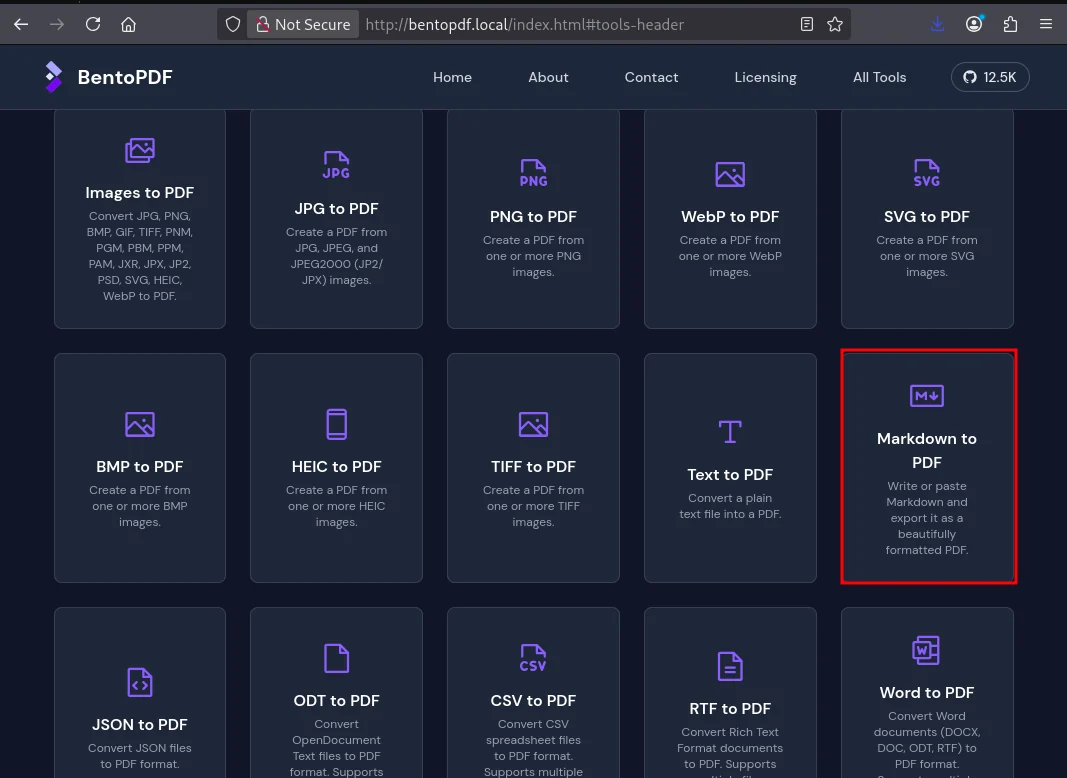 astaruf/cve-2026-41653
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
 aseemyash/krle
CVE-2025-55182 & CVE-2025-66478 proof of concepts