

DDWPasteRecon
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
data-exfiltrationdefensive-toolsincident-response+4
46
viralmaniar/ddwpastereconDDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 ac3lives/kyocera-cve-2022-1026
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords
 robertaitch/telegram-story-scraper
A Python script that allows you to automatically scrape and download stories from your Telegram friends using the Telethon library. The script…
 absholi7ly/apache-ofbiz-directory-traversal-exploit
Exploit for Apache OFBiz CVE-2024-32113 path traversal via crafted XML-RPC requests, enabling arbitrary file read and potential command execution on…
 qmf0c3uk/cve-2020-17518
Python exploit for CVE-2020-17518, allowing arbitrary file write via Apache Flink REST API. Supports single target and batch scanning from a file.
 jakabakos/cve-2024-34102-cosmicsting-xxe-in-adobe-commerce-and-magento
CosmicSting: critical unauthenticated XXE vulnerability in Adobe Commerce and Magento (CVE-2024-34102)
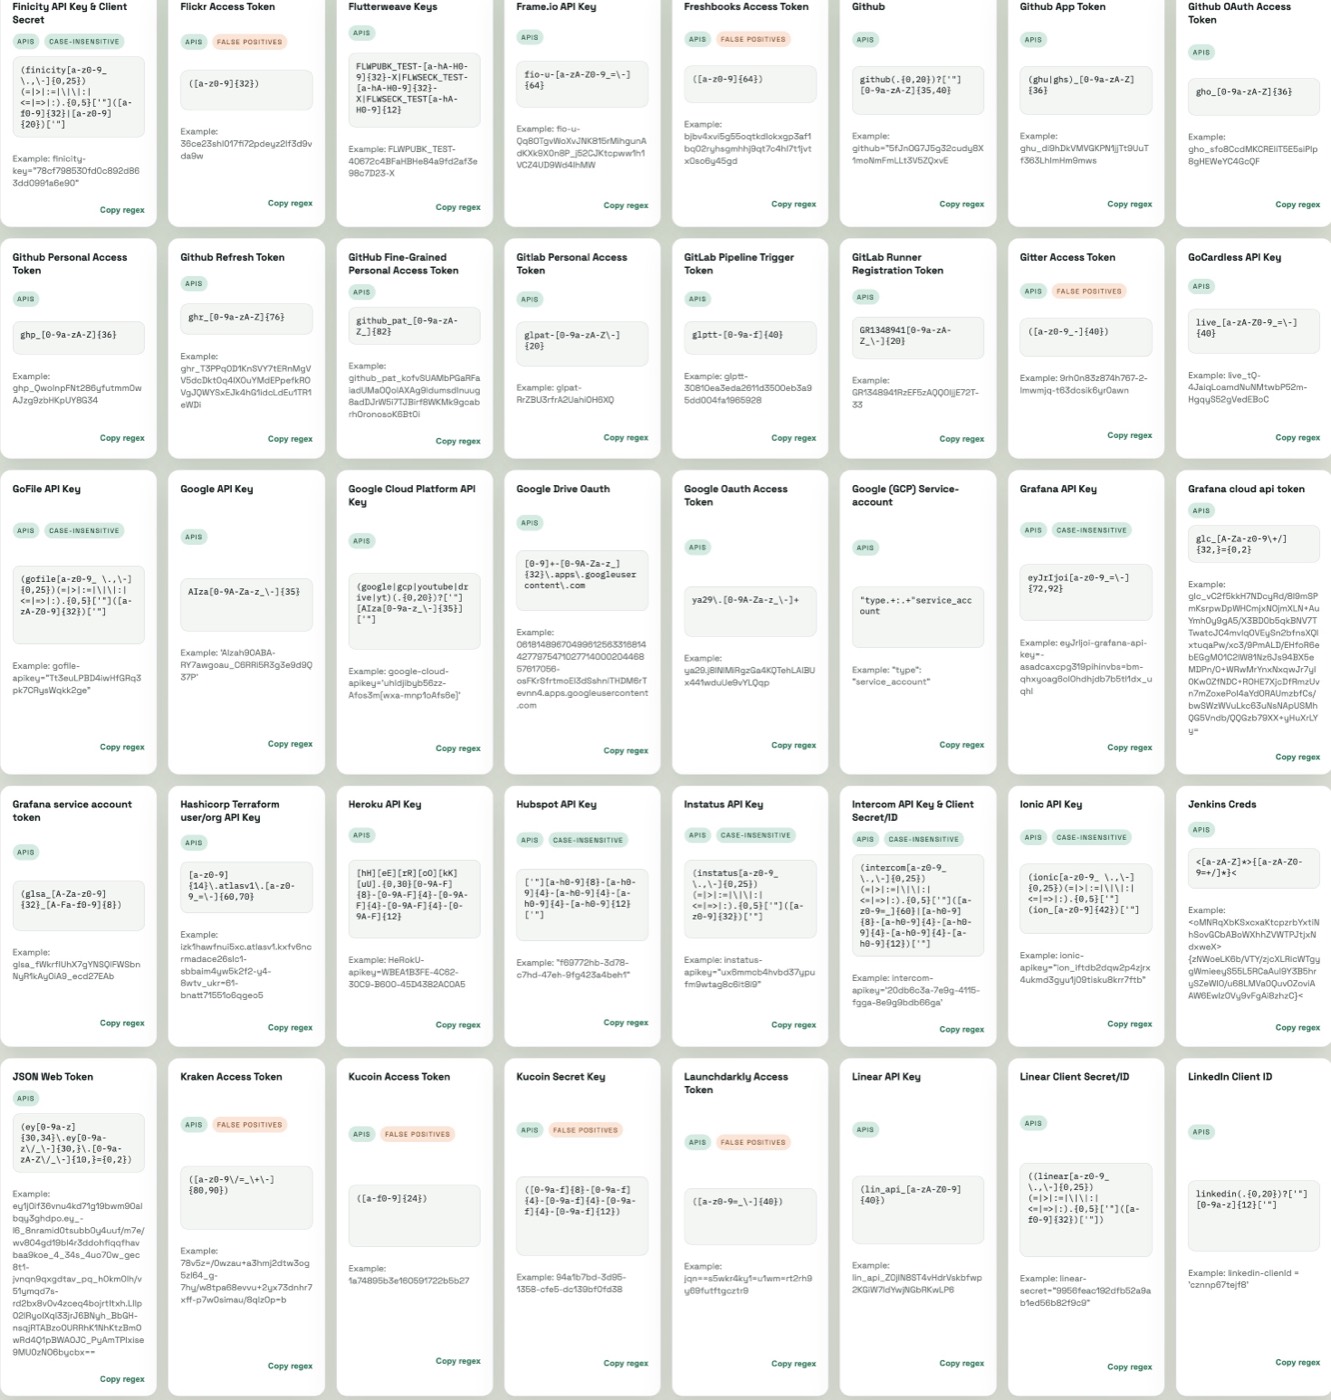 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.
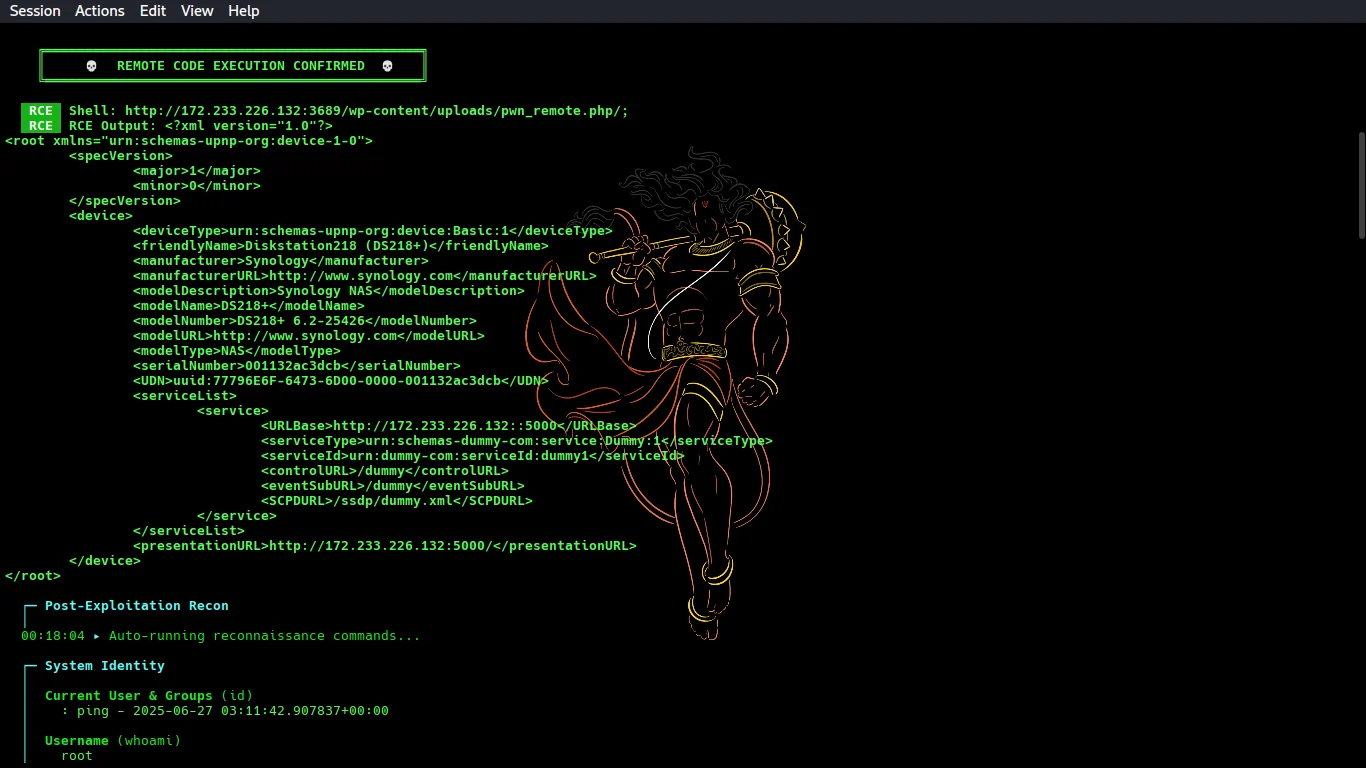 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
 numanturle/cve-2025-25279
Proof-of-concept for CVE-2025-25279: path traversal in Mattermost Boards allows arbitrary file read via crafted import archive and board duplication.
 doany1/cve-2026-24849
Proof-of-concept exploit for CVE-2026-24849, an authenticated path-traversal arbitrary file read in OpenEMR's EtherFax module. Reads server files…
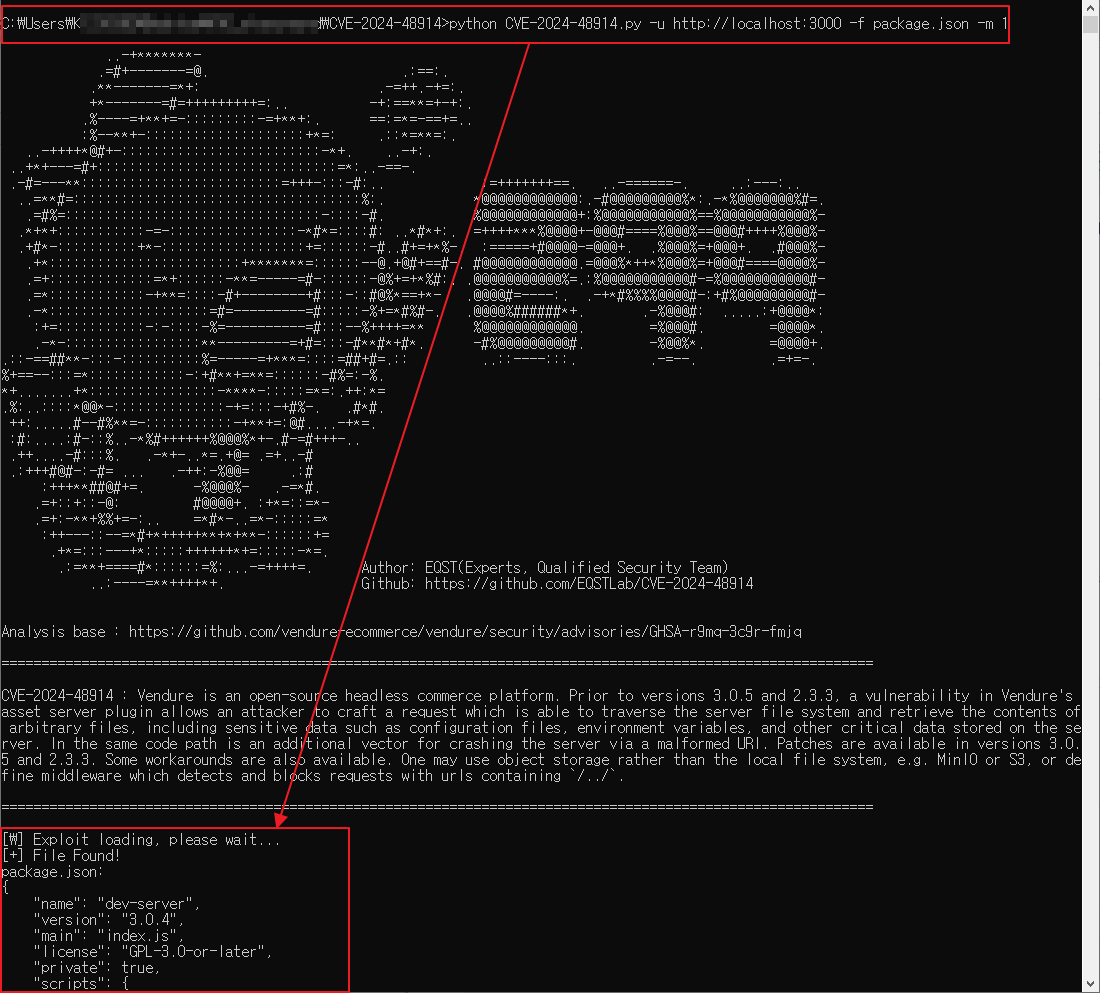 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 l0lsec/cve-2021-26837
CVE-2021-26837 - SQL Injection in the SearchTextbox parameter of HelpSystems/Fortra DeliverNow. Payloads, annotated requests, and evidence. Fixed in…