
LangAlpha
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
crawlerdata-exfiltrationinformation-gathering+6
1.8k
ginlix-ai/langalphaAutomated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 rndinfosecguy/scavenger
Crawler (Bot) searching for credential leaks on paste sites.
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 brigadeops32/cve-2026-85706
Python PoC exploiting CVE-2026-85706, an unauthenticated path traversal and arbitrary file read in GitLab CE/EE via the create-commit endpoint, with…
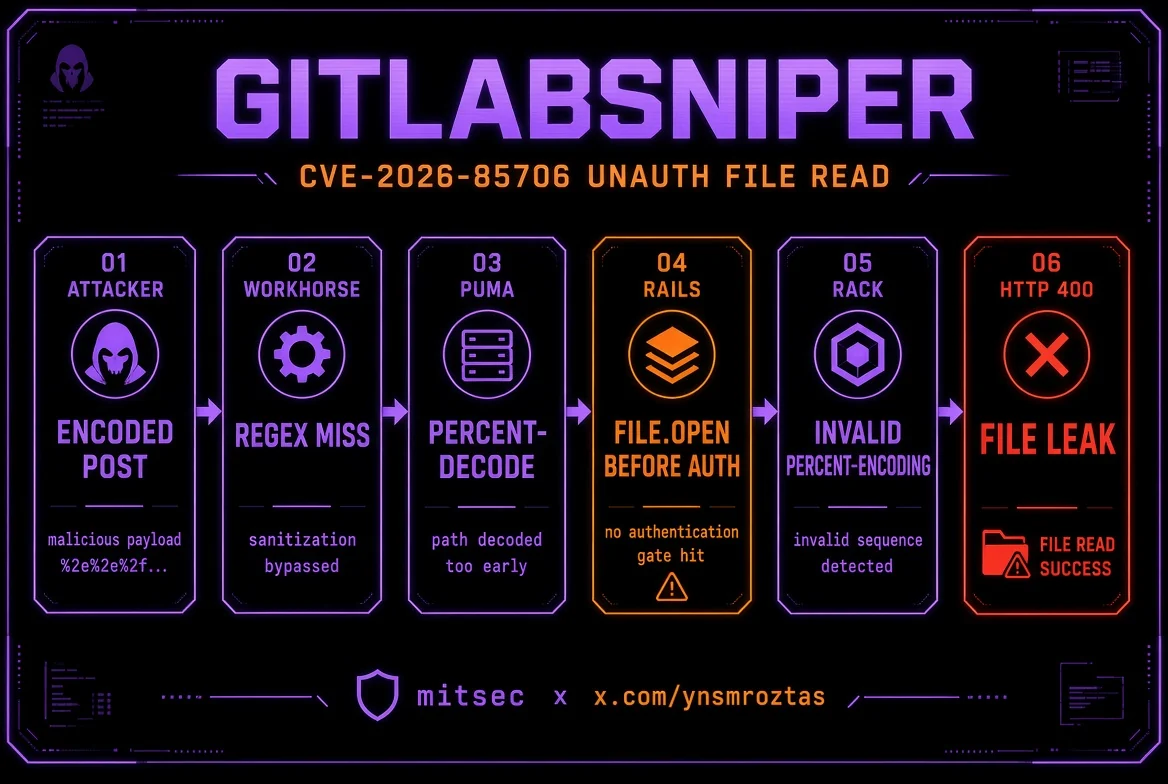 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 solivaquaant/cve-2026-85706-poc
PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 soxoj/telegram-bot-dumper
🔪 Dumper & ripper for Telegram bots by token. Forensic CLI tool with web interface
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
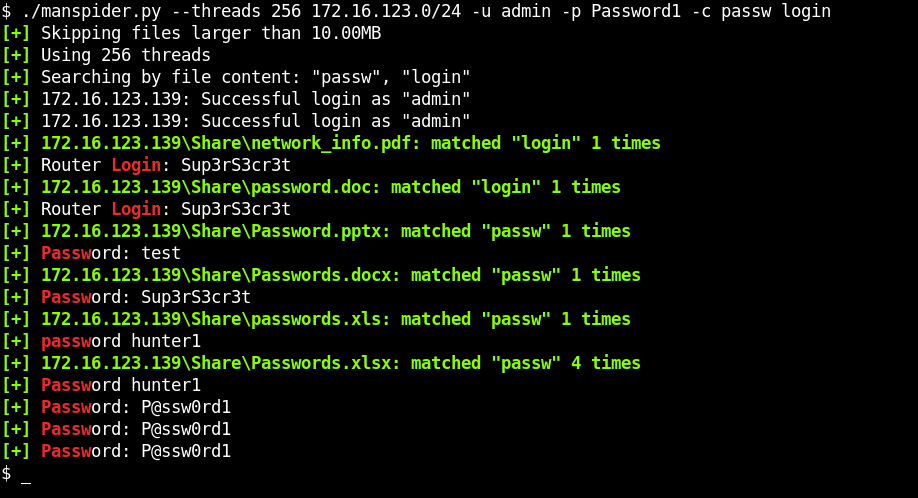 blacklanternsecurity/manspider
Spider entire networks for juicy files sitting on SMB shares. Search filenames or file content - regex supported!
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 abdugafforov-bobur/cve-2026-72550-poc
CVE-2026-72550 — Friendica Unauthenticated Stacked-Query SQL Injection PoC (CVSS 9.8 Critical)
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 majpuv/flowise-arbitrary-file-read-getfilefromstorage
Unauthenticated arbitrary file read in Flowise (< 2.2.4) via path traversal in getFileFromStorage (storageUtils.ts). Caused by un-sanitized file path…