
presidio
 data-privacy-stack/presidio
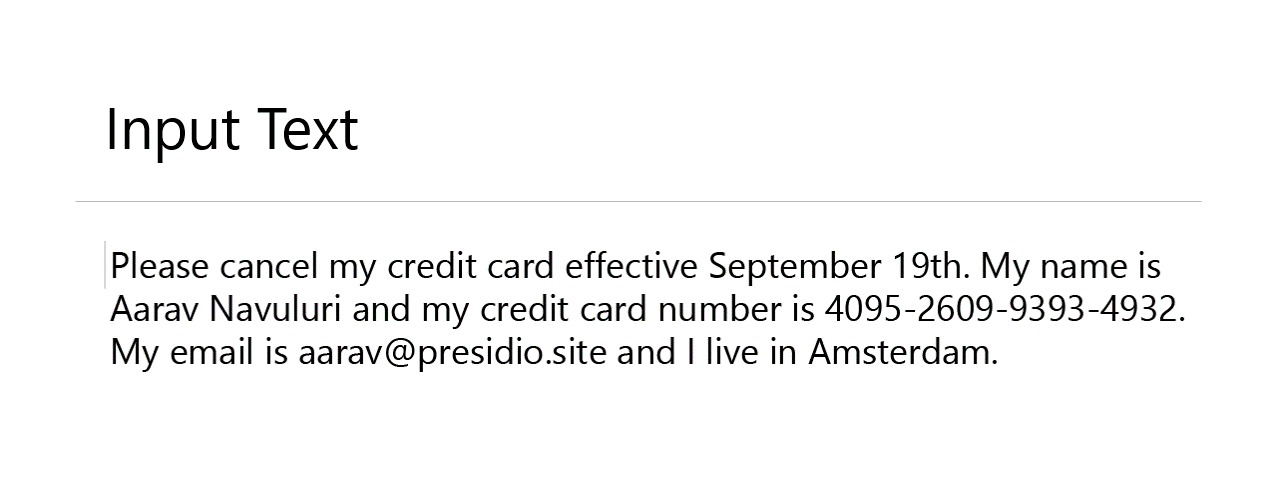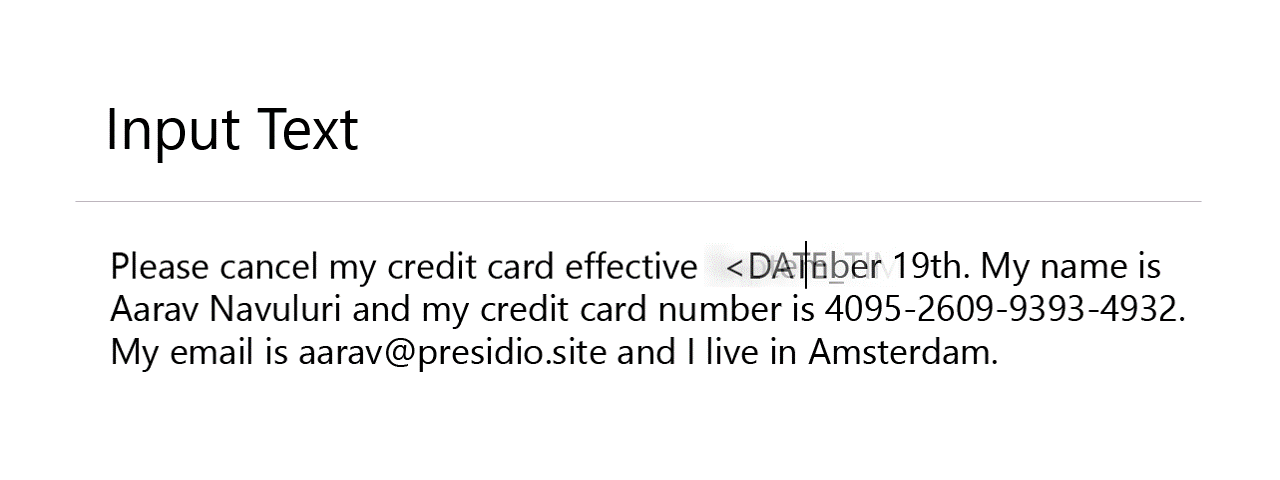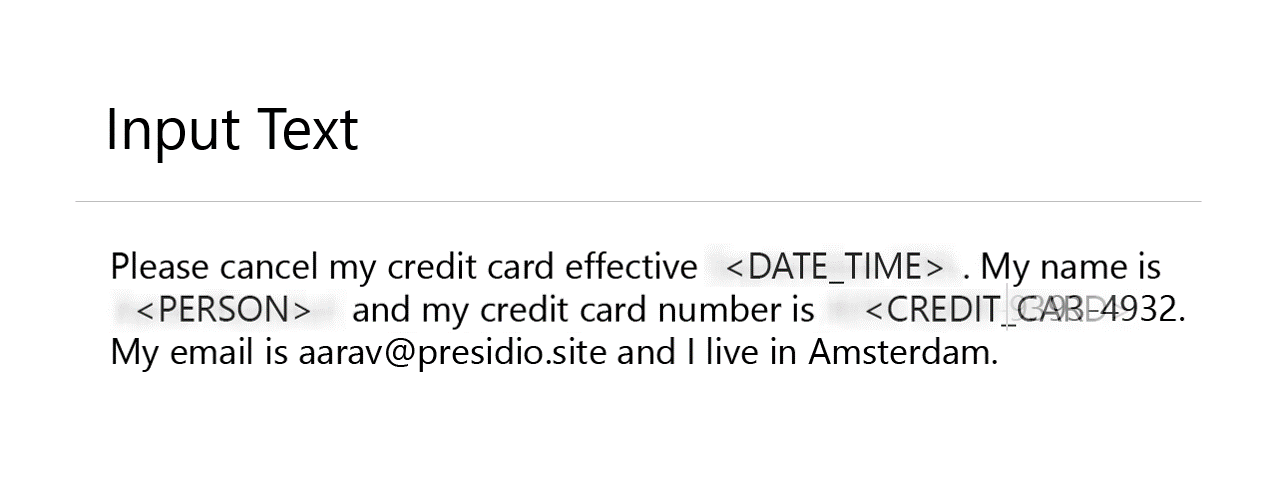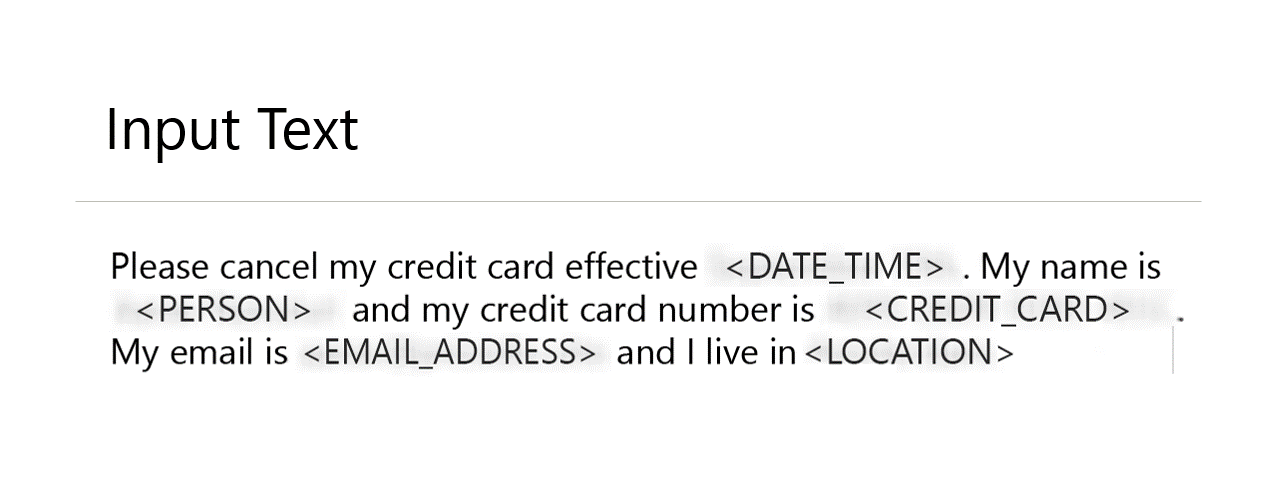
An open-source framework for detecting, redacting, masking, and anonymizing sensitive data (PII) across text, images, and structured data. Supports…
curated-resourcesdata-exfiltrationeducation+3
11.6k
data-privacy-stack/presidioAn open-source framework for detecting, redacting, masking, and anonymizing sensitive data (PII) across text, images, and structured data. Supports…
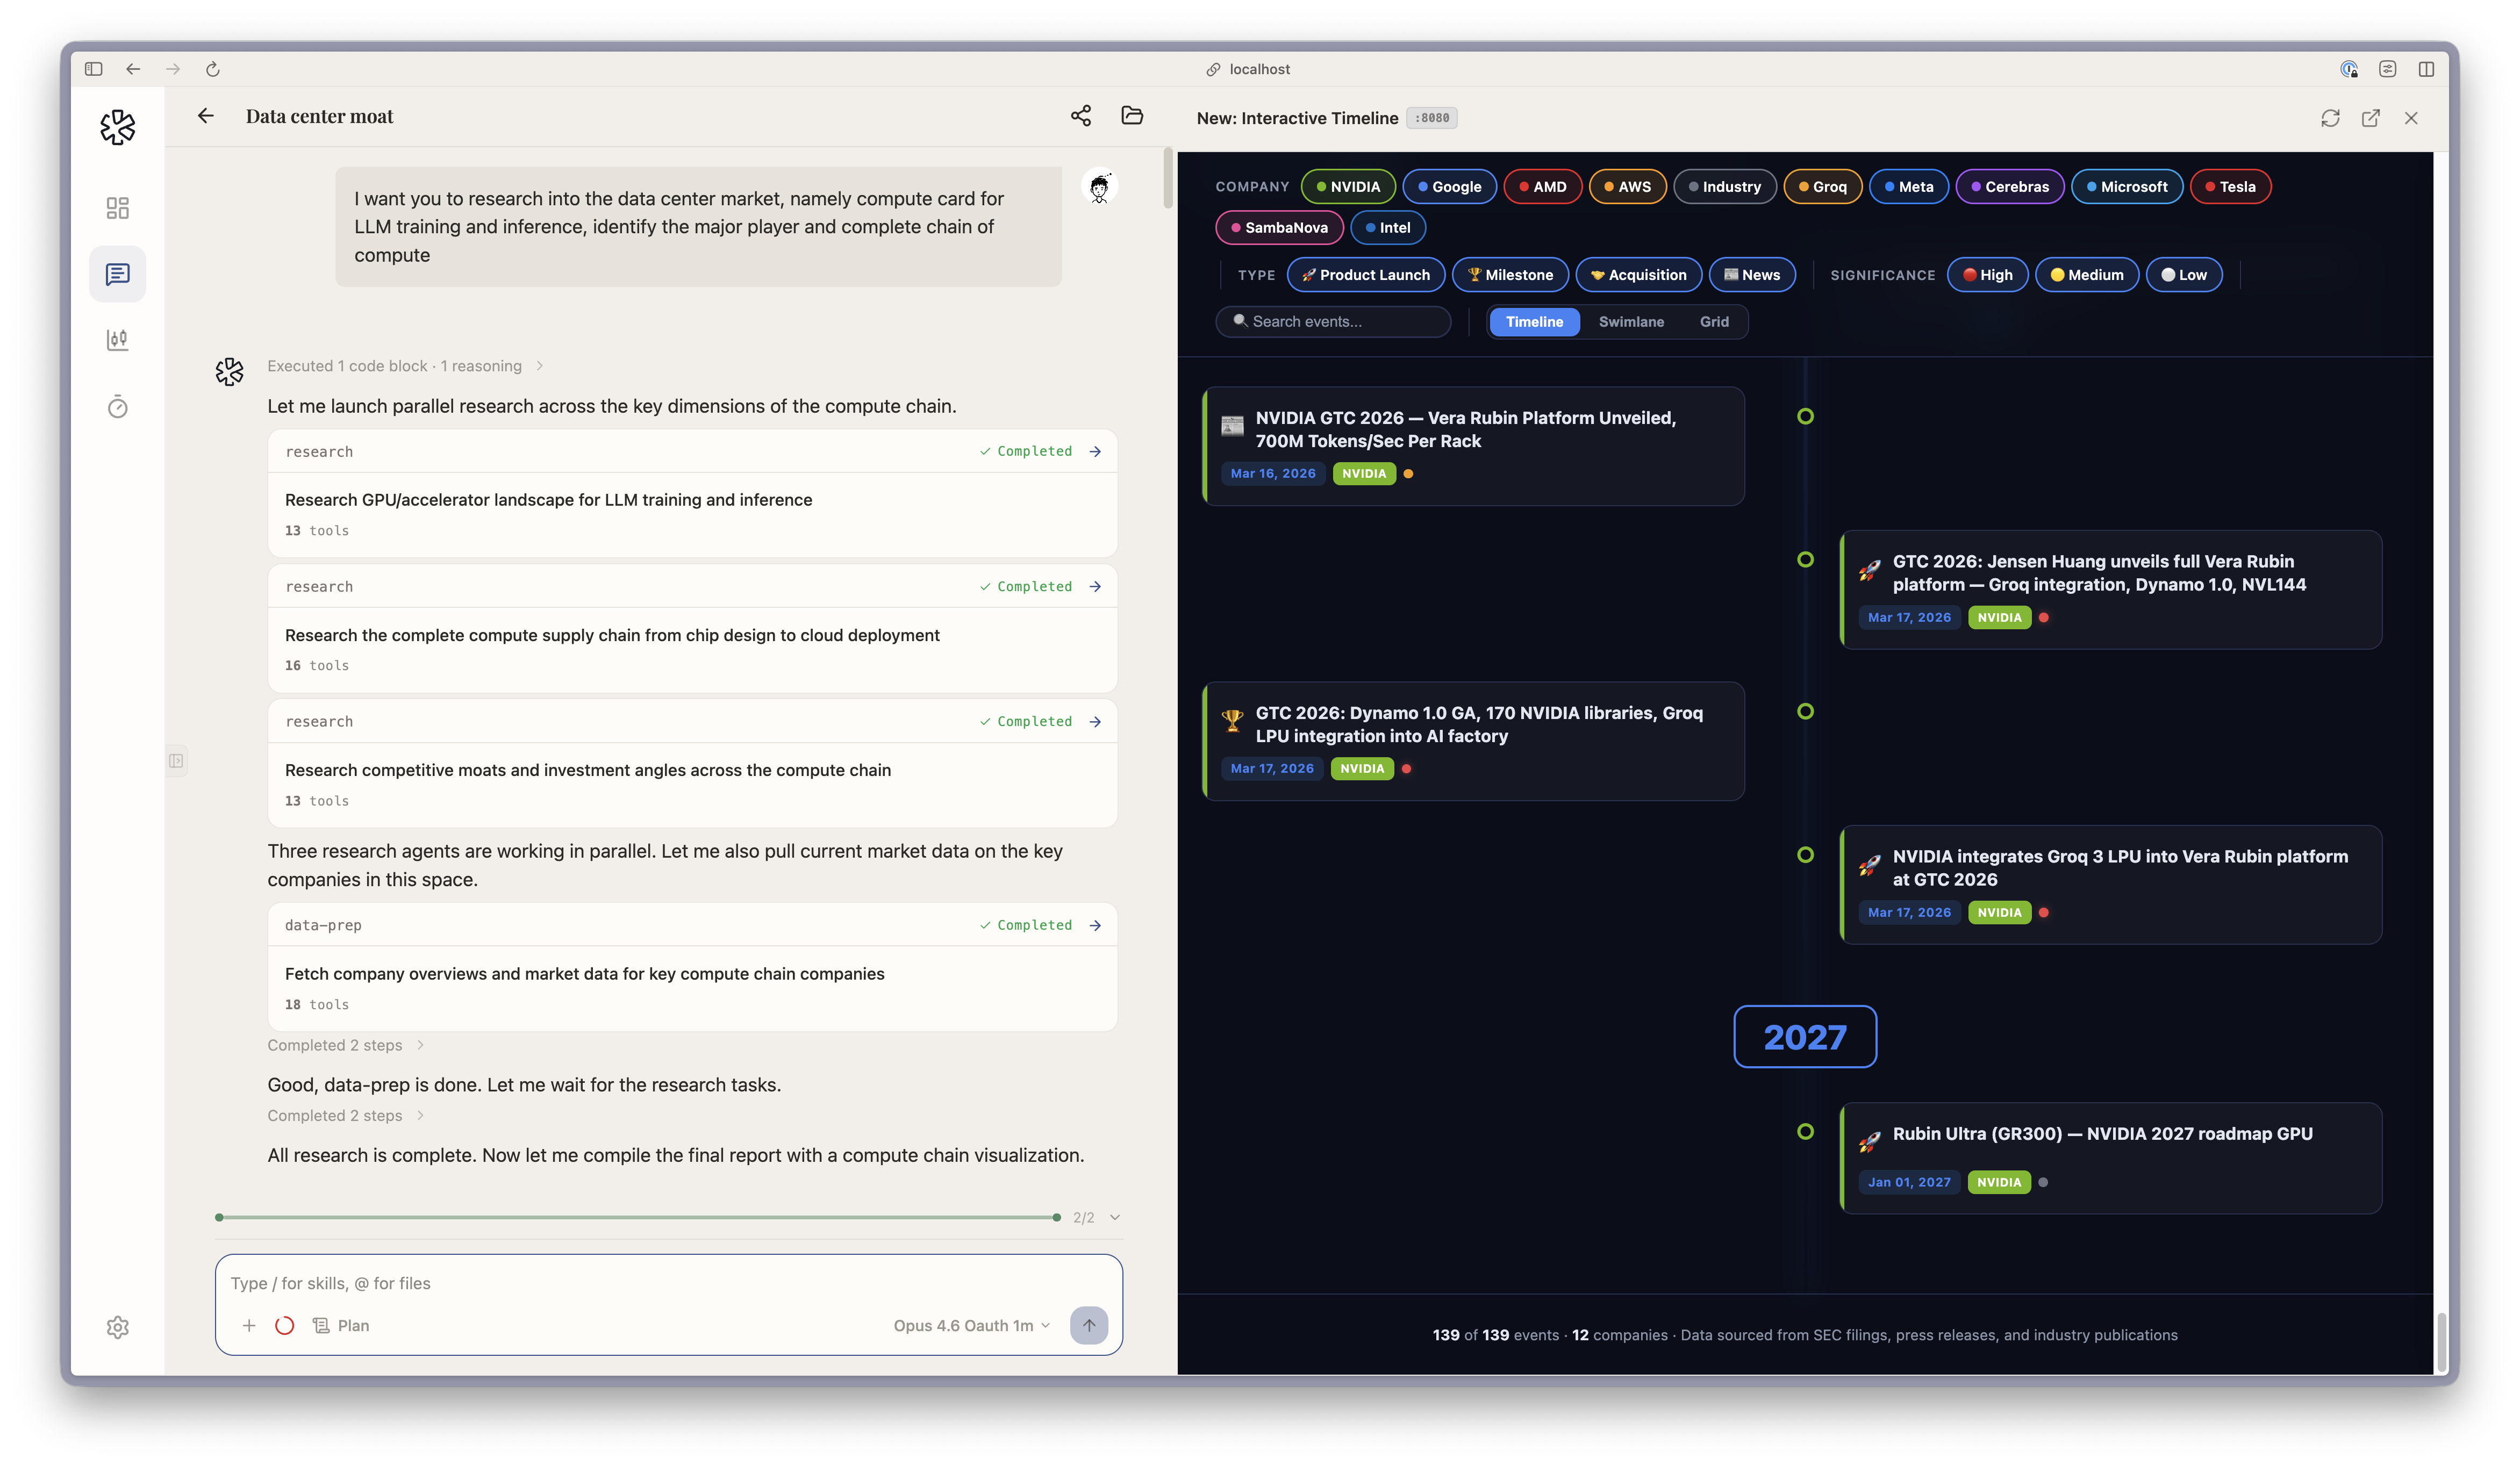 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
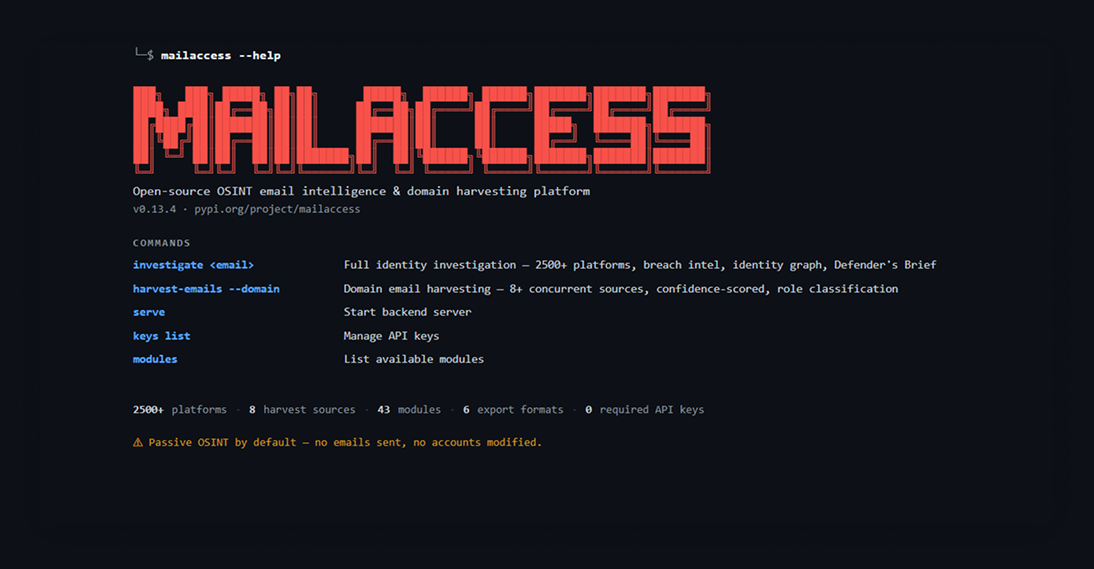 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 abraxas/pfsense-api-acb-userkey
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - ACB userkey capability URL
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 dutchcoders/transfer.sh
Easy and fast file sharing from the command-line.
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
 izcoser/stegpy
Simple steganography program based on the LSB method.