EXPLOIT-CVE-2026-33634

Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
cloud-securitycontainer-securitydata-exfiltration+7
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…

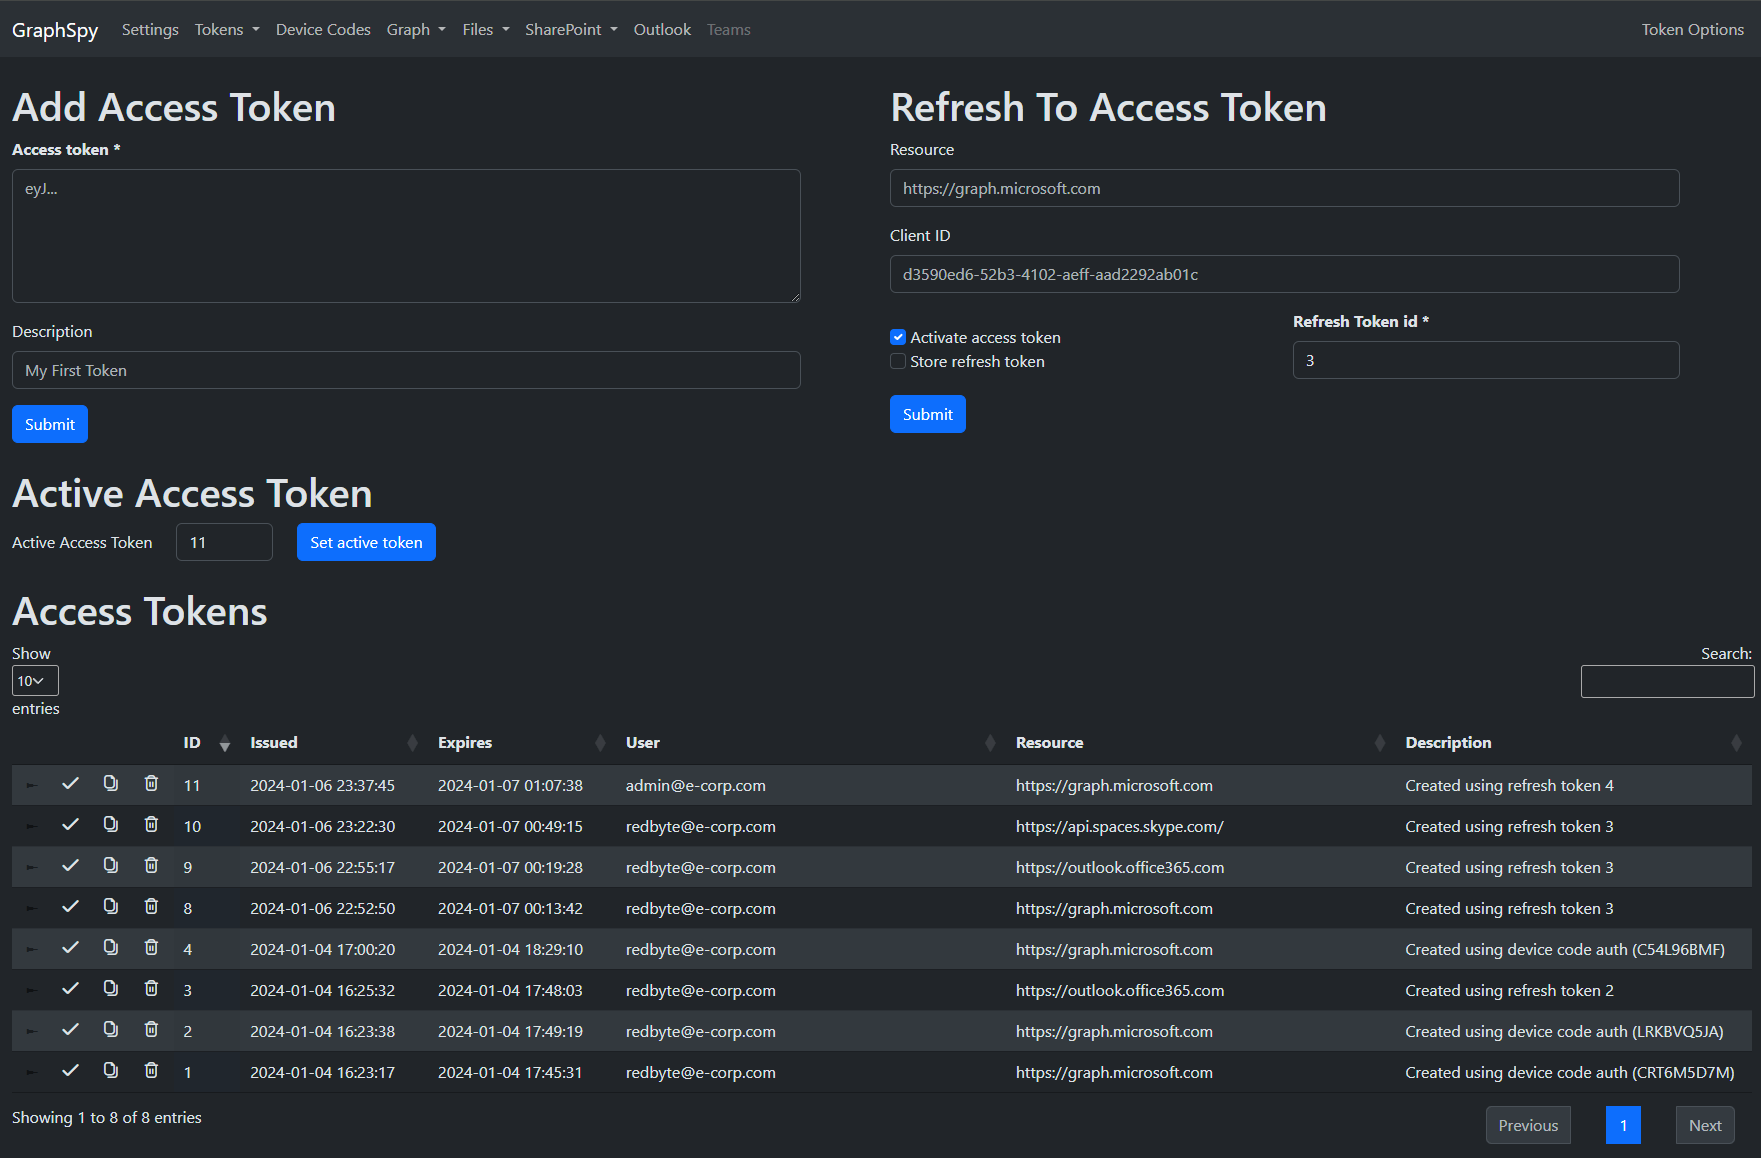
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI

Consul Template validated where a symlink pointed during template evaluation, but its later dependency fetch read the original path. Retargeting the…