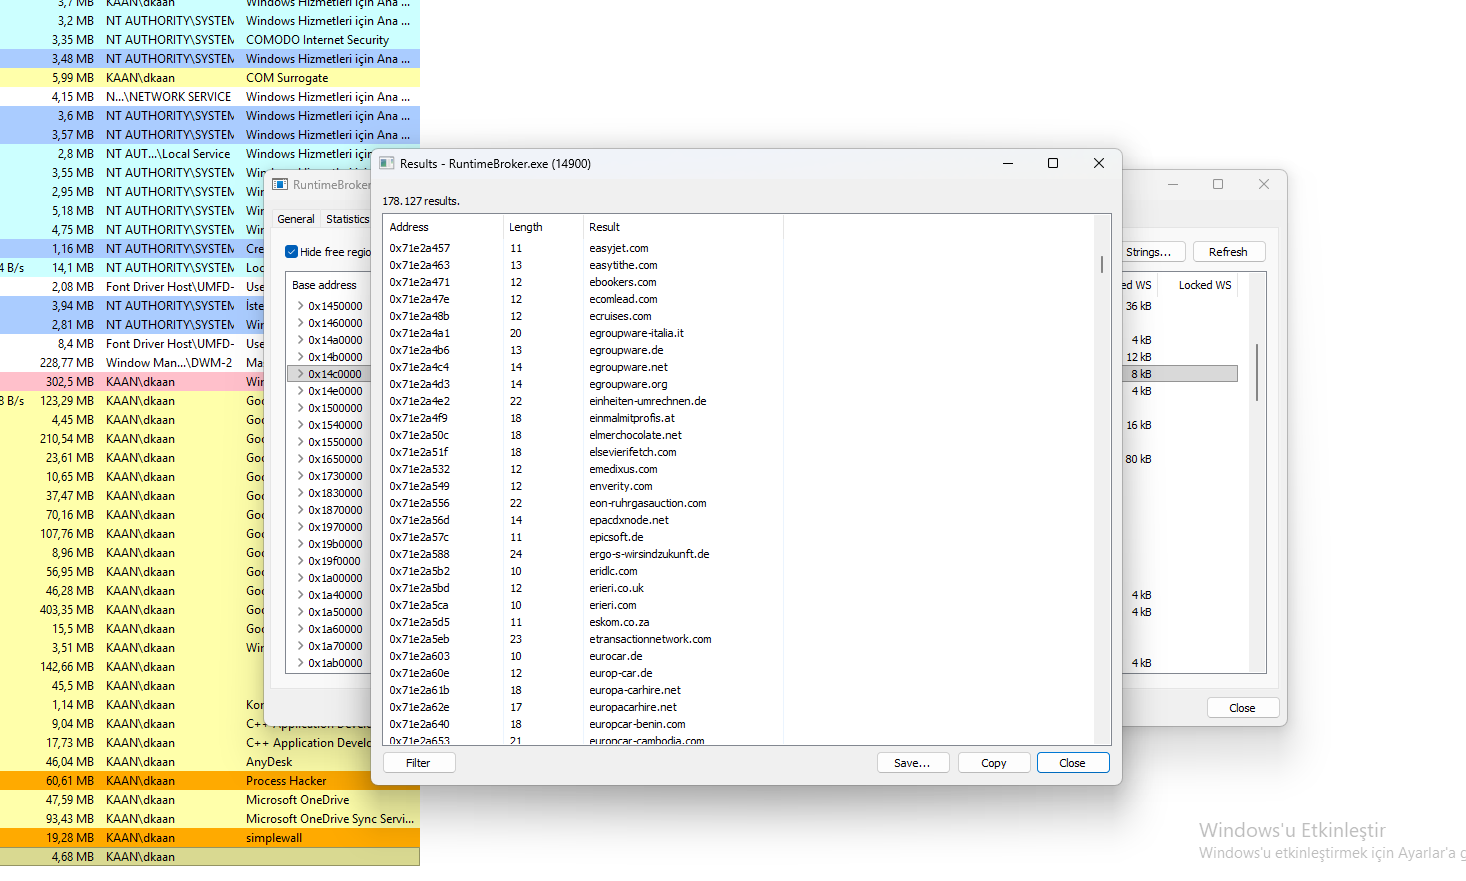
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…

A collection of selenium tests that might aid it takeover of a selenium node

Azure Post Exploitation Framework

SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.


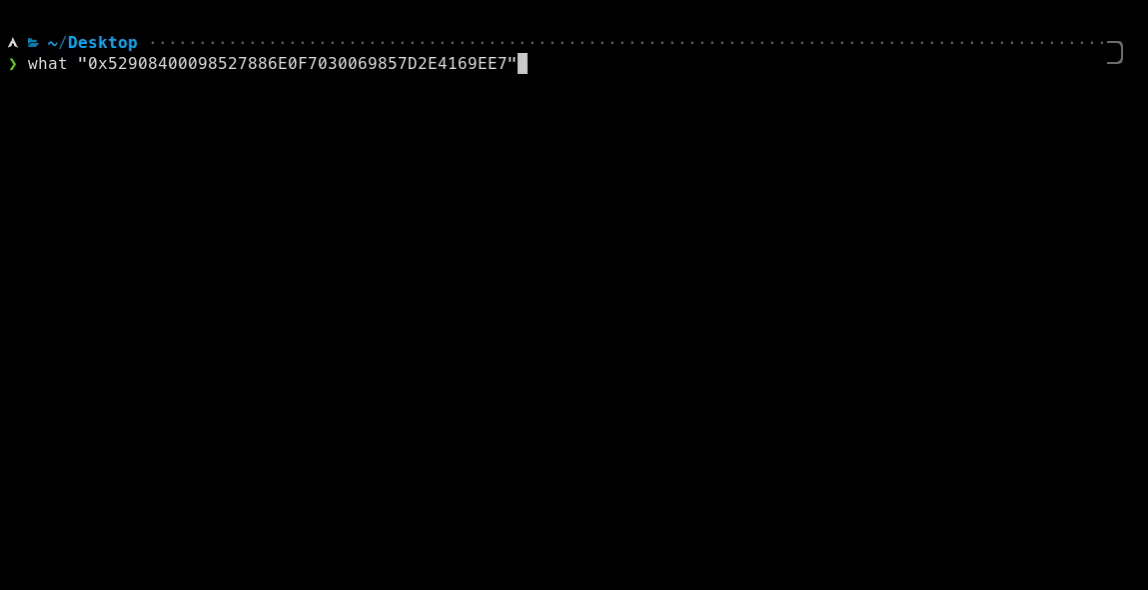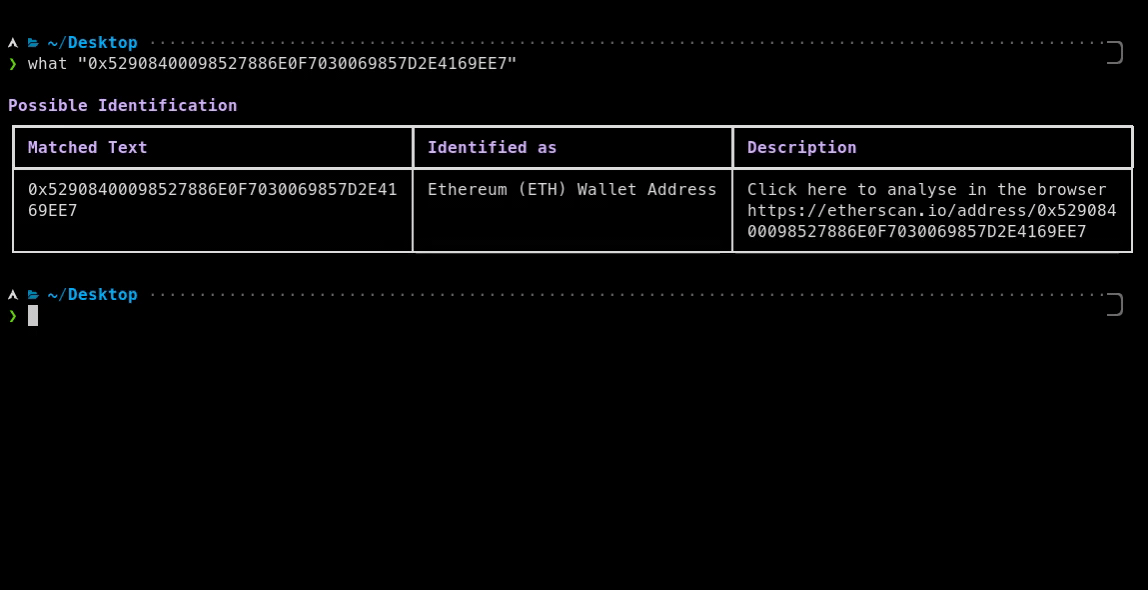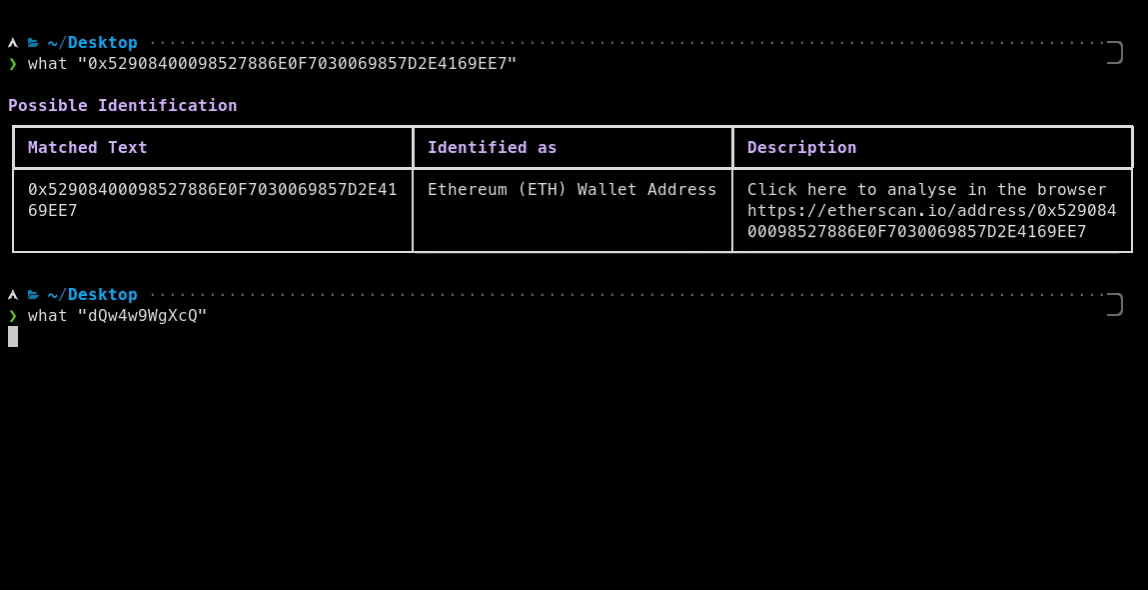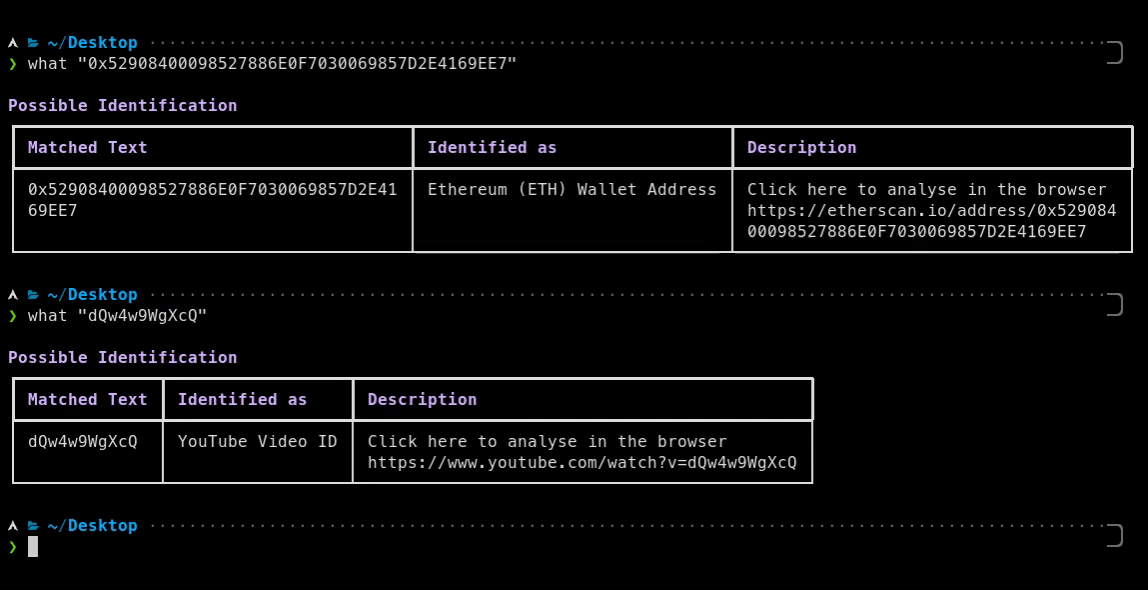
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…


WORK IN PROGRESS. RAT written in C++ using Win32 API

This tool queries the emails that registered the domain and verifies if they were leaked in some data leak.

some python3 functions to add spreading features to any python backdoor