
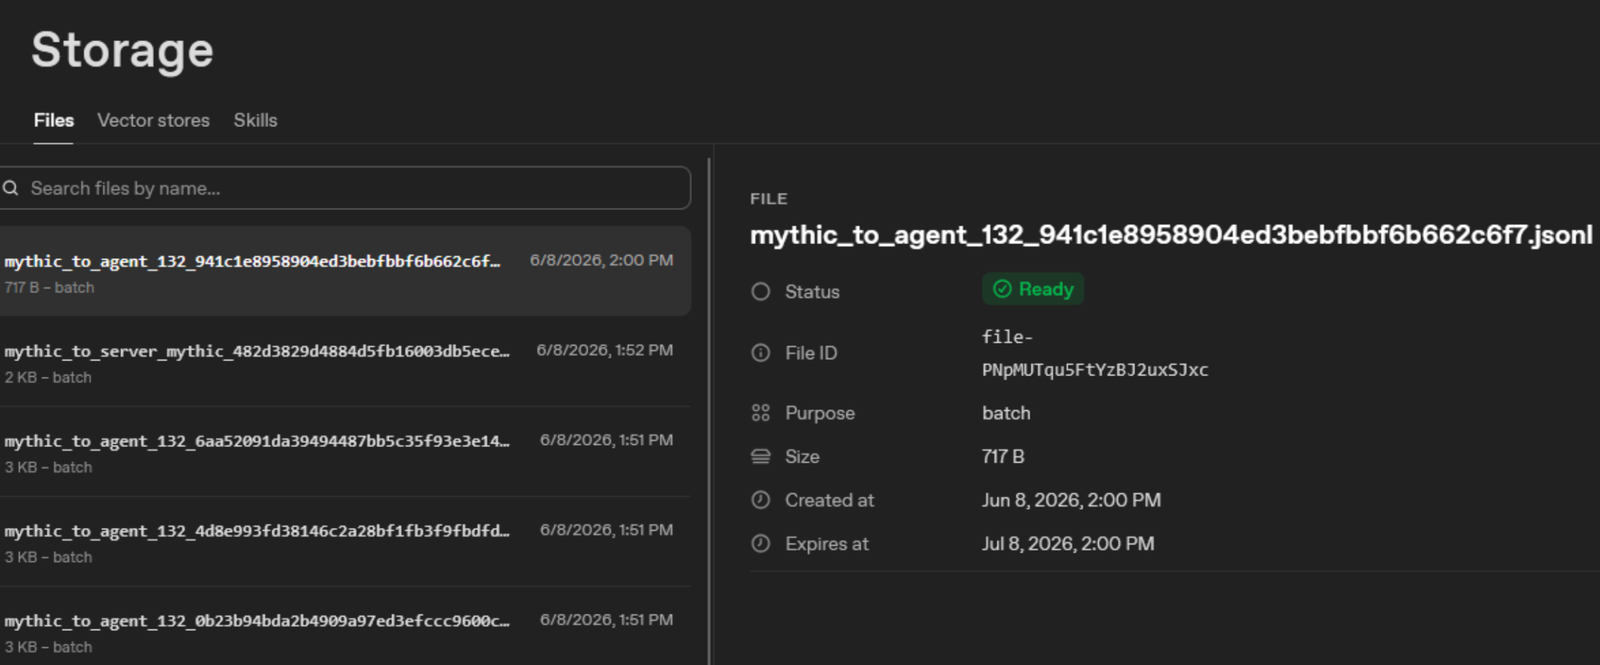
AI-FILE
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
ai-securitycommand-and-controldata-exfiltration+7
131 day ago
kyle41111/ai-fileA listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 kaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 imcpwn/browser-backdoor
BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener
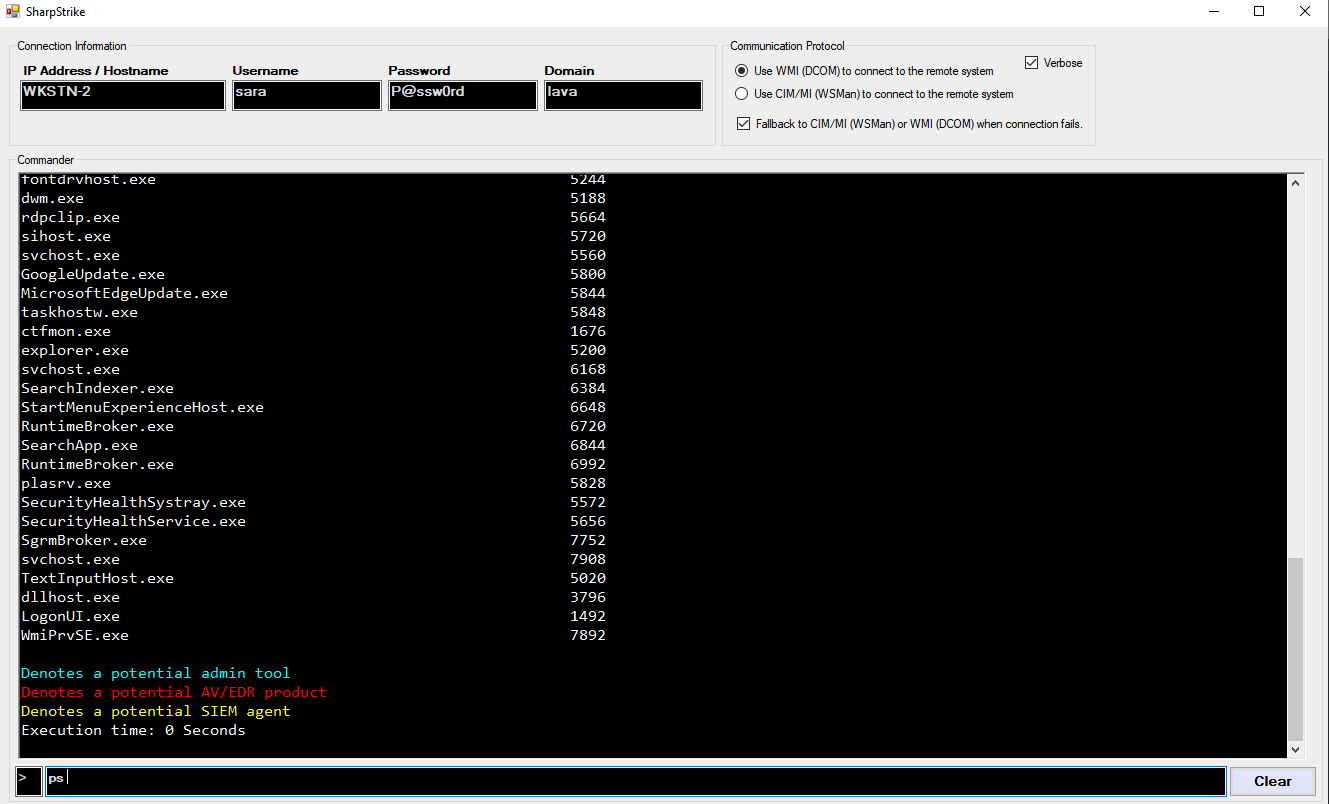 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 geeoon/dns-tunnel-keylogger
Keylogging server and client that uses DNS tunneling/exfiltration to transmit keystrokes through firewalls.