gitread
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
data-exfiltrationexploitationinformation-gathering+7
2
plur1bu5/gitreadCVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
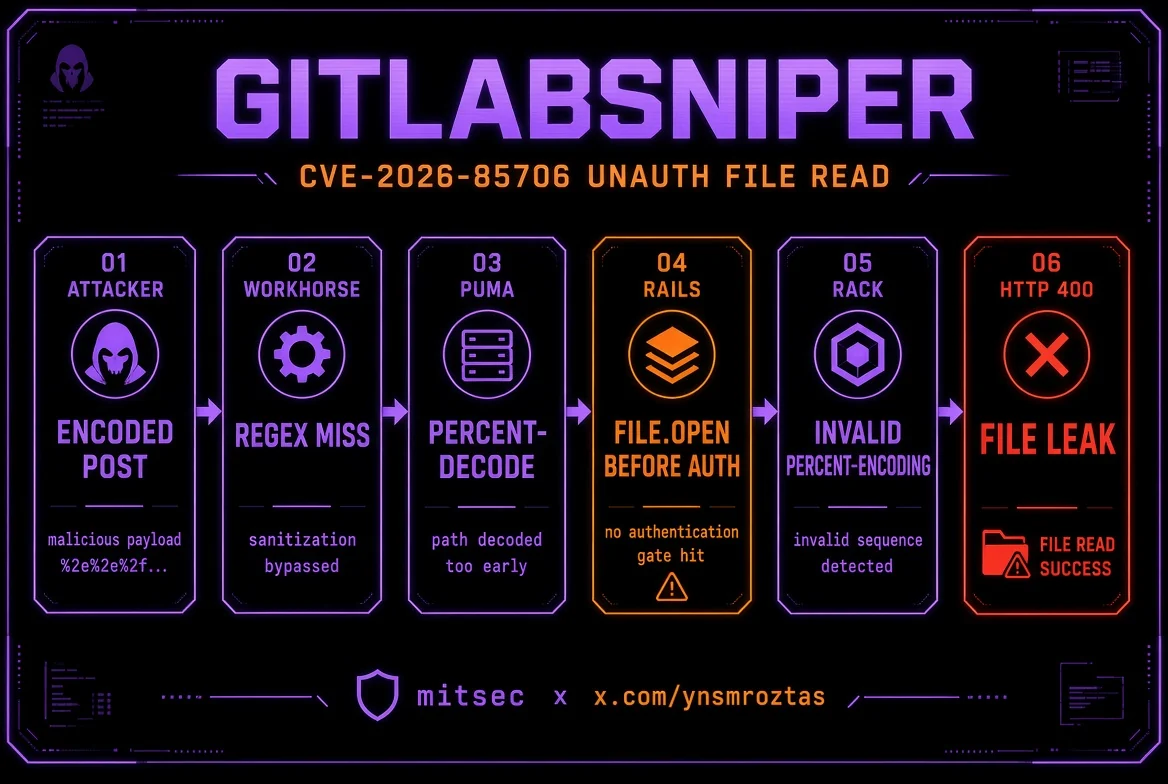 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 davidrxchester/cve-2026-5530
Proof-of-concept exploit for CVE-2026-5530, an SSRF in Ollama's Pull/Push API, enabling internal endpoint enumeration and full response exfiltration…
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 shadowbq/pastenum
Pastenum is a text dump enumeration tool.
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
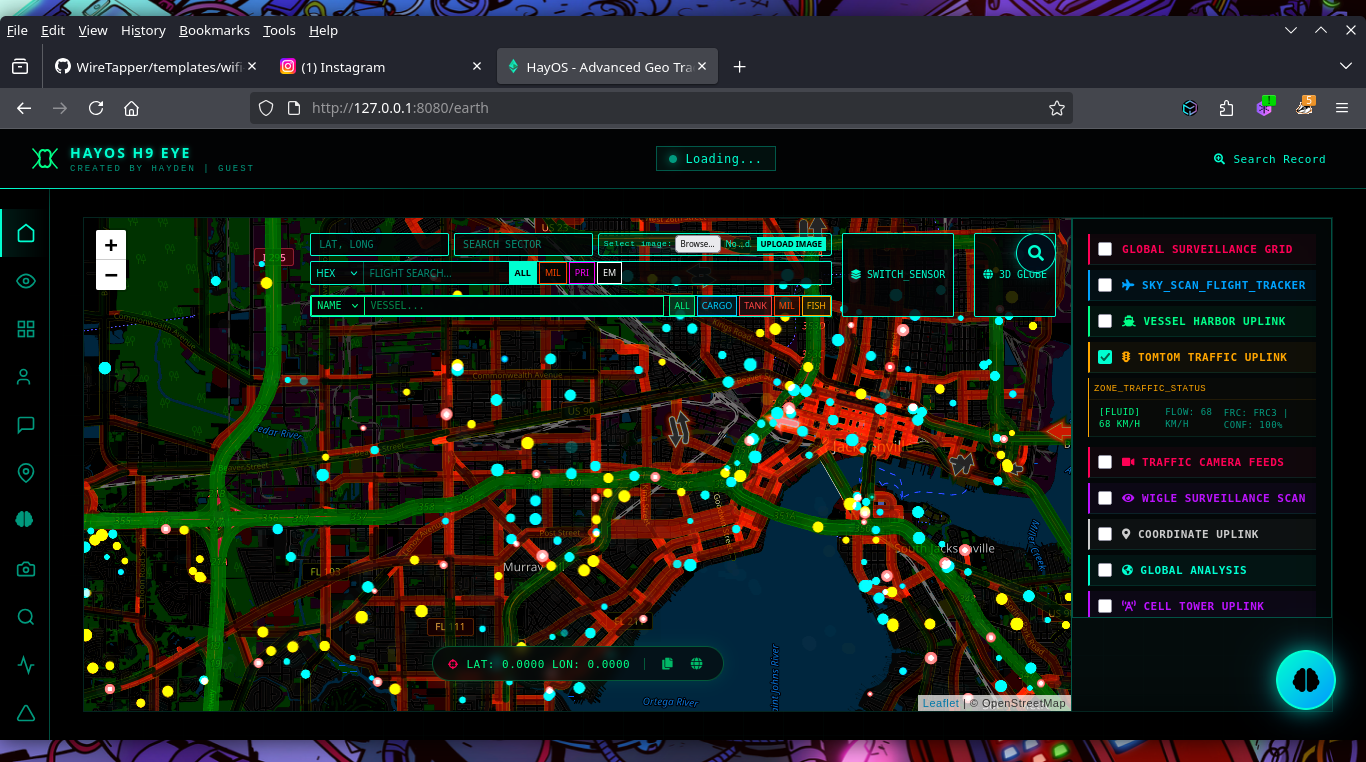 h9zdev/geosentinel
Real-time geospatial OSINT platform aggregating flight, vessel, and satellite data with dark web search, social media dorking, and AI-powered…
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
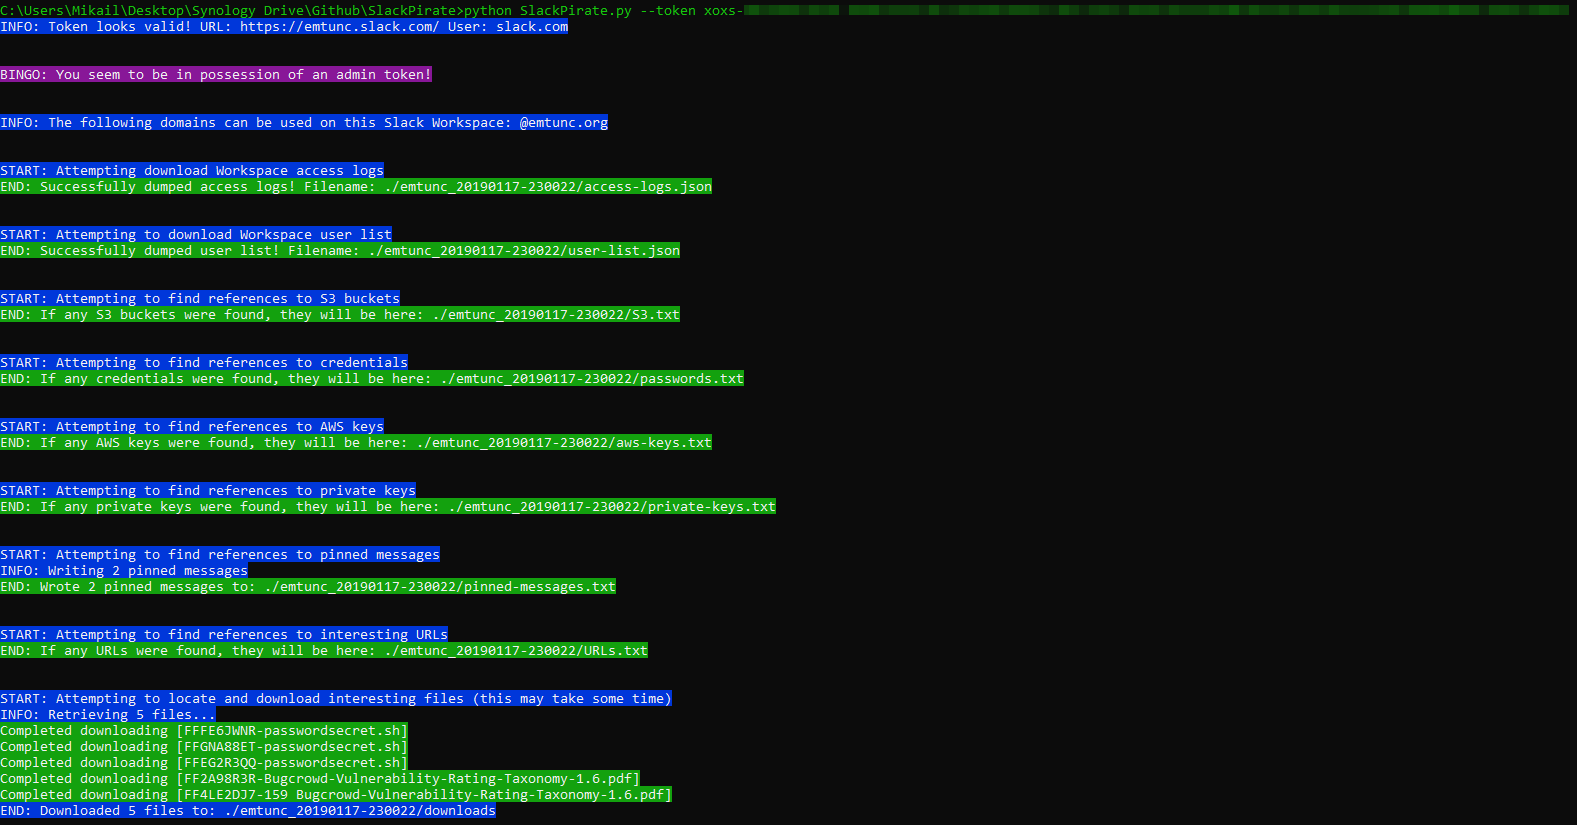 emtunc/slackpirate
Slack Enumeration and Extraction Tool - extract sensitive information from a Slack Workspace
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
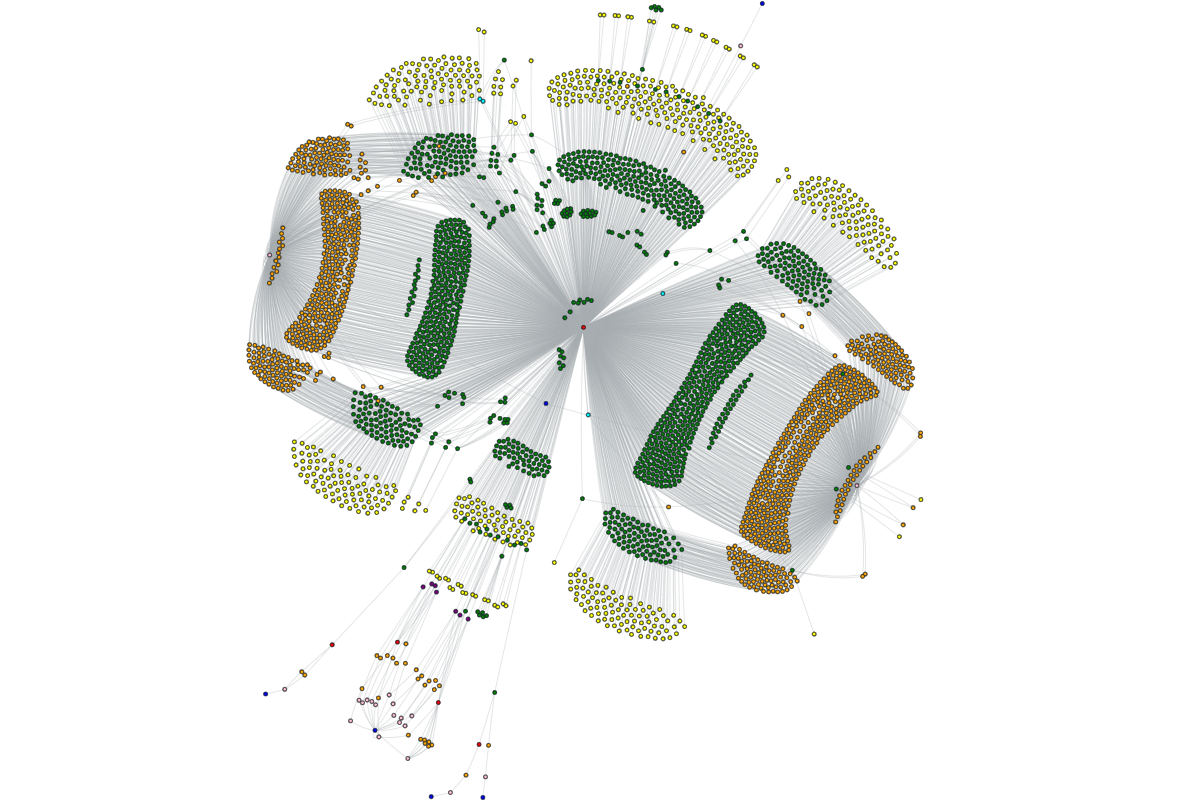 owasp-amass/amass
In-depth attack surface mapping and asset discovery