
bucketbuster
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
cloud-infrastructure-securitycloud-securitydata-exfiltration+6
ooafa/bucketbusterScans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 prox0959/spectralcovert
Detects network covert channels using Shannon entropy and Sarle's bimodality coefficient to flag encrypted ICMP/TCP payload exfiltration and…
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
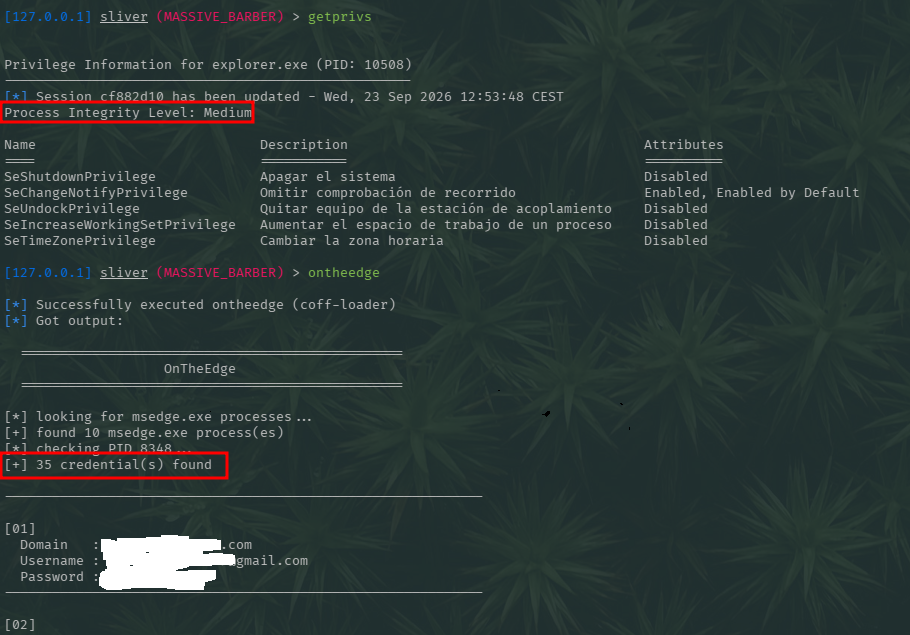 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 shadowforge-cyber/cve-2026-84388-poc
Improper Restriction of Rendered UI Layers or Frames (CWE-1021)
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 openai/privacy-filter
Bidirectional token-classification model for PII detection and masking in text, with CLI for redaction, evaluation, and finetuning on-premises.
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…