
CVE-2026-86259
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
api-securitycloud-securitydata-exfiltration+6
uziii2208/cve-2026-86259OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 monoxgas/mailorder
Nalpeiron Licensing Service (NLSSRV32) arbitrary disk read [CVE-2019-19315]
 dicanio/cve-2021-44228-docker-example
Docker-based demonstration of CVE-2021-44228 (Log4Shell) exploitation, featuring a vulnerable Java server, malicious LDAP server, and data…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 internetangel/zerocrumb
Dumping App Bound Protected Credentials & Cookies Without Privileges.
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
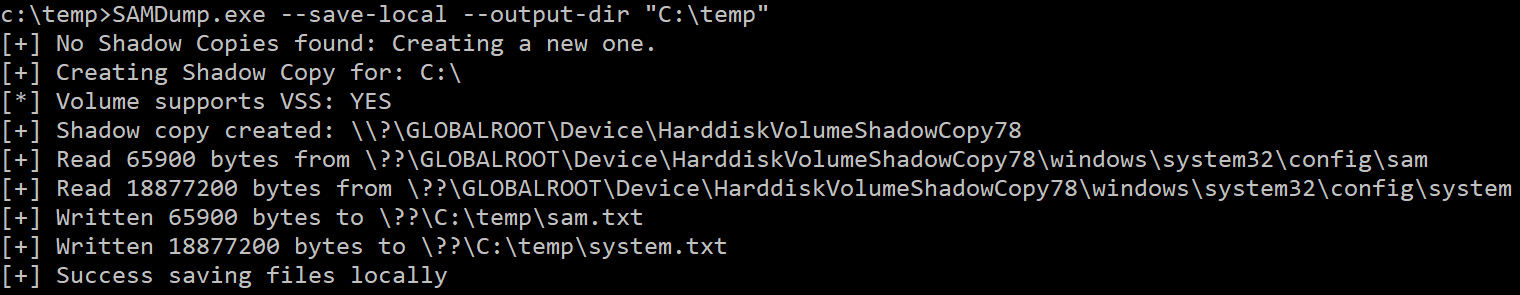 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search
 davidtavarez/pwndb
Search for leaked credentials
 jxlil/pwndb
Tor-based leaked credential search tool that queries the pwndb2 hidden service to find emails and passwords exposed in data breaches, with wildcard…
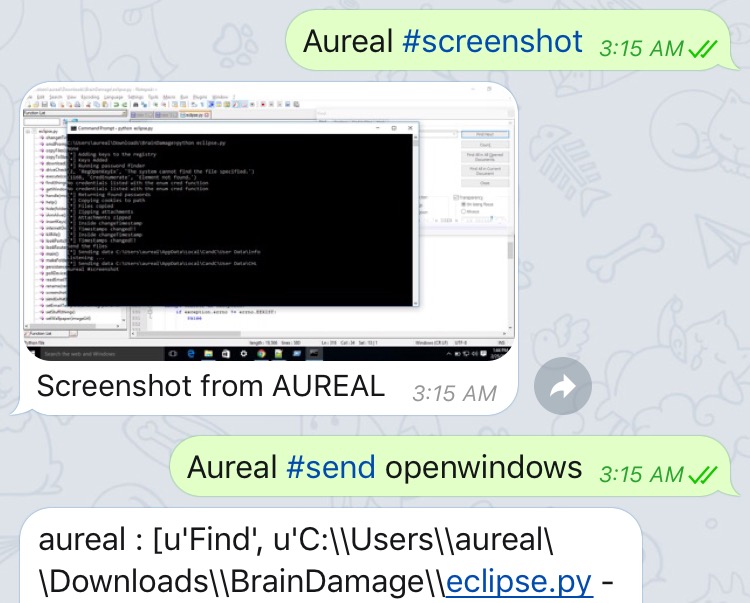 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server