

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
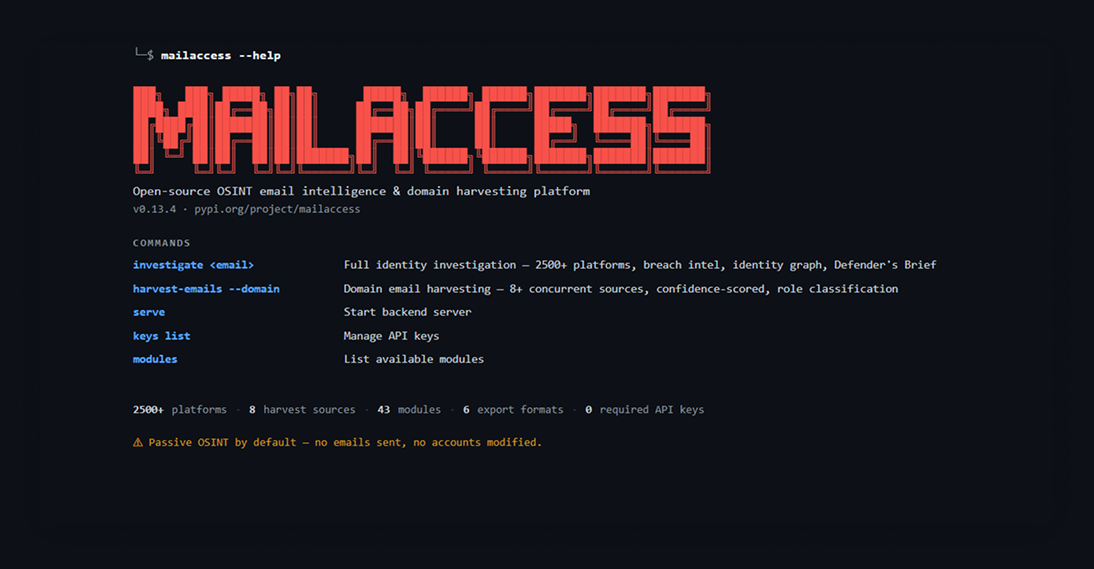 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
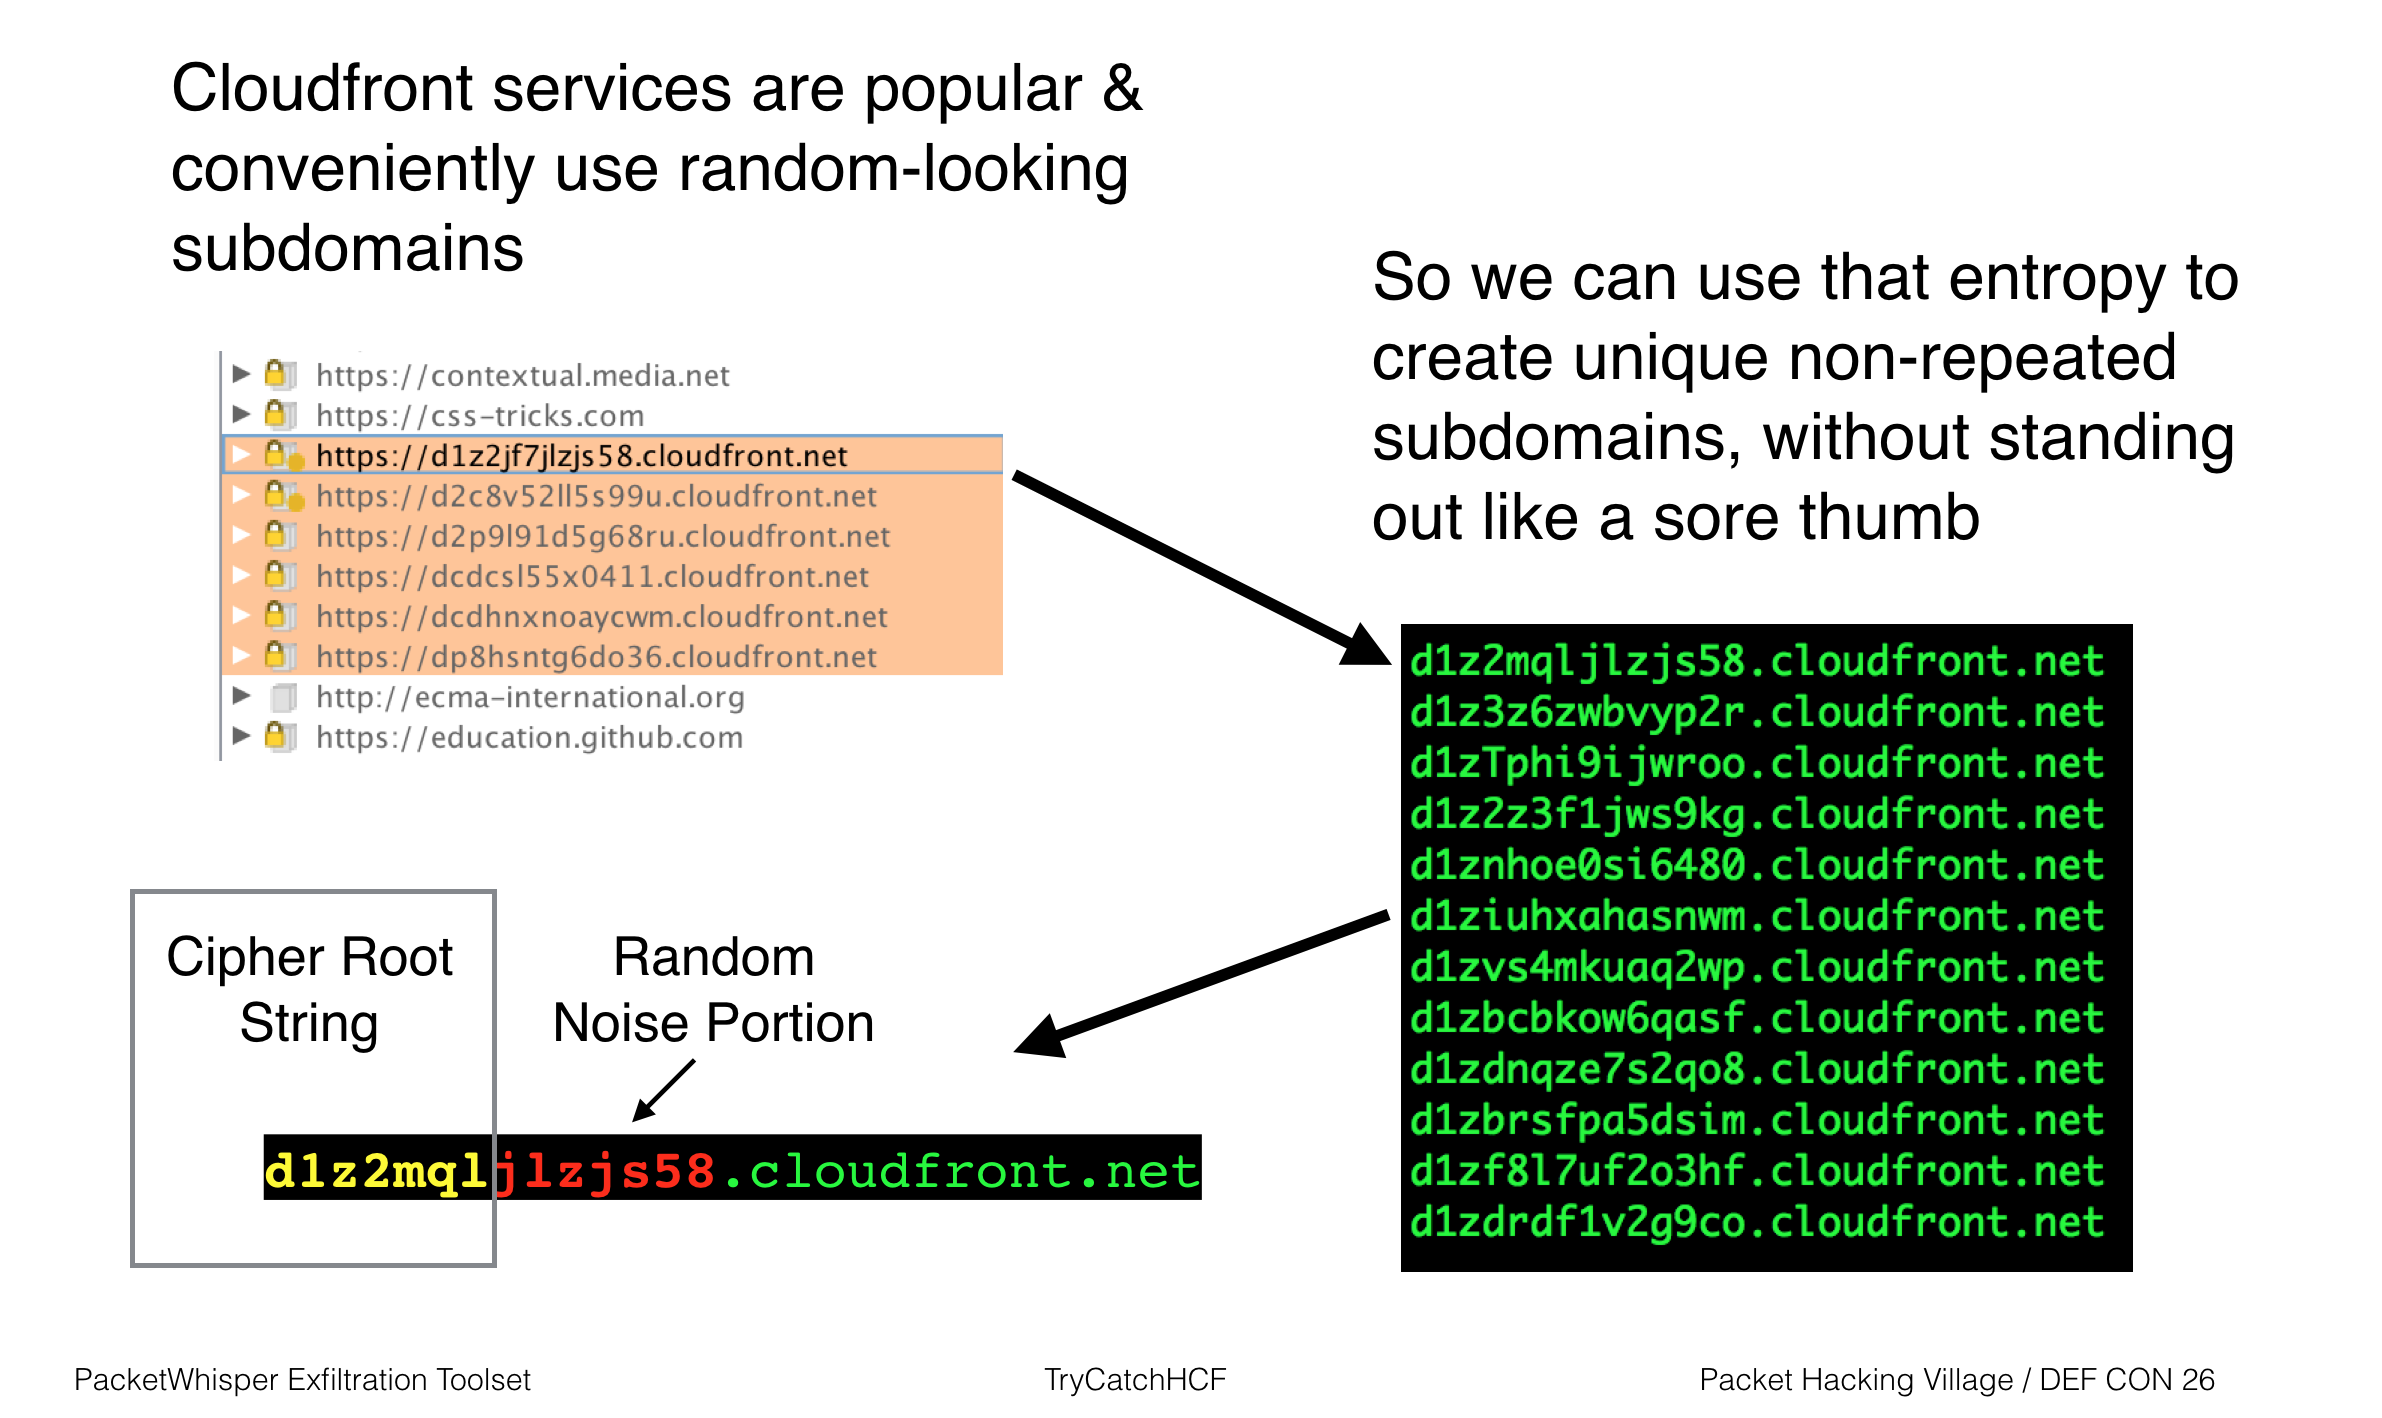 trycatchhcf/packetwhisper
PacketWhisper: Stealthily exfiltrate data and defeat attribution using DNS queries and text-based steganography. Avoid the problems associated with…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 nccgroup/onelogicalmyth_shell
A HTA shell to assist with breakout assessments.
 tarlogicsecurity/arecibo
Endpoint for Out-of-Band Exfiltration (DNS & HTTP)
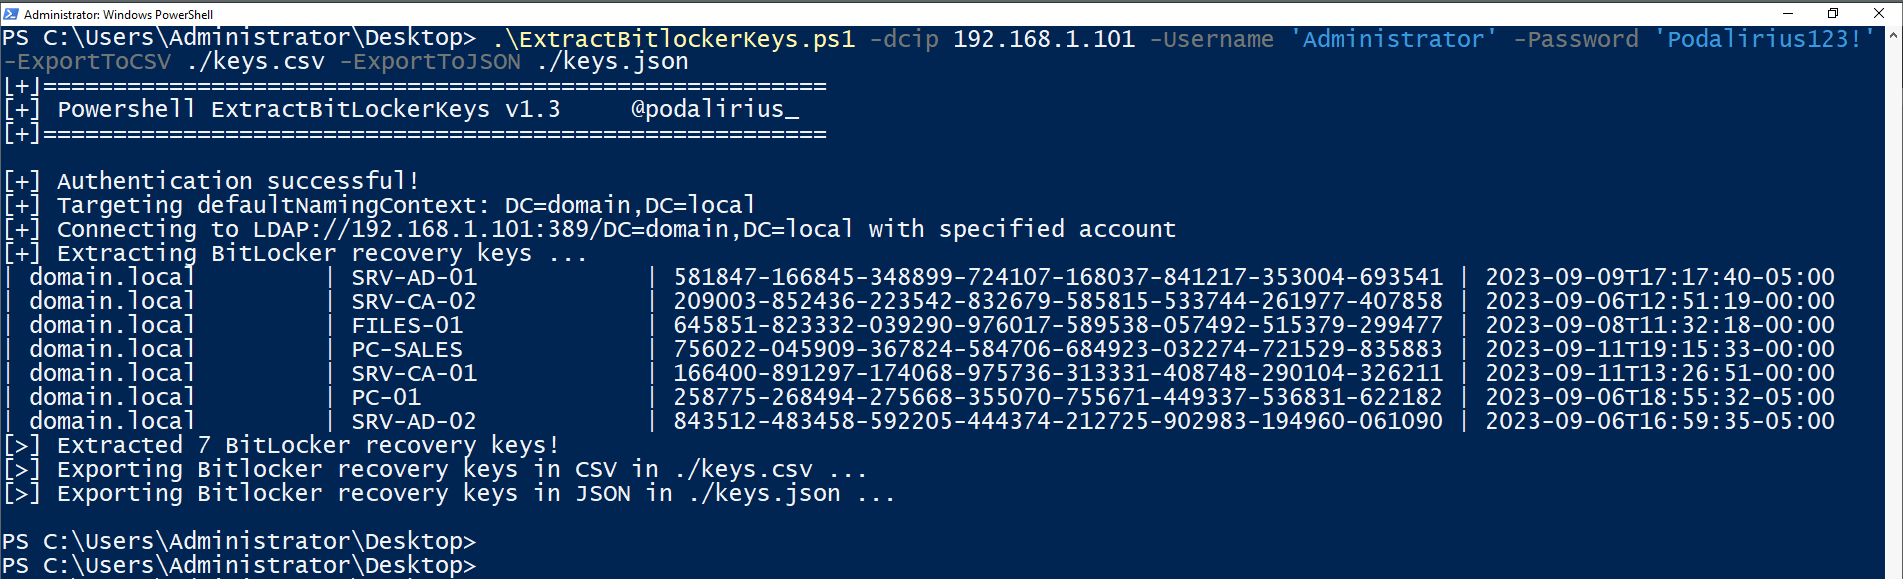 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
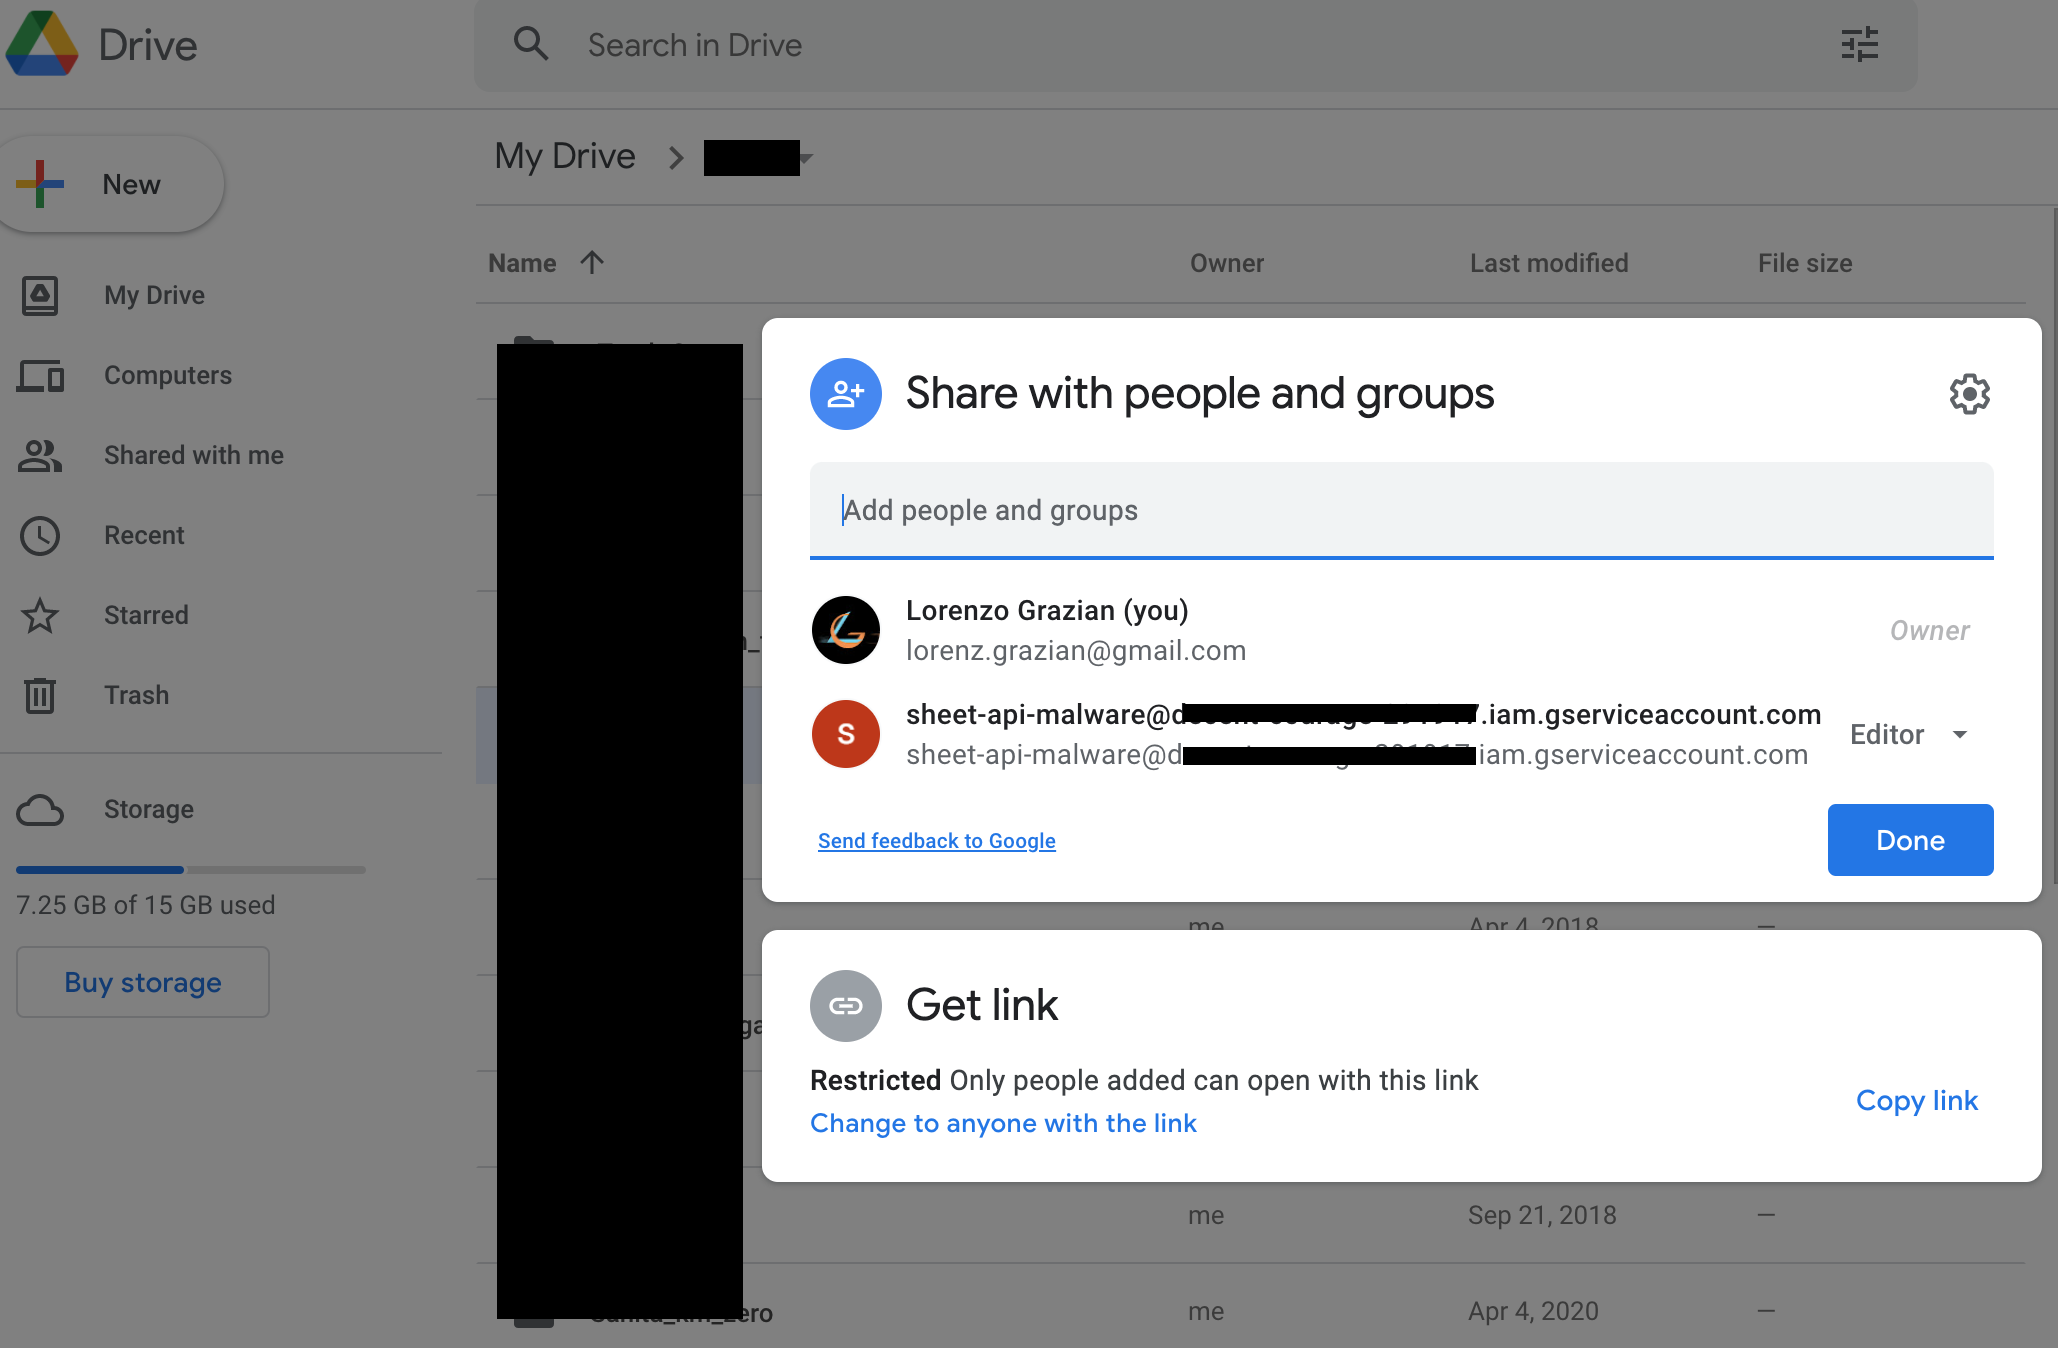 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
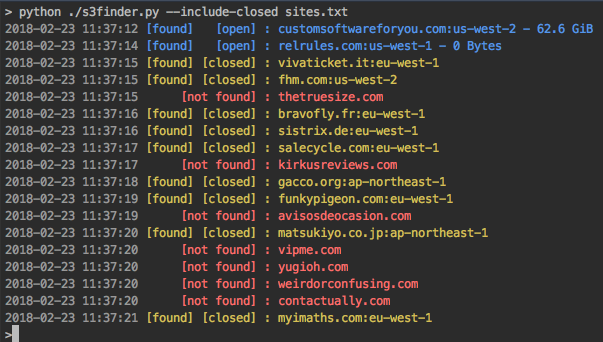 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 dvopsway/datasploit
A tool to perform various OSINT techniques, aggregate all the raw data, visualise it on a dashboard, and facilitate alerting and monitoring on the…
 joelgmsec/leaksearch
Searches and parses plaintext passwords from public breach databases (ProxyNova COMB) by keyword (user/domain/password), with proxy support and…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…