
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
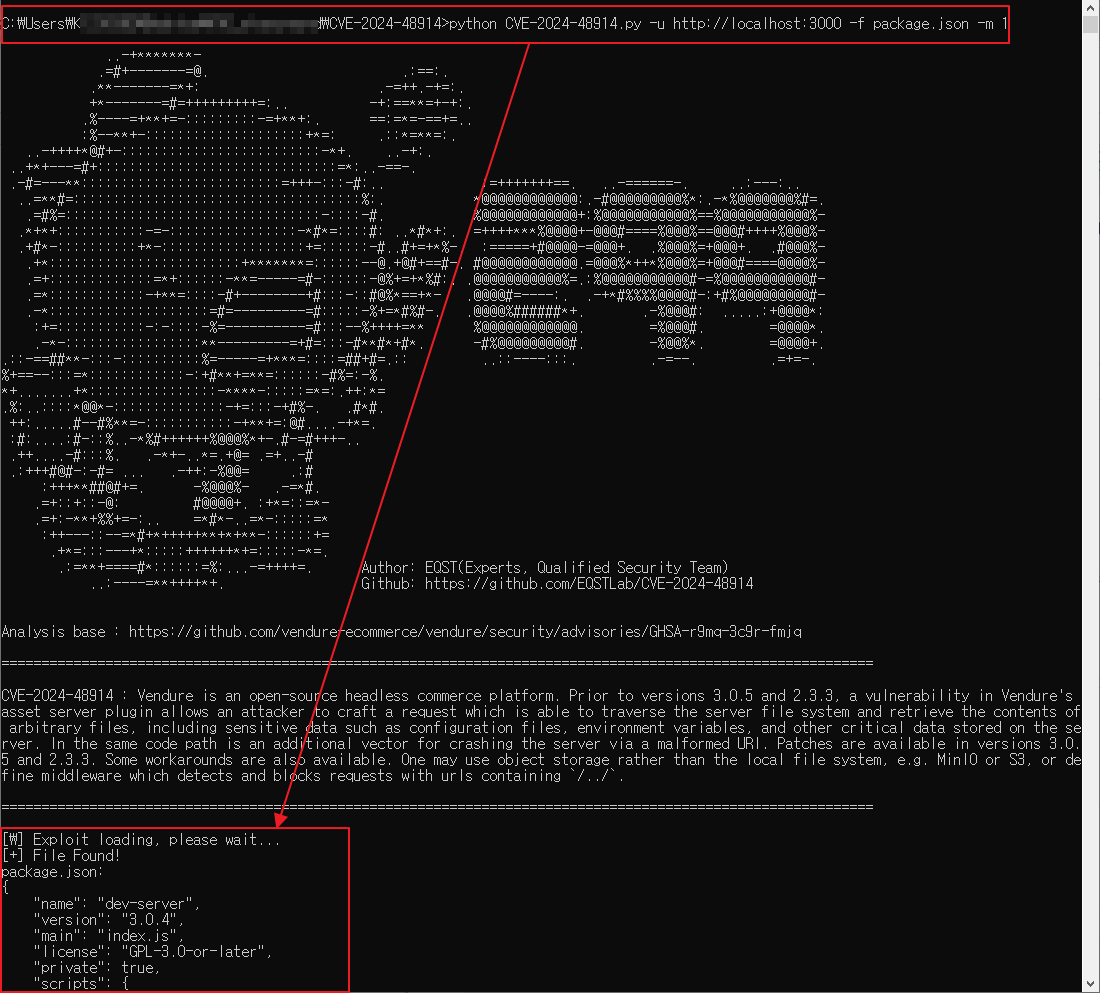
CVE-2024-48914 preview

CVE-2024-48914

GitHubeqstlab/cve-2024-48914

Arbitrary File Read and DoS in vendure-ecommerce exploit
data-exfiltrationexploitationinformation-gathering+3
52 years ago
FiberBreak preview

FiberBreak

GitHubscumfrog/fiberbreak

React2Shell Exploitation Tool (CVE-2025-55182)
cloud-securitycommand-and-controldata-exfiltration+8
10 months ago
CVE-2024-42009-PoC preview

CVE-2024-42009-PoC

GitHubdanithehack3r/cve-2024-42009-poc

CVE-2024-42009 Proof of Concept
data-exfiltrationeducationemail-security+3
81 year ago
CVE-2026-42527 preview

CVE-2026-42527

GitHuboscerd/cve-2026-42527

Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel
data-exfiltrationdns-analysisexploitation+3
3 months ago
CVE-2018-12633-TPLink-Auth-Bypass preview

CVE-2018-12633-TPLink-Auth-Bypass

GitHubwiliam227user/cve-2018-12633-tplink-auth-bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
data-exfiltrationeducationembedded-systems-security+8
110 months ago
CVE-2026-85706 preview

CVE-2026-85706

GitHubgabrielunknown/cve-2026-85706

Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
data-exfiltrationexploitationinformation-gathering+6
1 month ago
CVE-2026-26980 preview

CVE-2026-26980

GitHubvognik/cve-2026-26980

Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
database-securitydata-exfiltrationexploitation+4
102 months ago
CVE-2026-85706-gitlab-poc preview

CVE-2026-85706-gitlab-poc

GitHubgagaltotal/cve-2026-85706-gitlab-poc

Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
data-exfiltrationexploitationpenetration-testing+3
11 month ago
Grafana-CVE-2021-43798 preview

Grafana-CVE-2021-43798

GitHubjas502n/grafana-cve-2021-43798

Grafana Unauthorized arbitrary file reading vulnerability
data-exfiltrationexploitationinformation-gathering+3
3703 years ago
CVE-2026-27944 preview

CVE-2026-27944

GitHubskynoxk/cve-2026-27944

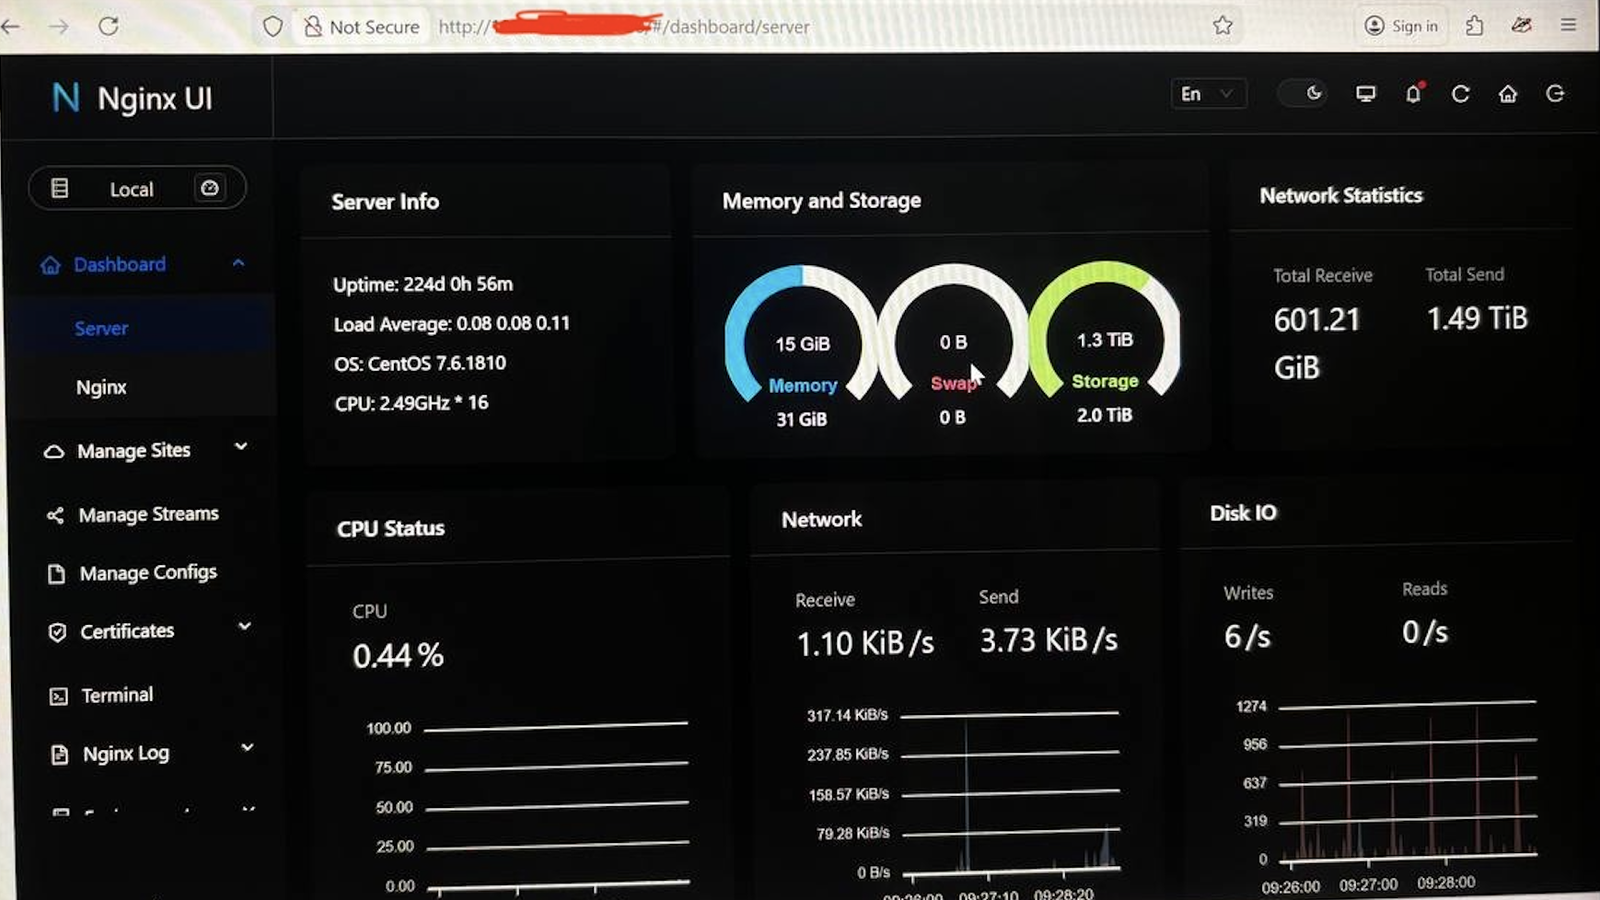
Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
authentication-authorizationdata-exfiltrationexploitation+3
97 months ago
CVE-2026-41653 preview

CVE-2026-41653

GitHubastaruf/cve-2026-41653

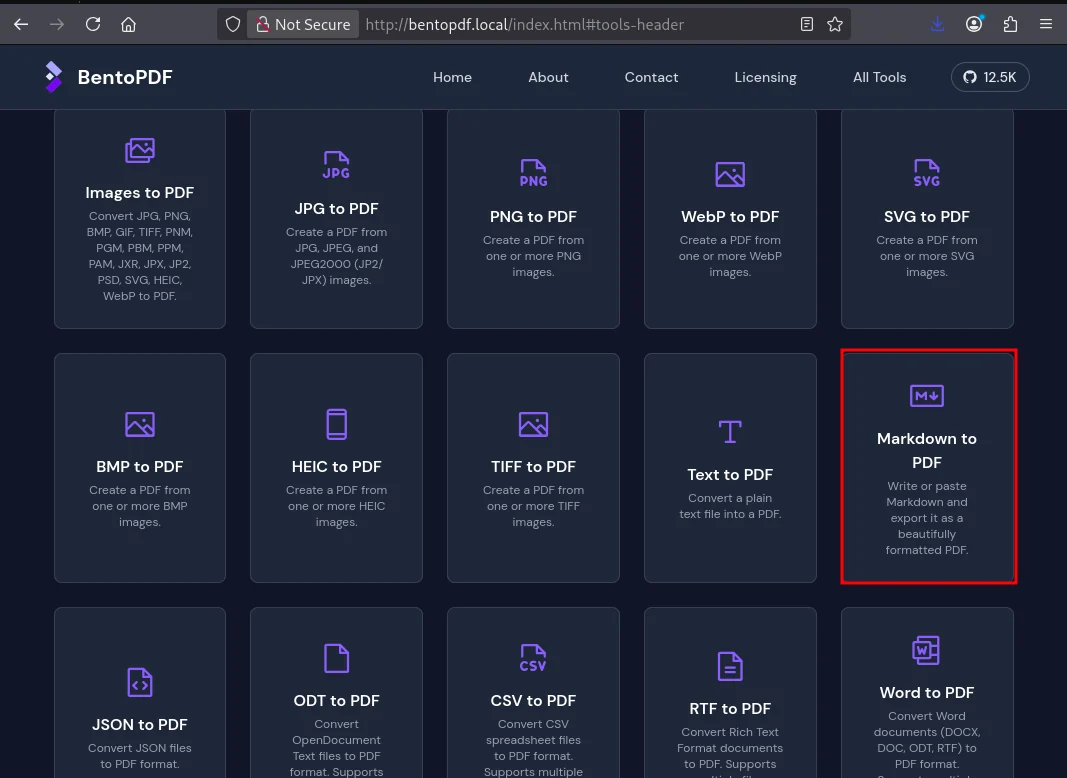
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
data-exfiltrationexploitationpayload-development+2
6 months ago
CVE-2023-22047-Oracle-PeopleSoft-LFI preview

CVE-2023-22047-Oracle-PeopleSoft-LFI

GitHub0xterror/cve-2023-22047-oracle-peoplesoft-lfi

CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
data-exfiltrationexploitationinformation-gathering+3
12 months ago
cve-2016-1764 preview

cve-2016-1764

GitHubmoloch--/cve-2016-1764

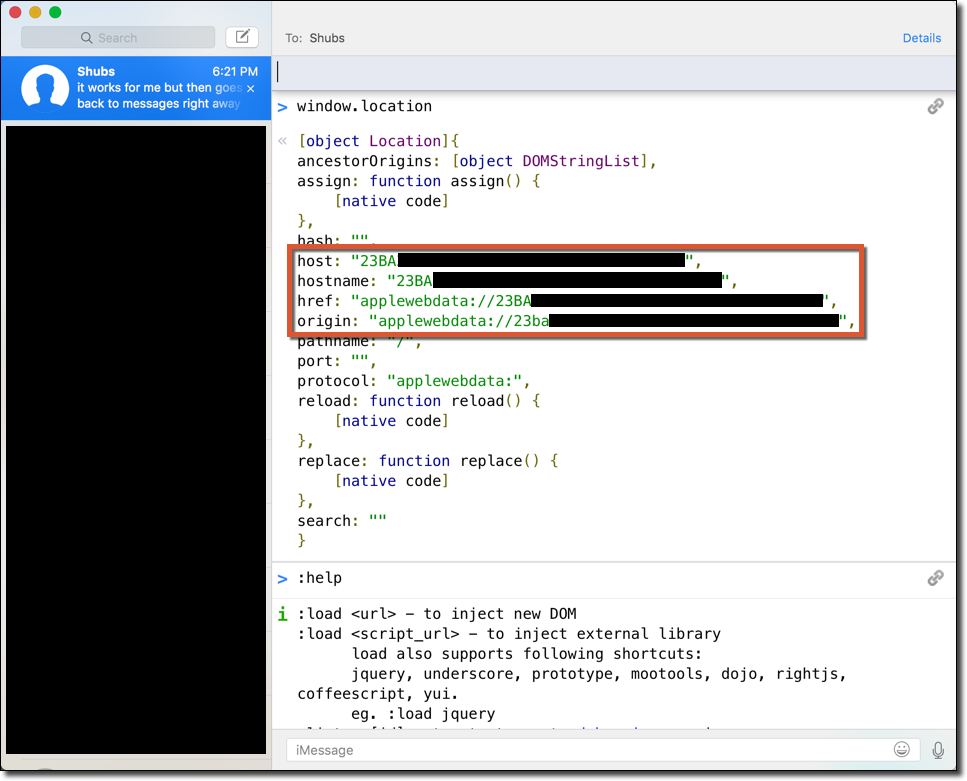
Extraction of iMessage Data via XSS
data-exfiltrationexploitationinformation-gathering+4
5110 years ago
CVE-2024-34693 preview

CVE-2024-34693

GitHubmr-r00t11/cve-2024-34693

An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
database-securitydata-exfiltrationexploitation+3
2 years ago
flar3ad preview

flar3ad

GitHubdaemoncibsec/flar3ad

POC of CVE-2026-51031 for arbitrary local file read
data-exfiltrationexploitationpenetration-testing+2
2 months ago
CVE-2024-28987 preview

CVE-2024-28987

GitHubdarabium/cve-2024-28987

**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…
data-exfiltrationexploitationpenetration-testing+2
13 months ago
CVE-2026-25253 preview

CVE-2026-25253

GitHubyym8538/cve-2026-25253

Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
authenticationdata-exfiltrationexploitation+6
12 months ago
CVE-2024-12849-Poc preview

CVE-2024-12849-Poc

GitHubnxploited/cve-2024-12849-poc

Exploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…

data-exfiltrationexploitationpenetration-testing+2
1 year ago
Previous123Next