

nuclei-templates
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
code-analysiscrawlercurated-resources+6
13.0k
projectdiscovery/nuclei-templatesCommunity curated list of templates for the nuclei engine to find security vulnerabilities.
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 tg12/phantomstars
Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure
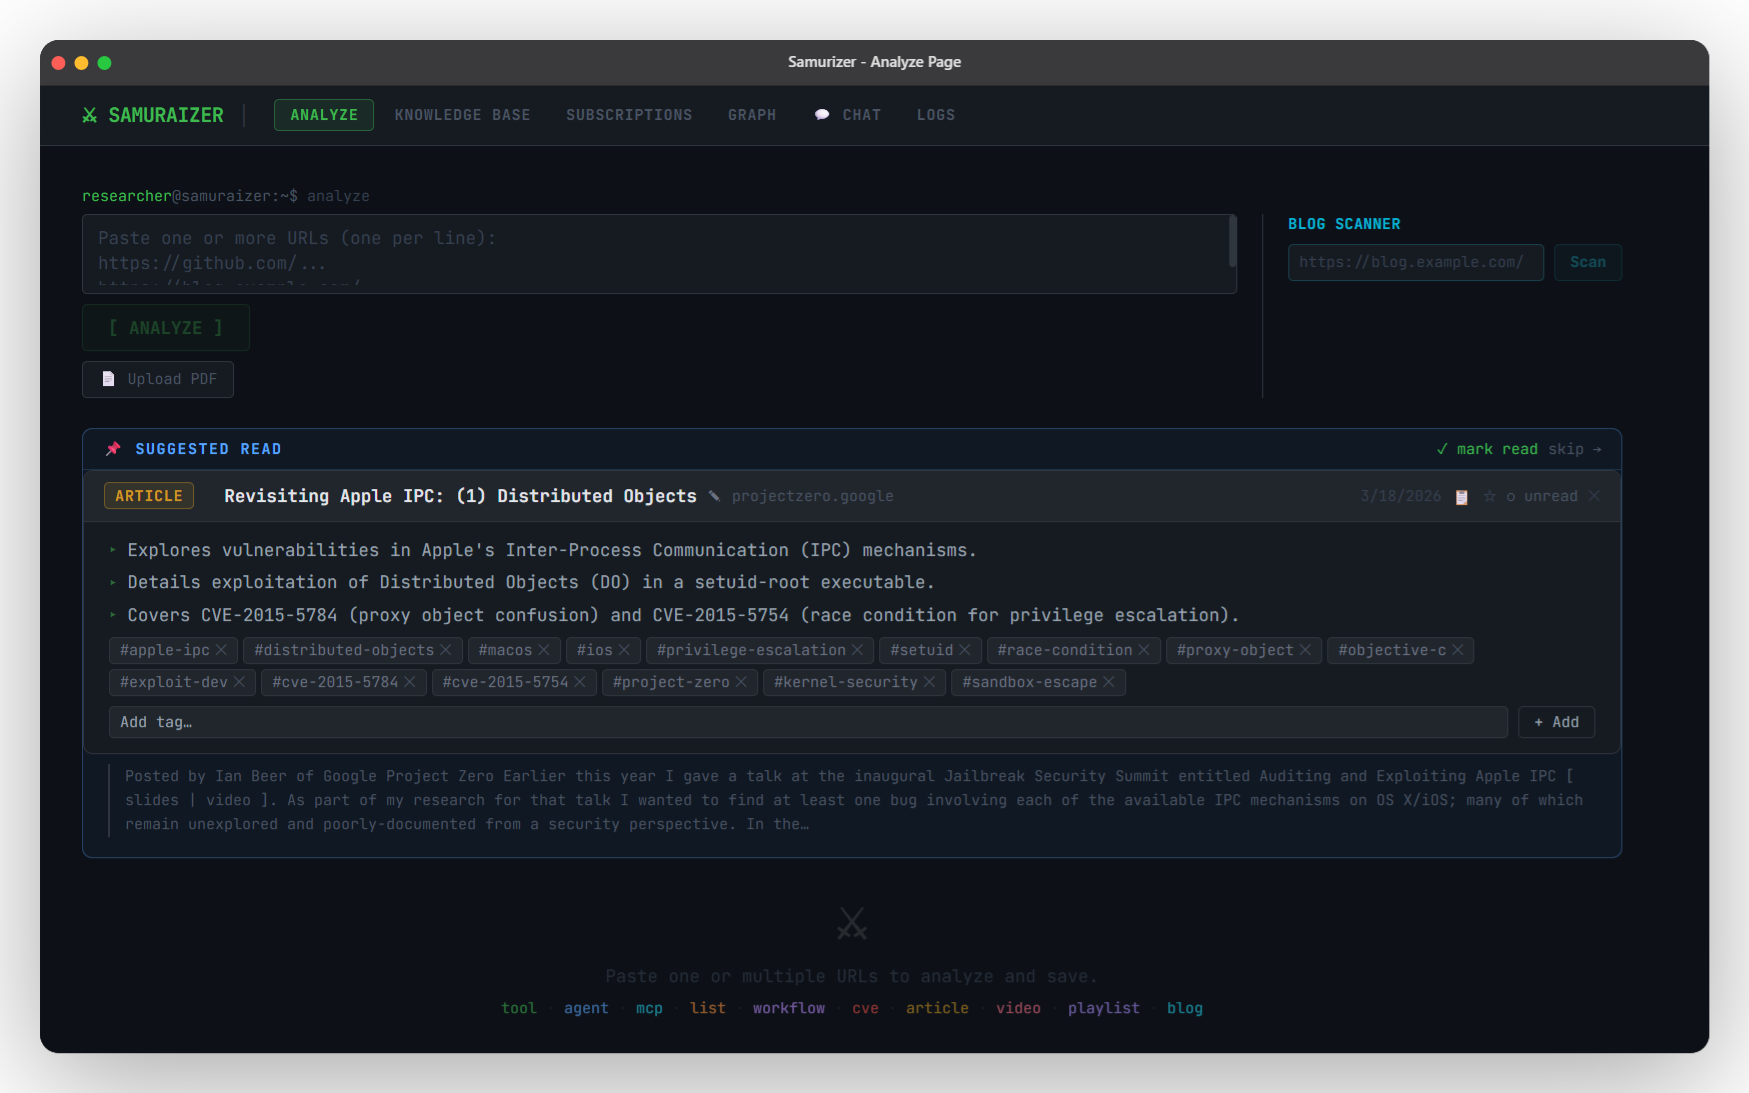 zomry1/samuraizer
NotebookLM on steroids — purpose-built for security researchers.
 rxerium/ai-bot-ip-ranges
Official IP ranges for AI bot crawlers (OpenAI, Anthropic, Google, Microsoft, Perplexity). Weekly auto-updates.
 jas502n/security_article
scrapy website Article and link ...
 kalilinux/recipes/kali-preseed-examples
Preseed configuration examples and guides for automated, hands-off Kali Linux installation, including partitioning, package selection, and boot…
 edoardottt/missing-cve-nuclei-templates
Weekly updated list of missing CVEs in nuclei templates official repository. Mainly built for bug bounty, but useful for penetration tests and…
 zhangyongbo100/-ruby-dl-handle.c-cve-2009-5147-
Community-maintained database of Ruby gem security advisories with structured CVE data, CVSS scores, and patched version requirements. Integrates…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 rxerium/cisa-kev
Aggregates and cross-references CISA's Known Exploited Vulnerabilities with VulnCheck KEV and Nuclei scanning templates for coverage analysis.
 577industries/aegisgraph
AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…
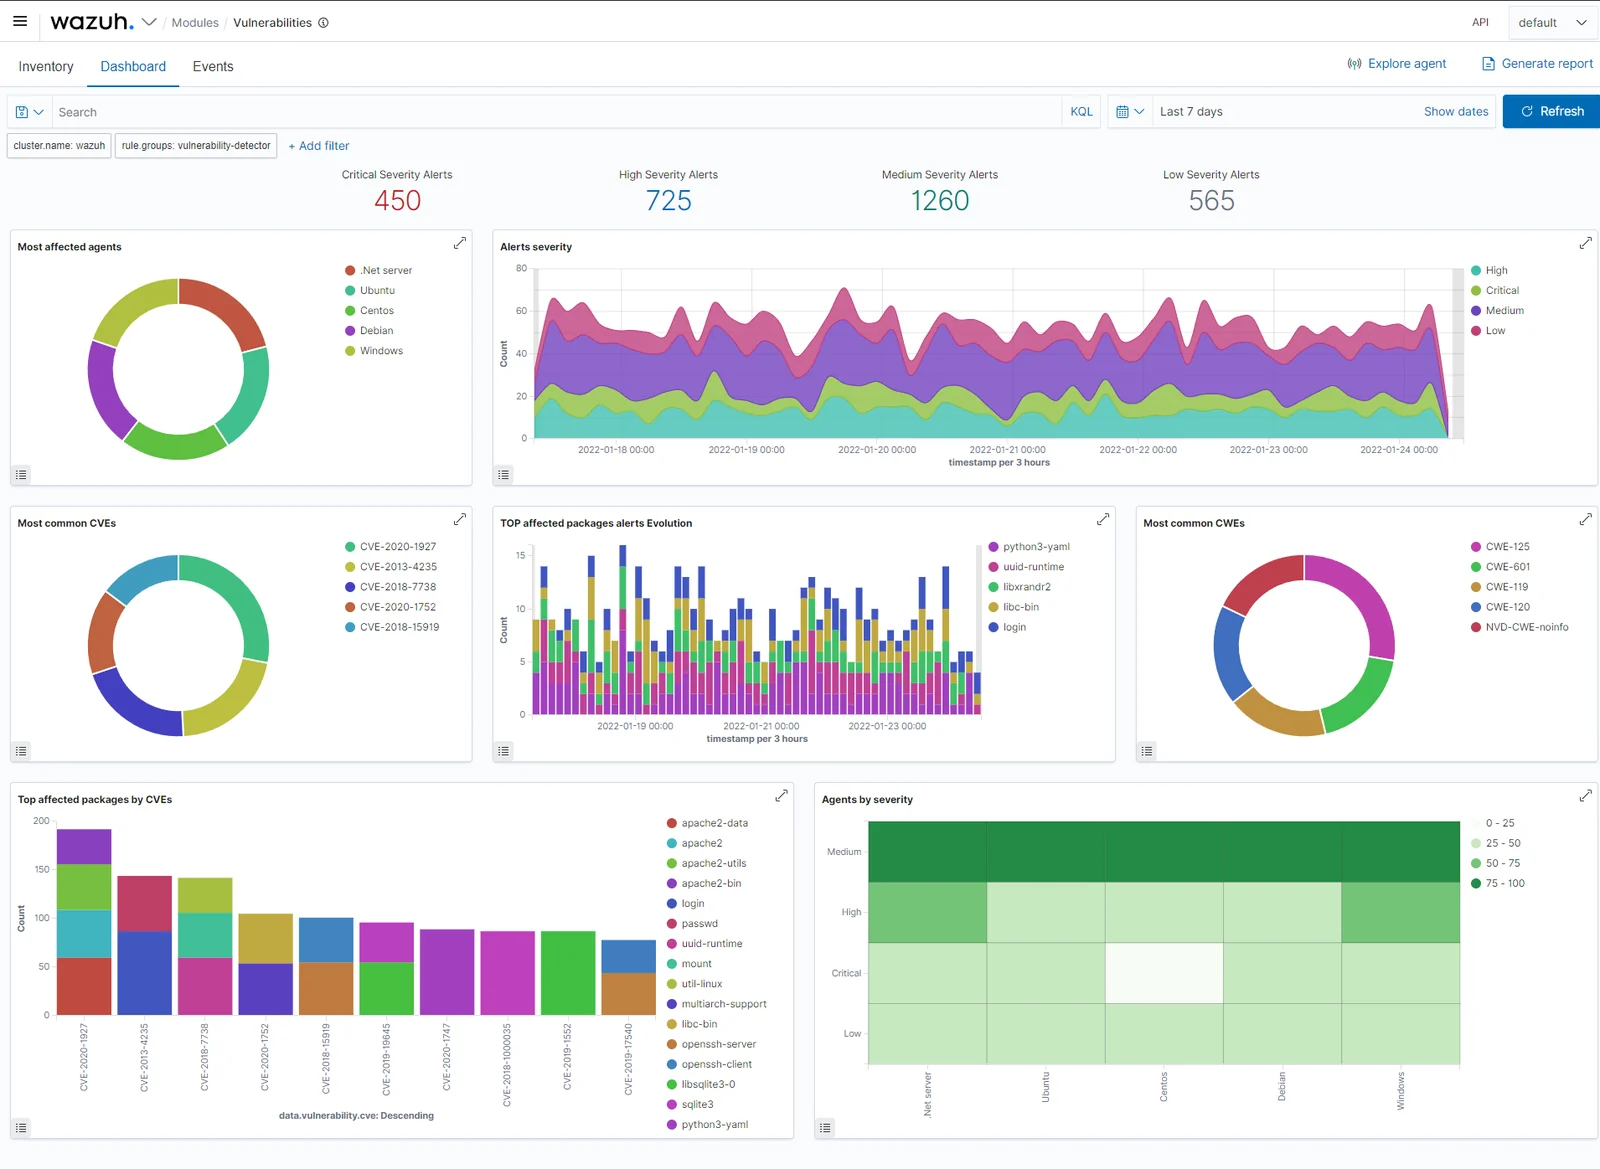 pvharmo2/gha-lab-becf103a54
Authorized security-research reproduction of CVE-2025-15617 (GHSA-6xqr-4q5g-xc7x): artipacked GITHUB_TOKEN leak in wazuh FIM Windows integration…
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 pvharmo2/gha-lab-fb6df3d456
Authorized security-research lab reproducing CVE-2025-46820 (GHSA-cwj7-6v67-2cm4): GITHUB_TOKEN persisted into publicly downloadable CI artifacts in…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 cavi-au/consent-o-matic
Browser extension that automatically fills out cookie popups based on your preferences