

Blue-Team-Notes
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
curated-resourcesdigital-forensicseducation+5
1.8k
purp1ew0lf/blue-team-notesYou didn't think I'd go and leave the blue team out, right?
 r1cksec/cheatsheets
Collection of knowledge about information security
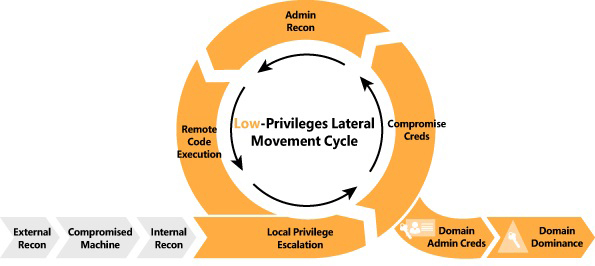 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 ice-wzl/hacknetics
Contained is all my reference material for my OSCP / Red Teaming. Designed to be a one stop shop for code, guides, command syntax, and high level…
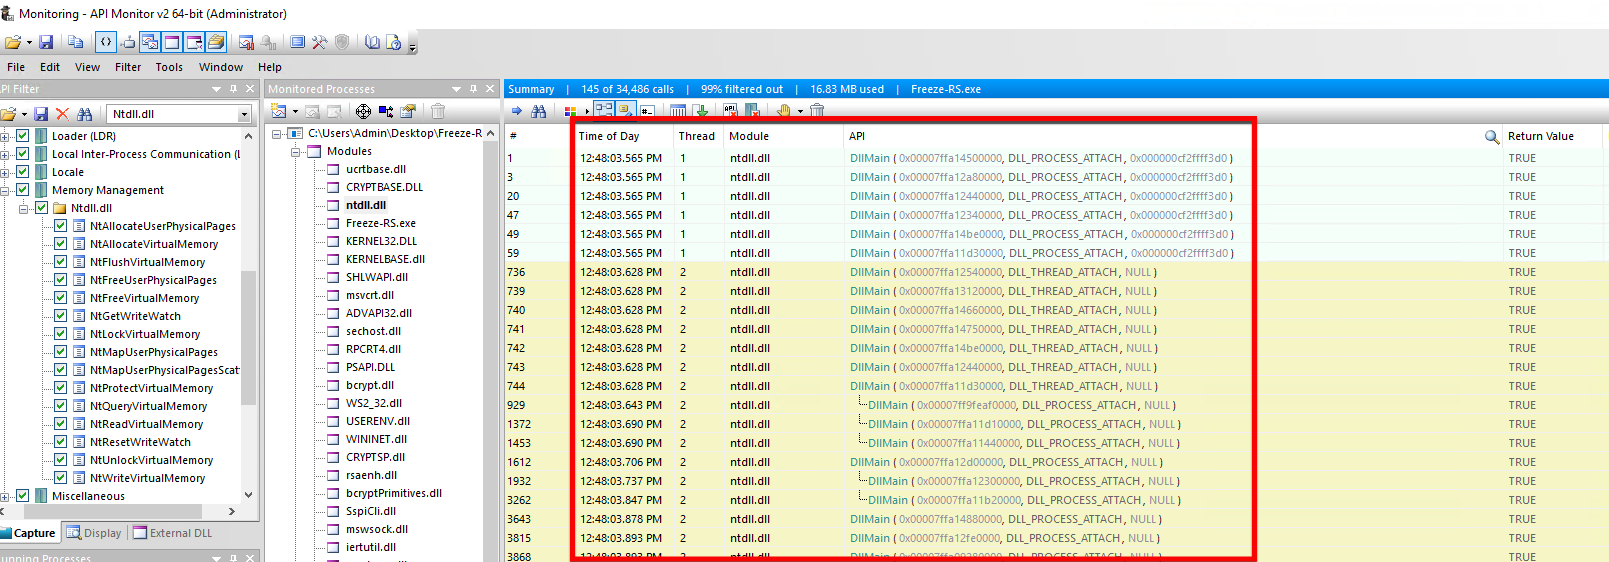
 edu0x01/hack-tools
Project that brings together several pentest tools
 professionallyevil/c4
Cyberdelia, a Collection of Command and Control frameworks
 hahwul/mad-metasploit
Metasploit custom modules, plugins, resource script and.. awesome metasploit collection
 tjnull/tj-opt
This repo contains my pentesting template that I have used in PWK and for current assessments. The template has been formatted to be used in Obsidian
 himanshusharma20/linux-for-a-pentester
Practical Penetration Testing Notes.
 pvharmo2/gha-lab-6904b2ccbe
Security-research lab: reproduction of CVE-2025-61584 (GHSA-9g7x-737f-5xpc) — command injection via github.head_ref in pull_request_target workflow…
 pvharmo2/gha-lab-85f022290a
Research lab reproduction of CVE-2026-34243 (GHSA-r4fj-r33x-8v88): command injection via issue_comment.body in .github/workflows/comment.yaml —…
 pvharmo2/gha-lab-3b0a828a69
Security-research lab reproducing CVE-2025-53104 (GHSA-432r-9455-7f9x): command injection in discussion-to-slack.yml of gluestack/gluestack-ui
 pvharmo2/gha-lab-d14c91f1bb
Security-research lab: reproduction of CVE-2025-58371 (GitHub Actions command injection via PR title in Discord PR Notifier), snapshot of…
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 pvharmo2/gha-lab-6255f5fc33
Security-research lab reproducing CVE-2023-6572 (GHSA-gqvf-3hgp-5hxv): command injection in gradio-app/gradio's workflow_run handling of…