
Pentest-Bookmarkz
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
ctfcurated-resourceseducation+9
1801 year ago
sofianehamlaoui/pentest-bookmarkzA collection of useful links for Pentesters
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 darkarnium/secpub
Published security vulnerabilities, research, and associated information.
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
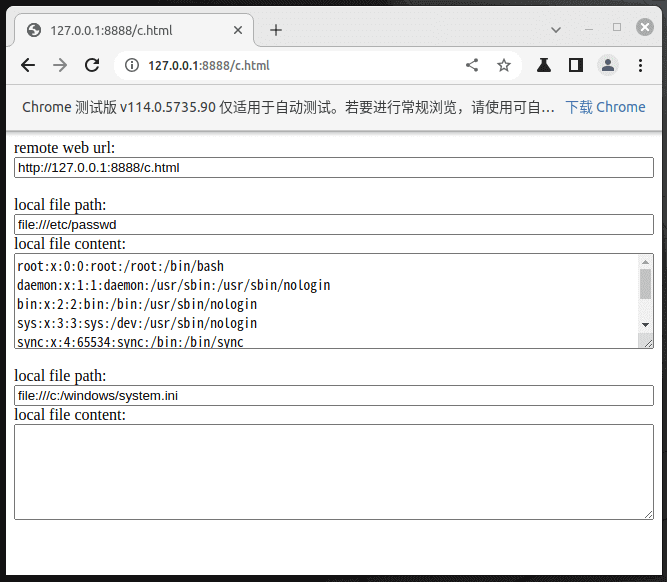 xcanwin/cve-2023-4357-chrome-xxe
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
 eclypsium/boothole
Detection scripts and mitigation resources for the BootHole vulnerability (CVE-2020-10713), including PowerShell and Bash tools to audit EFI System…
 al1ex/awesome-pentest
Collection of penetration testing tools
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
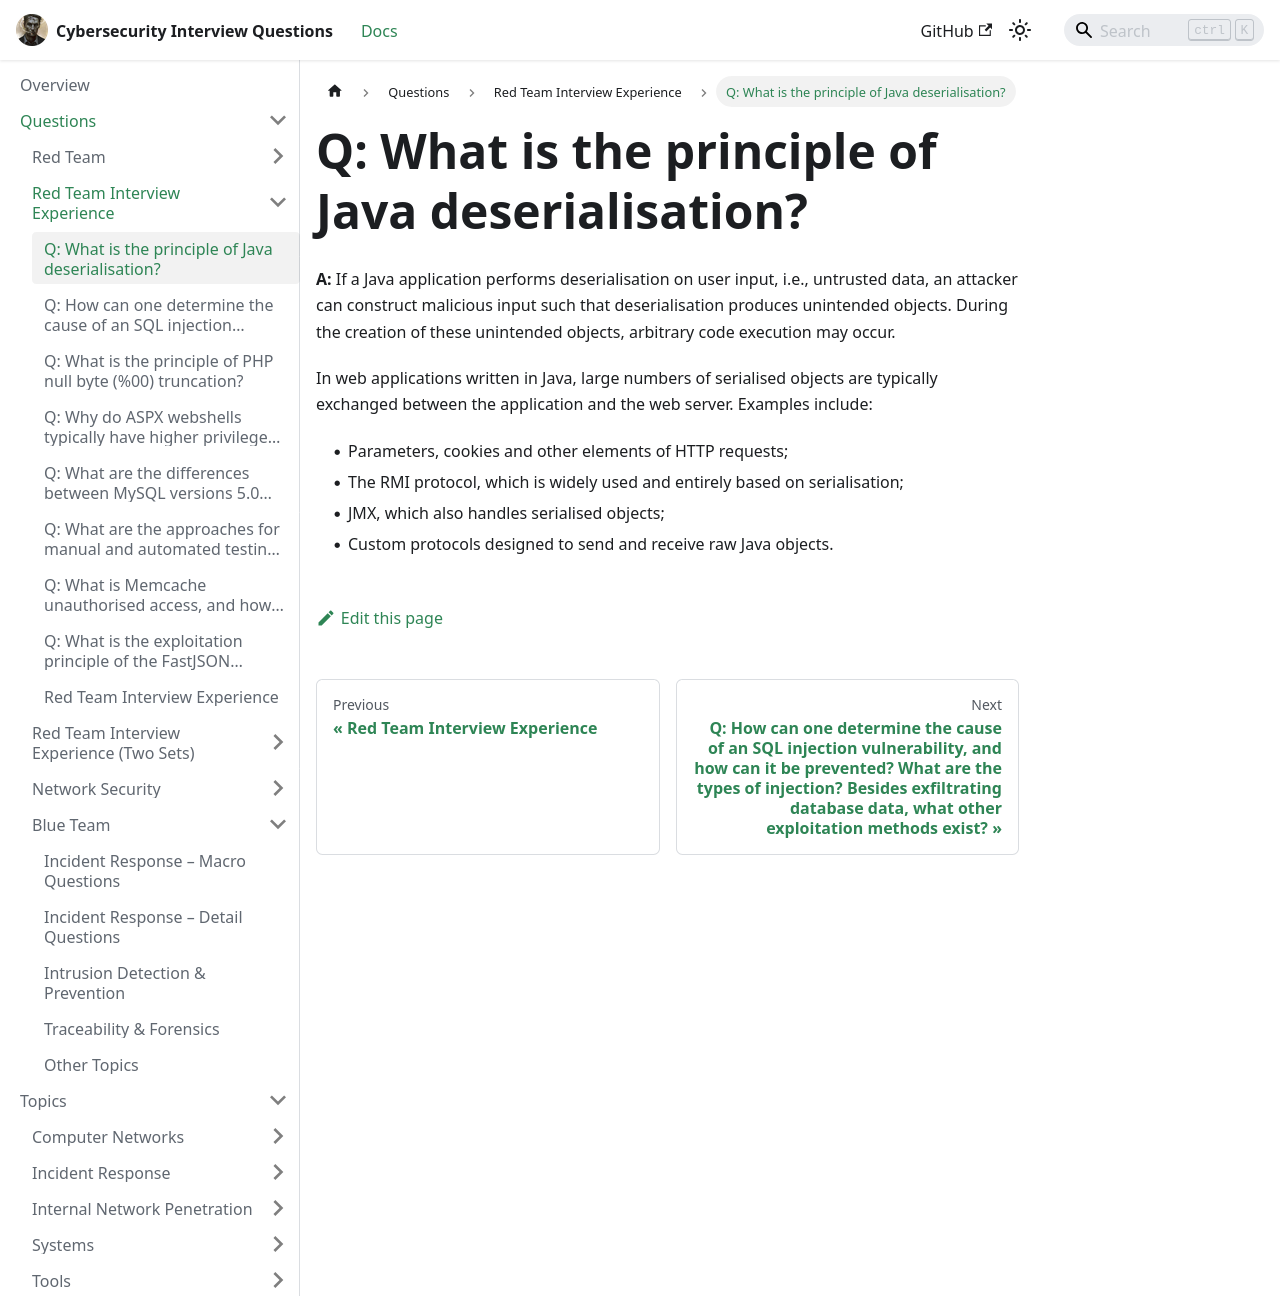 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
 cakuzo/cve-2015-7547
Shell script to detect glibc CVE-2015-7547 vulnerability on RPM-based systems, with verification steps and guidance for remediation.
 mikecostanzi/ricerca-tesi
risorse di ricerca per cve-2026-7228

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
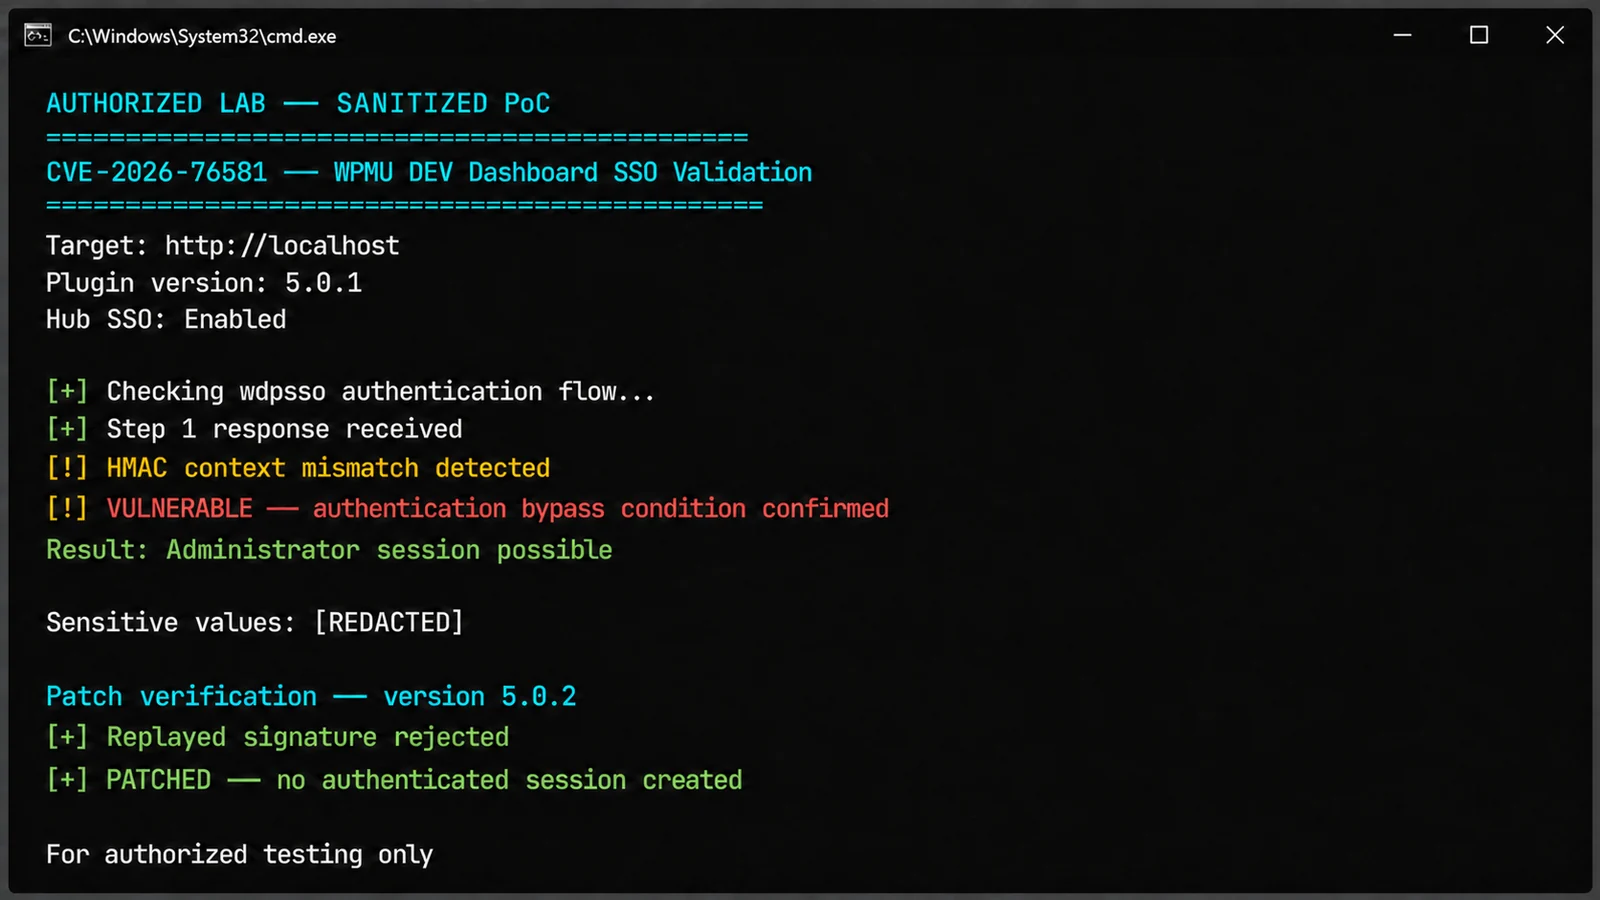 hackersroot/cve-2026-76581-detector
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…