

nosqli-flintcms
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
ctfdatabase-securityeducation+3
nisaruj/nosqli-flintcmsBlind noSQL injection case study lab based on CVE-2018-3783
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.
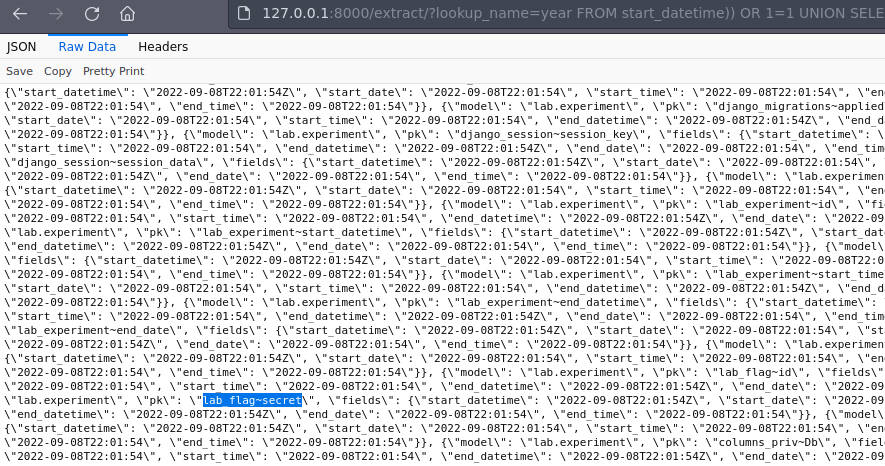 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 netw0rk7/cve-2012-2122-home-lab
CVE-2012-2122 MySQL Authentication Bypass Home Lab
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 tempuss/ctf_cve-2020-7471
CTF challenge exploiting CVE-2020-7471, a Django SQL injection vulnerability in PostgreSQL StringAgg, with Docker setup and exploit scripts.
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
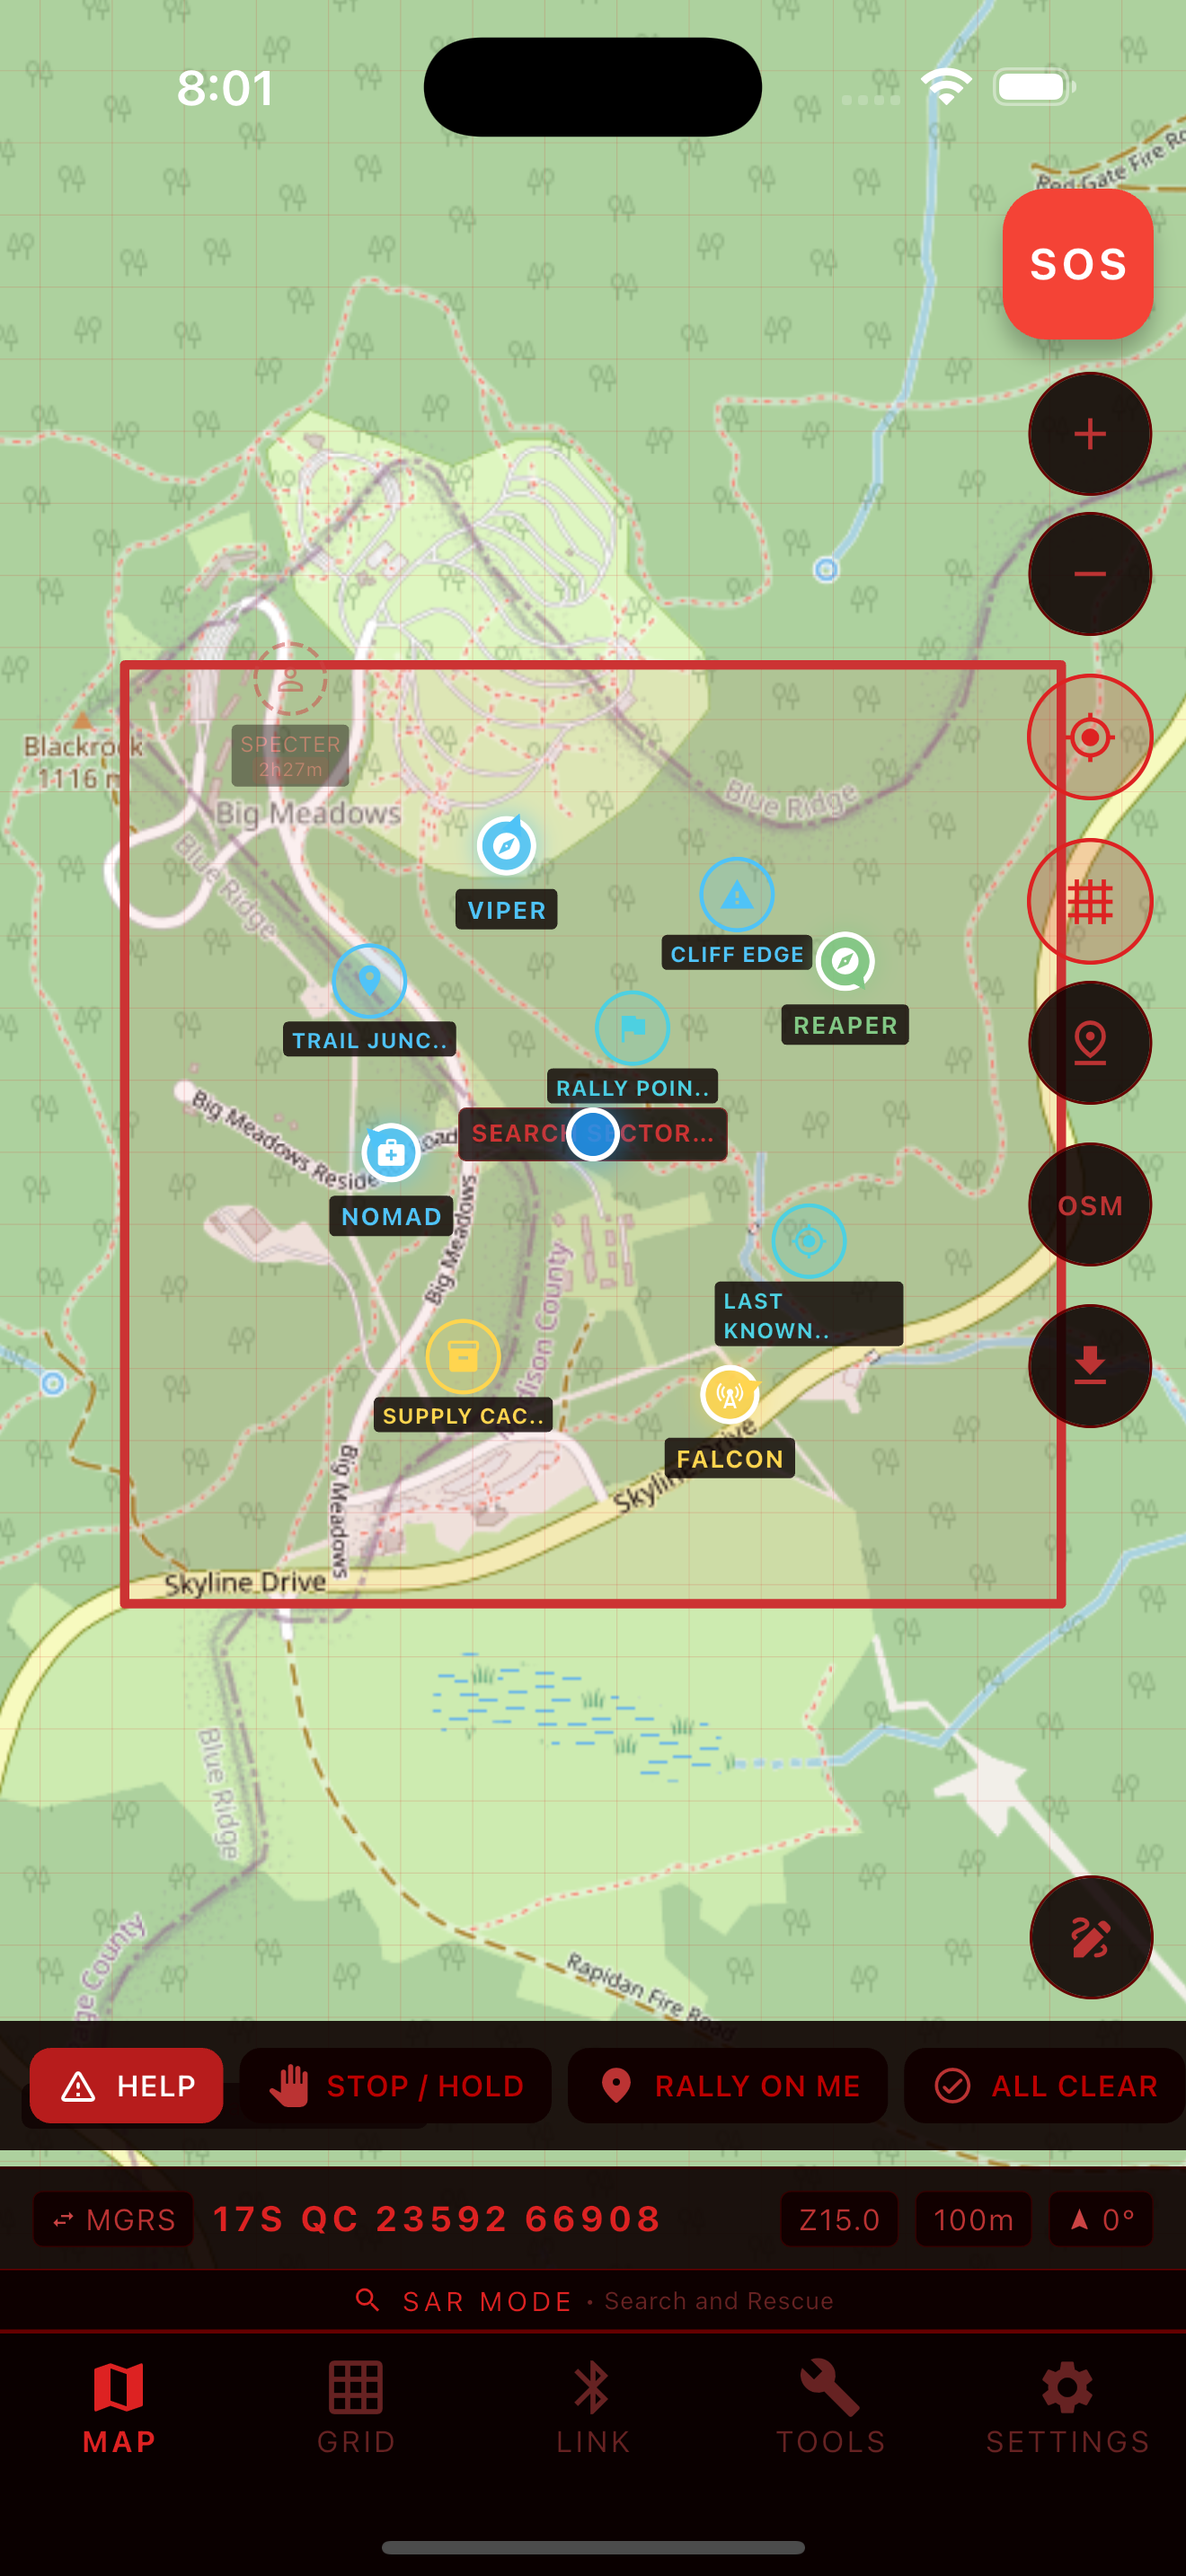 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
 stigtsp/cve-2019-6690-python-gnupg-vulnerability
Proof-of-concept exploit for CVE-2019-6690, demonstrating input validation bypass in python-gnupg symmetric encryption via newline injection in…
 ptechamanja/cve-2026-29000-pac4j-jwt-auth-bypass
Proof-of-Concept (PoC) for an authentication bypass vulnerability affecting applications using pac4j-jwt with JWE (JSON Web Encryption).
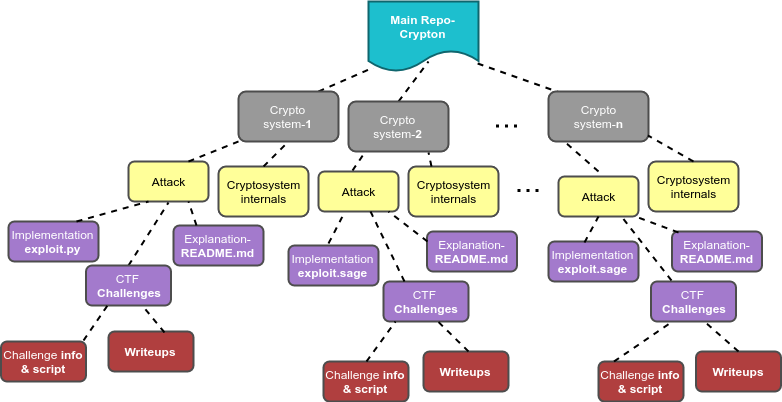 ashutosh1206/crypton
Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange,…
 acceis/crypto_identifier
Crypto tool for pentest and ctf : try to uncipher data using multiple algorithms and block chaining modes. Usefull for a quick check on unknown…