

CVE-2025-33073
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
ctfexploitationexploit-frameworks+4
67
uziii2208/cve-2025-33073Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
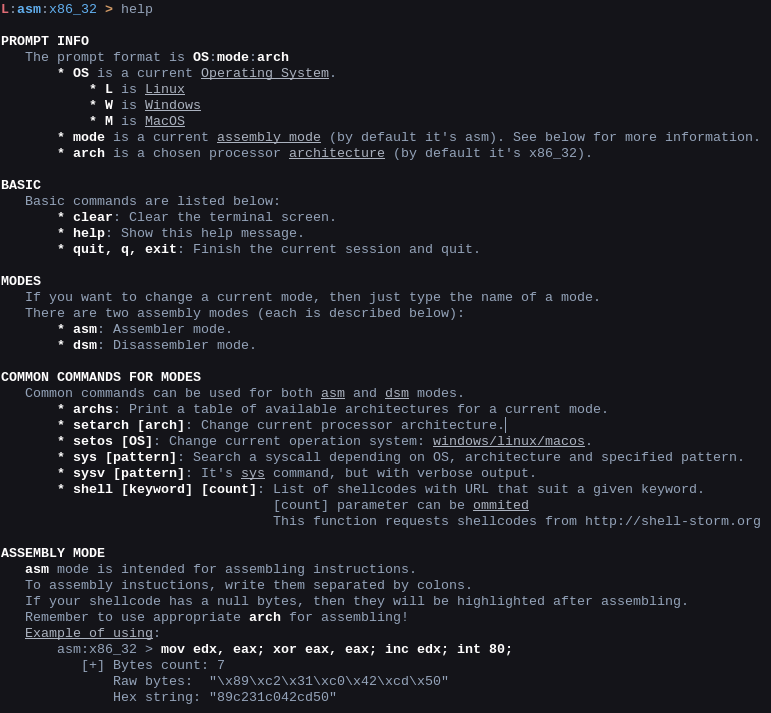 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 daemon-404/poc-cve-2025-24071
Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.
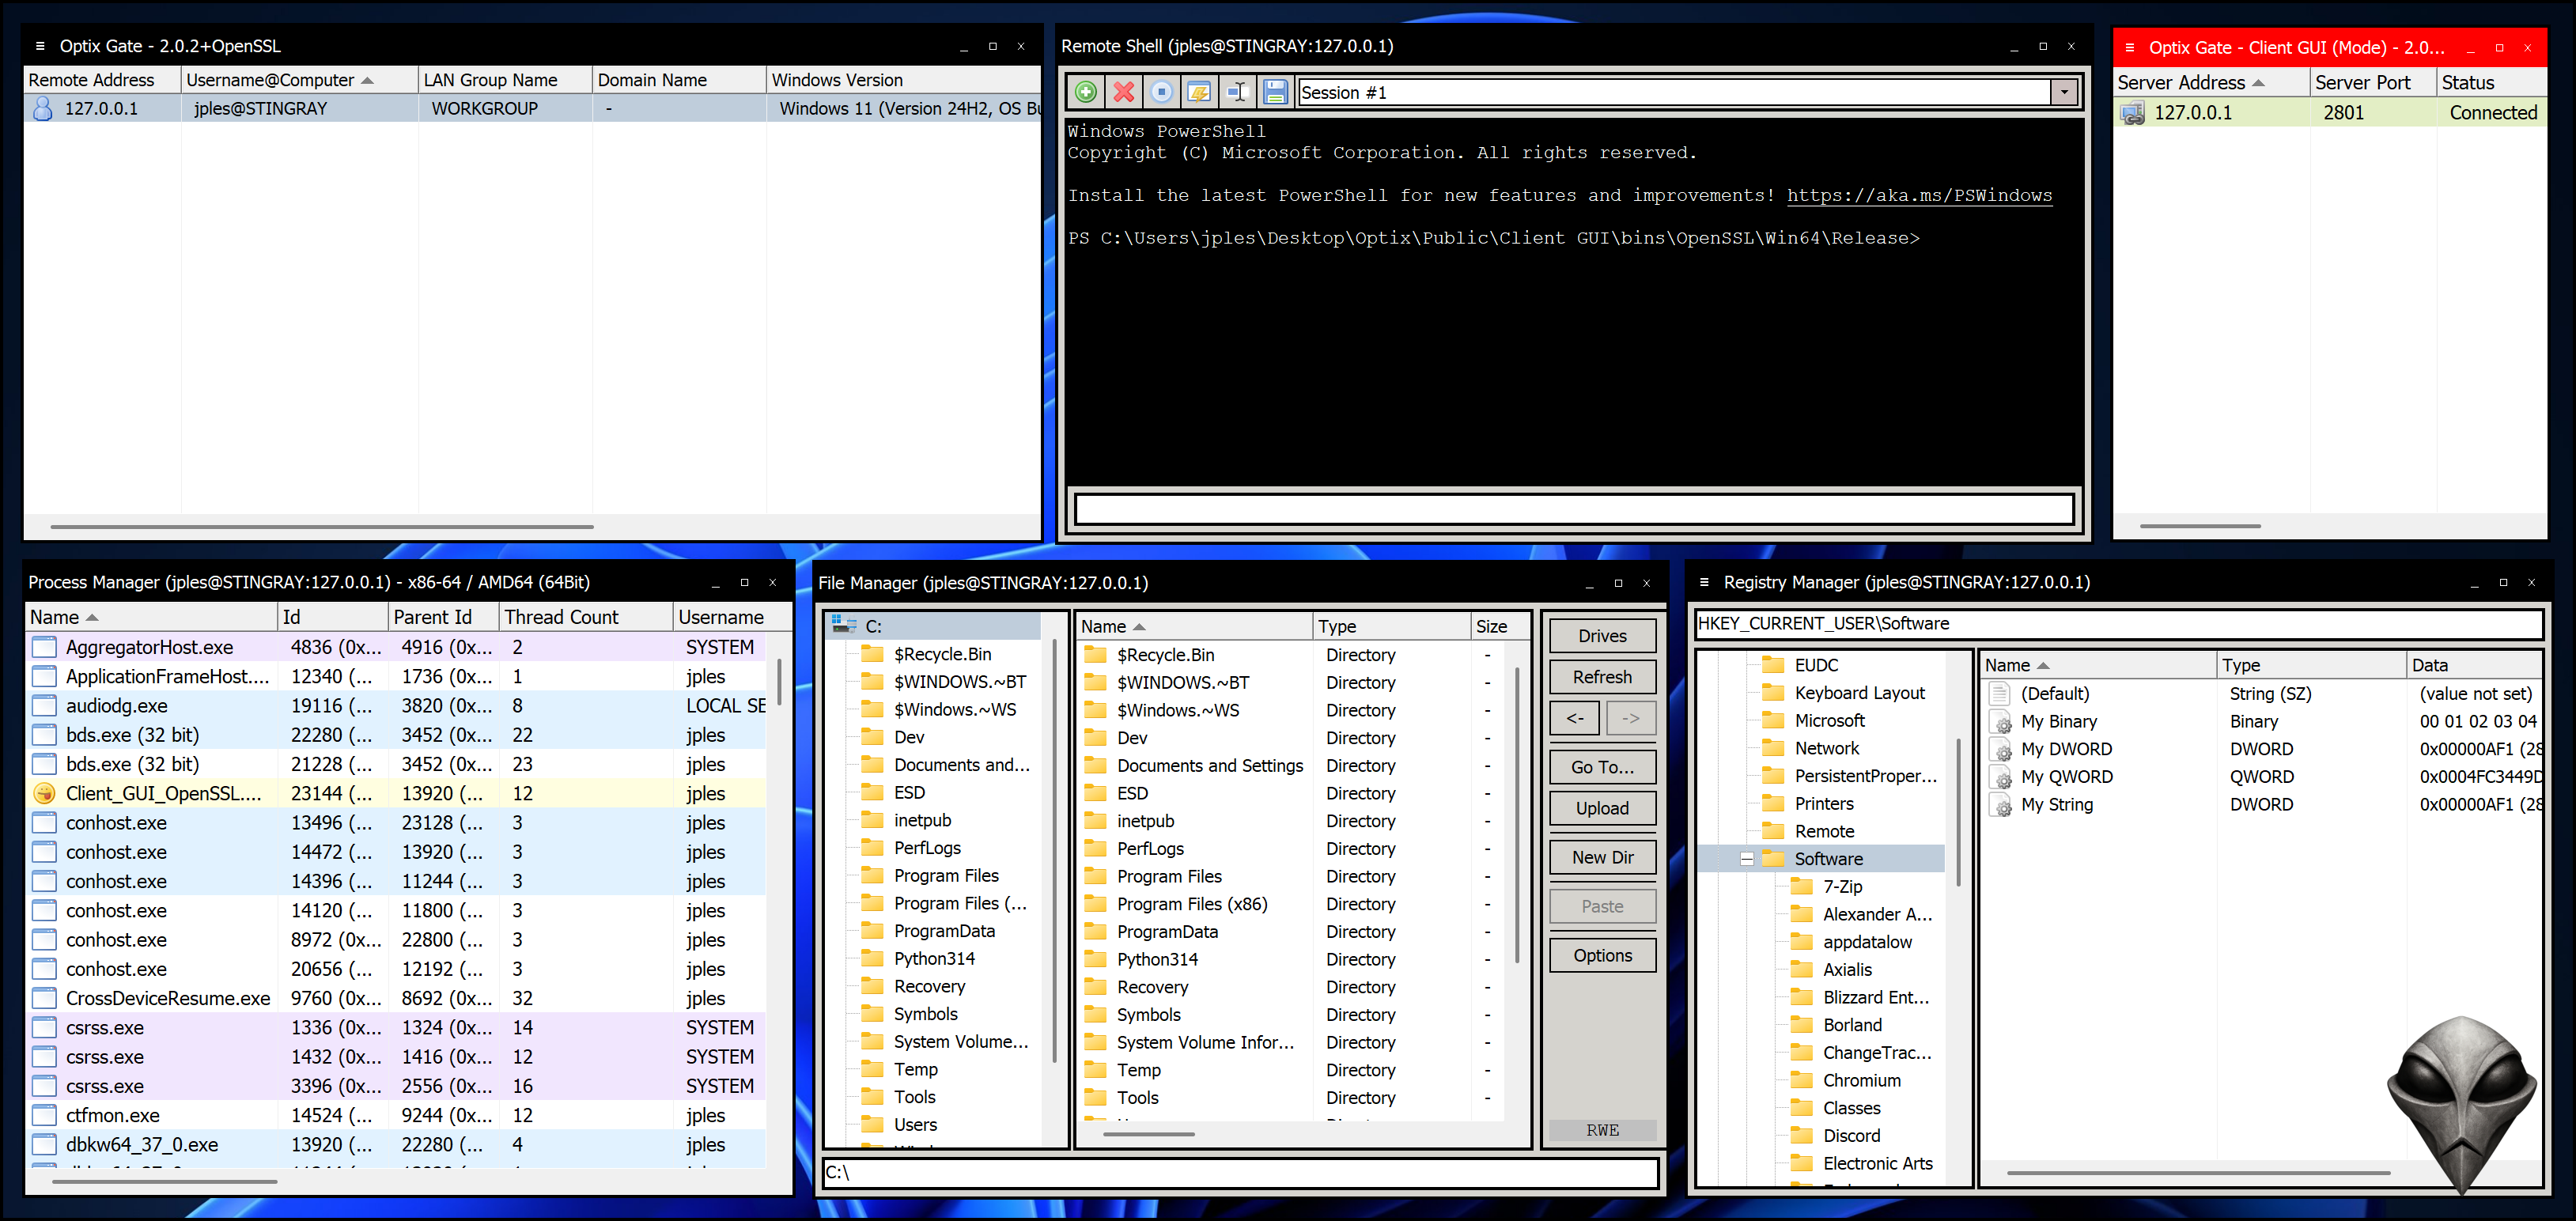 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 abrewer251/cve-2025-62215_windows_kernel_pe
This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…
 dfdxarjy/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670, abusing CheckMK Agent MSI repair to escalate from low-privileged user to SYSTEM on Windows targets. Designed…
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
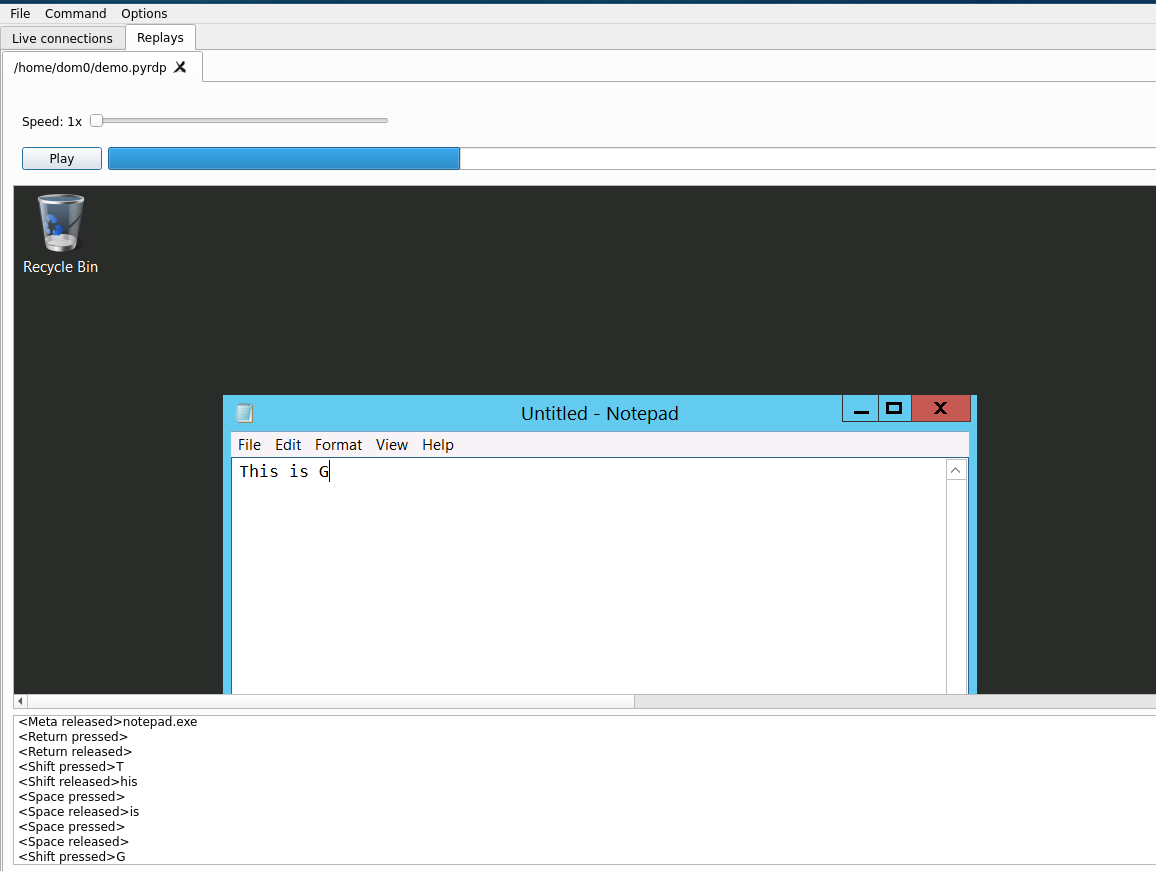 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 mitsu-bis/eternal-blue-cve-2017-0144-thm-write-up
The SMBv1 server in Microsoft Windows Vista SP2; Windows Server 2008 SP2 and R2 SP1; Windows 7 SP1; Windows 8.1; Windows Server 2012 Gold and R2;…
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool