

payloads
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
ctfcurated-resourceseducation+6
foospidy/payloadsGit All the Payloads! A collection of web attack payloads.
 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
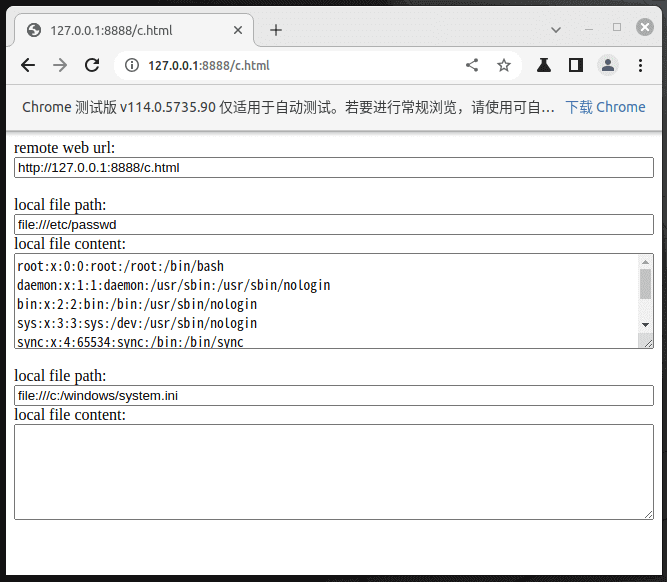 xcanwin/cve-2023-4357-chrome-xxe
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
 entr0pie/cve-2022-44268
Proof-of-concept exploit for ImageMagick arbitrary file read vulnerability (CVE-2022-44268) via crafted PNG textual chunks, enabling extraction of…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
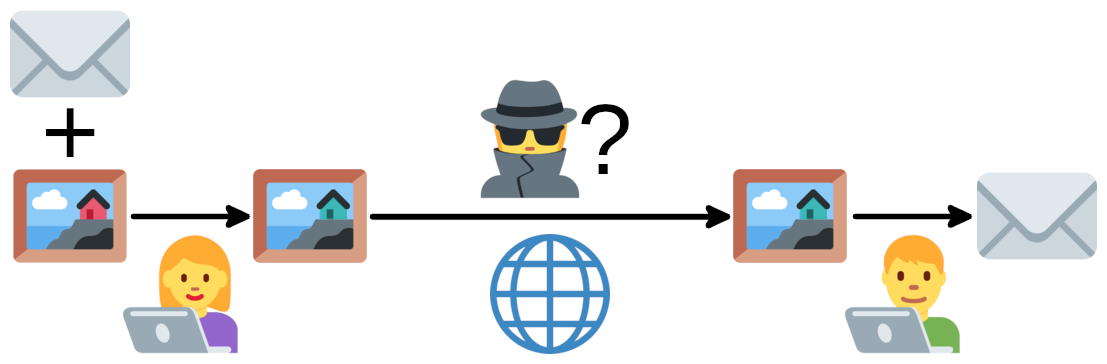 ragibson/steganography
Least Significant Bit Steganography for bitmap images (.bmp and .png), WAV sound files, and byte sequences. Simple LSB Steganalysis (LSB extraction)…
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
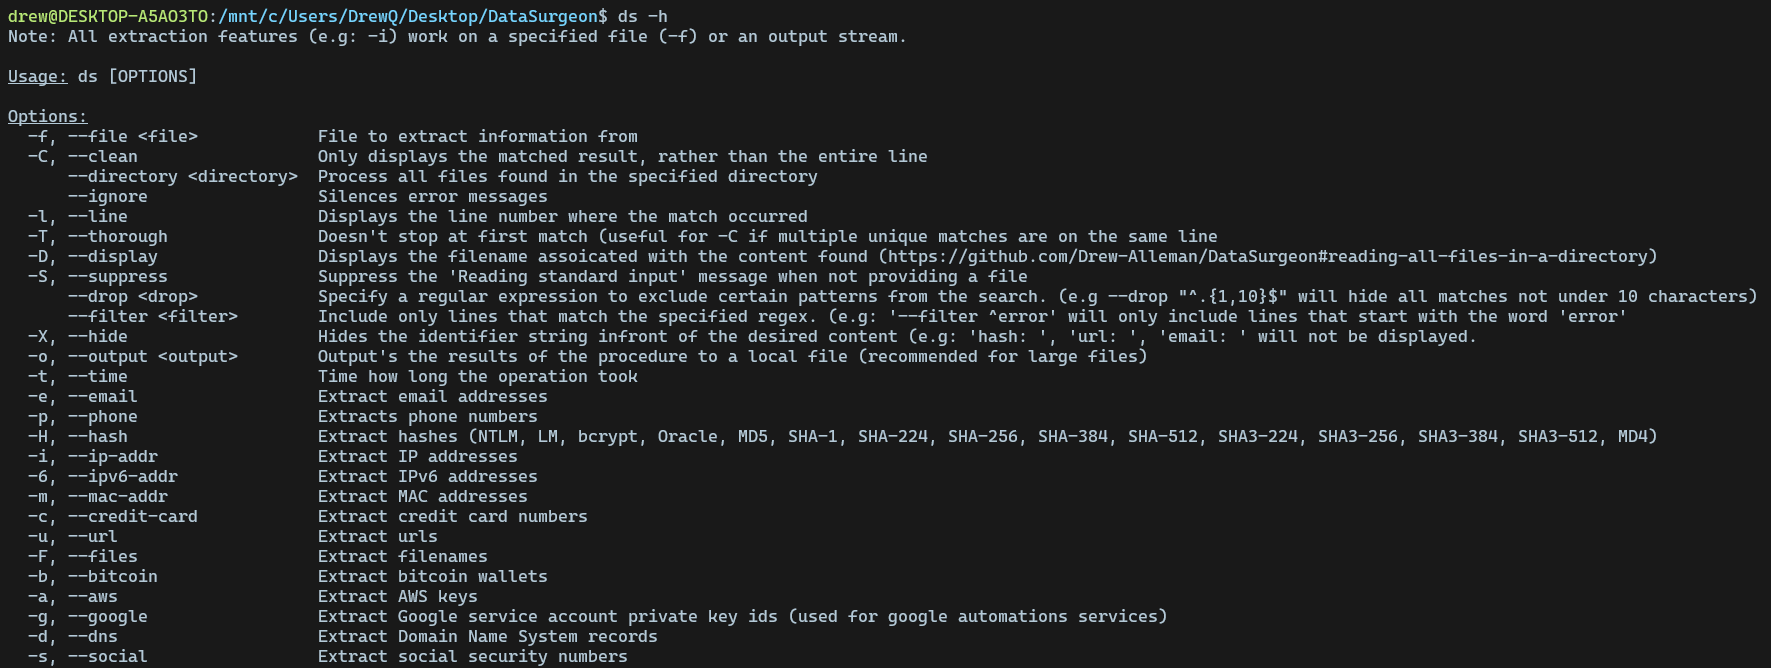 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 downunderctf/challenges_2022_public
Files + Writeups for DownUnderCTF 2022 Challenges
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 stellardriftlabs/cve-2018-8097-poc
POC for CVE-2018-8097 This script exploits CVE-2018-8097 and can retrieve files and contents using a blind RCE method.
 justinye377/ctf-cve-2022-0847
CTF challenge deploying CVE-2022-0847 (Dirty Pipe) exploit to overwrite read-only files. Includes setup scripts, hints, and verification for kernel…