
CVE-2021-32724-Target
 maximeschlegel/cve-2021-32724-target
Deliberately vulnerable GitHub repository configured with CVE-2021-32724 for practicing exploitation of the Check Spelling Workflow in a controlled…
ctfeducationexploitation+2
maximeschlegel/cve-2021-32724-targetDeliberately vulnerable GitHub repository configured with CVE-2021-32724 for practicing exploitation of the Check Spelling Workflow in a controlled…
 swe-agent/swe-agent
LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use…
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
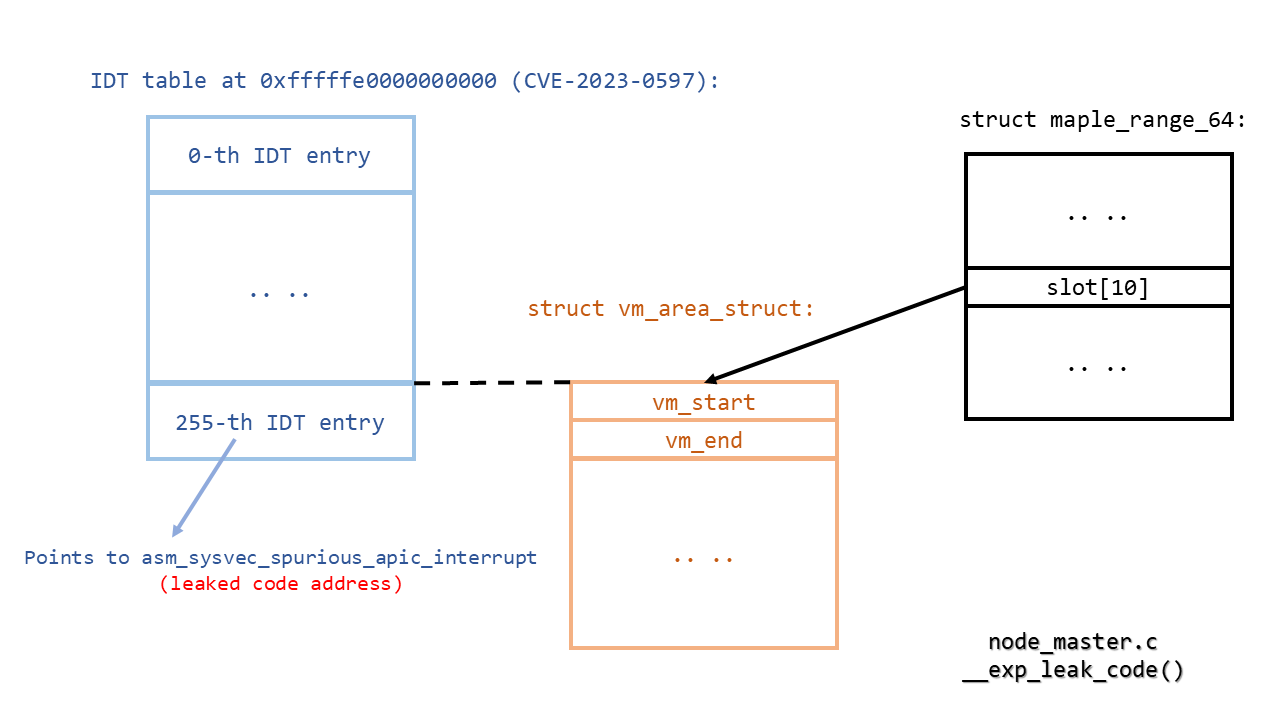 lrh2000/stackrot
CVE-2023-3269: Linux kernel privilege escalation vulnerability
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 4qu4r1um/cve-2026-54337-poc
CVE-2026-54337 - Unauthenticated File Write/Overwrite PoC for fireshare <= 1.16.3
 yafiah-darwesh/cs50-cyber-paloalto-oauth
CS50 Cybersecurity final project — Palo Alto OAuth token breach (CVE-2024-3400)