
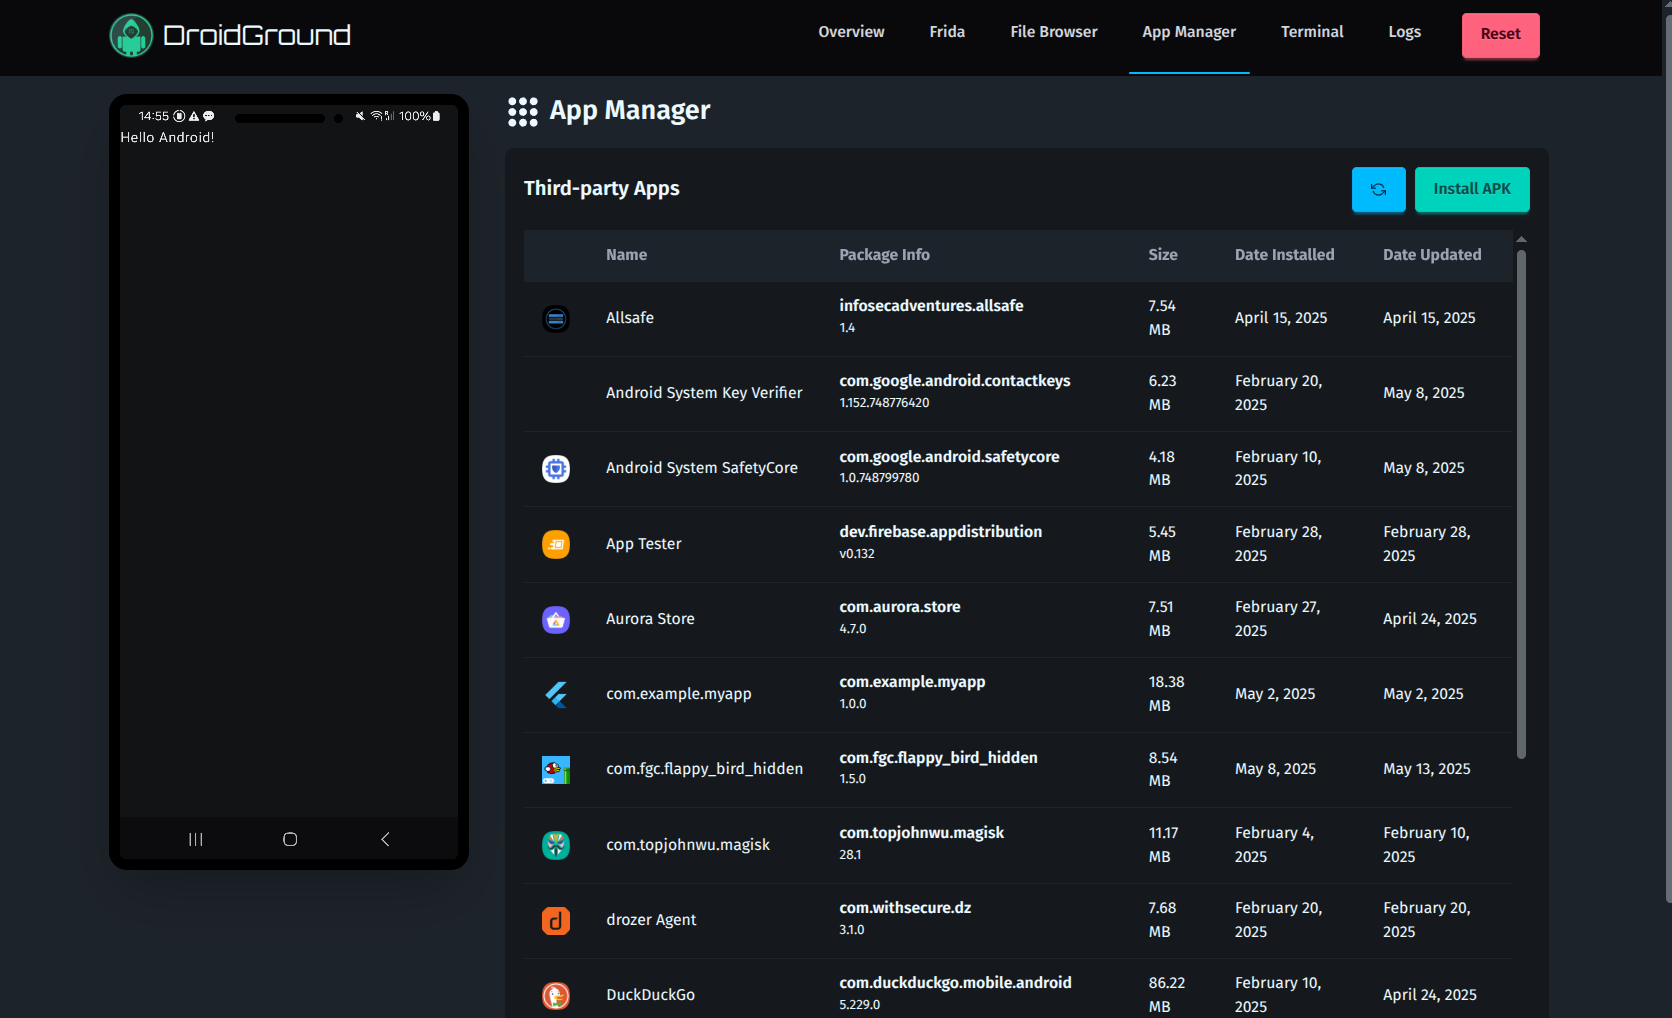
droidground
 secforce/droidground
A flexible playground for Android CTF challenges.
android-securityctfdynamic-analysis-sandboxing+5
secforce/droidgroundA flexible playground for Android CTF challenges.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
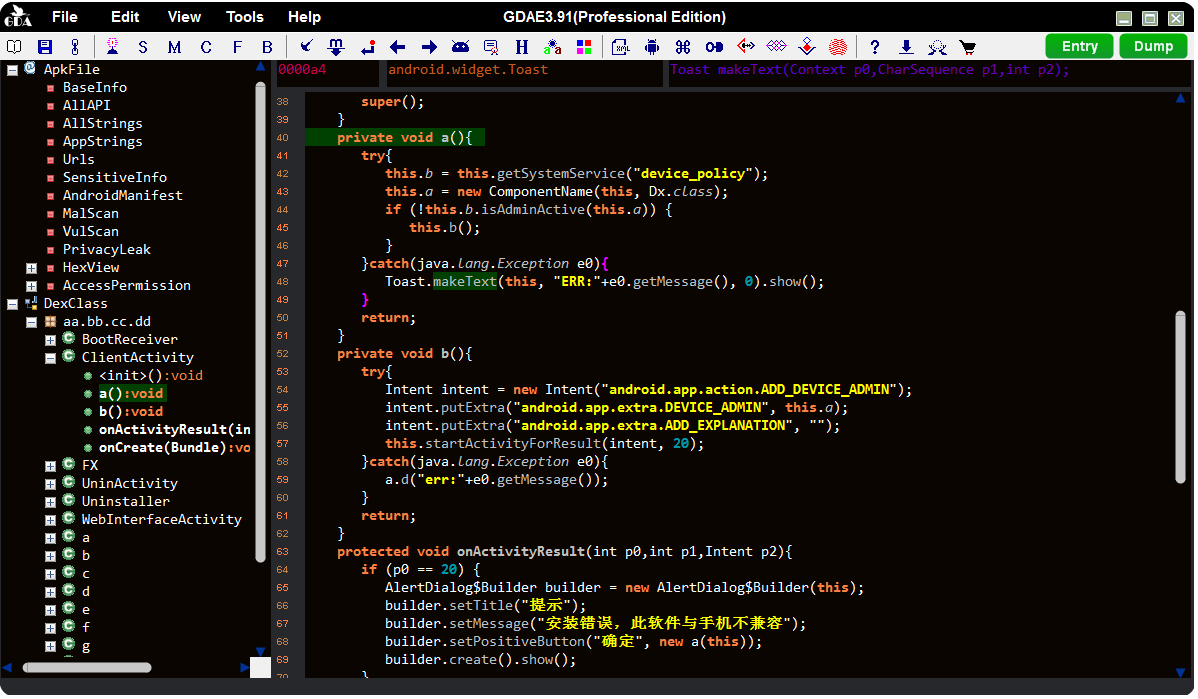 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
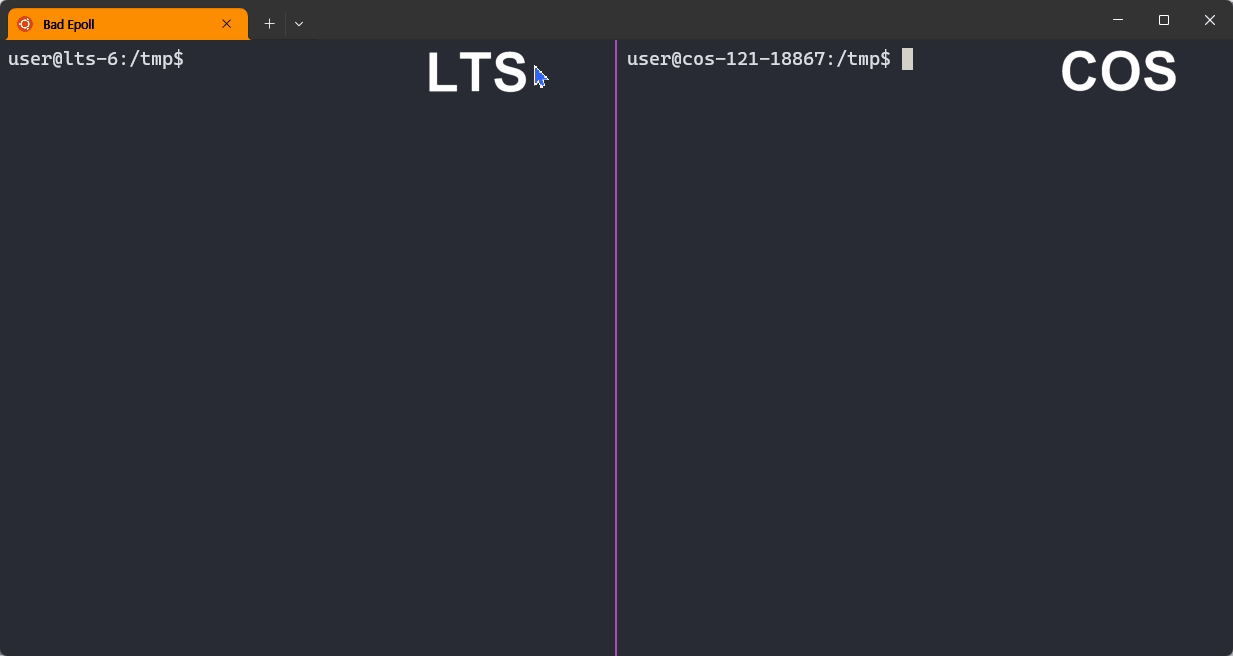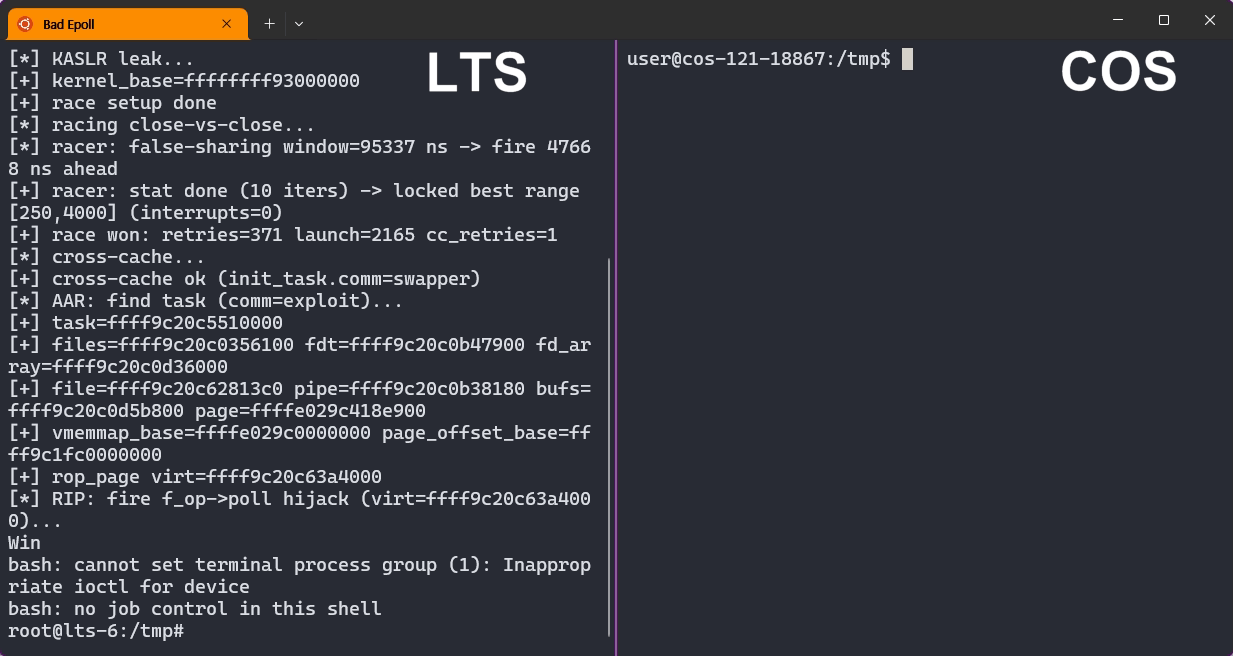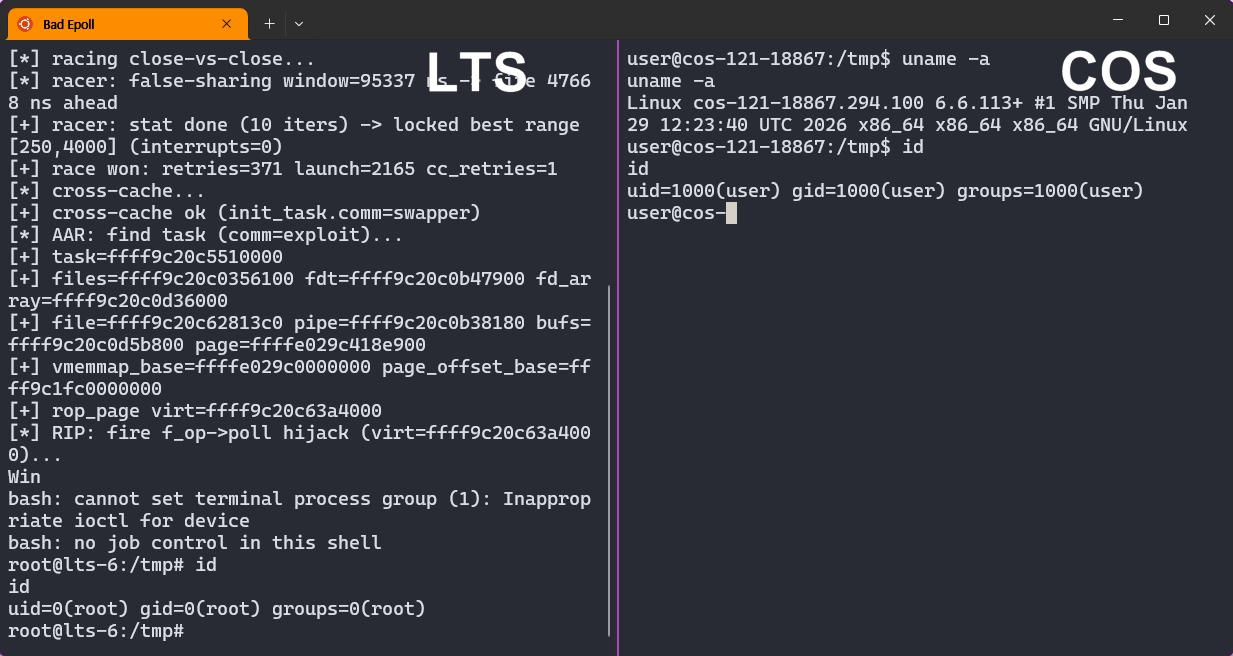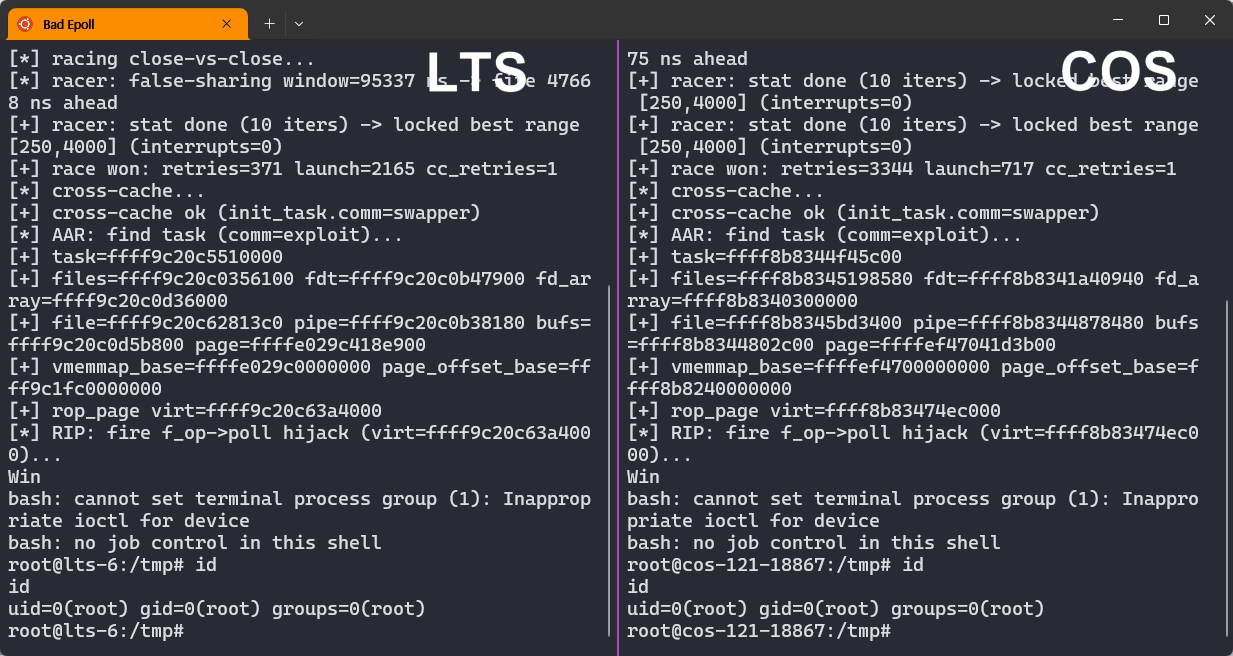 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.
 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 zinja-coder/damn-vulnerable-android-components
An intentionally vulnerable Android Application to demonstrate various vulnerabilities that airses in Android Components.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 byt3quester/cve-2023-20938-poc
Local privilege escalation proof-of-concept for CVE-2023-20938, a use-after-free in Android binder, achieving root and disabling SELinux on…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…