CVE-2024-24945-NGINX-RIFT---TryHackMe-Lab-Walkthrough

This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…

This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…

PoC scripts to exploit LFR (Local File Read) via PHP filters chain oracle (php://filter), especially for CTF purposes or the exploit of…

RSA attack tool (mainly for ctf) - retrieve private key from weak public key and/or uncipher data

BadZure automates the deployment of intentionally misconfigured Entra ID tenants and Azure subscriptions, populating them with diverse entities and…

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).

An updated collection of resources targeting browser-exploitation.

This is an intentionally vulnerable smart contract truffle deployment aimed at allowing those interested in smart contract security to exploit a wide…

:triangular_flag_on_post: A CLI tool & library to enhance and speed up script/exploit writing with string conversion/manipulation.

This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…

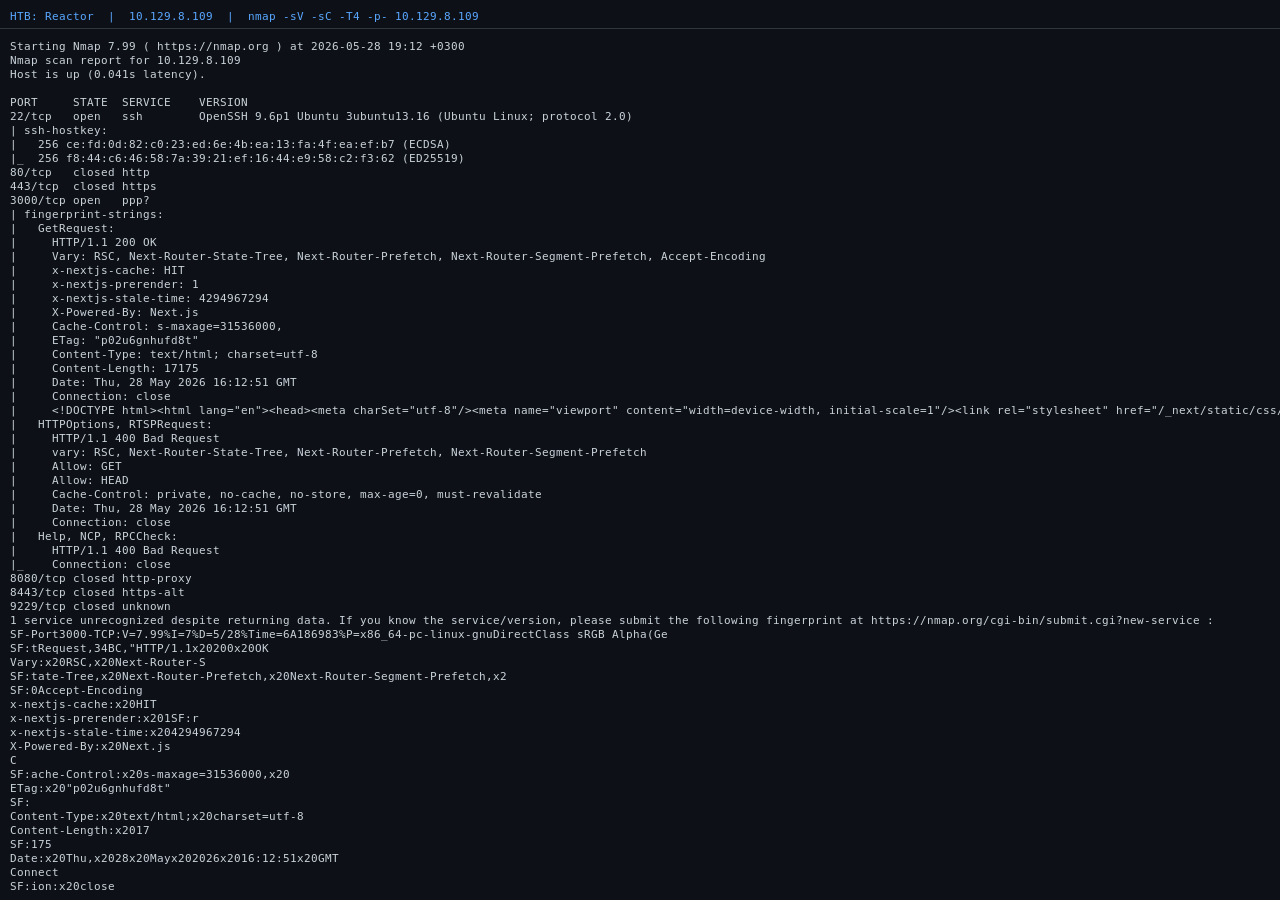
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…

Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.

A Python PoC for CVE-2022-21661, adapted from z92g's Go PoC, designed to demonstrate the vulnerability in a more accessible scripting environment.

:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens

"Lavel Exploit CVE-2018-15133 is a powerful exploit that allows attackers to gain unauthorized access to vulnerable systems. This exploit was…

A collection of useful links for Pentesters

How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.

Educational proof-of-concept replicating CVE-2021-38297, a Go WASM buffer overflow leading to stored XSS. Includes vulnerable app setup, exploit…

CVE-2022-24227 [Updated]: BoltWire v8.00 vulnerable to "Stored Cross-site Scripting (XSS)"