
CVE-2022-37706
 ecu-10525611-xander/cve-2022-37706
All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
binary-exploitationctfexploitation+2
2
ecu-10525611-xander/cve-2022-37706All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 ledksv/interpreter-hackthebox
HackTheBox Interpreter walkthrough: CVE-2023-43208 Mirth Connect deserialization RCE, PBKDF2 hash cracking, and eval() injection privilege escalation…
 tr00jan99/pwntilldawn-portal-walkthrough
A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…
 oscerd/process-injection-playground
A collection of samples and material related to process injection
 ns-projects-unina/ctf_cve_dsp_1
Una CTF, in formato DSP-compliant, basata sulla CVE-2025-29927 di nextjs.
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 jason-siu/cve-2019-9053-exploit-in-python-3
Python 3 exploit for CVE-2019-9053 (SQL injection) with hash-cracking, updated from outdated Python 2 code for TryHackMe CTF use.
 materaj2/mintinstall-object-injection
CVE-2019-17080

 trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 theporgs/exegol
Fully featured and community-driven hacking environment
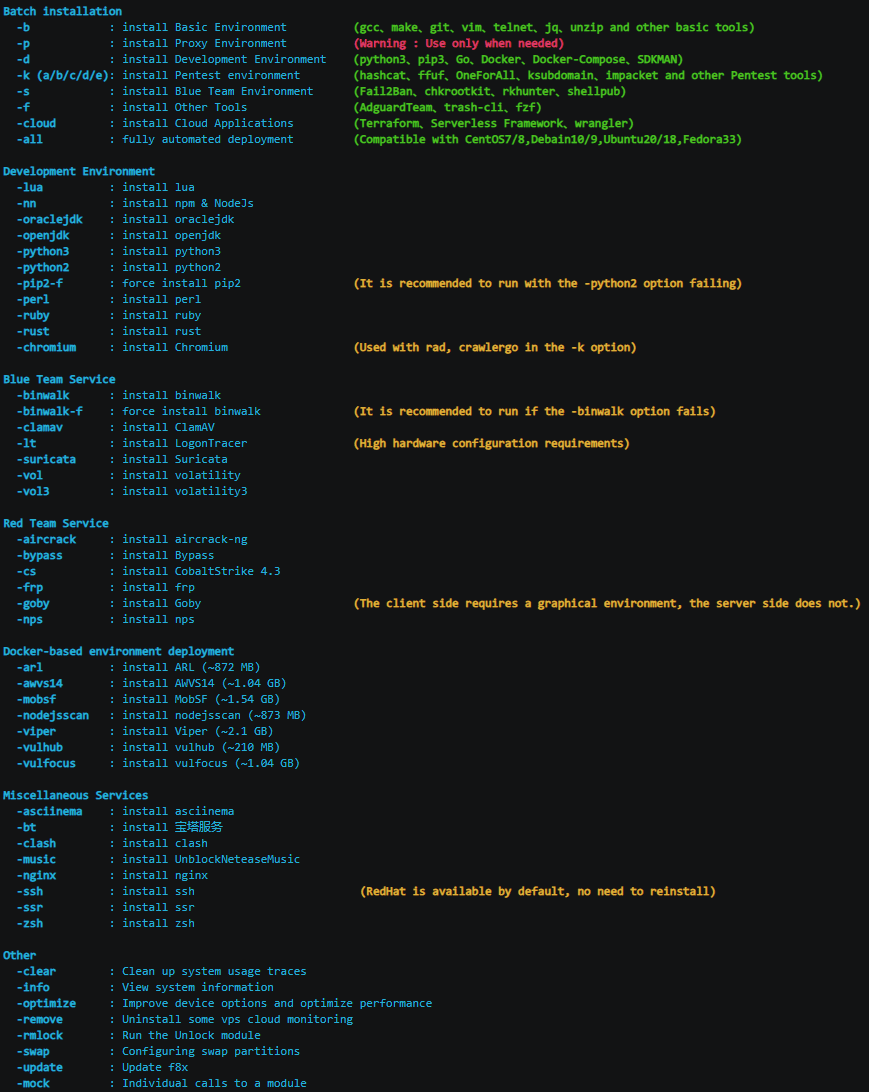 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool