Juiceshopgl
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
ctfeducationlabs-practice+5
mbrandner-group/juiceshopglIntentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
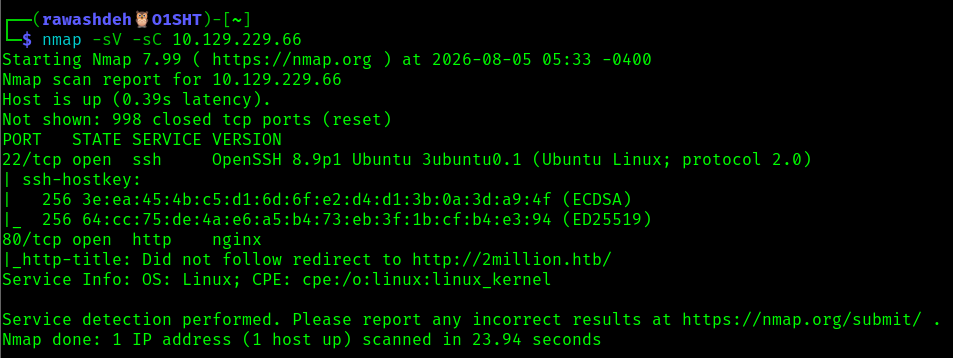 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…