
polkit-CVE-2021-3560_writeup
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
binary-exploitationctfeducation+4
realatharva15/polkit-cve-2021-3560_writeupbeginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.

 downunderctf/challenges_2022_public
Files + Writeups for DownUnderCTF 2022 Challenges
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
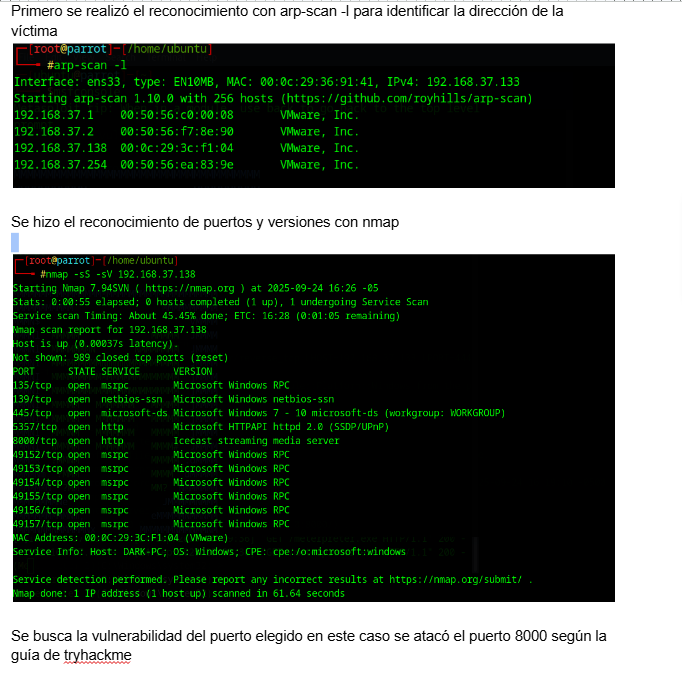 monseigneurpatas/thm-ice-icecast-rce-privesc
Full compromise of TryHackMe's Ice machine — Icecast 2.0.1 RCE (CVE-2004-1561) via buffer overflow, followed by Windows privilege escalation through…
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 vladko312/research_successful_errors
Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF