

thm-cybersec-portfolio
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
ctfeducationpenetration-testing+3
moscvv/thm-cybersec-portfolioWrite-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
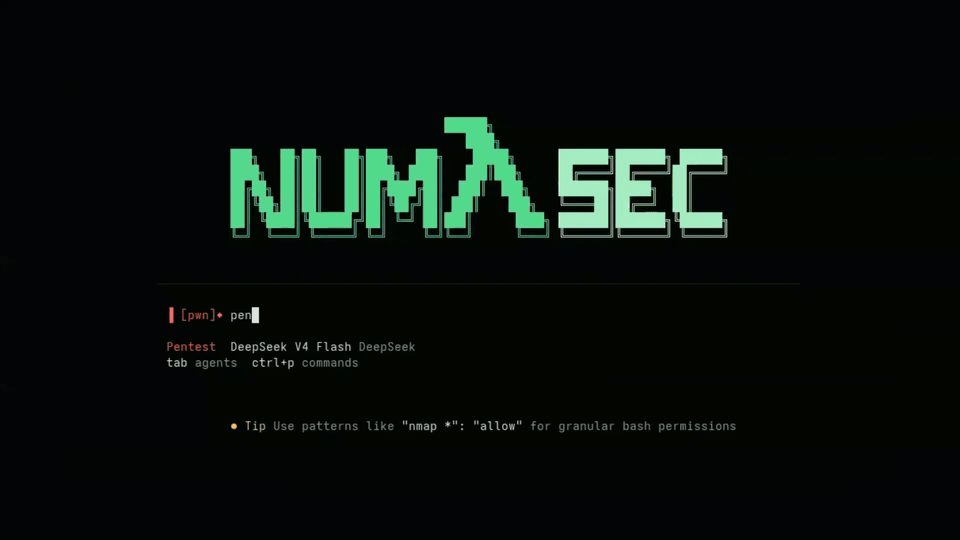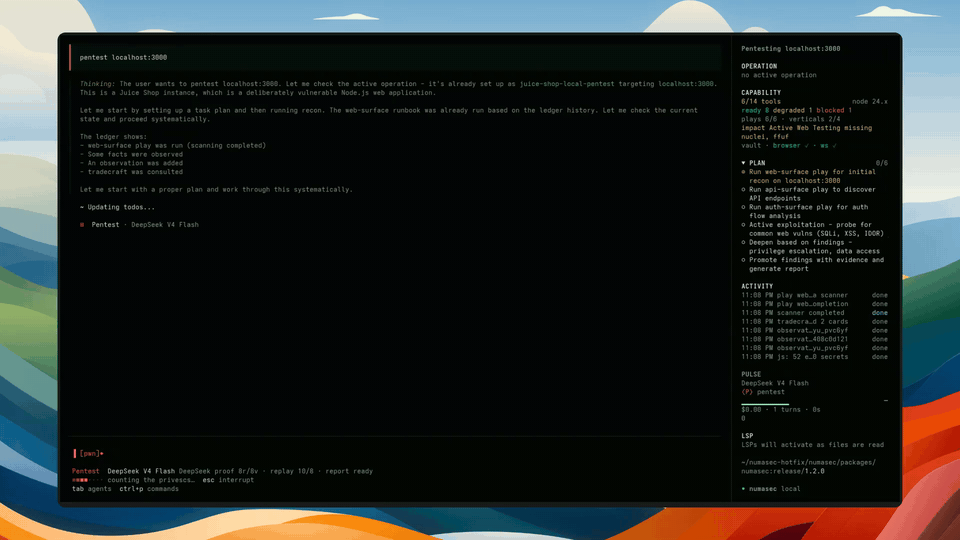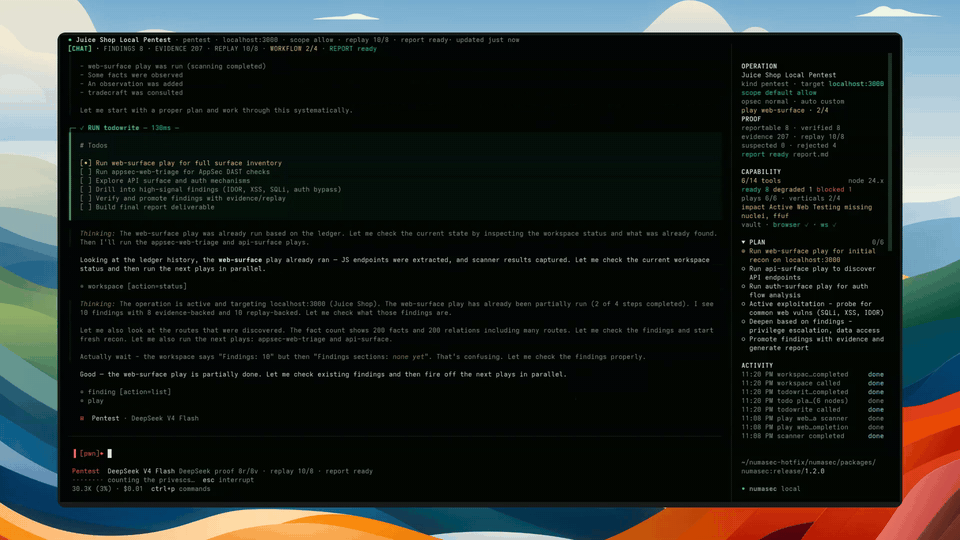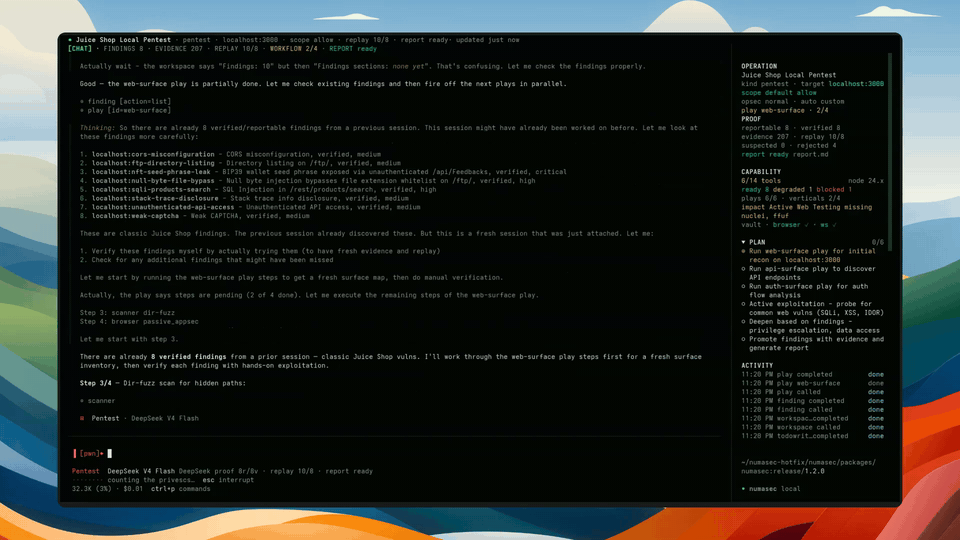 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 juice-shop/multi-juicer
Host and manage multiple Juice Shop instances for security trainings and Capture The Flags
 security-prince/resources-for-application-security
Some good resources for getting started with application security
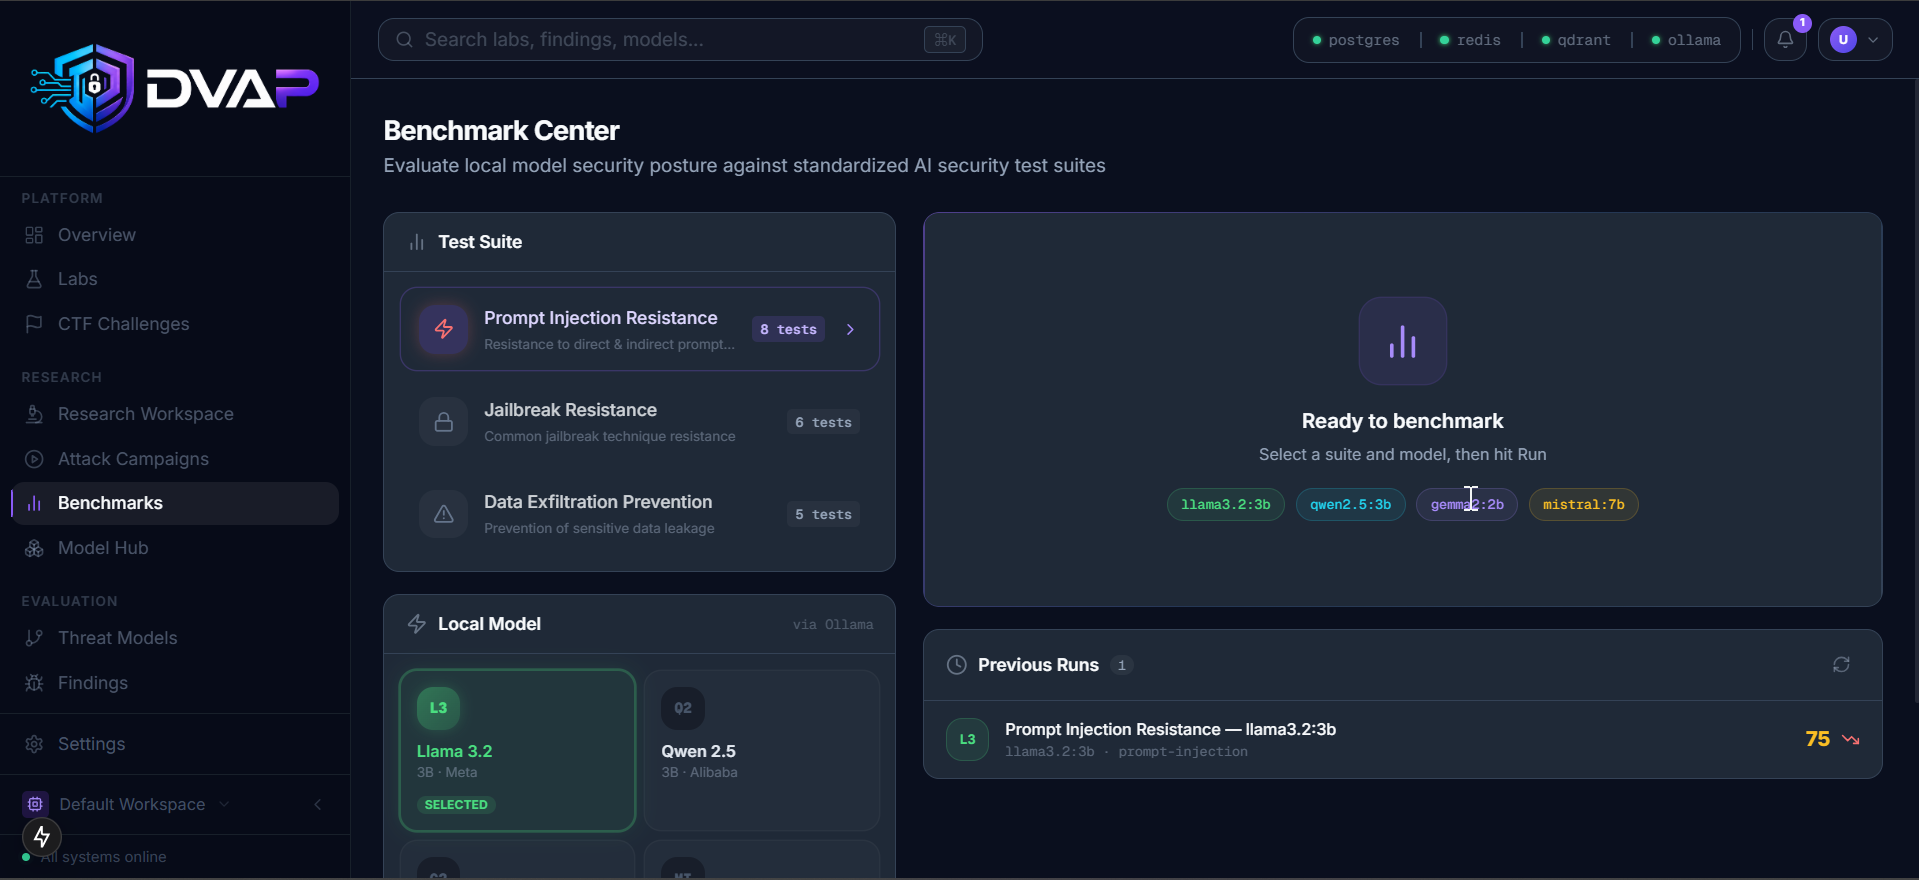 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/owasp-learning-gateway
OWASP Learning Gateway Project