
AllAboutBugBounty
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
ctfcurated-resourceseducation+7
6.9k3 years ago
daffainfo/allaboutbugbountyAll about bug bounty (bypasses, payloads, and etc)
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
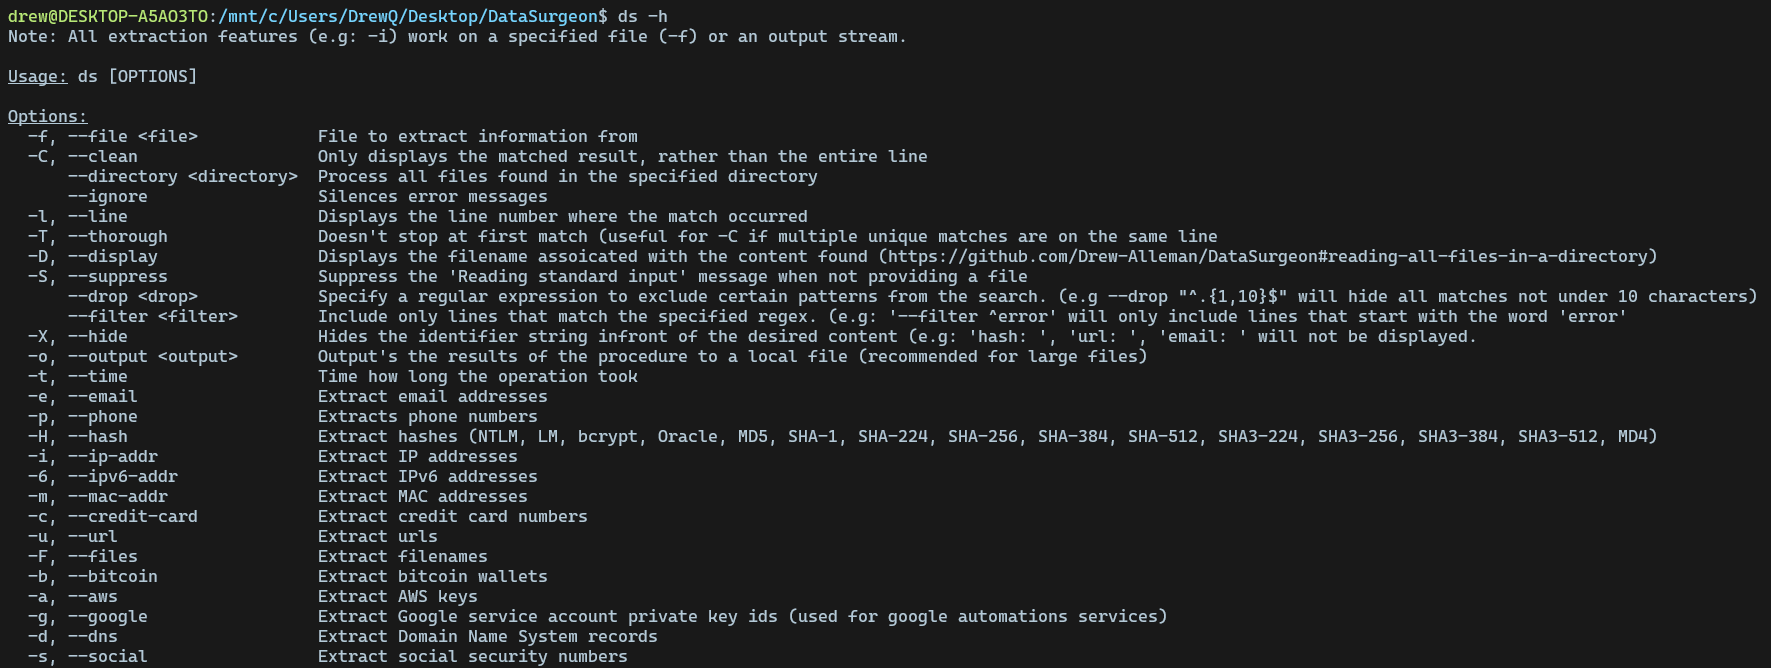 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
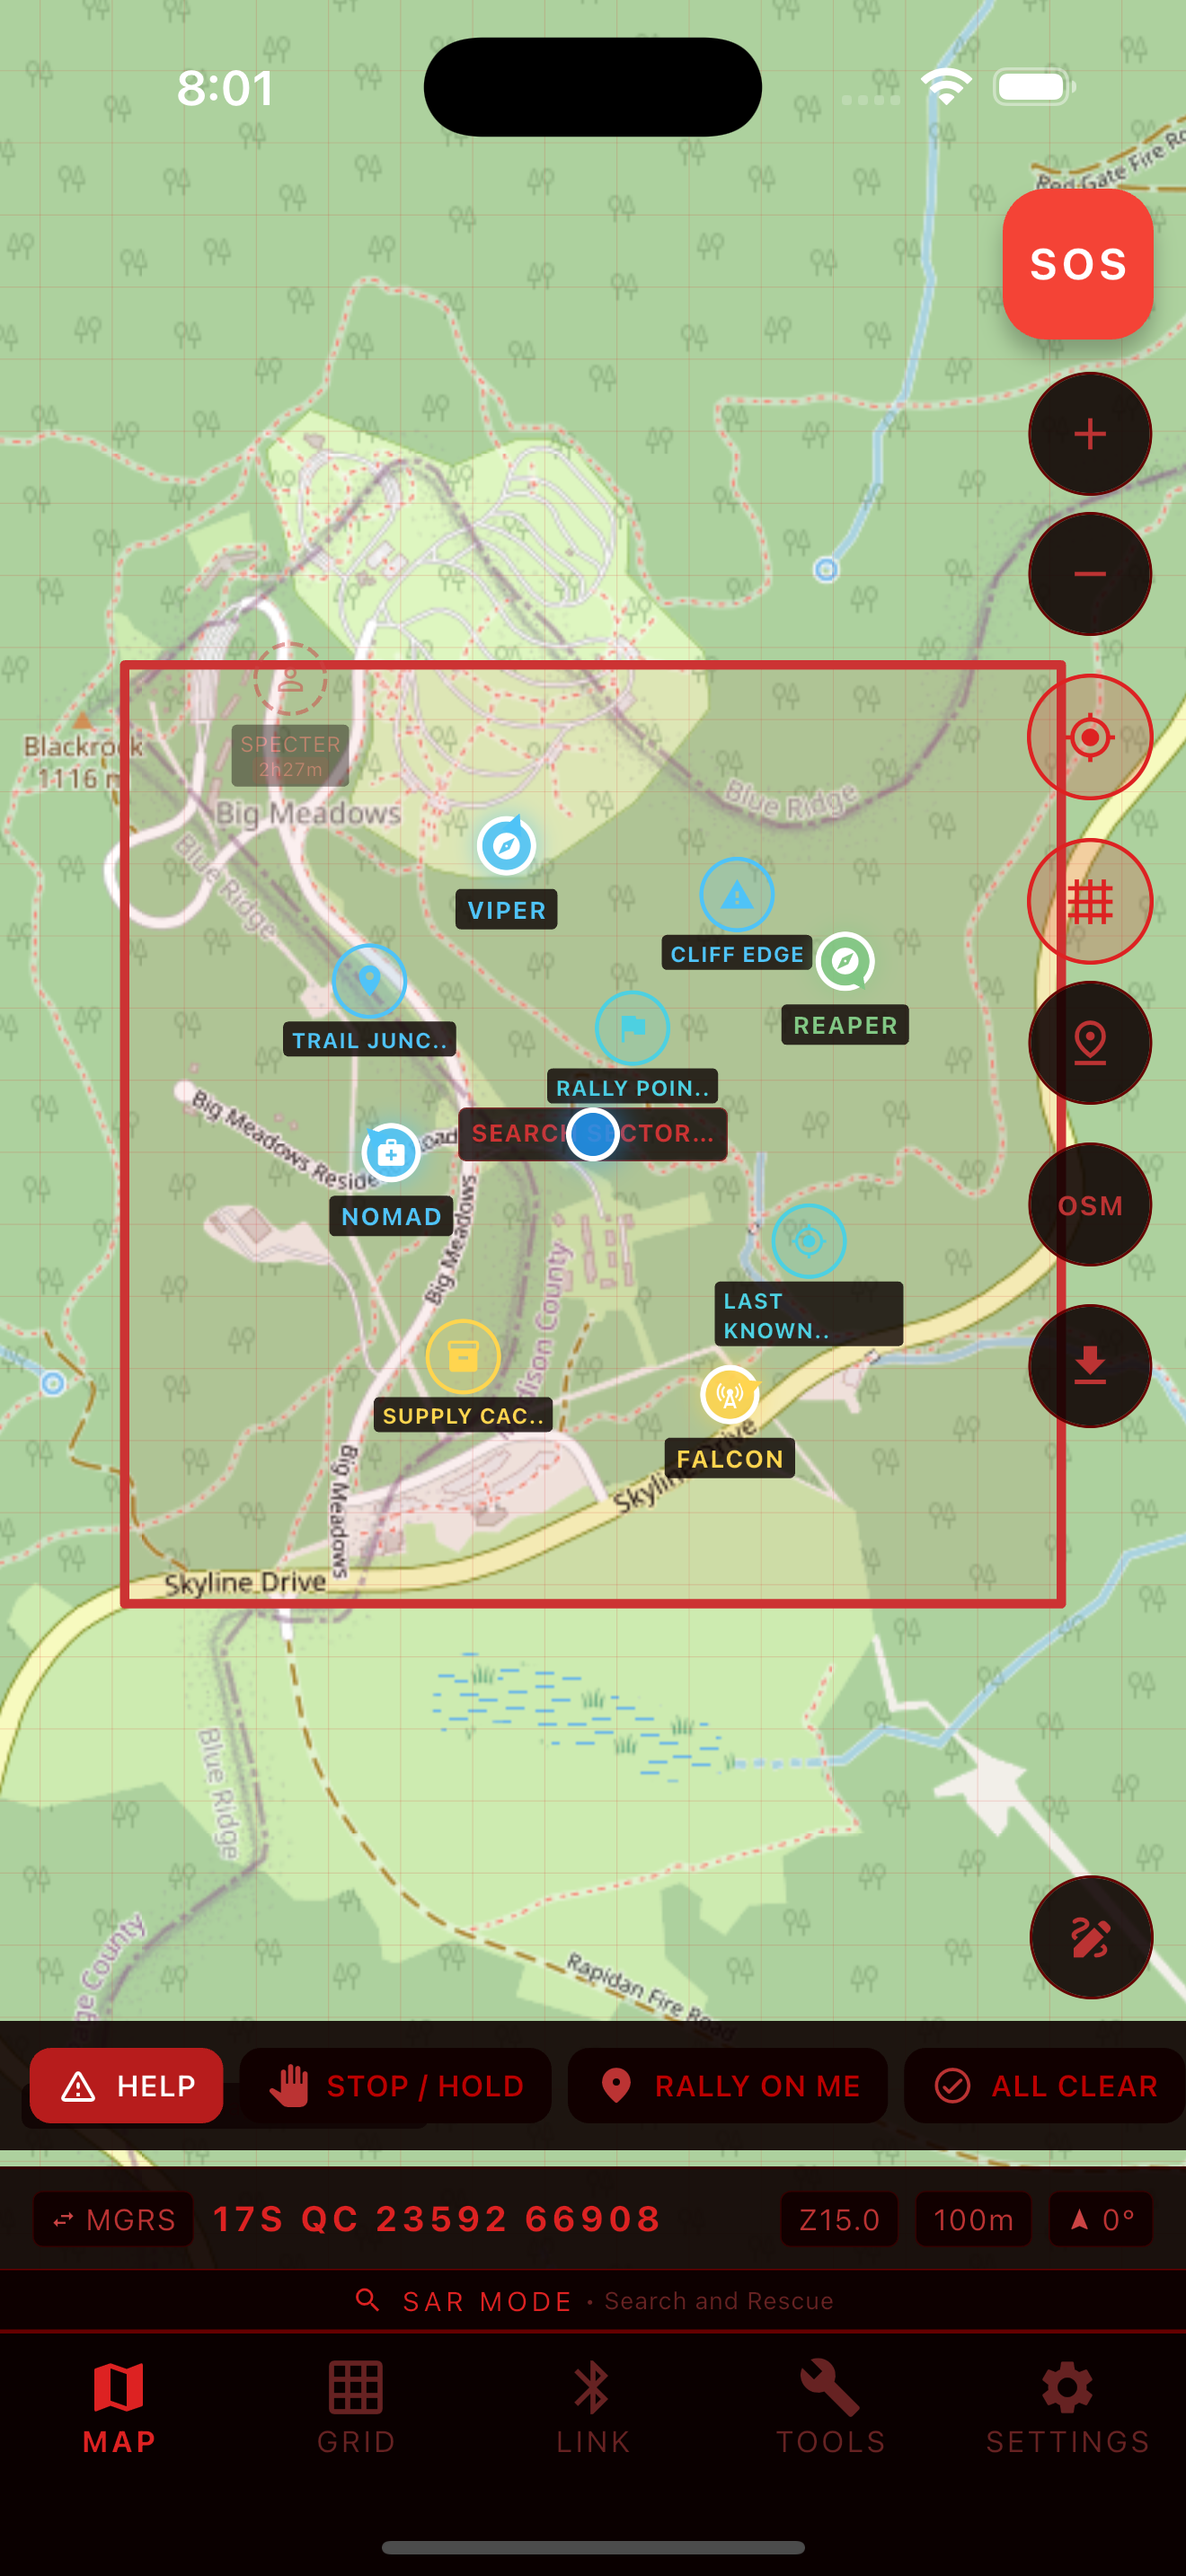 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
 hydr0nium/ctftools
Curated database of CTF and pentesting tools with add/remove functionality, enabling quick access to community-vetted hacking utilities.
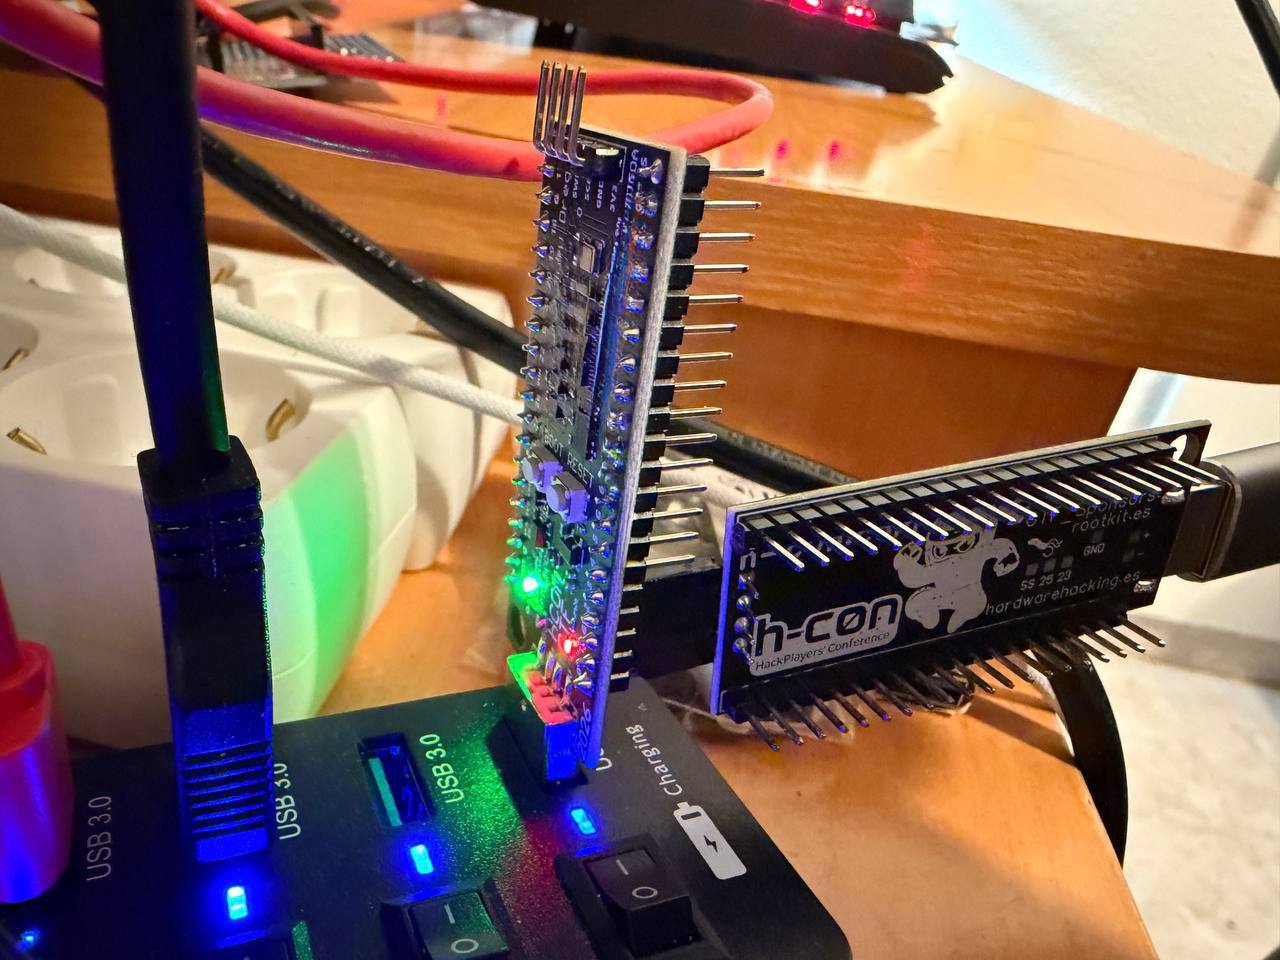 therealdreg/hcon2026hwctf
Hardware Hacking CTF hcon2026hwctf - RISCV Hazard3 (@Wren6991) Exploiting by @b1n4ri0 @antoniovazquezblanco & @therealdreg
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 theporgs/exegol
Fully featured and community-driven hacking environment