
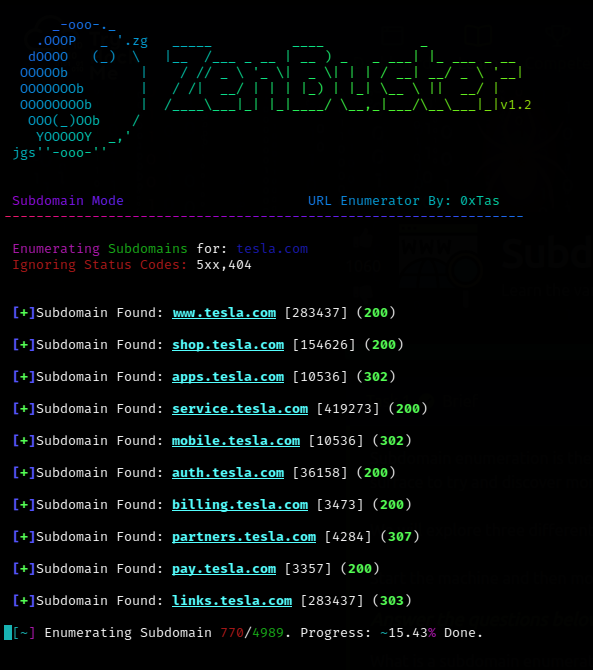
zenbuster
 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
ctfinformation-gatheringpenetration-testing+2
0xtas/zenbusterMulti-threaded URL enumeration/content-discovery tool in Python.
 th3xace/offport_killer
This tool aims at automating the identification of potential service running behind ports identified manually either through manual scan or services…
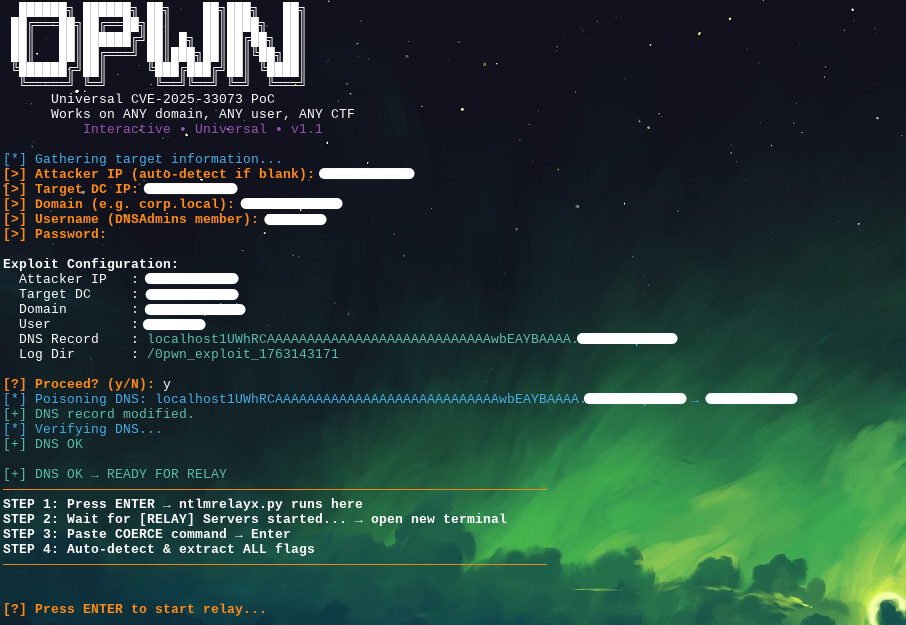 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
 motechstore/cve-2025-27591-poc
# CVE-2025-27591 PoC — Below Local Privilege Escalation This repository contains a Proof of Concept (PoC) demonstrating the local privilege…
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
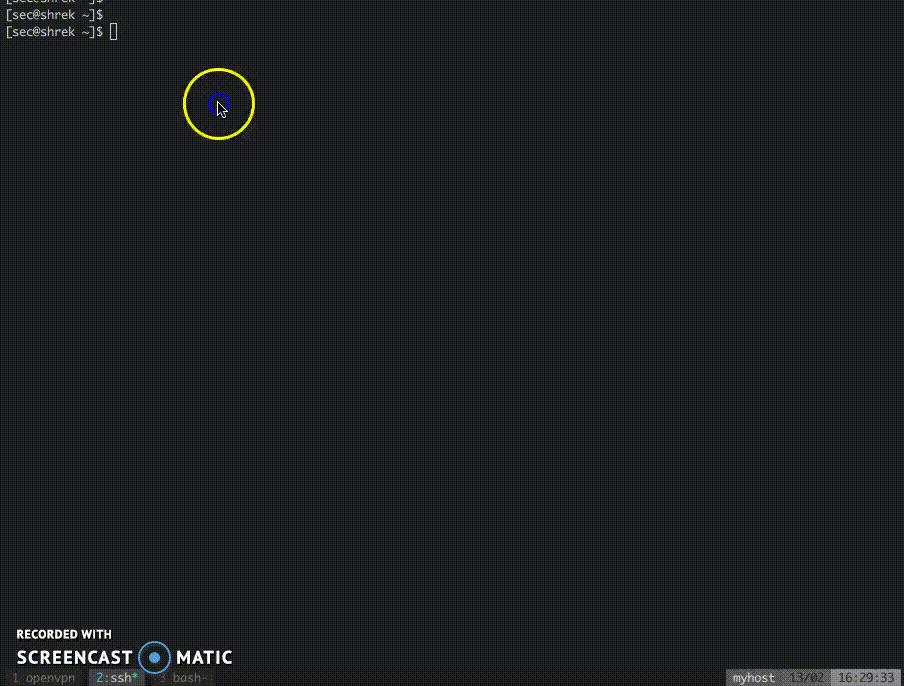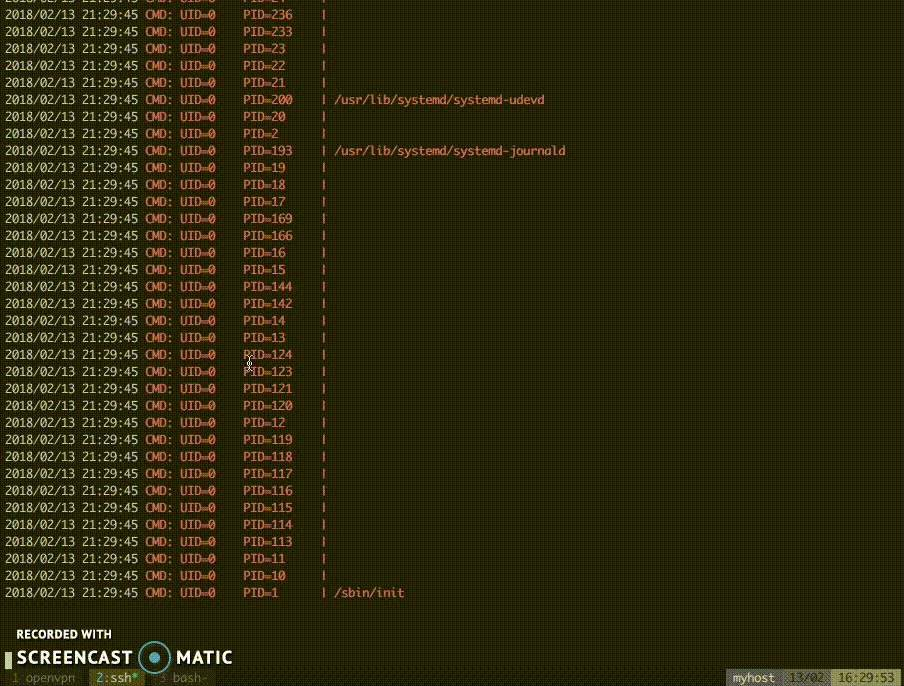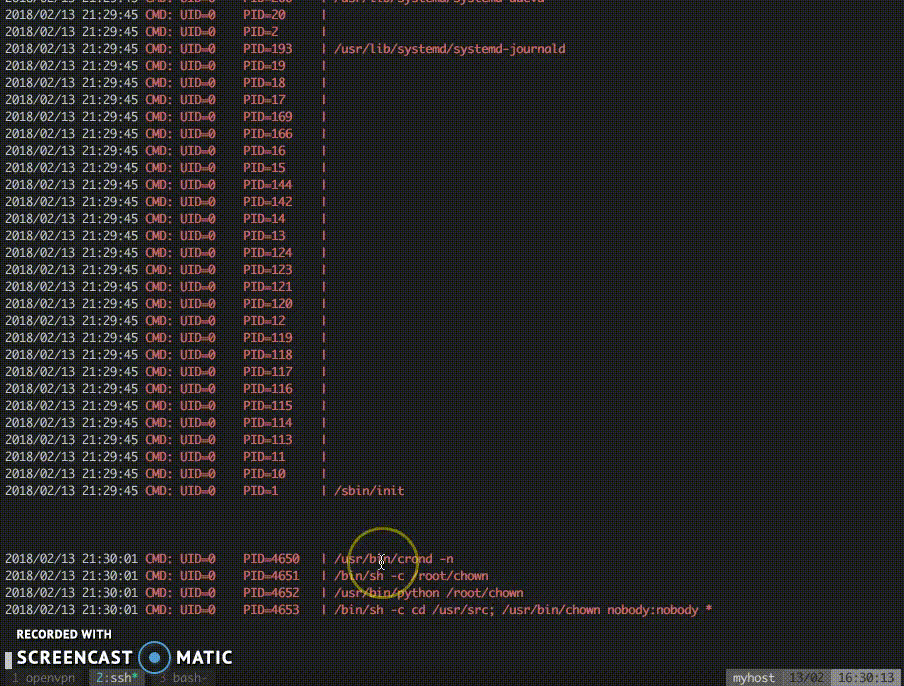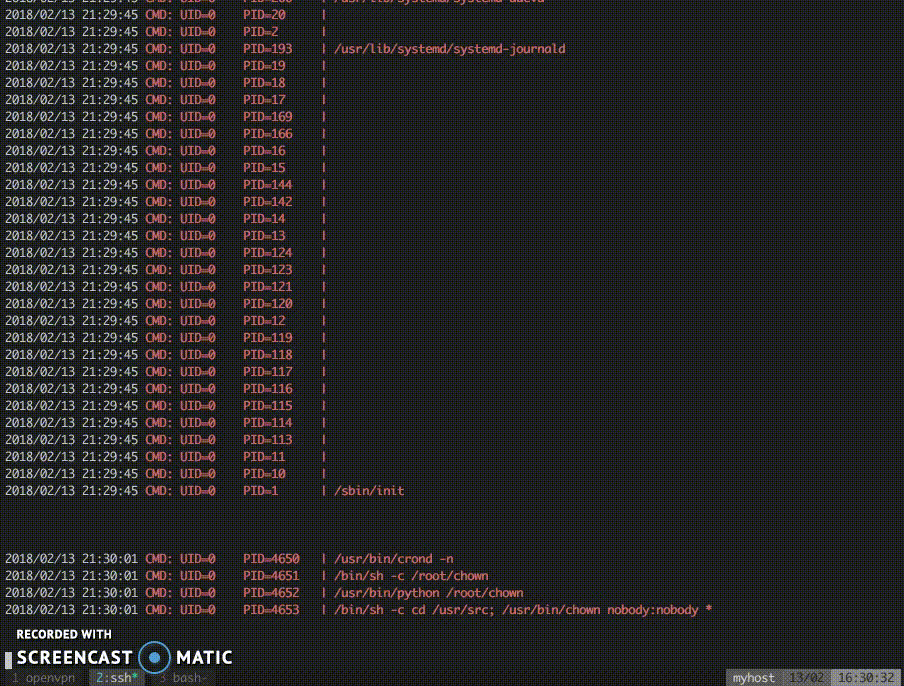 dominicbreuker/pspy
Monitor linux processes without root permissions
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
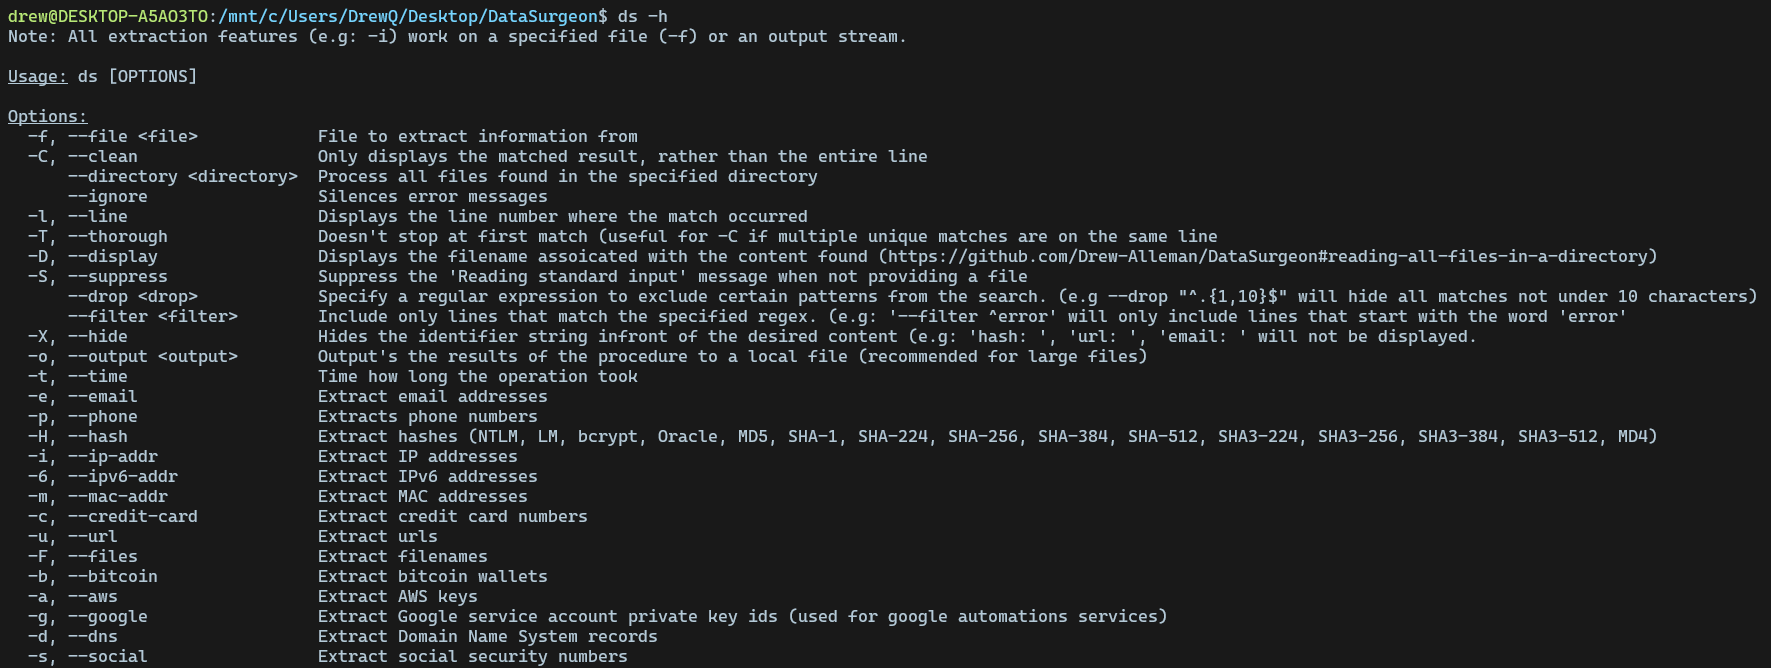 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 gr1mmie/autoenum
Automatic Service Enumeration Script
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
 katseyres2/cve-2022-44268-pilgrimage
Automated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
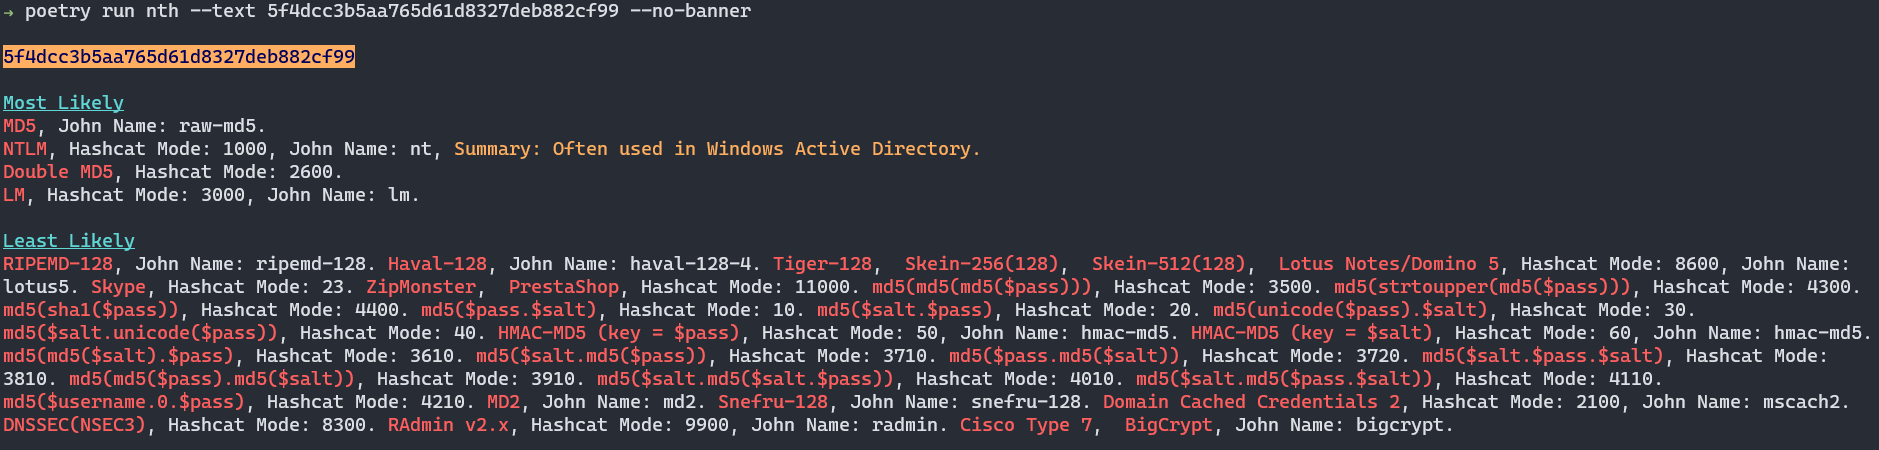 bee-san/name-that-hash
Identify 300+ hash types instantly via CLI or web app. Prioritizes popular hashes, provides summaries, and integrates with HashCat and John the…
 alreadyclosed/cve-2026-39987
CVE-2026-39987 for marimo 0.20.4 PoC
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 noraj/ctf-party
:triangular_flag_on_post: A CLI tool & library to enhance and speed up script/exploit writing with string conversion/manipulation.