CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 r4y-br/cve-2022-22963
Python automation script that reproduces CVE-2022-22963, a critical SpEL injection in Spring Cloud Function, enabling reverse shell in authorized lab…
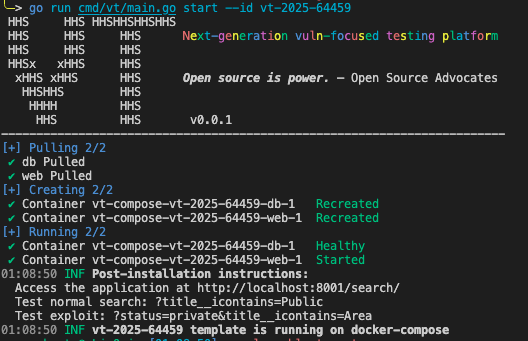 omarkurt/django-connector-cve-2025-64459-testbed
A self-contained testbed for Django CVE-2025-64459. Demonstrates QuerySet.filter() parameter injection via dictionary expansion using Docker.
 yucaerin/cve-2025-6254
CVE-2025-6254 — Doctreat Core <= 1.6.8 — Unauthenticated Privilege Escalation
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
 sparshbiswas-ai/cve-2025-11844-smolagents
Educational sandbox and dynamic proof-of-concept scanner for CVE-2025-11844 XPath injection in Hugging Face smolagents library, enabling local data…
 johnwickakash12/cve-2021-41773
Detailed writeup of CVE-2021-41773 Apache path traversal and RCE exploitation, with step-by-step commands and root cause analysis from a TryHackMe…
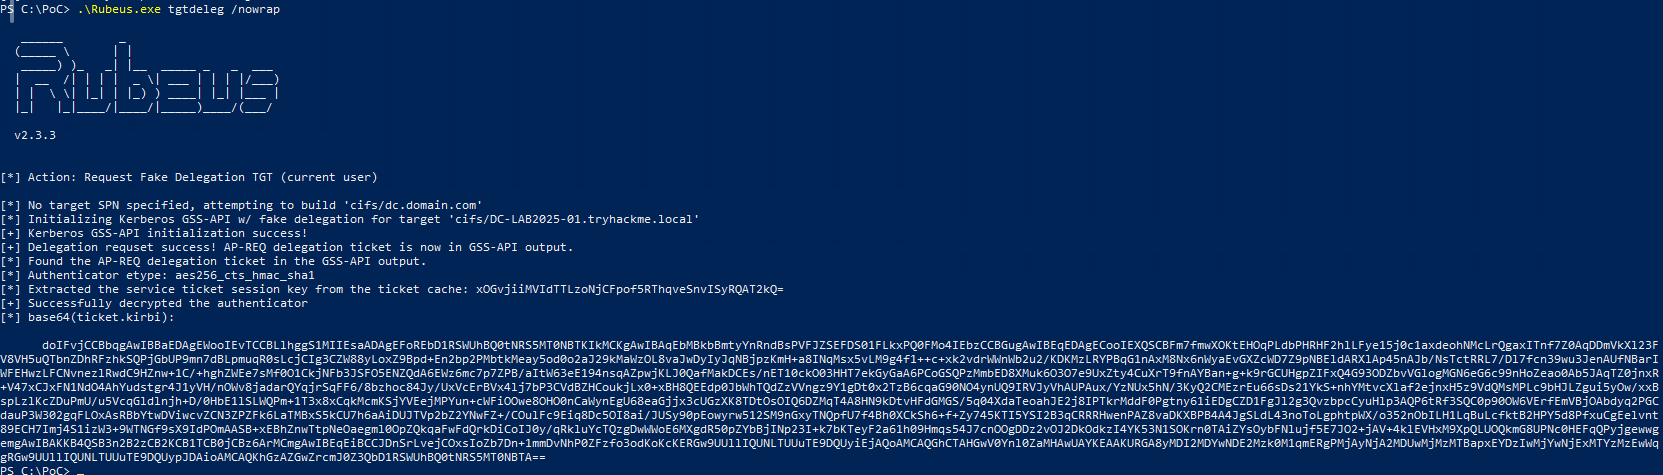 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
 jithinodattu/cve-2023-24329-lab
Self-contained Docker lab demonstrating CVE-2023-24329, a Python urllib parser differential that bypasses URL scheme and host filters, with…
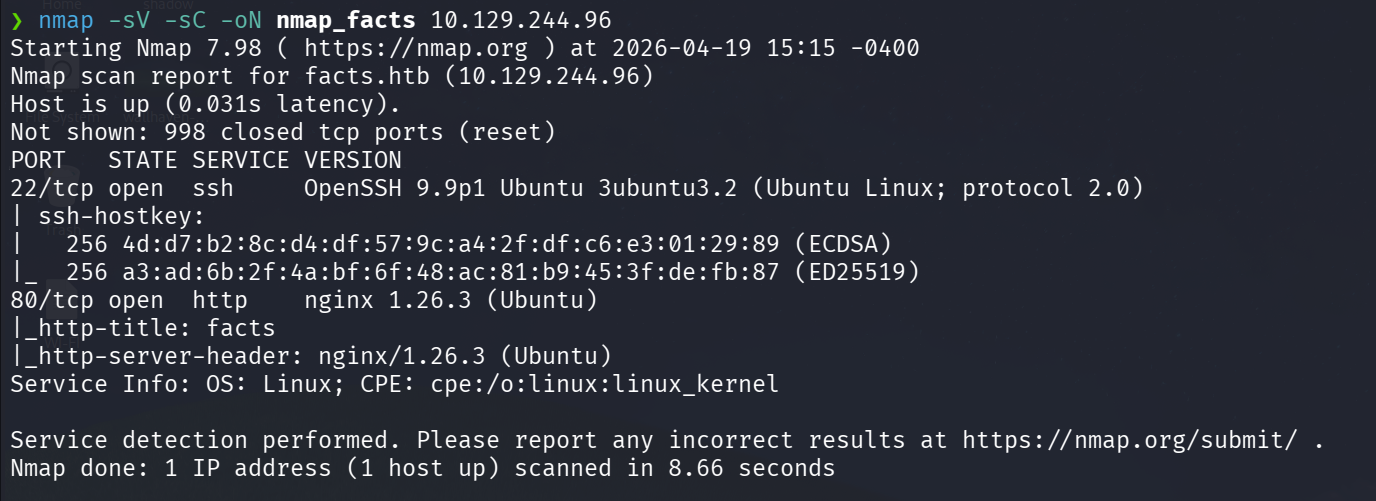 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 jeanback1/react-rsc-cve-2025-55182-lab
Educational lab demonstrating CVE-2025-55182: Critical RCE in React Server Components via prototype pollution in the Flight protocol
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).