
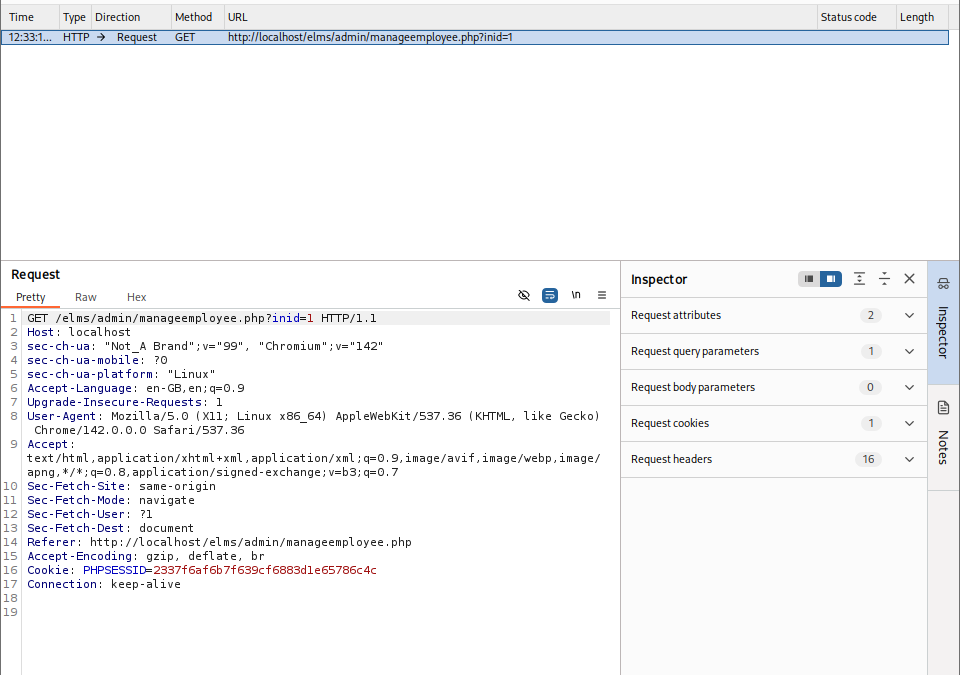
CVE-2025-67315
 r-pradyun/cve-2025-67315
CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
ctfeducationexploitation+3
r-pradyun/cve-2025-67315CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
 datntsec/cve-2019-12735
Detailed technical analysis and proof-of-concept for CVE-2019-12735, an arbitrary code execution vulnerability in Vim/Neovim via modeline sandbox…
 naveen-005/next.js-middleware-bypass-vulnerability-cve-2025-29927
A basic proof of concept of the CVE-2025-29927 vulnerability that allows to bypass the middleware scripts.
 m0d0ri205/pdfjs
Wargame exploiting CVE-2024-4367 in PDF.js for educational vulnerability analysis and exploitation practice.
 hanmin0512/cve-2014-6271_pwnable
Hands-on lab demonstrating the Shellshock (CVE-2014-6271) Bash vulnerability with privilege escalation via environment variable injection, based on…
 r1skkam/printnightmare
Learn about the vulnerability known as PrintNightmare (CVE-2021-1675) and (CVE-2021-34527)
 w1ngless/cve-2021-39172-rce
Cachet 2.4 Code Execution via Laravel Configuration Injection CVE-2021-39172
 cd-ratel/cve-2025-32432
Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)

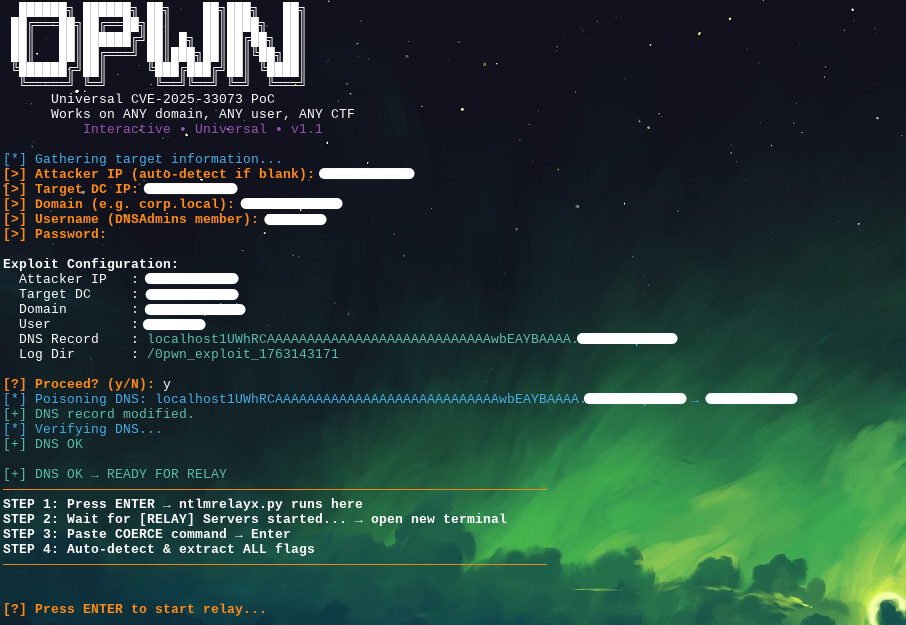 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 kaist-hacking/cve-2023-6702
Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
 xib3rr4dar/wannarace
WebApp intentionally made vulnerable to Race Condition for practicing Race Condition
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
 nxploited/cve-2025-2266
Checkout Mestres do WP for WooCommerce 8.6.5 - 8.7.5 - Unauthenticated Arbitrary Options Update