

owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
13
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 juice-shop/multi-juicer
Host and manage multiple Juice Shop instances for security trainings and Capture The Flags
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/securityshepherd
Web and mobile application security training platform
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
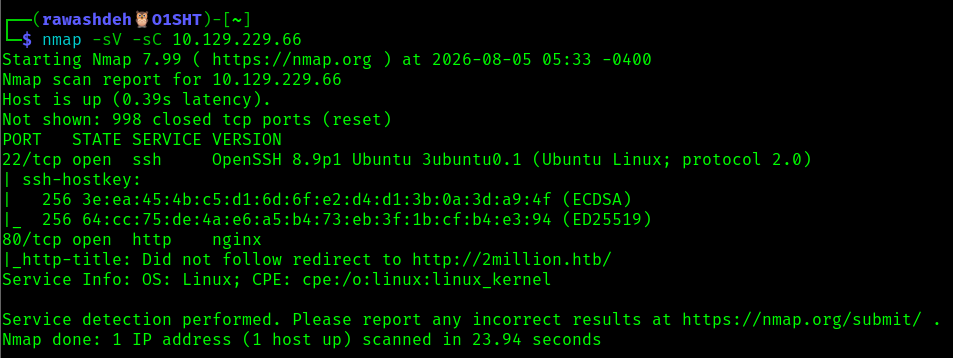 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).