
striatum-ctf
 jawh3/striatum-ctf
Research artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
ai-securityctfcurated-resources+5
2
jawh3/striatum-ctfResearch artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 firmianay/ctf-all-in-one
Open-source CTF guidebook covering Pwn, reverse engineering, and web security, with structured chapters, worked examples, and tooling setup for…
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 dev-angelist/ejptv2-notes
eLearnSecurity Junior Penetration Tester (eJPT) v2 Notes
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 planners1490/sclock
Hardware-Bound 256-Slot Polymorphic VM, Non-Linear MBA & Apple Secure Enclave Binary Protector for macOS arm64 (Apple Silicon) — Public CrackMe & SDK…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
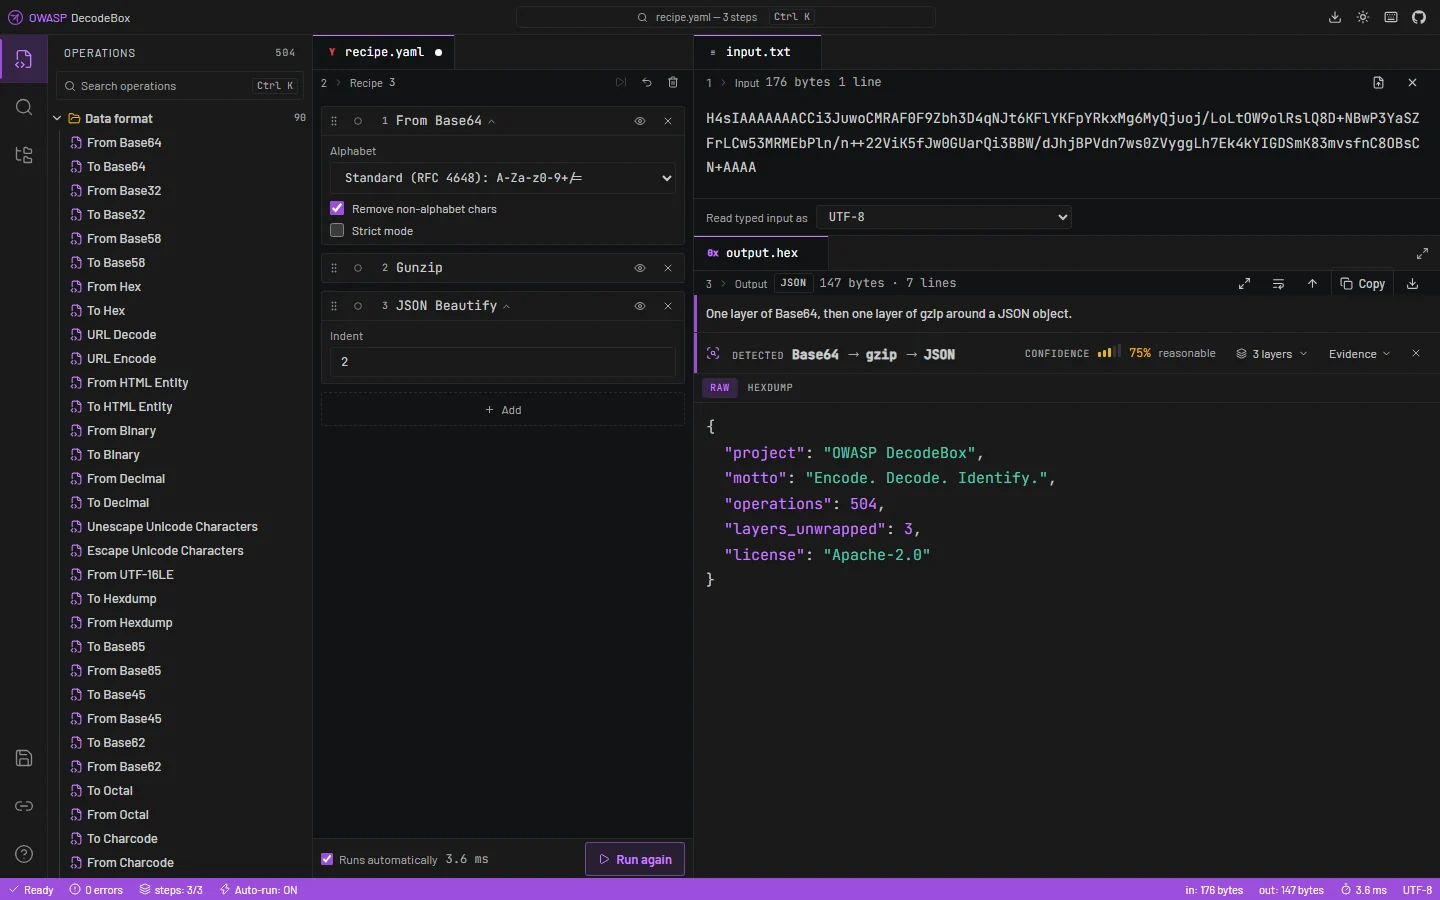 owasp/decodebox
Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
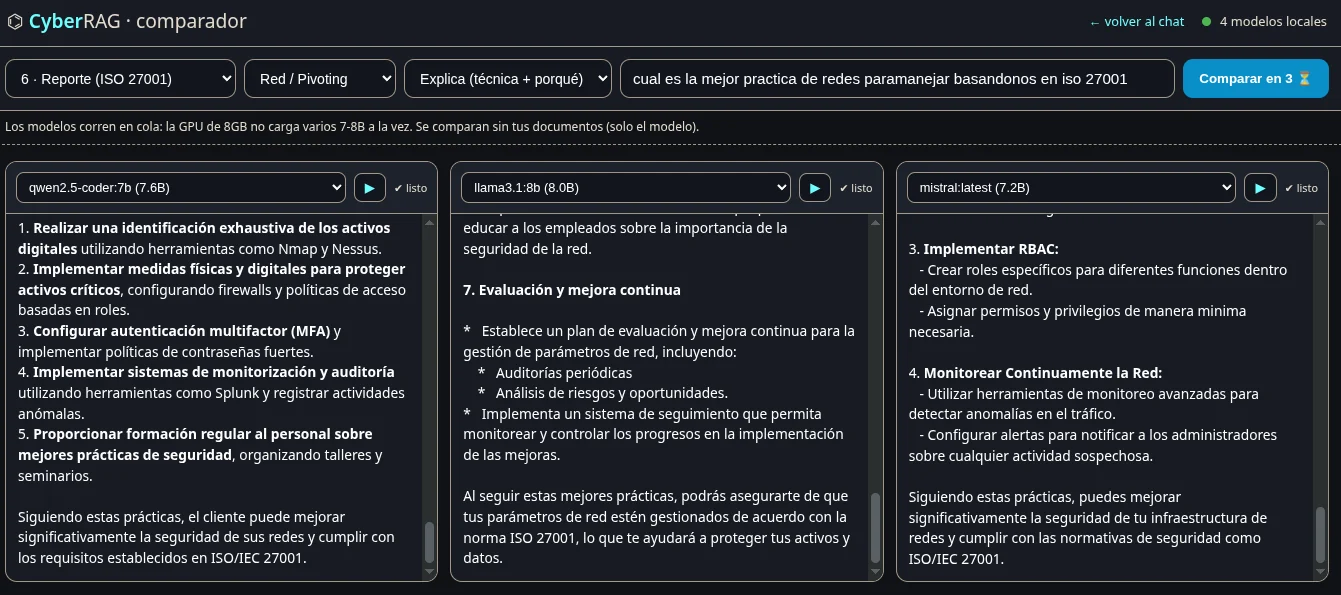
 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 liquid-sec/variatype.htb-cve-2025-66034
Python exploit script for CVE-2025-66034 in the HackTheBox Variatype machine, delivering command execution and reverse shell payloads for initial…
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…