
security-portfolio
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
ctfcurated-resourceseducation+6
mitsu-bis/security-portfolioSecurity portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 danreis20/pentest-lab-metasploitable2
Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 anlominus/bug-bounty
Bug Bounty ~ Awesomes | Books | Cheatsheets | Checklists | Tools | Wordlists | More

 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 portbuster1337/cve-2026-52806
Gogs RCE via argument injection in git rebase (CWE-88) — Python PoC. CVE-2026-52806
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 nahamsec/resources-for-beginner-bug-bounty-hunters
A list of resources for those interested in getting started in bug bounties
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 kikechans/-grafana-lfi-cve-2021-43798
📂 Grafana LFI Exploit (CVE-2021-43798). Extracción automatizada de credenciales y configuración. 🕵️
 cd-ratel/cve-2025-32432
Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
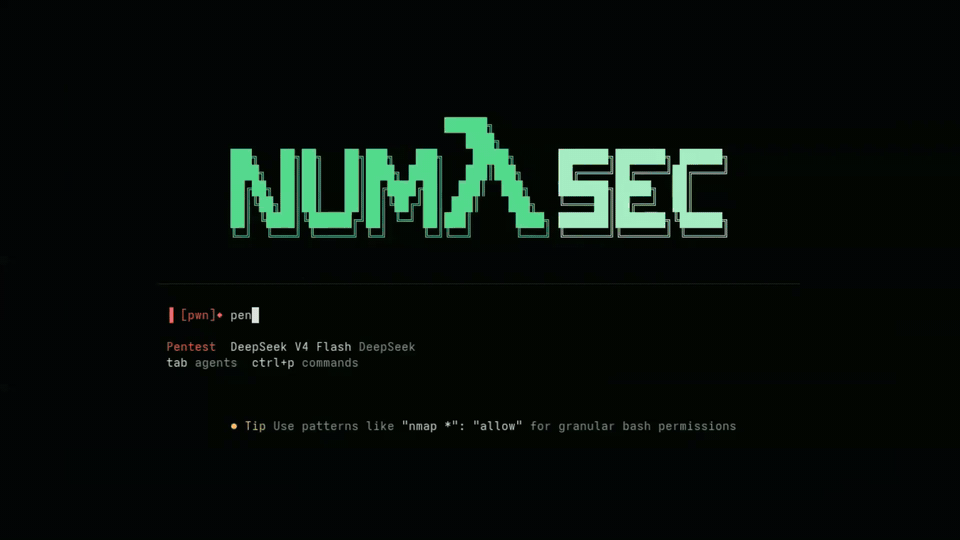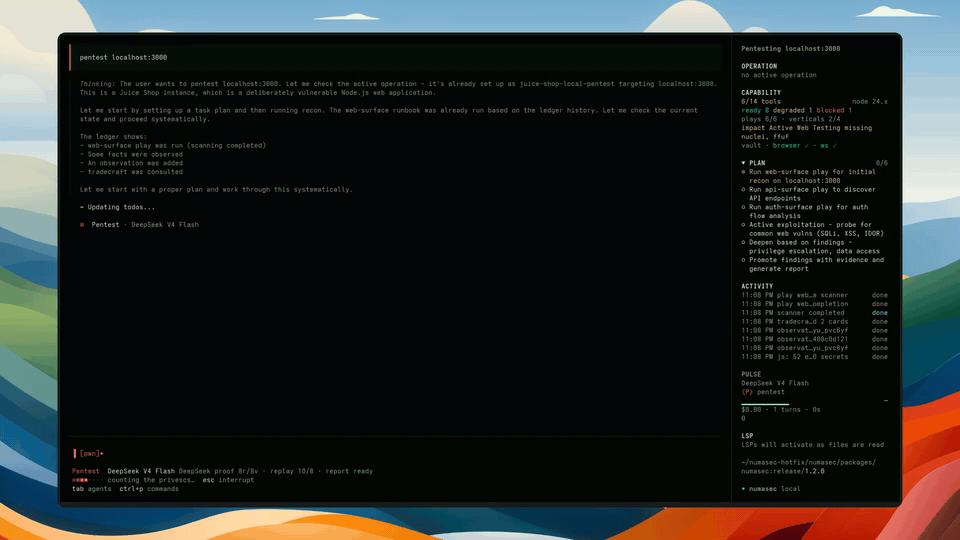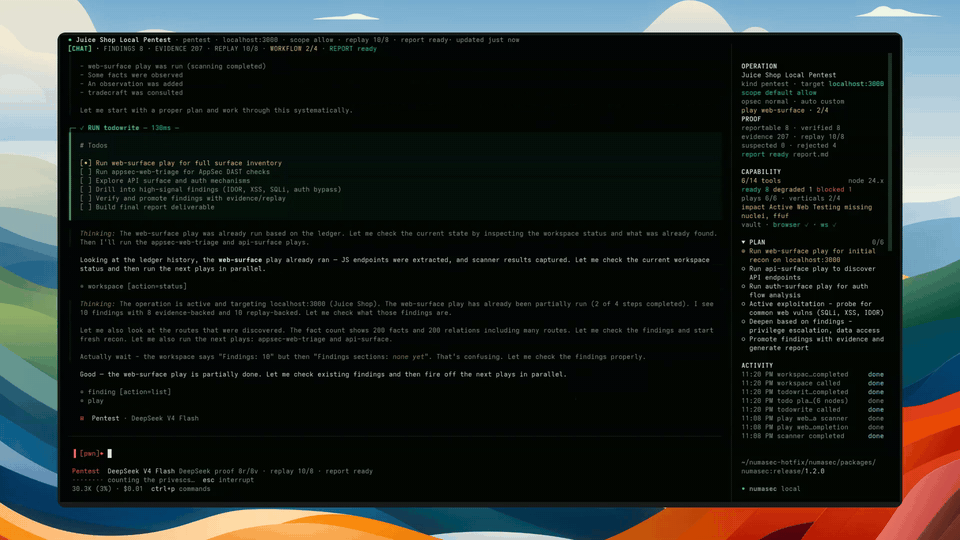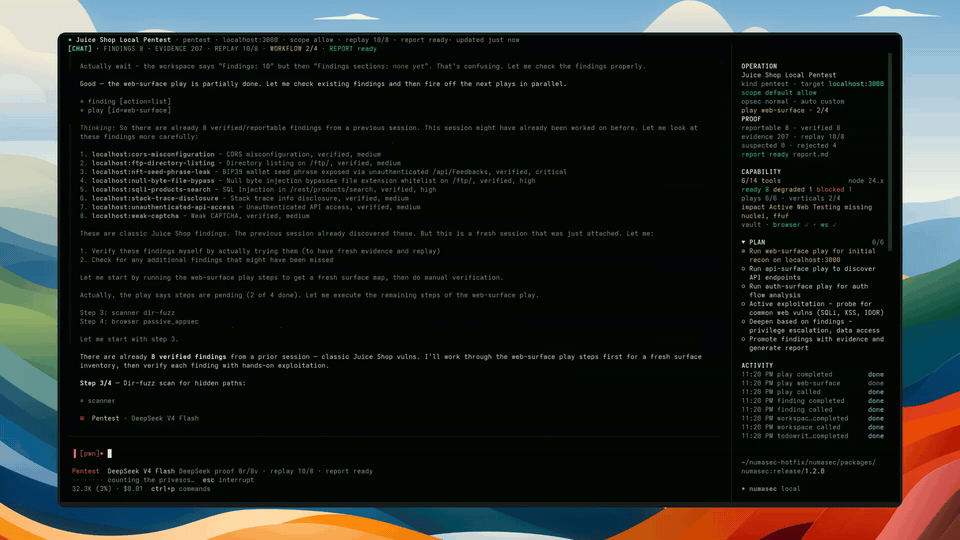 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 ffffffff0x/1earn
ffffffff0x 团队维护的安全知识框架,内容包括不仅限于 web安全、工控安全、取证、应急、蓝队设施部署、后渗透、Linux安全、各类靶机writup

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…